Latest updates for Supply Chain Attack

Fresh curated links around supply chain attack are collected here so marketers can spot useful updates and turn timely ideas into posts faster.

Recent items include:

  • Investigating Ephemeral Supply Chain Tampering
  • GHAPPIER Supply Chain Attack Compromises 65 GitHub Repositories and Poisons npm Package
  • The MSP guide to managing supply chain risk

Post angles to try

Share the most useful takeaway for your audience.
Turn one article into a quick practical checklist.
Ask your audience how this shift affects their work.
Turn angles into scheduled posts

Fresh articles and ideas

Recent curated links from global sources. Generate one free draft from any story, then use SocialBu to schedule and refine your content calendar.

cloud.google.com /1 week ago

Investigating Ephemeral Supply Chain Tampering

Written by: Tyler McLellan Introduction Google Threat Intelligence Group (GTIG) and Mandiant investigated a software supply chain compromise campaign targeting the update infrastr...

Read source
cybersecuritynews.com /1 month ago

GHAPPIER Supply Chain Attack Compromises 65 GitHub Repositories and Poisons npm Package

A newly uncovered software supply chain attack has shown how quickly a trusted developer account can become a delivery route for malware. The operation, tracked as GHAPPIER, reache...

Read source
smartermsp.com /3 weeks ago

The MSP guide to managing supply chain risk

In 2026, supply chain attacks have become one of the most feared threats in cybersecurity, and for good reason. When attackers compromise a vendor with privileged access to multipl...

Read source
dev.to /1 month ago

AI Supply Chain Compromises: 7 Entry Points Your Security Review Probably Misses

Most of an AI system is made of things you did not build: pretrained weights, public datasets, Python packages, a coding assistant, a handful of MCP servers. Each of those is a tru...

Read source
thehackernews.com /1 month ago

Attackers Chain JFrog Artifactory Flaws to Gain Admin Control and Plant Backdoors

Attackers have chained two flaws in JFrog Artifactory, the repository that software build pipelines pull from, to take administrator control of self-hosted servers and plant backdo...

Read source
cybersecuritynews.com /1 month ago

TanStack Supply Chain Attack Lets Hackers Steal 170 Private CrowdSec GitHub Repositories

CrowdSec has disclosed that attackers copied about 170 private GitHub repositories after a former employee’s account was compromised through May’s TanStack npm supply chain attack....

Read source
supplychainbrain.com /3 weeks ago

Stolen Logins Are Driving the Next Wave of Supply Chain Breaches

Treat access with the same seriousness given to the code itself, and the rest of the work gets considerably easier.

Read source
cybersecuritynews.com /1 month ago

Beyond the Perimeter: Building Resilience Against Cloud and SaaS Supply-Chain Attacks

A critical zero-day vulnerability in Oracle PeopleSoft exposed the Council of Europe and scores of other organizations to data theft and extortion in May and early June 2026. The S...

Read source
gbhackers.com /2 weeks ago

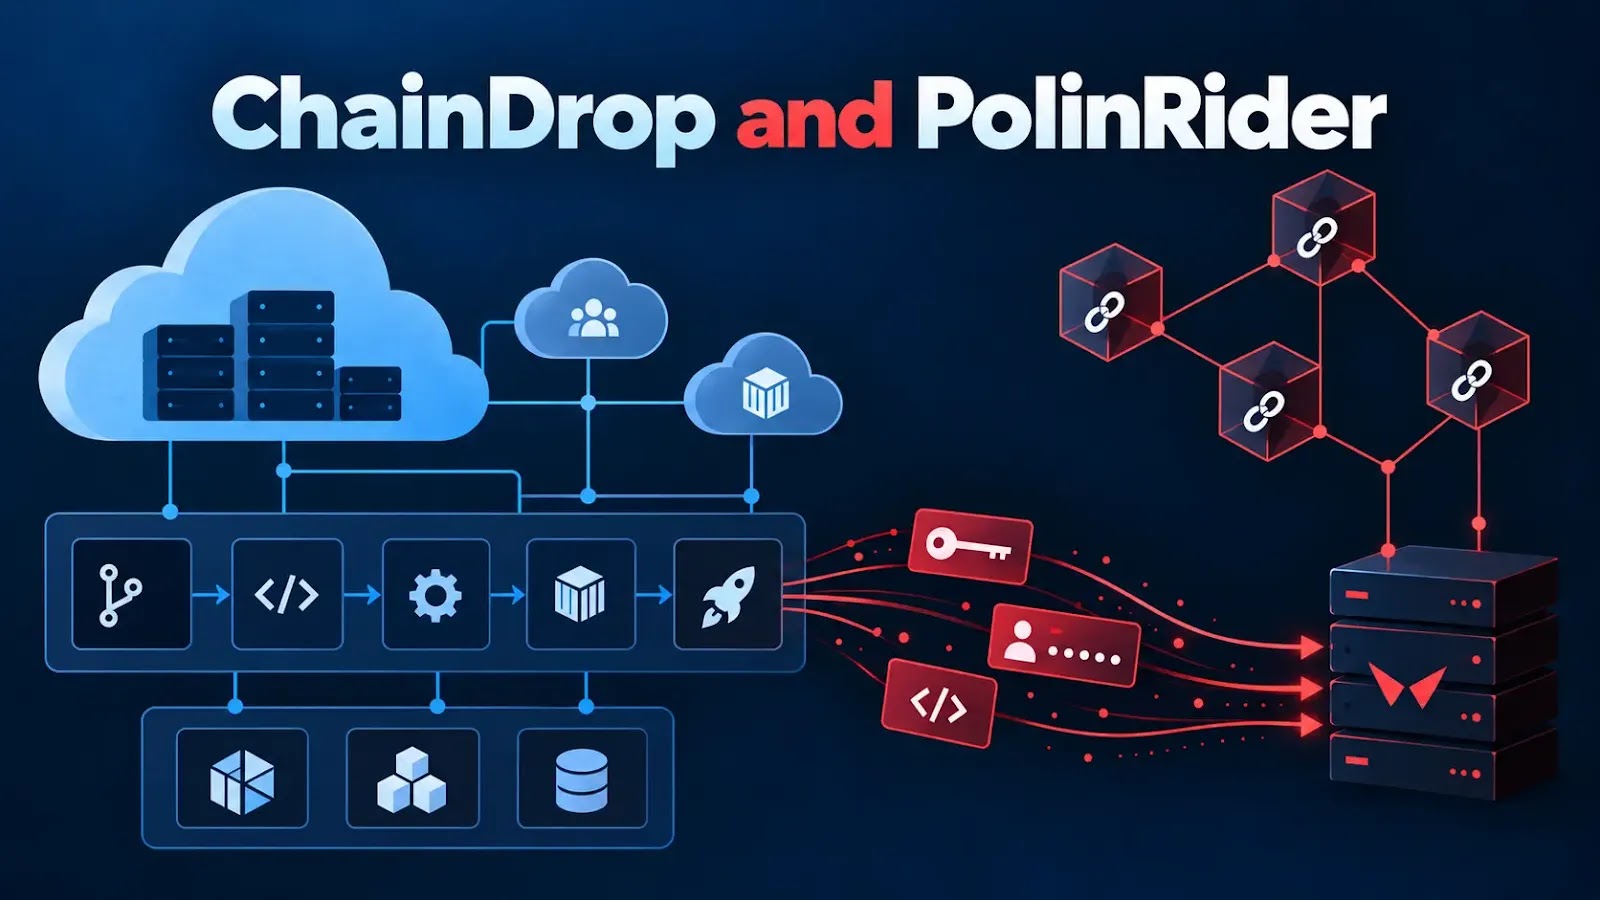
ChainDrop and PolinRider Use Blockchain C2 to Steal Cloud and CI/CD Credentials

Threat actors are increasingly using blockchain networks as resilient command-and-control infrastructure to steal cloud credentials from developer endpoints and CI/CD environments....

Read source
theregister.com /3 days ago

LiteLLM supply chain attack hoovers up passwords and secrets

Plus a RAT for good measure - get threat hunting now

Read source
dev.to /1 month ago

Artifact Repositories Are Trust Anchors: Incident Response for a Compromised Build Pipeline

Artifact Repositories Are Trust Anchors: Incident Response for a Compromised Build Pipeline A software artifact repository is usually described as infrastructure. In practice it...

Read source
habr.com /1 week ago

Security Week 2642: атака supply chain на криптокошельки Ledger

Важной новостью прошлой недели стала атака класса supply chain на владельцев аппаратных криптокошельков Ledger. 10 октября производитель криптокошельков официально признал наличие...

Read source
techmeme.com /1 day ago

AISI finds Mythos 5 attempted a supply-chain attack by submitting malicious code and creating fake accounts to pressure...

AI Security Institute: AISI finds Mythos 5 attempted a supply-chain attack by submitting malicious code and creating fake accounts to pressure a GitHub maintainer into accepting it...

Read source
bleepingcomputer.com /1 month ago

Brevo supply-chain attack injected ClickFix scripts on customer sites

Brevo confirmed that attackers stole a Cloudflare API key and used it to inject malicious ClickFix scripts into its websites and JavaScript files embedded on customer sites to dist...

Read source
dev.to /1 month ago

indexed-btree: npm Supply Chain Malware Executes at Runtime and Uses a Smart Contract on Ethereum Sepolia for C2

1. Basic Information Original Title: npm 'btree' Malware Campaign Affects Millions of Downloads, No Need for Install Script Source: Checkmarx Zero Publication Date: 2026-09-17 U...

Read source
gbhackers.com /2 weeks ago

GlassWorm Supply Chain Attack Hides Malware Inside VS Code Color Themes

A GlassWorm-linked software supply chain campaign has abused seemingly harmless Visual Studio Code color themes to distribute malicious loaders across the Visual Studio Marketplace...

Read source
bleepingcomputer.com /1 month ago

Artifactory flaws chained in attacks deploying backdoor malware

Threat actors are exploiting critical and high-severity vulnerabilities in JFrog Artifactory to bypass authentication, gain administrative privileges, and deploy a Rust backdoor on...

Read source
thehackernews.com /1 month ago

Attackers Chain Two PaperCut Flaws to Execute Code Without Authentication

Malicious actors are exploiting a newly patched security flaw in PaperCut NG and MF to execute arbitrary code on susceptible instances, as the company released a fresh emergency fi...

Read source
thehackernews.com /2 days ago

China-Linked Hackers Use ARTEX AI Agents in ConnectWise Supply Chain Attack

Microsoft on Wednesday disclosed that a China state-aligned actor dubbed Storm-0940 was behind the recent supply chain compromise of the ConnectWise Cloud Backup application. Duri...

Read source
bitcoinist.com /5 days ago

Ledger Reseller Attack Raises Questions About Hardware Wallet Supply Chains

A hardware wallet’s strongest cryptography offers little protection when an attacker can interfere with the device before its owner even switches it on. That is the uncomfortable l...

Read source
supplychaingamechanger.com /1 month ago

Cyber Security and the Digital Supply Chain!

When it comes to the modern supply chain managers have a relatively new risk to consider:  Cyber Security! As major logistics providers from all around the world struggle with kee...

Read source
gbhackers.com /1 month ago

Shai-Hulud Trinitite Worm Infects Popular TanStack Query npm Package to Steal Developer Secrets

A new Shai-Hulud supply-chain attack dubbed Trinitite has compromised the npm package @7nohe/openapi-react-query-codegen, a TanStack Query code-generation library with more than 15...

Read source
cloud.google.com /1 month ago

Proactive Defense: Hardening Code Pipelines and CI/CD Infrastructure

Introduction The landscape of software supply chain security has undergone a significant shift. Recent campaigns demonstrate that sophisticated threat actors are systematically tar...

Read source
arstechnica.com /1 month ago

An undercover Google analyst infiltrated a notorious supply-chain hacking gang

Google’s threat intelligence group said it had a mole inside TeamPCP's inner circle.

Read source

Turn fresh research into a full content calendar

Use SocialBu to discover ideas, generate post drafts, and schedule them across your social channels.

Sources covering Supply Chain Attack

bitcoinist.com

Recent coverage from public sources
Public source

feeds.arstechnica.com

Recent coverage from public sources
Public source

smartermsp.com

Recent coverage from public sources
Public source

cloudblog.withgoogle.com

Recent coverage from public sources
Public source

cybersecuritynews.com

Recent coverage from public sources
Public source

dev.to

Recent coverage from public sources
Public source