Latest updates for Malware

Fresh curated links around Malware are collected here so marketers can spot useful updates and turn timely ideas into posts faster.

Recent items include:

  • What Is Malware? Complete Guide to Types, Risks, Detection, Prevention & Removal | Hire Hacker
  • Low-cost Android phones ship with residential proxy malware
  • Low-Cost Android Phones Ship With Preinstalled Malware That Turns Them Into Residential Proxies

Post angles to try

Share the most useful takeaway for your audience.
Turn one article into a quick practical checklist.
Ask your audience how this shift affects their work.
Turn angles into scheduled posts

Fresh articles and ideas

Recent curated links from global sources. Generate one free draft from any story, then use SocialBu to schedule and refine your content calendar.

medium.com /4 weeks ago

What Is Malware? Complete Guide to Types, Risks, Detection, Prevention & Removal | Hire Hacker

Malware remains one of the most persistent and damaging threats in cybersecurity. Short for malicious software, malware refers to any…Continue reading on Medium »
Read source
bleepingcomputer.com /2 weeks ago

Low-cost Android phones ship with residential proxy malware

A malware campaign dubbed 'Midnight Mimosa' has been discovered on low-cost Android smartphones that ship with malicious software embedded in their firmware, allowing attackers to...

Read source
thehackernews.com /1 week ago

Low-Cost Android Phones Ship With Preinstalled Malware That Turns Them Into Residential Proxies

Low-cost Android smartphones have been shipped with malicious software baked into the device firmware, allowing bad actors to covertly install apps, conduct ad fraud, and turn devi...

Read source
inc.com /1 month ago

Researchers Just Discovered New Malware That Lets a Panel of LLMs Decide How to Attack

Malware is bad. Malware that uses AI to steal login credentials and crypto wallets is even worse.

Read source
gbhackers.com /1 week ago

Android Firmware Malware Uses Ad Fraud and Proxy Botnets to Generate Revenue

Midnight Mimosa, an Android malware campaign embedded in firmware that monetizes compromised smartphones through advertising fraud and residential proxy services. Disclosed on Octo...

Read source
gbhackers.com /4 days ago

Hackers Turn Low-Cost Android Phones Into Hidden Proxy Botnets Through Preinstalled Malware

Midnight Mimosa, a widespread Android malware campaign, is turning inexpensive smartphones into advertising fraud engines and potential residential proxy nodes by embedding malicio...

Read source
cnet.com /1 month ago

Say Hello to RatHat, a New AI-Powered Malware Invading the Android Ecosystem

The malware pretends to be a legitimate download for an app like Google Chrome.

Read source
gbhackers.com /1 month ago

Rogue ScreenConnect Clients Spread Worm-Like Malware Across Connected Windows Systems

A malicious ScreenConnect campaign in which rogue remote-access clients do more than provide attackers with hands-on control: modified clients can automatically push a multi-stage...

Read source
thehackernews.com /1 month ago

F5 BIG-IP APM Malware Injects a PHP Web Shell Into Memory, Evading Disk Scans

Malware linked to break-ins at F5 BIG-IP Access Policy Manager appliances hides a PHP web shell in memory instead of in a file on disk, Sophos said in an analysis published on Sept...

Read source
cybersecuritynews.com /1 month ago

A Fake Streaming App Turned Android Phones Into Remote-Controlled Devices

A free television offer led Android users to a dangerous download. Ads for a streaming service urged them to install an app that could give criminals control of their phones, rathe...

Read source
theblaze.com /1 month ago

New malware is crippling Android phones, but not yours if you do this

Android users beware! A new version of a tried-and-true malware is out in the wild, and its latest capabilities make it dangerous not just to rooted devices, but it can attack run-...

Read source
bleepingcomputer.com /1 month ago

New Android malware encrypts files, steals data, and harasses victims

A new Android malware strain called Mantax Otax combines ransomware and spyware capabilities to encrypt files, steal sensitive data, and spam and harass victims. [...]

Read source
gbhackers.com /1 month ago

Researchers Uncover 10,000+ Malware Loaders Behind YouTube and SEO Poisoning Campaign

A long-running pay-per-install (PPI) operation that used YouTube gaming channels and SEO-poisoned software downloads to distribute malware at scale. The cluster, tracked as CL-CRI-...

Read source
infosecurity-magazine.com /1 month ago

MantaxOtax Android Malware Combines Ransomware With Spyware

MantaxOtax Android malware combines ransomware with extensive spyware capabilities

Read source
cybersecuritynews.com /1 month ago

Hackers Poison Movie Torrents With MovieReaper Malware That Uses Solana for C2

Movie torrents are being used to deliver a new Windows malware framework called MovieReaper. Attackers have poisoned torrent downloads for popular films, turning a routine search f...

Read source
gbhackers.com /2 weeks ago

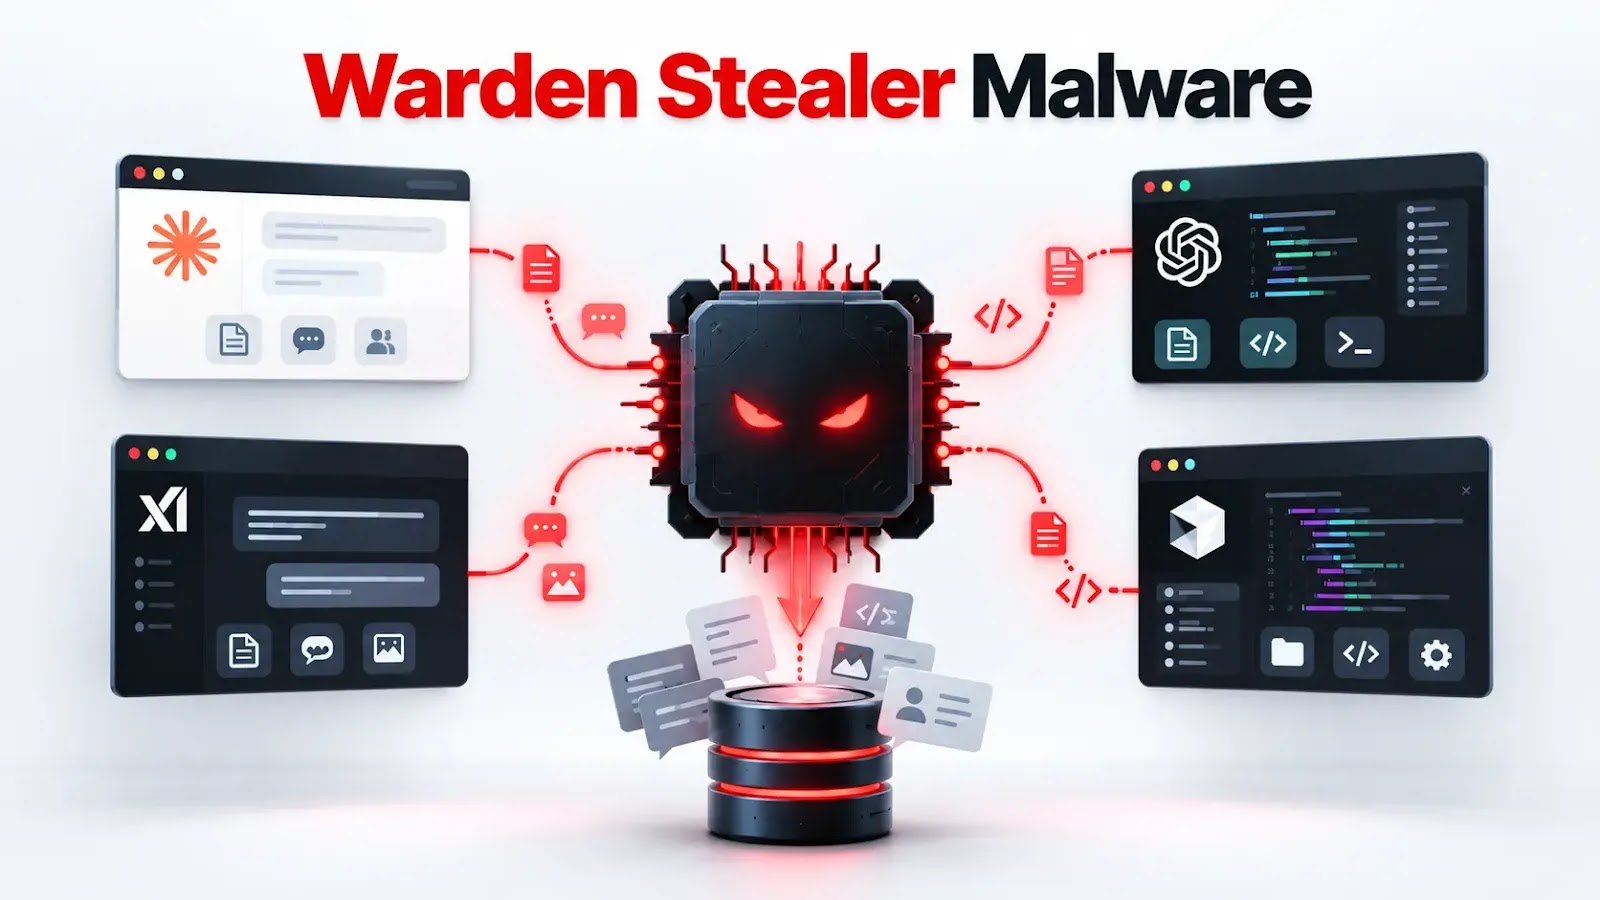
Warden Stealer Malware Targets Claude, Codex, Grok and Cursor to Steal AI Agent Data

Warden Stealer as a rapidly growing malware-as-a-service operation targeting data stored by AI assistants and coding agents, including Claude, Codex, Grok, and Cursor. The Rust-bas...

Read source
gbhackers.com /9 hours ago

Hackers Use Fake Chocolatey and Microsoft Activation Websites to Spread New Armorsteal Malware

Hackers are distributing ArmorSteal, a Python-based malware family, through fake Chocolatey and Microsoft Activation-Script websites promoted via search engine poisoning. The malwa...

Read source
tekno.sindonews.com /1 week ago

Malware Ditemukan Terpasang di Ribuan Ponsel Android Murah

Sebuah aplikasi aneh ditemukan yang secara otomatis mengunduh dan menghapus perangkat lunak di ribuan perangkat Android.

Read source
infosecurity-magazine.com /1 week ago

ROMULUS Malware Server Leverages ClickFix to Deliver Multiple Payloads

Researchers at Forescout said the discovery shows how ClickFix is evolving from a delivery technique into full-blown cyber-criminal infrastructure

Read source
gbhackers.com /1 week ago

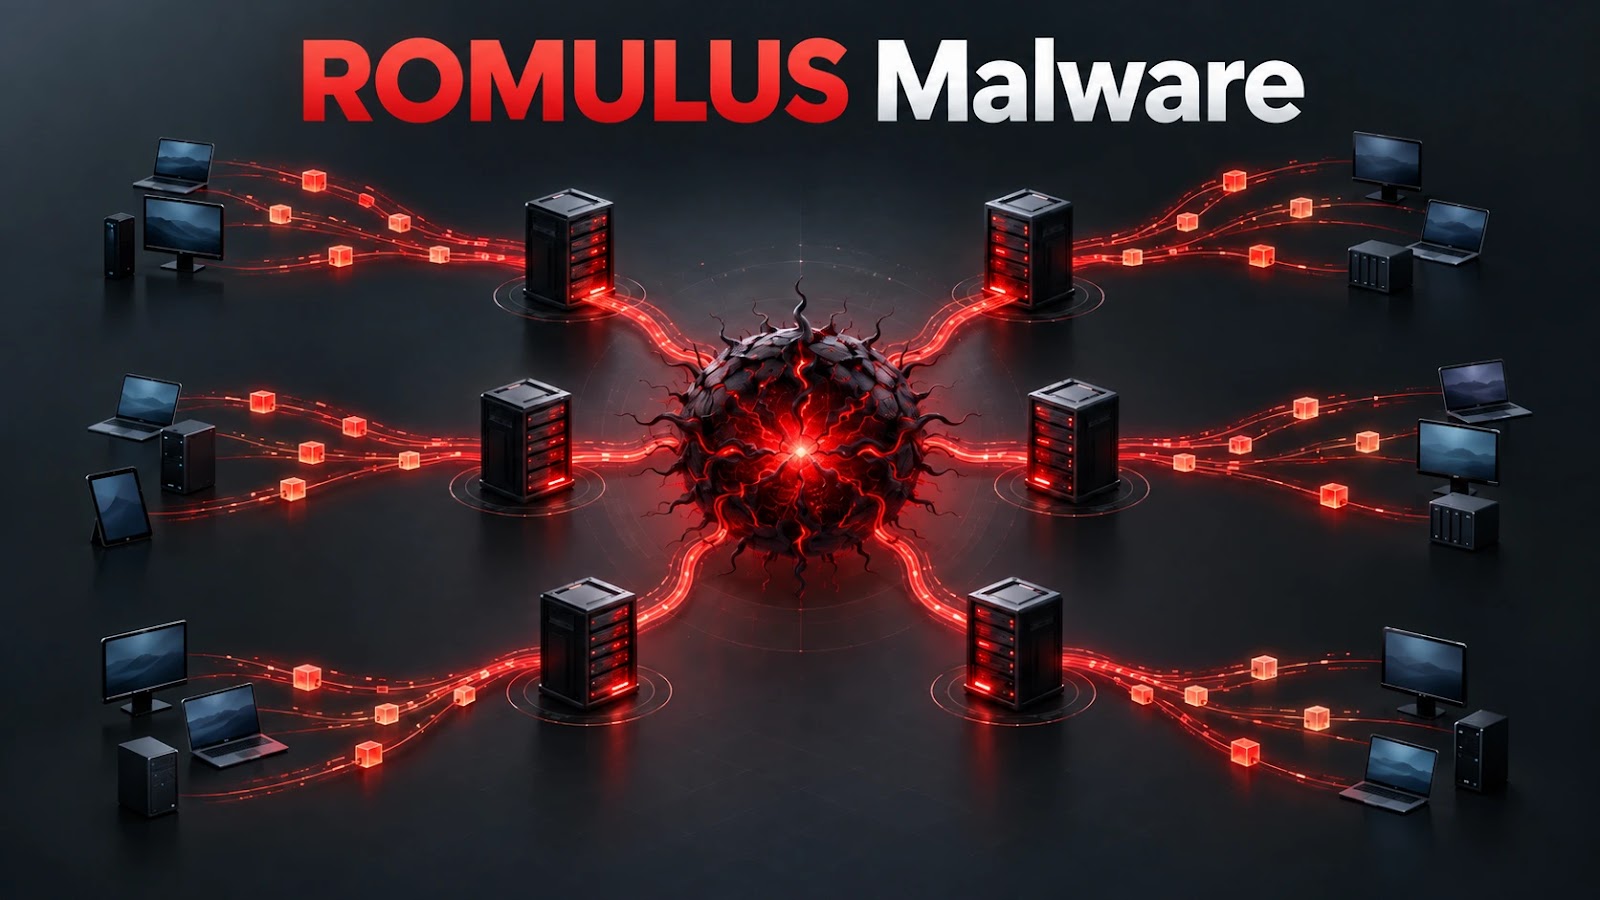
New ROMULUS Malware Platform Uses Six Servers to Deliver Multiple Malicious Payloads

ROMULUS, a shared ClickFix delivery platform operating across six identified servers, with confirmed routes distributing a trojanized Stardock package and LegionLoader. The discove...

Read source
cybersecuritynews.com /3 weeks ago

SilverFox Hackers Built Fake Software Sites That Hide Malware From Security Researchers

Fake software download pages are drawing Windows users into a Silver Fox-linked malware campaign. The pages imitate familiar vendors and supply installers that can leave an infecte...

Read source
thehackernews.com /3 weeks ago

Hackers Use NeedyMantis to Maintain Long-Term Access in Breached Networks

Hackers have used a malware family called NeedyMantis to maintain long-term access to networks they had already breached, Microsoft said in a technical analysis. The malware has b...

Read source
itmedia.co.jp /1 month ago

PayPay、身に覚えのない送金に注意 マルウェア感染で遠隔操作リスク

不審なSMSやメール、SNS上の広告に記載されたリンクからアプリをインストールしたことで感染し、不正に操作される事例を確認したという。

Read source
foxnews.com /1 month ago

Thousands of hacked sites trick you into installing malware

Over 5,400 legitimate websites now serve fake CAPTCHA scams that trick users into pasting malware commands into Windows Run via ClickFix attacks.

Read source

Turn fresh research into a full content calendar

Use SocialBu to discover ideas, generate post drafts, and schedule them across your social channels.

Sources covering Malware

feeds.foxnews.com

Recent coverage from public sources
Public source

cybersecuritynews.com

Recent coverage from public sources
Public source

feeds.feedburner.com

Recent coverage from public sources
Public source

gbhackers.com

Recent coverage from public sources
Public source

medium.com

Recent coverage from public sources
Public source

rss.itmedia.co.jp

Recent coverage from public sources
Public source