Latest updates for Devsecops

Fresh curated links around DevSecOps are collected here so marketers can spot useful updates and turn timely ideas into posts faster.

Recent items include:

  • Secure Application Development: Building Speed, Compliance, and Control into Every Release
  • Proactive Defense: Hardening Code Pipelines and CI/CD Infrastructure
  • Pipelines on Fire: Why Your CI/CD Tools Are the New Cyber Battlefield

Post angles to try

Share the most useful takeaway for your audience.
Turn one article into a quick practical checklist.
Ask your audience how this shift affects their work.
Turn angles into scheduled posts

Fresh articles and ideas

Recent curated links from global sources. Generate one free draft from any story, then use SocialBu to schedule and refine your content calendar.

testingxperts.com /1 month ago

Secure Application Development: Building Speed, Compliance, and Control into Every Release

Secure application development should support innovation without weakening compliance or enterprise control. This blog explains how risk-tiered governance, DevSecOps evidence, cont...

Read source
cloud.google.com /1 month ago

Proactive Defense: Hardening Code Pipelines and CI/CD Infrastructure

Introduction The landscape of software supply chain security has undergone a significant shift. Recent campaigns demonstrate that sophisticated threat actors are systematically tar...

Read source
dzone.com /1 month ago

Pipelines on Fire: Why Your CI/CD Tools Are the New Cyber Battlefield

Fifteen years in, and the conversation I have most often with security leads still starts the same way: how's your perimeter, how's your endpoint coverage, how's your SOC staffed?...

Read source
aws.amazon.com /1 week ago

Penetration testing every deployment with AWS Continuum

Most security tooling that fits into a CI/CD pipeline—static analysis (SAST), software composition analysis (SCA), and dynamic scanners (DAST)—flags potential issues from patterns...

Read source
dzone.com /3 weeks ago

Your Cloud Diagram Is Already Out of Date: An Operating Model for Continuous Security Architecture

The Diagram-to-Deployment Gap Cloud security architecture often begins with a strong design, account boundaries are defined, identity federation and vending patterns are selected,...

Read source
blogs.cisco.com /1 week ago

Always-On Assurance: How Cisco is Reimagining the Secure Development Lifecycle

Learn how Cisco’s Secure Development Lifecycle (CSDL) is evolving to support AI-driven development, ensuring secure and resilient software at speed.

Read source
salesforce.com /1 week ago

Managing Agentic Security at Scale

On the code we scan at depth, the volume of findings is now the constraint: frontier models plus an agentic harness surface more real, exploitable findings than engineering can abs...

Read source
dzone.com /1 month ago

Why Continuous Application Security Testing Is No Longer Optional

Your last pentest is already out of date. The moment you shipped new code after that report, your risk profile changed, and nobody re-tested it.  That's the reality most teams are...

Read source
cloud.google.com /3 weeks ago

Defending at machine speed: Securing the public sector in the agentic era

Over the last three decades in cybersecurity, I’ve witnessed major paradigm shifts — yet none match the velocity and complexity of today’s landscape. Attackers are now using AI to...

Read source
thehackernews.com /3 weeks ago

How Financial Services Companies Can Modernize Their Software Supply Chain

Every security leader at a bank, insurer, or asset manager has had a version of this conversation: Security wants to eliminate a class of vulnerabilities. Engineering explains what...

Read source
uploadarticle.com /1 month ago

Best Veracode Alternatives for Modern AppSec Teams

Application security has changed dramatically over the last few years. Development teams are releasing code... The post Best Veracode Alternatives for Modern AppSec Teams appeared...

Read source
projectmanagertemplate.com /1 month ago

Automatic Backup for DevOps: 7 Best Practices for Securing Your SDLC

In this article, we describe 7 best practices for SDLC backup automation that will bring your DevOps security to a whole new level.

Read source
ecpi.edu /1 week ago

Secure Coding Practices Using AI Tools

Secure Coding Practices Using AI Tools Anonymous (not verified) Wed, 10/14/2026 - 17:46 SDC315 315 SDC SDC315 Secure Coding Practices Using AI...

Read source
thehackernews.com /4 days ago

What Security Teams Can Do To Tame Wild Code

A sales manager builds an AI-assisted workflow to route leads. It connects to customer records, summarizes inbound requests, and posts updates to a shared channel. The workflow sav...

Read source
databricks.com /1 month ago

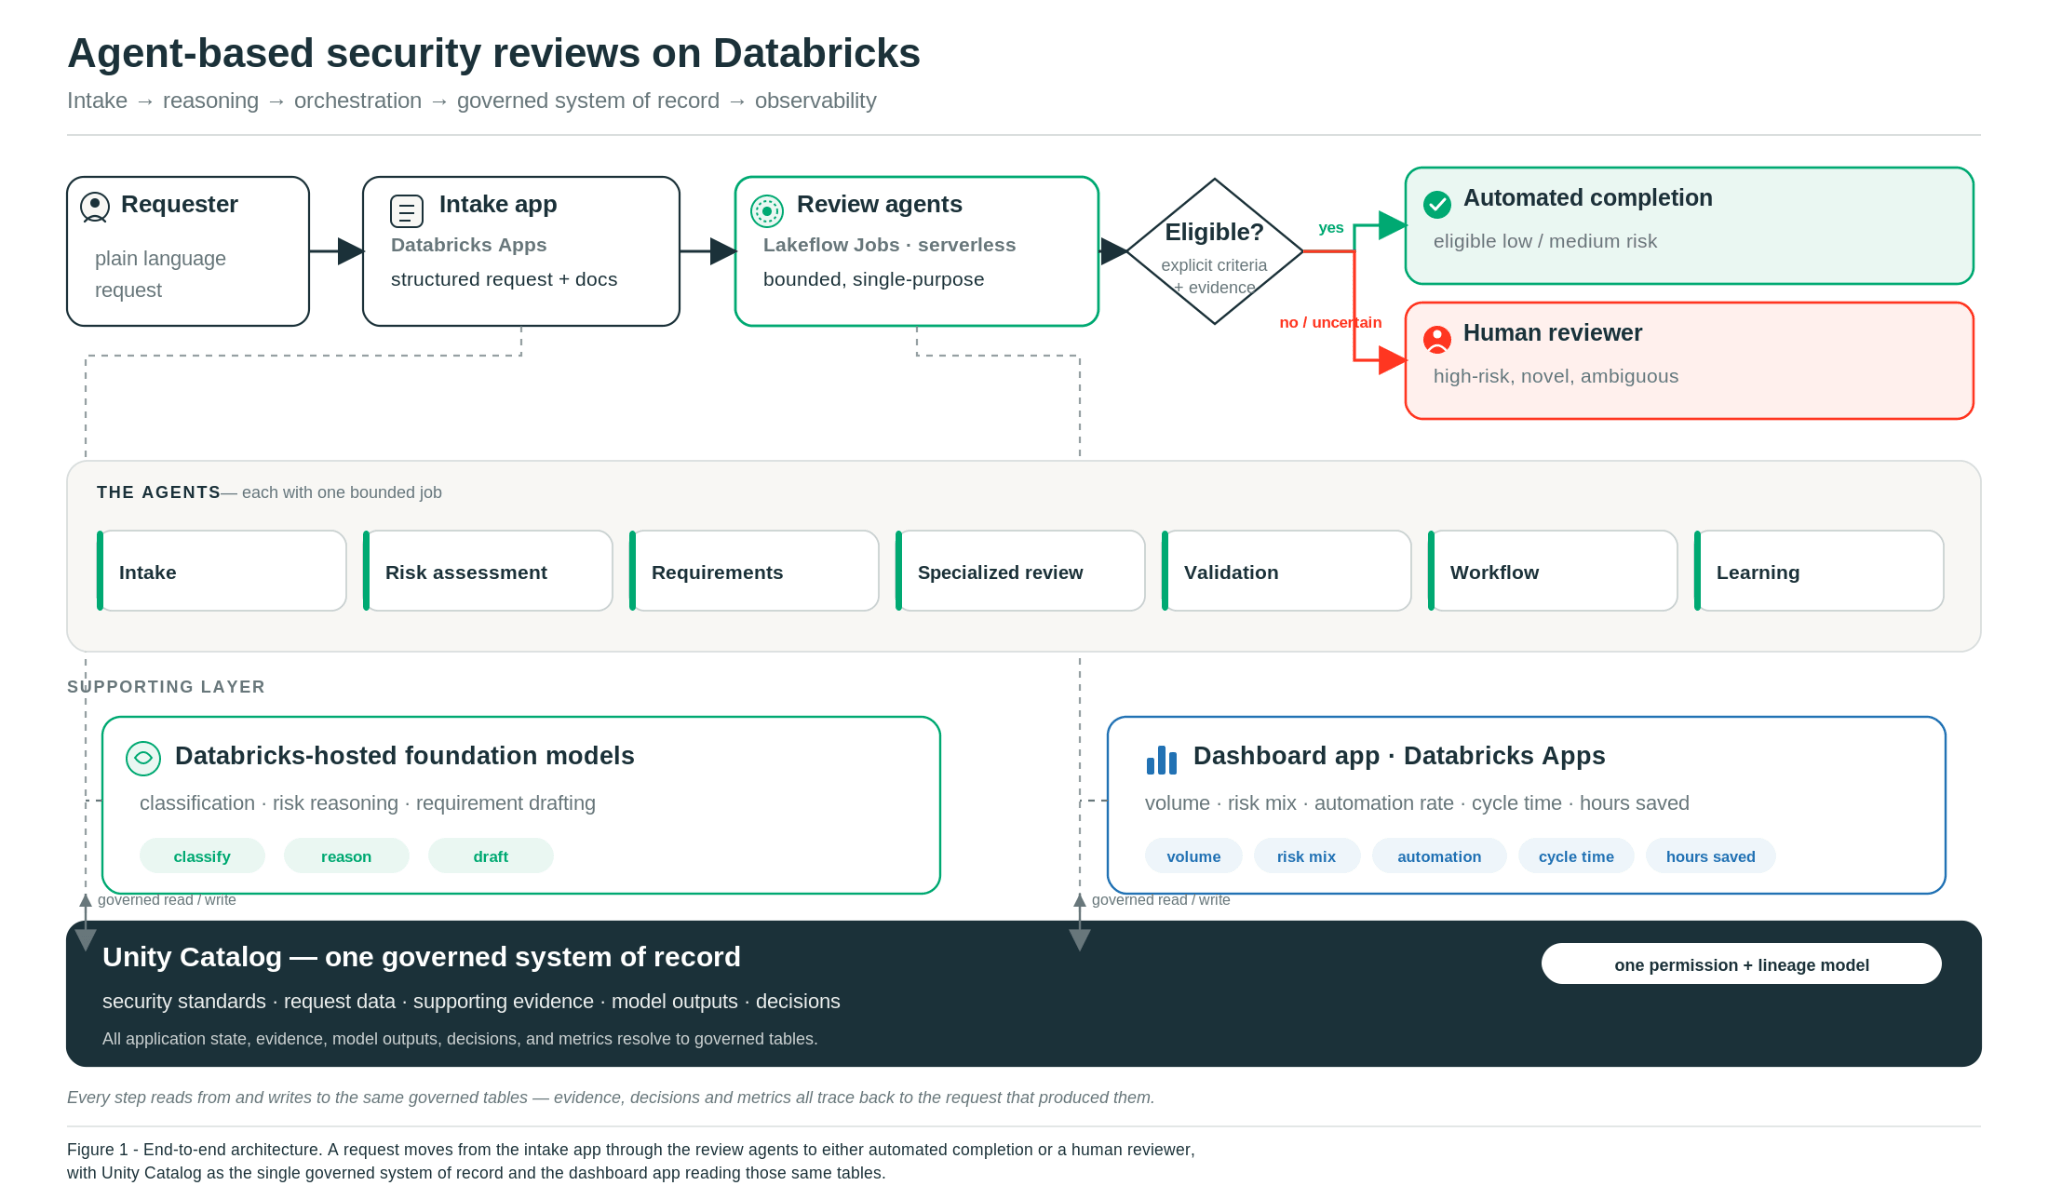
How I built agent-based security reviews on Databricks

We already had automation in parts of our security review process. It was useful,...

Read source
dzone.com /3 weeks ago

Detection and Response Did Its Job. Now Someone Has to Actually Fix It.

A host is isolated. A malicious process is killed. A compromised credential is revoked before an attacker can use it again. Detection and response worked exactly as intended, autom...

Read source
sdtimes.com /1 month ago

JFrog Delivers DevGovOps at Scale: Continuous Compliance for the AI-Era Software Supply Chain 

At its SwampIUP 2026 event in New York City, JFrog has unveiled DevGovOps for the AI-era – a new class of capabilities in JFrog AppTrust that automates governance across the softwa...

Read source
cm-alliance.com /4 days ago

Custom IT Services and Cybersecurity: Secure-by-Design Systems

Most companies start with generic IT. A managed service provider handles laptops, email and antivirus. A stack of SaaS subscriptions covers core functions. Someone internal becomes...

Read source
weworkremotely.com /2 weeks ago

Vercel: Security Software Engineer, IAM

Headquarters: Remote - United States About Vercel: Vercel is the agentic infrastructure company, freeing people and agents to ship what's next. For more than a decade we've helpe...

Read source
blogs.vmware.com /2 weeks ago

Mastering Cybersecurity with VMware vDefend and Avi via Hands-on Labs

<div><img width="300" height="136" src="https://blogs.vmware.com/wp-content/uploads/2026/10/HOL-banner.png" class="attachment-medium siz...

Read source
computerra.ru /1 month ago

Код быстрее, проверок больше: как ИИ меняет DevSecOps

Источник: Компьютерра - Журнал о науке и технологиях По данным исследования «Солара» и УЦСБ, 82% организаций уже используют ИИ для разработки ПО. Вайбкодинг ускоряет создание прил...

Read source
qualitydigest.com /1 month ago

AI-Driven Development Is Outpacing Traditional Application Security

AI-Driven Development Is Outpacing Traditional Application Security Report from Info-Tech Research Group Mark Hembree Wed, 08/26/2026 - 12:02 Off...

Read source
dev.to /1 month ago

AI Tools for Security Vulnerability Detection: 2026 Guide

Originally published at nlocoding.com 81%of critical vulnerabilities exploited in 2025 had known fixes available for over 60 days. (CISA, 2026) Software doesn’t get hacked bec...

Read source
dzone.com /1 week ago

AI-Era Cybersecurity, Part 2: Building the System Context, Governance and Agent Identity

Part 1 of this series walked through why AI has compressed the gap between a vulnerability's disclosure and its exploitation from months to hours, laid out the lifecycle every vuln...

Read source

Turn fresh research into a full content calendar

Use SocialBu to discover ideas, generate post drafts, and schedule them across your social channels.

Sources covering Devsecops

feeds.dzone.com

Recent coverage from public sources
Public source

aws.amazon.com

Recent coverage from public sources
Public source

blogs.cisco.com

Recent coverage from public sources
Public source

blogs.vmware.com

Recent coverage from public sources
Public source

cloudblog.withgoogle.com

Recent coverage from public sources
Public source

dev.to

Recent coverage from public sources
Public source