Latest updates for Cryptolocker

Fresh curated links around Cryptolocker are collected here so marketers can spot useful updates and turn timely ideas into posts faster.

Recent items include:

  • Tech Time Warp: Cryptolocker spreads fast and at great cost
  • One encryption tool can lock down 10GB in 35 seconds, and a lifetime subscription is only $40
  • Ransomware gang allegedly raids The Money Store, two class actions follow

Post angles to try

Share the most useful takeaway for your audience.
Turn one article into a quick practical checklist.
Ask your audience how this shift affects their work.
Turn angles into scheduled posts

Fresh articles and ideas

Recent curated links from global sources. Generate one free draft from any story, then use SocialBu to schedule and refine your content calendar.

smartermsp.com /1 month ago

Tech Time Warp: Cryptolocker spreads fast and at great cost

Thirteen years ago, computer users in the United States were returning to the office after the long Labor Day weekend when reports began surfacing of a new virus: Cryptolocker. The...

Read source
mashable.com /3 weeks ago

One encryption tool can lock down 10GB in 35 seconds, and a lifetime subscription is only $40

EncryptPro encrypts Windows files locally with AES-256, shares them over private PGP connections, and opens large files instantly. Now $39.99 for life.

Read source
mpamag.com /1 week ago

Ransomware gang allegedly raids The Money Store, two class actions follow

Loan applications, Social Security numbers, mortgage docs - all allegedly stolen

Read source
theregister.com /2 weeks ago

Ransomware fixer claimed he could decrypt files, allegedly defrauded clients instead

Feds claim he charged clients more than ransoms, paid up, pocketed the difference

Read source
cybersecuritynews.com /1 month ago

New SETTRA Ransomware Uses MeshAgent RMM and BYOVD to Encrypt Windows Systems

Settra ransomware is emerging as a serious threat to Windows networks after investigators linked it to two recent intrusions involving remote-management software and recovery-block...

Read source
infosecurity-magazine.com /1 month ago

Emerging Ransomware Gang Uses Backup Destruction Threats to Pressure Victims

Ransom notes by n0n ransomware claim to take double extortion to a new level of danger for victims

Read source
gbhackers.com /1 month ago

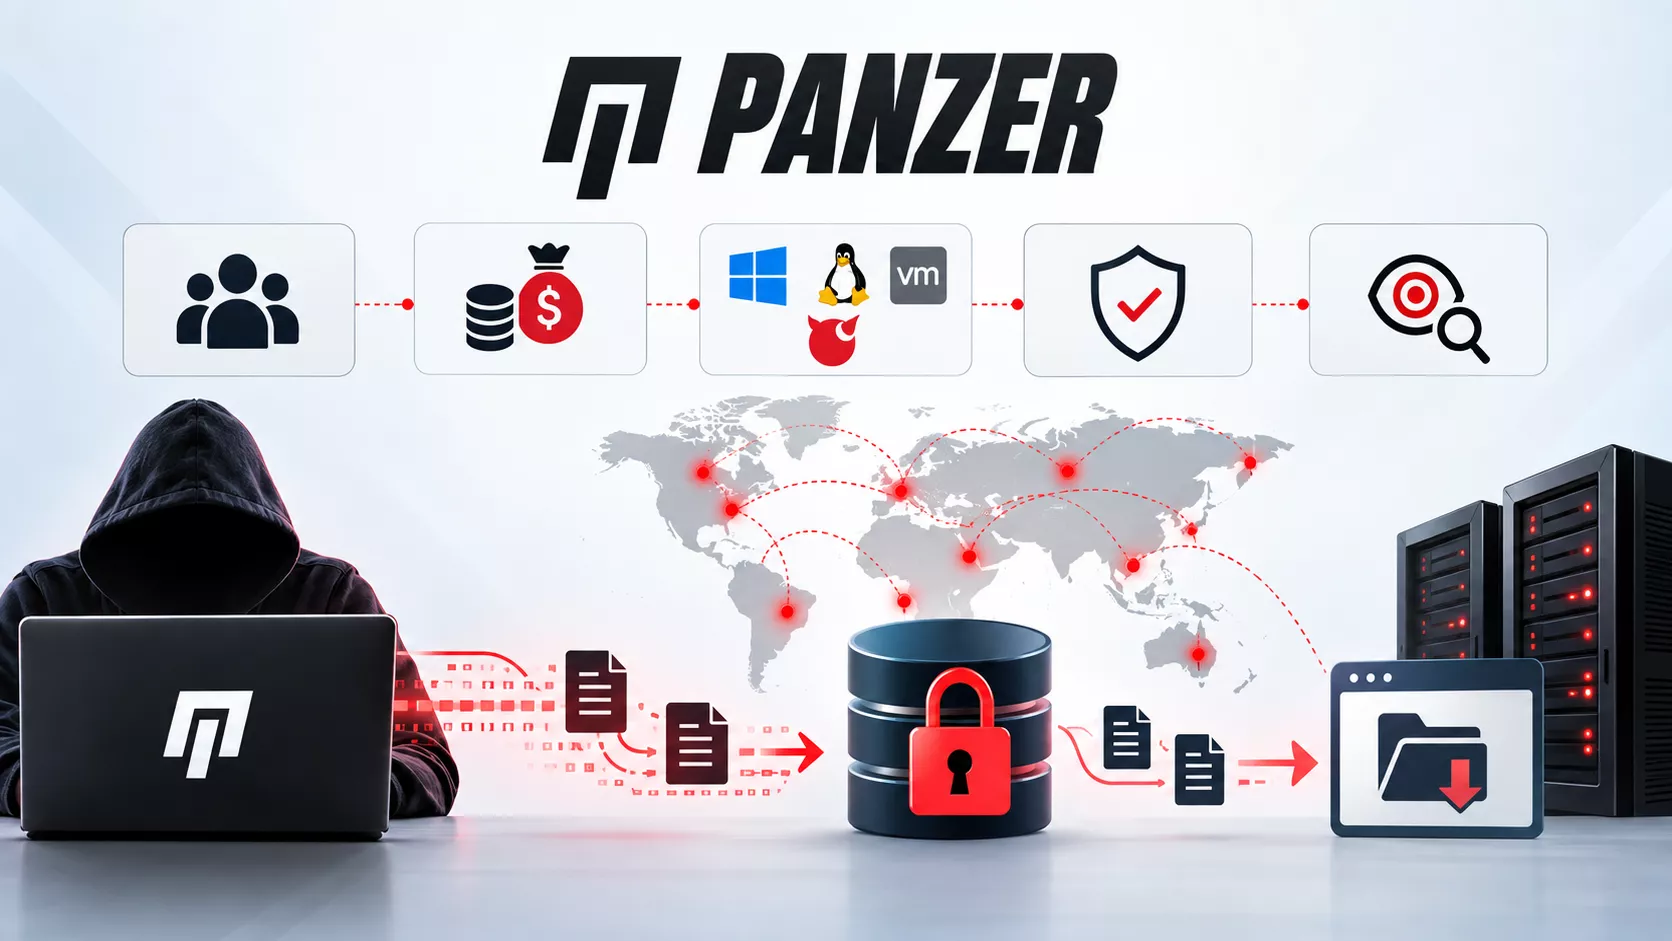
New Panzer Ransomware Hits 16 Victims Across 11 Countries With Data Theft and Encryption

Panzer ransomware has emerged as a new Ransomware-as-a-Service (RaaS) operation, publishing 16 alleged victims across 11 countries while combining data theft with file encryption....

Read source
gbhackers.com /1 month ago

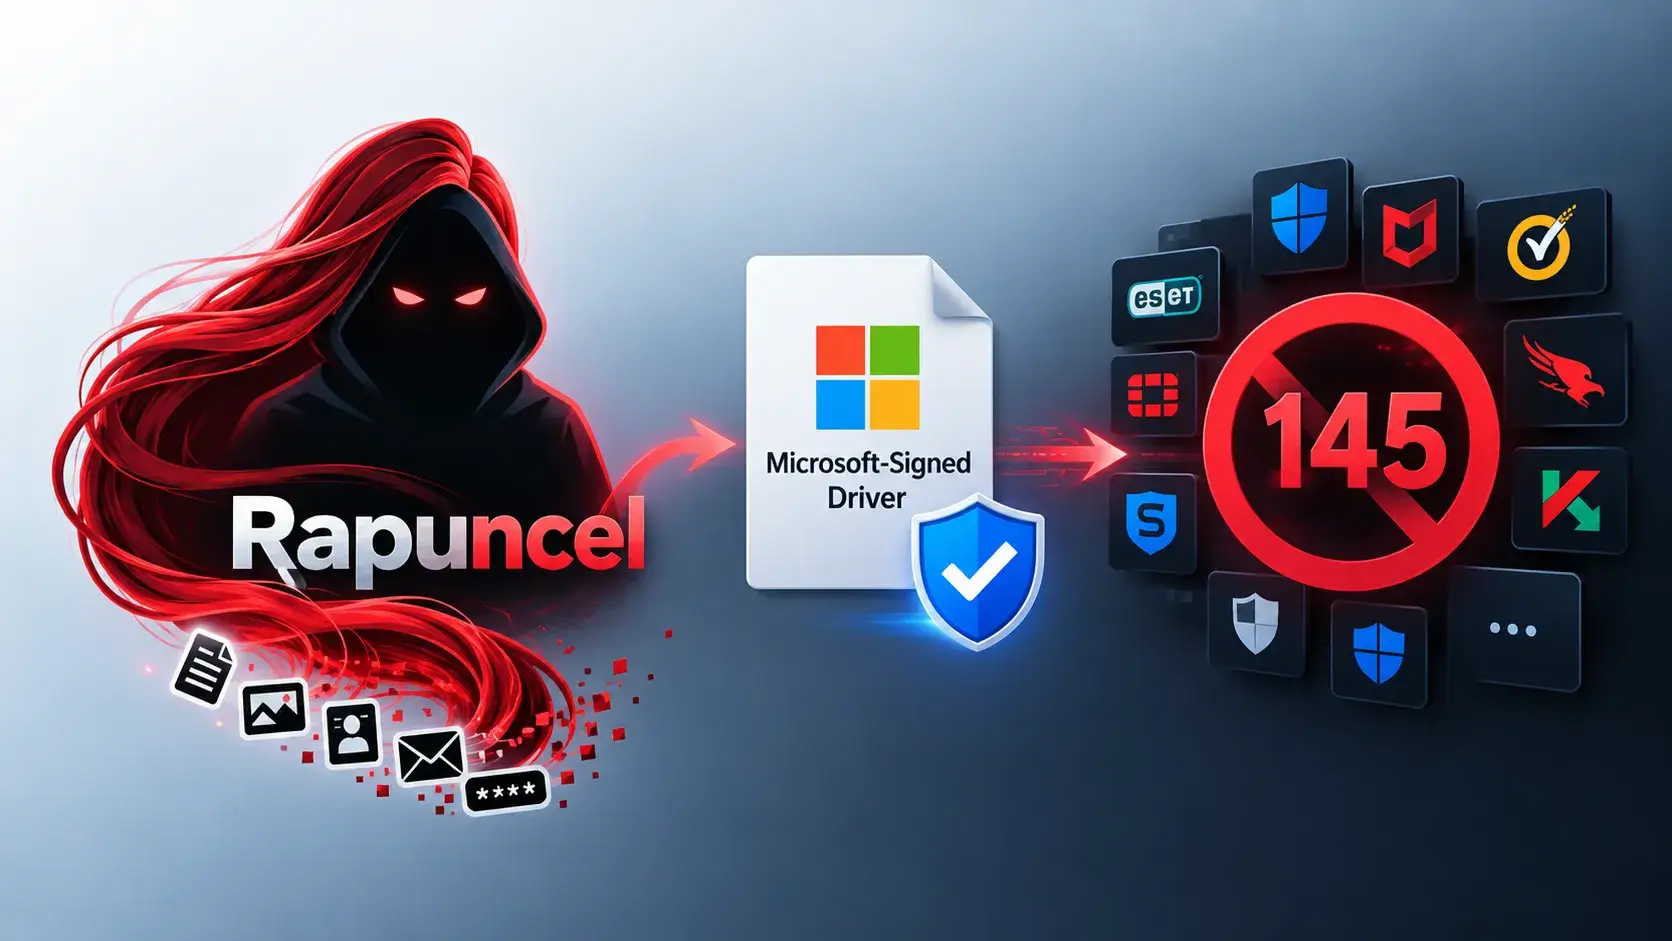
New Rapuncel Infostealer Abuses Microsoft-Signed Driver to Disable 145 Security Tools

A newly identified information-stealing campaign, tracked as Rapuncel, is exploiting a Microsoft-attested kernel driver to terminate up to 145 antivirus (AV) and endpoint detection...

Read source
cofense.com /1 month ago

From Payment Plan to Ransomware - Inside a Global Group Attack

The Cofense Phishing Defense Center (PDC) team has recently investigated a newly emerged Ransomware-as-a-Service (RaaS) operation organized by the Global Group, a financially motiv...

Read source
thehackernews.com /2 weeks ago

MonsterCloud Owner Accused of Billing Over $19M While Secretly Paying Ransoms to Decrypt Data

The U.S. Department of Justice (DoJ) on Wednesday announced charges against a 50-year-old U.S. and Israeli national for allegedly defrauding ransomware victims by secretly paying t...

Read source
gbhackers.com /1 month ago

Feral Wolf Hackers Exploit Confluence and 1C to Deploy GenieLocker Ransomware

Feral Wolf has expanded its ransomware tradecraft by abusing exposed Atlassian Confluence servers and insecure 1C:Enterprise deployments to gain access to Russian corporate network...

Read source
gbhackers.com /1 month ago

New SETTRA Ransomware Uses MeshAgent RMM and BYOVD to Encrypt Windows Systems

A newly observed ransomware operation dubbed SETTRA is abusing the legitimate MeshAgent remote monitoring and management platform for persistence while using recovery-inhibition an...

Read source
cybersecuritynews.com /3 days ago

Hackers Use Gentlemen Ransomware to Disable Windows Defender and Destroy Backups

A ransomware operation known as The Gentlemen is using a mix of security tampering, service disruption and file encryption to make recovery harder for affected organizations. Its W...

Read source
bleepingcomputer.com /2 weeks ago

Ransomware has a new target. Is your backup ready?

Ransomware groups are increasingly targeting backup infrastructure to eliminate recovery options and increase pressure on victims to pay. Kaseya explains why organizations need iso...

Read source
freelancer.com /2 days ago

Decrypt LockBit 3.0 SQL Files

My Microsoft SQL Server data files were locked during a recent LockBit 3.0 (Black) incident and I need them brought back to a usable state. I already have the official decryptor an...

Read source
bleepingcomputer.com /1 month ago

New Android malware encrypts files, steals data, and harasses victims

A new Android malware strain called Mantax Otax combines ransomware and spyware capabilities to encrypt files, steal sensitive data, and spam and harass victims. [...]

Read source
legaltechdaily.com /2 weeks ago

MonsterCloud indictment exposes the ransom payment a victim’s own file may not record

Editor’s Note: Zohar Pinhasi, owner of Florida ransomware-recovery firm MonsterCloud, was arraigned Oct. 7 in Brooklyn on federal charges that he told clients he had proprietary de...

Read source
cybersecuritynews.com /4 weeks ago

Sauron Loader Malware Uses DLL Side-Loading and In-Memory Decryption to Evade Detection

Sauron Loader has surfaced in attacks on German organizations, giving intruders a way to deliver more malware. The new tool need not be the first thing a victim encounters. In the...

Read source
ubergizmo.com /1 month ago

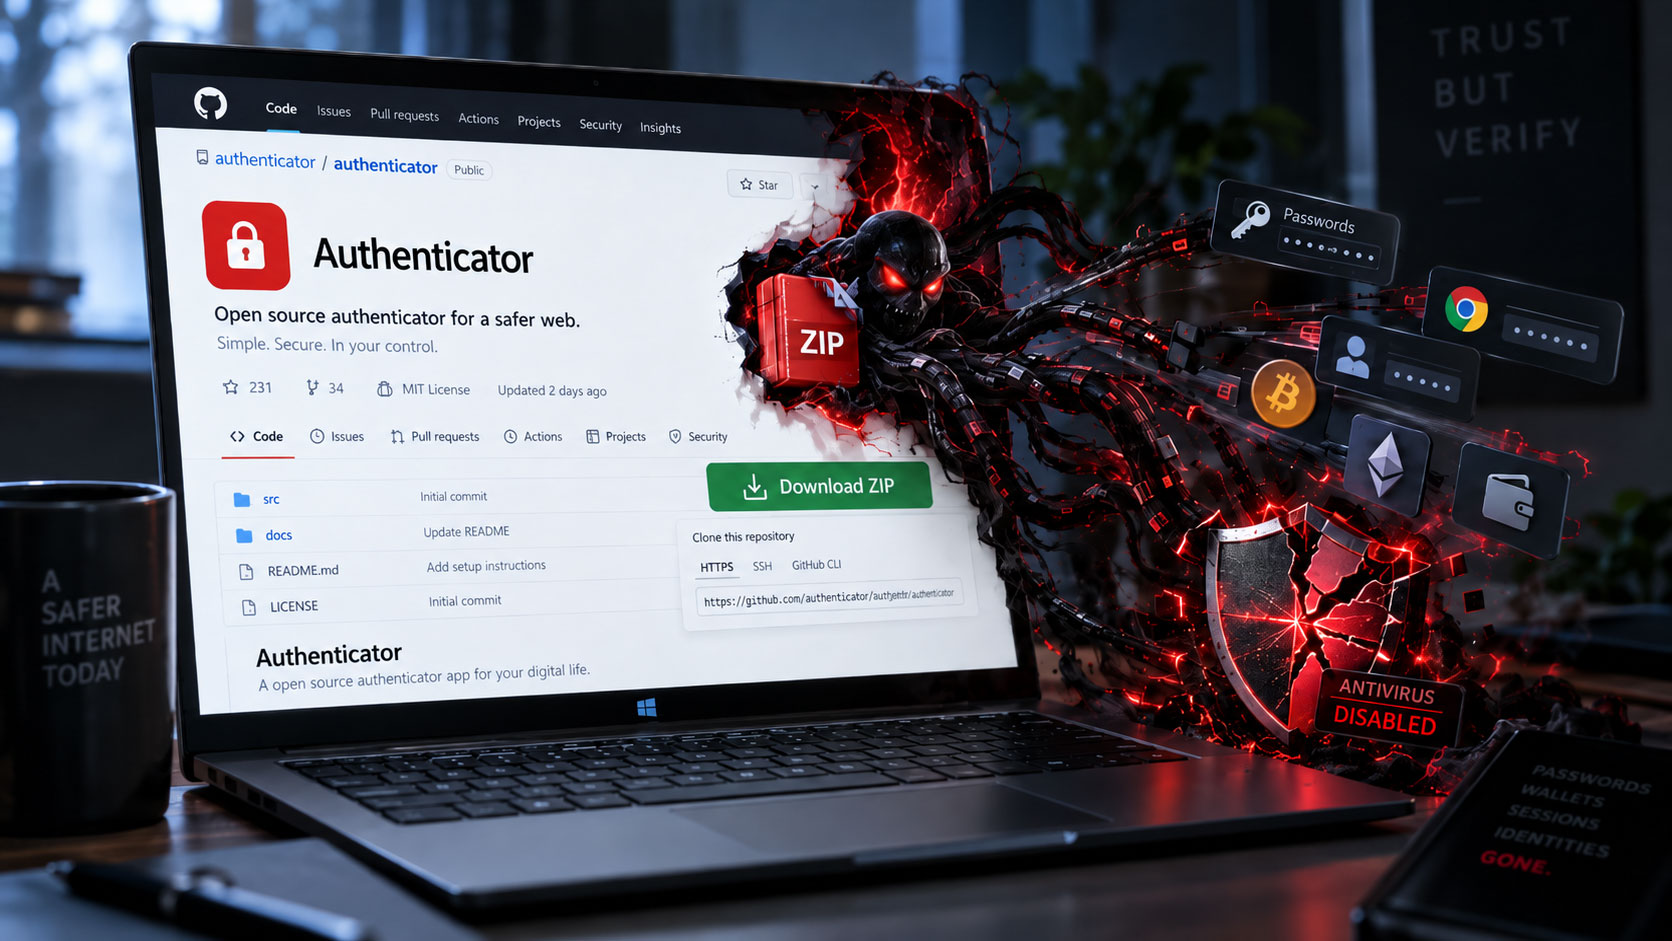
Fake LastPass Authenticator Can Kill Your Antivirus. Take This Action

AI Image, for illustration purposes If you searched for “LastPass Authenticator download” and landed on a shiny GitHub page with LastPass branding and fake “VirusTotal Approved” ba...

Read source
bleepingcomputer.com /1 month ago

Fake LastPass Authenticator GitHub repos push new Rapuncel infostealer

 An ongoing malware campaign uses SEO-optimized GitHub repositories to impersonate well-known software firms to push a previously undocumented information stealer called Rapuncel....

Read source
theregister.com /1 month ago

Swiss court sentences 52-year-old Ukrainian ransomware dev to nearly 13 years in the cooler

The man allegedly wrote the code that powered the Lockergoga, MegaCortex, and Nefilim operations

Read source
thehackernews.com /1 month ago

Four REVSTEALER-Linked Modules Disable Windows Update and Defender to Run a Crypto Miner

Elastic Security Labs has documented four previously unreported programs associated with REVSTEALER, an emerging Windows information stealer, that remain on an infected machine aft...

Read source
gizmodo.com /2 weeks ago

Feds Say Ransomware Expert’s Miracle Cure Was Just Paying the Hackers

An indictment says Zohar Pinhasi's MonsterCloud billed ransomware victims millions for a decryptor it did not have, then paid the attackers a fraction of that fee.

Read source
bleepingcomputer.com /1 week ago

Inside AvisLoader: A Windows Malware Loader Built to Resist Disruption

A new Windows malware loader called AvisLoader uses encrypted peer-to-peer communications to make command-and-control infrastructure harder to disrupt. Varonis researchers explain...

Read source

Turn fresh research into a full content calendar

Use SocialBu to discover ideas, generate post drafts, and schedule them across your social channels.

Sources covering Cryptolocker

smartermsp.com

Recent coverage from public sources
Public source

cofense.com

Recent coverage from public sources
Public source

cybersecuritynews.com

Recent coverage from public sources
Public source

feeds.feedburner.com

Recent coverage from public sources
Public source

feeds.feedburner.com

Recent coverage from public sources
Public source

gbhackers.com

Recent coverage from public sources
Public source