Vulnerabilities: Everything You’ve Wanted To Know
<div><img width="300" height="150" src="https://blogs.vmware.com/wp-content/uploads/2026/10/cybersecurity-awareness-banner-1200x600-1.png" cl...
Adversaries today are weaponizing vulnerabilities even before patches are released. According to Qualys’s 2026 report on vulnerabilities, drawn from over one billion remediation re...
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Friday added two security flaws impacting Ivanti Connect Secure (ICS) to its Known Exploited Vulnerabilities (KE...
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Friday added four flaws impacting Apache Roller, Cisco Expressway, SAP NetWeaver, and Broadcom VMware vCenter to...
Anthropic's Jason Clinton warned of a vulnerability tsunami. October 2026 brought PHP, eMudhra, Railway and Node.js incidents. What PR teams should watch next.
AI-discovered vulnerabilities are more likely to enable RCE, as disclosures and exploitation rise
Attackers exploited critical AI-identified PHP vulnerabilities before the fixes were publicly released. On August 11, 2026, researchers from OpenAI privately reported critical secu...
This summer delivered one record-breaking Patch Tuesday after another. First was July, when Microsoft issued its then-largest single month release to date (covering 600+ CVEs, trip...
The window between vulnerability disclosure and active exploitation continues to shrink. About one-third (28.3%) of exploited vulnerabilities are weaponized within 24 hours of disc...
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) Tuesday added two security flaws impacting Cisco BroadWorks and Openwave Messaging Webtop Media Transcoder to its K...
Microsoft’s analysis of approximately 383,000 disclosed vulnerabilities shows that attackers overwhelmingly favor weaknesses enabling system takeover rather than exploiting vulnera...
Five critical NGINX vulnerabilities could allow unauthenticated attackers to remotely execute code and potentially take control of affected servers
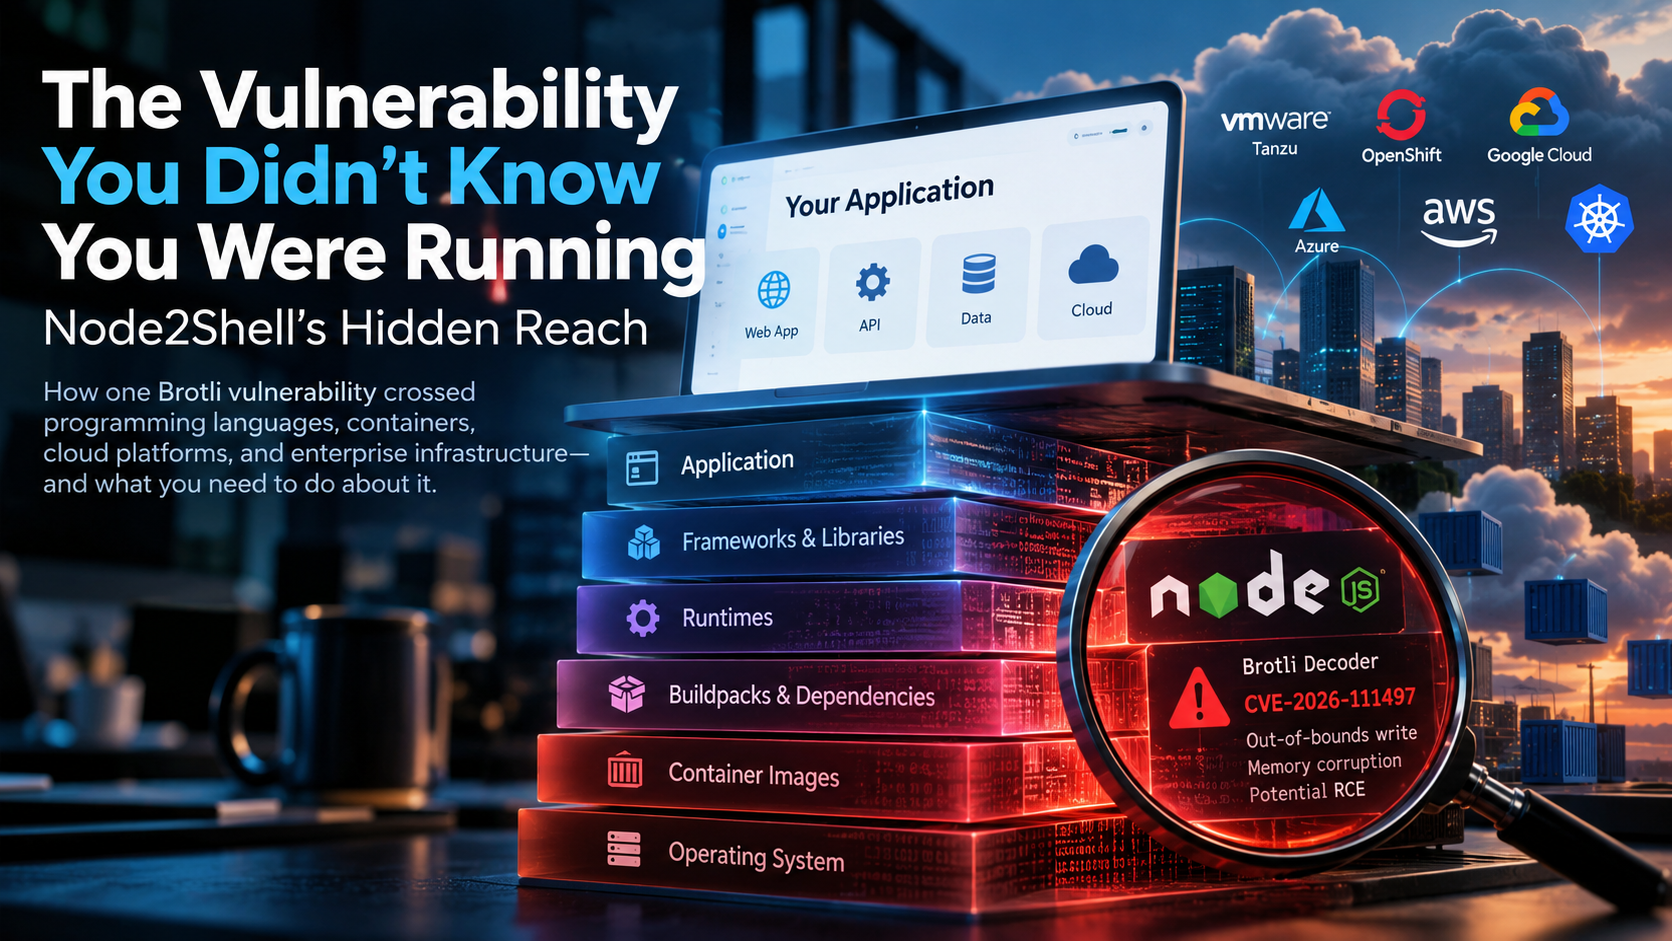
<p><strong>Security analysis | CVE-2026-111497 | October 31, 2026</strong></p> The 60-second security briefing <p><strong>Node2Shell is not just...
At 14:00 UTC on October 21, PHP released patches to two critical CVEs, both of which can lead to remote code execution. CVE-2026-109618 addresses an RCE through an out-of-memory er...
CVE-2026-35029 and CVE-2026-59823 affect LiteLLM, which is commonly used by enterprises to connect their AI applications to providers like OpenAI and Anthropic
A major flaw in the code behind most websites has cyber agencies on high alert
hidden-software-vulnerabilities-put-roofing-data-at-risk
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Thursday added five security flaws to its Known Exploited Vulnerabilities (KEV) catalog, following their abuse b...
Recently discovered security flaws in PHP programming language, used by many websites globally, has highlighted the potential for cyber risk aggregation, which has long worried ins...
VulnCheck’s Patrick Garrity has found that seven months on, Project Glasswing resulted in only 217 vulnerabilities getting fixed, despite thousands reported
CVE-2026-115560 is a critical vulnerability in PHP's session upload progress feature that can let an attacker run code on a web server. PHP fixed it on November 19, 2026, in a secu...
Anthropic's Jason Clinton warned of a vulnerability tsunami in August, then the PHP emergency hit. Here is the crisis PR plan that comms teams need now.
PHP2Shell shows how quickly attackers can exploit critical vulnerabilities, often before organizations have time to patch. Token Security explains why limiting the access of servic...
Use SocialBu to discover ideas, generate post drafts, and schedule them across your social channels.