bleepingcomputer.com /1 month ago

Machine speed attacks require machine speed detection and response

Attackers can steal credentials and begin exfiltrating data within minutes, often before security teams can respond. Exaforce examines real-world attacks involving stolen GitHub to...
Read source
dzone.com /1 month ago

Detection and Response Did Its Job. Now Someone Has to Actually Fix It.

A host is isolated. A malicious process is killed. A compromised credential is revoked before an attacker can use it again. Detection and response worked exactly as intended, autom...

Read source
tulsatoday.com /2 weeks ago

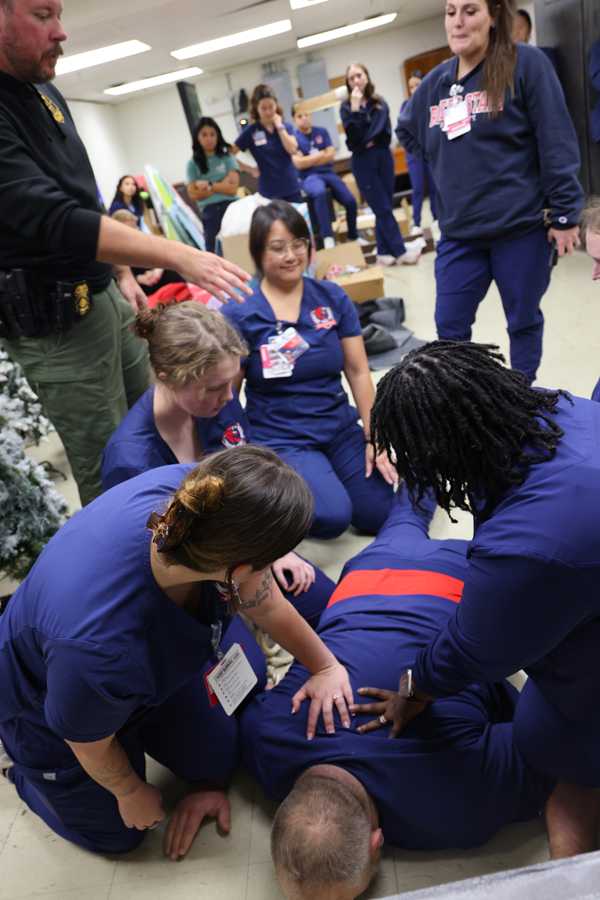
Nursing Trains for Attacker Response

Rogers State University senior nursing students recently completed an active attacker training exercise led by the RSU Police Department. Held in the basement of the Will Rogers Au...

Read source
mitnicksecurity.com /3 weeks ago

What an Adversarial Attack Simulation Engagement Delivers

An adversarial attack simulation engagement delivers an attack narrative: an account of how a realistic attacker moved through your environment, which Key Assets they reached, and...

Read source
cloud.google.com /1 month ago

ARMORY CASTLE Exploits BeyondTrust

Written by: Jayson Frost, Bryce Greathouse, Brian Meyer, John Palmisano, Rajesh Rajeshirke, Steve Rasch, John Wolfram Introduction  On October 15, BeyondTrust disclosed a vulnerab...

Read source
vbrainstorm.com /4 days ago

From Alert to Restore Point: Commvault Connects Microsoft Defender Signals to Threat Scan

<p><strong>The attack isn't over when it's contained</strong></p> <p>#MSIgnite #Commvault #MicrosoftSecurity #CyberResilience #AI #Com...

Read source
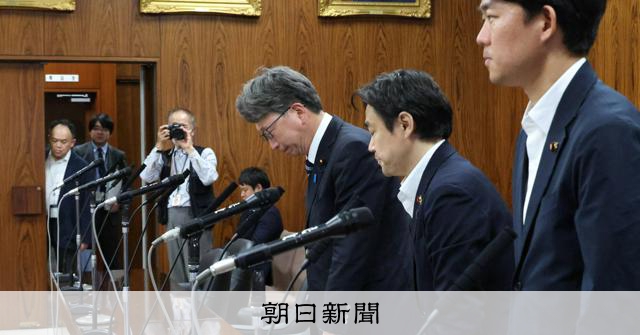
asahi.com /4 weeks ago

能動的サイバー防御とは? 警察・自衛隊が攻撃側に侵入し「無害化」

Read source
thehackernews.com /3 weeks ago

Between alerts: What Attackers Do in the Spaces Ordinary Detection Misses

Every SOC struggles with a pile of alerts. Very few of those alerts explain how an attack started or how it progressed. Network data, like that from a network detection and respons...

Read source
blog.invgate.com /3 days ago

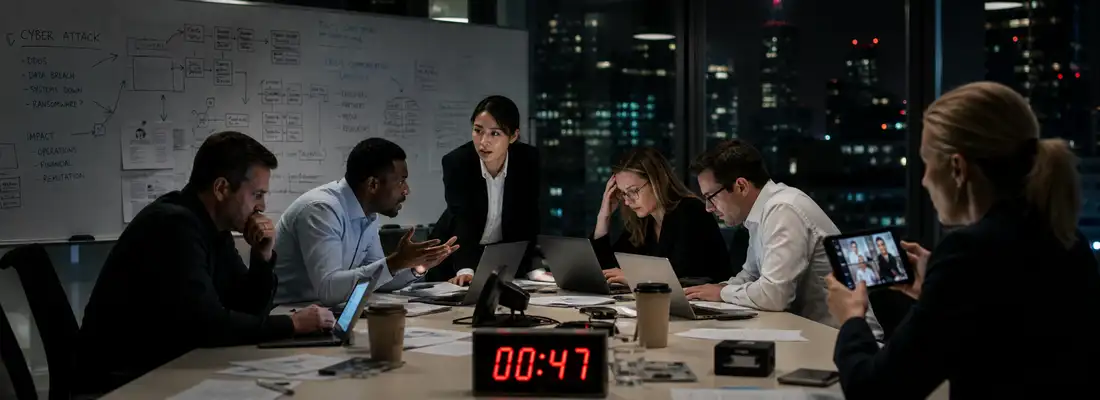
Inside The War Room: How InvGate Responds to Critical Vulnerabilities

No one wants to be the victim of a cyberattack. But truth be told, that's not entirely up to you. You can do everything by the book, have all the guardrails in place, train your pe...

Read source
cloud.google.com /1 month ago

Defending Against Active Exploitation of Citrix NetScaler ADC and Gateway Appliances

Introduction In late September 2026, Mandiant Consulting and Google Threat Intelligence Group (GTIG) identified active, in-the-wild exploitation of a zero-day vulnerability (CVE-20...

Read source
supplychaingamechanger.com /1 month ago

Inside the Mind of a Cyber Attacker!

In the perpetual game of cat and mouse between cyber attackers and defenders, the battleground is vast and dynamic. Understanding the Tactics, Techniques, and Procedures (TTPs) emp...

Read source
cloud.google.com /3 weeks ago

ARTEX and Friends: Enter Agentic Offensive Frameworks

Written by: Aurora Blum, David Mainor, Rohit Nambiar, Omar ElAhdan, Matthew McWhirt, Will Silverstone, Bhavesh Dhake, Chris Busse Introduction  Recent intrusions in which threat a...

Read source
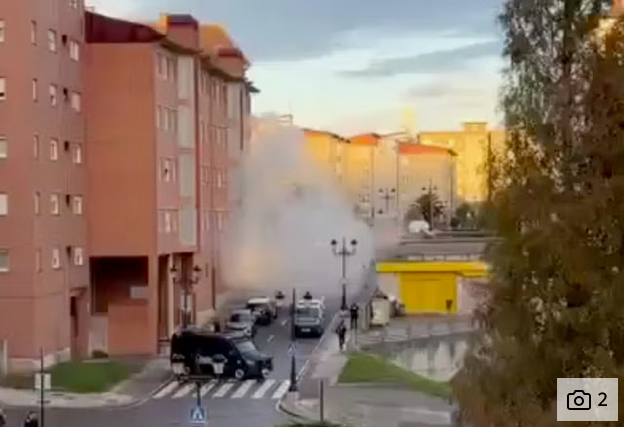
activeresponsetraining.net /1 week ago

Active Killer Attack with an Explosive Component

Read this short article. Police officer dies after backpack explodes at scene of Spain shooting     An active shooter who was additionally armed with an improvised bomb killed an o...

Read source
cm-alliance.com /1 month ago

The Best Cybersecurity Platforms for Detection and Response in 2026

From the moment an attacker gains access to their victim’s network, the average time it takes to move laterally into other systems and applications fell to just 34 minutes last yea...

Read source
itmedia.co.jp /1 month ago

「能動的サイバー防御」きょう開始 警察・自衛隊などが攻撃元サーバを無害化 高市首相も狙いを説明

政府は10月1日、「サイバー対処能力強化法」と同整備法の一部施行に伴い、重大なサイバー攻撃を未然に防ぐ「能動的サイバー防御」の運用を始めた。攻撃元のサーバに警察や自衛隊がアクセスし、...

Read source
thehackernews.com /1 month ago

Attackers Exploit NetScaler Flaw for Root Access, Deploy WHIPSHOT and SLAPSHOT

Unknown threat actors have been observed exploiting a newly patched security flaw in Citrix NetScaler ADC and NetScaler Gateway appliances to target organizations in North America...

Read source
cybersecuritynews.com /3 weeks ago

When Threats Don’t Wait, Security Can’t Either 

Dhananjay Ganjoo, Managing Director – India & SAARC  The uncomfortable part of an adaptive attack is not how quickly it starts, but  how quickly it can change course.   AI-assi...

Read source
cofense.com /4 days ago

The Next Cyberattack Won’t Wait. Are You Ready?

During the last several days, there has been an unprecedented number of unique cyberattacks across the globe. These attacks have evaded AI automation detection and defenses, impact...

Read source
climb.co.jp /1 month ago

攻撃者に先んじて実施すべき5つのバックアップセキュリティチェック

我々が最も頻繁に目にするのは、攻撃者がペイロードを実行する前に、数日から数週間に … <a href="https://www.climb.co.jp/blog_vmware/security-9545">続きを読む...

Read source
thehackernews.com /1 month ago

Attackers Exploit WordPress CVE-2026-87902 Within Hours of Disclosure

Threat actors have begun to actively exploit a critical security flaw in WordPress within hours of public disclosure. The vulnerability in question is CVE-2026-87902 (CVSS score:...

Read source
webwire.com /1 week ago

Cyber Attackers Are Targeting the Aviation Sector. How Should Air Traffic Controllers Respond?

Keeping aviation safe involves a complex ecosystem of stakeholders including aircraft manufacturers and airlines, airport authorities, air navigation service providers (ANSPs), cro...

Read source
thehackernews.com /1 month ago

Critical SonicWall SMA 1000 Flaw Targeted in 135 Exploitation Attempts After Patch

Threat actors have been observed exploiting a recently disclosed critical security flaw in SonicWall Secure Mobile Access (SMA) 1000 appliances within days of public disclosure. T...

Read source
thehackernews.com /1 month ago

Attackers Tampered with AOMEI Backupper's Update Servers for Minutes to Deliver a Backdoor

Attackers repeatedly changed the files that AOMEI Backupper fetches from the vendor's own update servers, in windows of five to ten minutes at a time between May and July 2026, so...

Read source
cm-alliance.com /1 month ago

Why Incident Response Plans Need Real-World Testing

At 07:35 on 28 October 2023, the British Library detected a cyber attack. By 09:15 its crisis process was activated, and by 10:00 its Gold Crisis Response Team had convened. On pap...

Read source

Turn fresh research into a full content calendar

Use SocialBu to discover ideas, generate post drafts, and schedule them across your social channels.