Latest updates for Splunk Enterprise Security

Fresh curated links around Splunk Enterprise Security are collected here so marketers can spot useful updates and turn timely ideas into posts faster.

Recent items include:

  • Admin in the Loop: Firewalls and the Agentic SOC
  • Building a Risk-Based Secure Network Analytics Detection with Splunk Detection Editor (Alpha)
  • Splunk .conf26: Tracking the Triage Agent in the Agentic SOC

Post angles to try

Share the most useful takeaway for your audience.
Turn one article into a quick practical checklist.
Ask your audience how this shift affects their work.
Turn angles into scheduled posts

Fresh articles and ideas

Recent curated links from global sources. Generate one free draft from any story, then use SocialBu to schedule and refine your content calendar.

blogs.cisco.com /2 weeks ago

Admin in the Loop: Firewalls and the Agentic SOC

Discover how Cisco Secure Firewall and Cloud Control stream structured Snort 3 and EVE telemetry into Splunk ES to power the .conf26 Agentic SOC pipeline.
Read source
blogs.cisco.com /1 month ago

Building a Risk-Based Secure Network Analytics Detection with Splunk Detection Editor (Alpha)

At Black Hat USA, we used Splunk Detection Editor Alpha to turn Cisco SNA alarms into risk events with context, drilldowns & analyst-ready investigation paths.

Read source
blogs.cisco.com /2 weeks ago

Splunk .conf26: Tracking the Triage Agent in the Agentic SOC

How Cisco used Splunk as the SOC data platform at .conf26 to unify security telemetry and track the Splunk AI Triage Agent with human-validated workflows.

Read source
blogs.cisco.com /12 hours ago

Unified Defense from Endpoint to Cloud: Real-Time Protection with Cisco Security, Splunk, and SentinelOne

Discover how Cisco and SentinelOne work together across Splunk, Duo, Firepower and now ISE — turning endpoint detection into automated network access decisions.

Read source
blogs.cisco.com /2 weeks ago

One Cisco in Action: Inside the Agentic SOC at .conf26

Read how Cisco Cloud Control and Splunk Enterprise Security powered the live Agentic SOC at .conf26 to deliver unified TDIR across live event traffic.

Read source
healthtechmagazine.net /1 week ago

Your Security Stack Is Working. Are Your Security Operations?

Walk into a modern enterprise security operations center today, and you'll discover just how inexpensive 65-inch monitors are: The walls are covered with them, showing dashboards f...

Read source
blogs.cisco.com /2 weeks ago

Chasing AMMYY at Splunk .conf

Discover how Cisco's Encrypted Visibility Engine (EVE) and Endace PCAP uncovered Flawed AMMYY RAT traffic at Splunk .conf without breaking TLS encryption.

Read source
blogs.cisco.com /2 weeks ago

The Zero-Day Blind Spot: Why Your Agentic SOC needs Retrospective Packet Replay

Learn how the .conf26 Agentic SOC paired Endace full PCAP with Cisco Secure Firewall and Talos rules to retrospectively replay wire data against zero-days.

Read source
computerweekly.com /1 month ago

Splunk helps US research uni embrace ‘student-powered’ security

When she was asked to let IT students run its SOC, New Jersey Institute of Technology CISO Sharon Kelley ran a mile. Find out why she changed her mind, and how Splunk is helping he...

Read source
dev.to /1 month ago

Armé un SIEM gratis con Wazuh y Kibana: así detecta un ataque de fuerza bruta en tiempo real

El problema que casi nadie mira hasta que es tarde Trabajando en infraestructura para más de 25 sedes de una corporación, aprendí algo que se repite en todo el sector IT: el pr...

Read source
salesforce.com /1 month ago

Trust & Security at Dreamforce 2026

Discover how to secure the agentic enterprise with hands-on training, expert guidance, and Security Keynote in San Francisco and on Salesforce+.

Read source
blogs.cisco.com /2 days ago

Hardened by Design: Applying the NSA’s OT Guidance with Cisco Security & Splunk

Apply the NSA’s new Zero Trust guidance to your OT environments. Learn how Cisco Cyber Vision and Splunk provide the visibility and telemetry needed to secure critical infrastructu...

Read source
aws.amazon.com /1 month ago

Securing Amazon Quick from POC to production: Agents, Flows, and Spaces

Amazon Quick proof-of-concept projects often stall when security teams review the production plan. This post walks through designing dashboards, Spaces, knowledge bases, agents, an...

Read source
salesforce.com /1 month ago

Introducing Security Mesh: Unify Your Security Data for Greater Visibility

When signals live in silos, its hard to see the whole picture. Turn a flood of security data into a clear, actionable picture of risk.

Read source
marktechpost.com /1 month ago

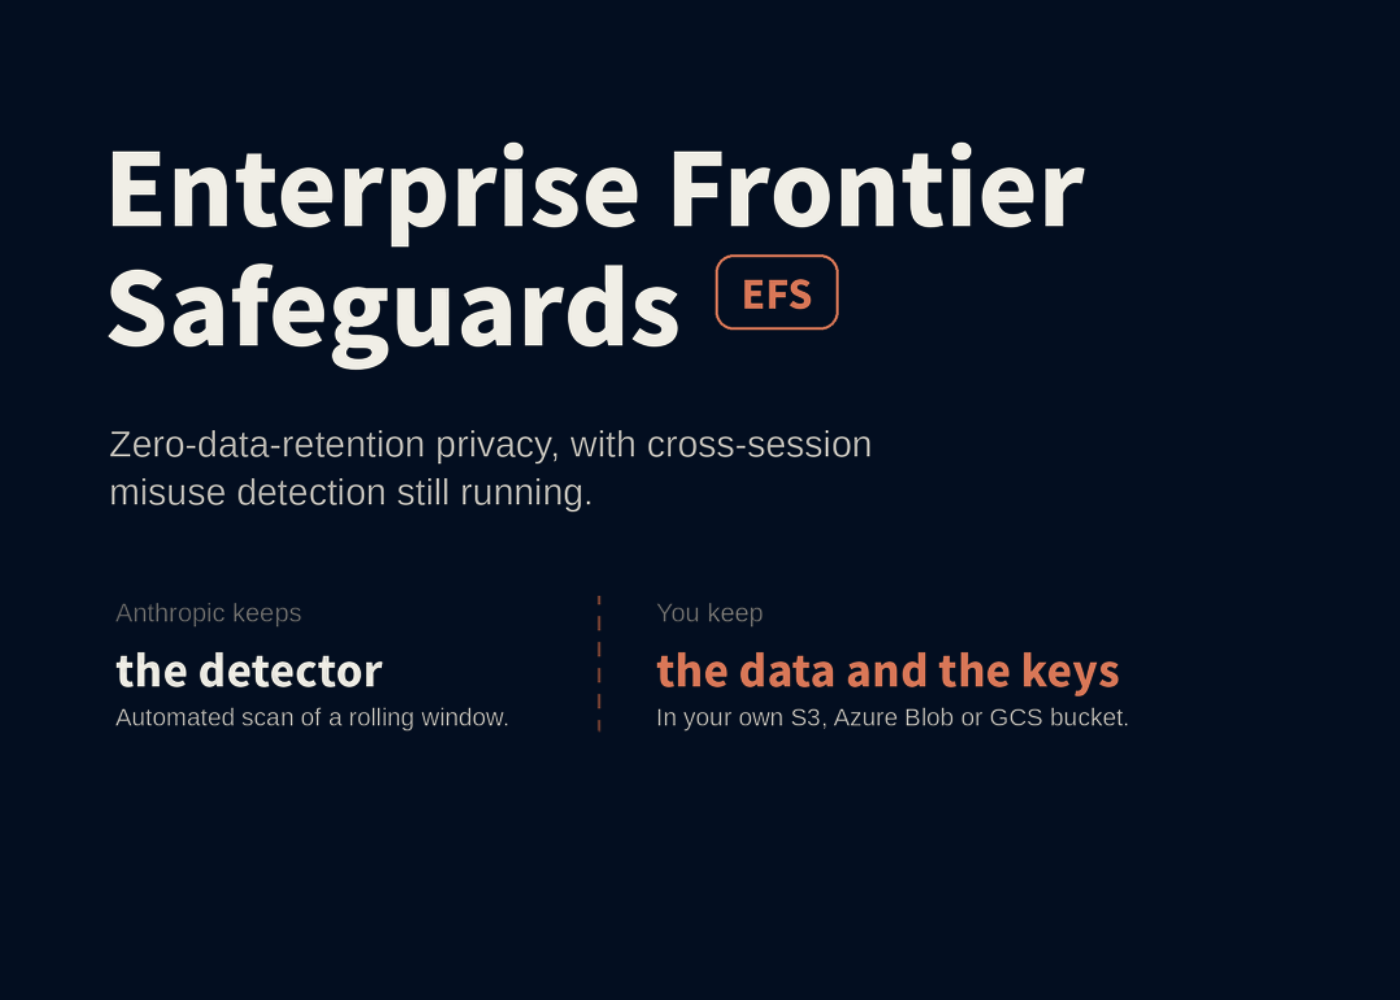
Anthropic Introduces Enterprise Frontier Safeguards (EFS): Zero-Data-Retention Privacy Plus Cross-Session Misuse Detecti...

Anthropic announced Enterprise Frontier Safeguards on September 1, 2026, an architecture that stores monitoring data in the customer's own cloud account rather than Anthropic's. De...

Read source
gbhackers.com /2 weeks ago

Critical Splunk Enterprise Vulnerability Lets Unauthenticated Attackers Execute OS Commands

Splunk has addressed a critical vulnerability in Splunk Enterprise that allows unauthenticated attackers to execute operating system commands through the Patroni REST API on a sear...

Read source
blogs.vmware.com /1 month ago

VMware vDefend IDPS: Securing Private Cloud Workloads in the Age of Frontier AI

<div><img width="300" height="162" src="https://blogs.vmware.com/wp-content/uploads/2026/08/GettyImages-1310129244.png" class="attachmen...

Read source
cybersecuritynews.com /2 weeks ago

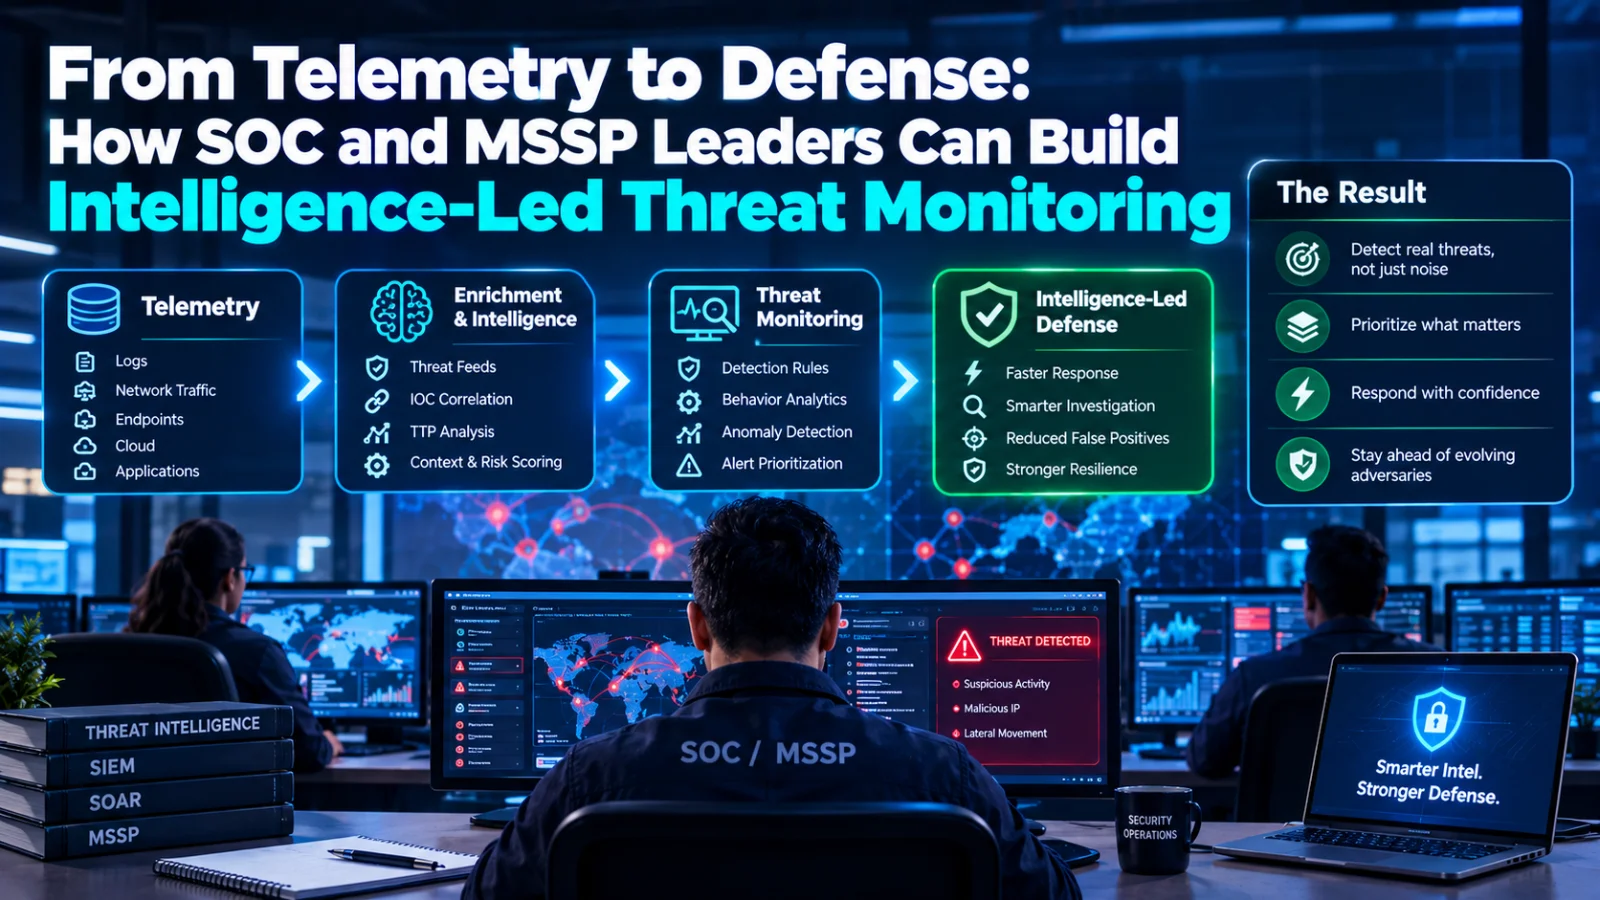
From Telemetry to Defense: How SOC and MSSP Leaders Can Build Intelligence-Led Threat Monitoring 

Every function in a security operations center, from alert triage to incident response, depends on how well threats are monitored. Yet many SOCs and managed security providers stil...

Read source
blogs.vmware.com /1 week ago

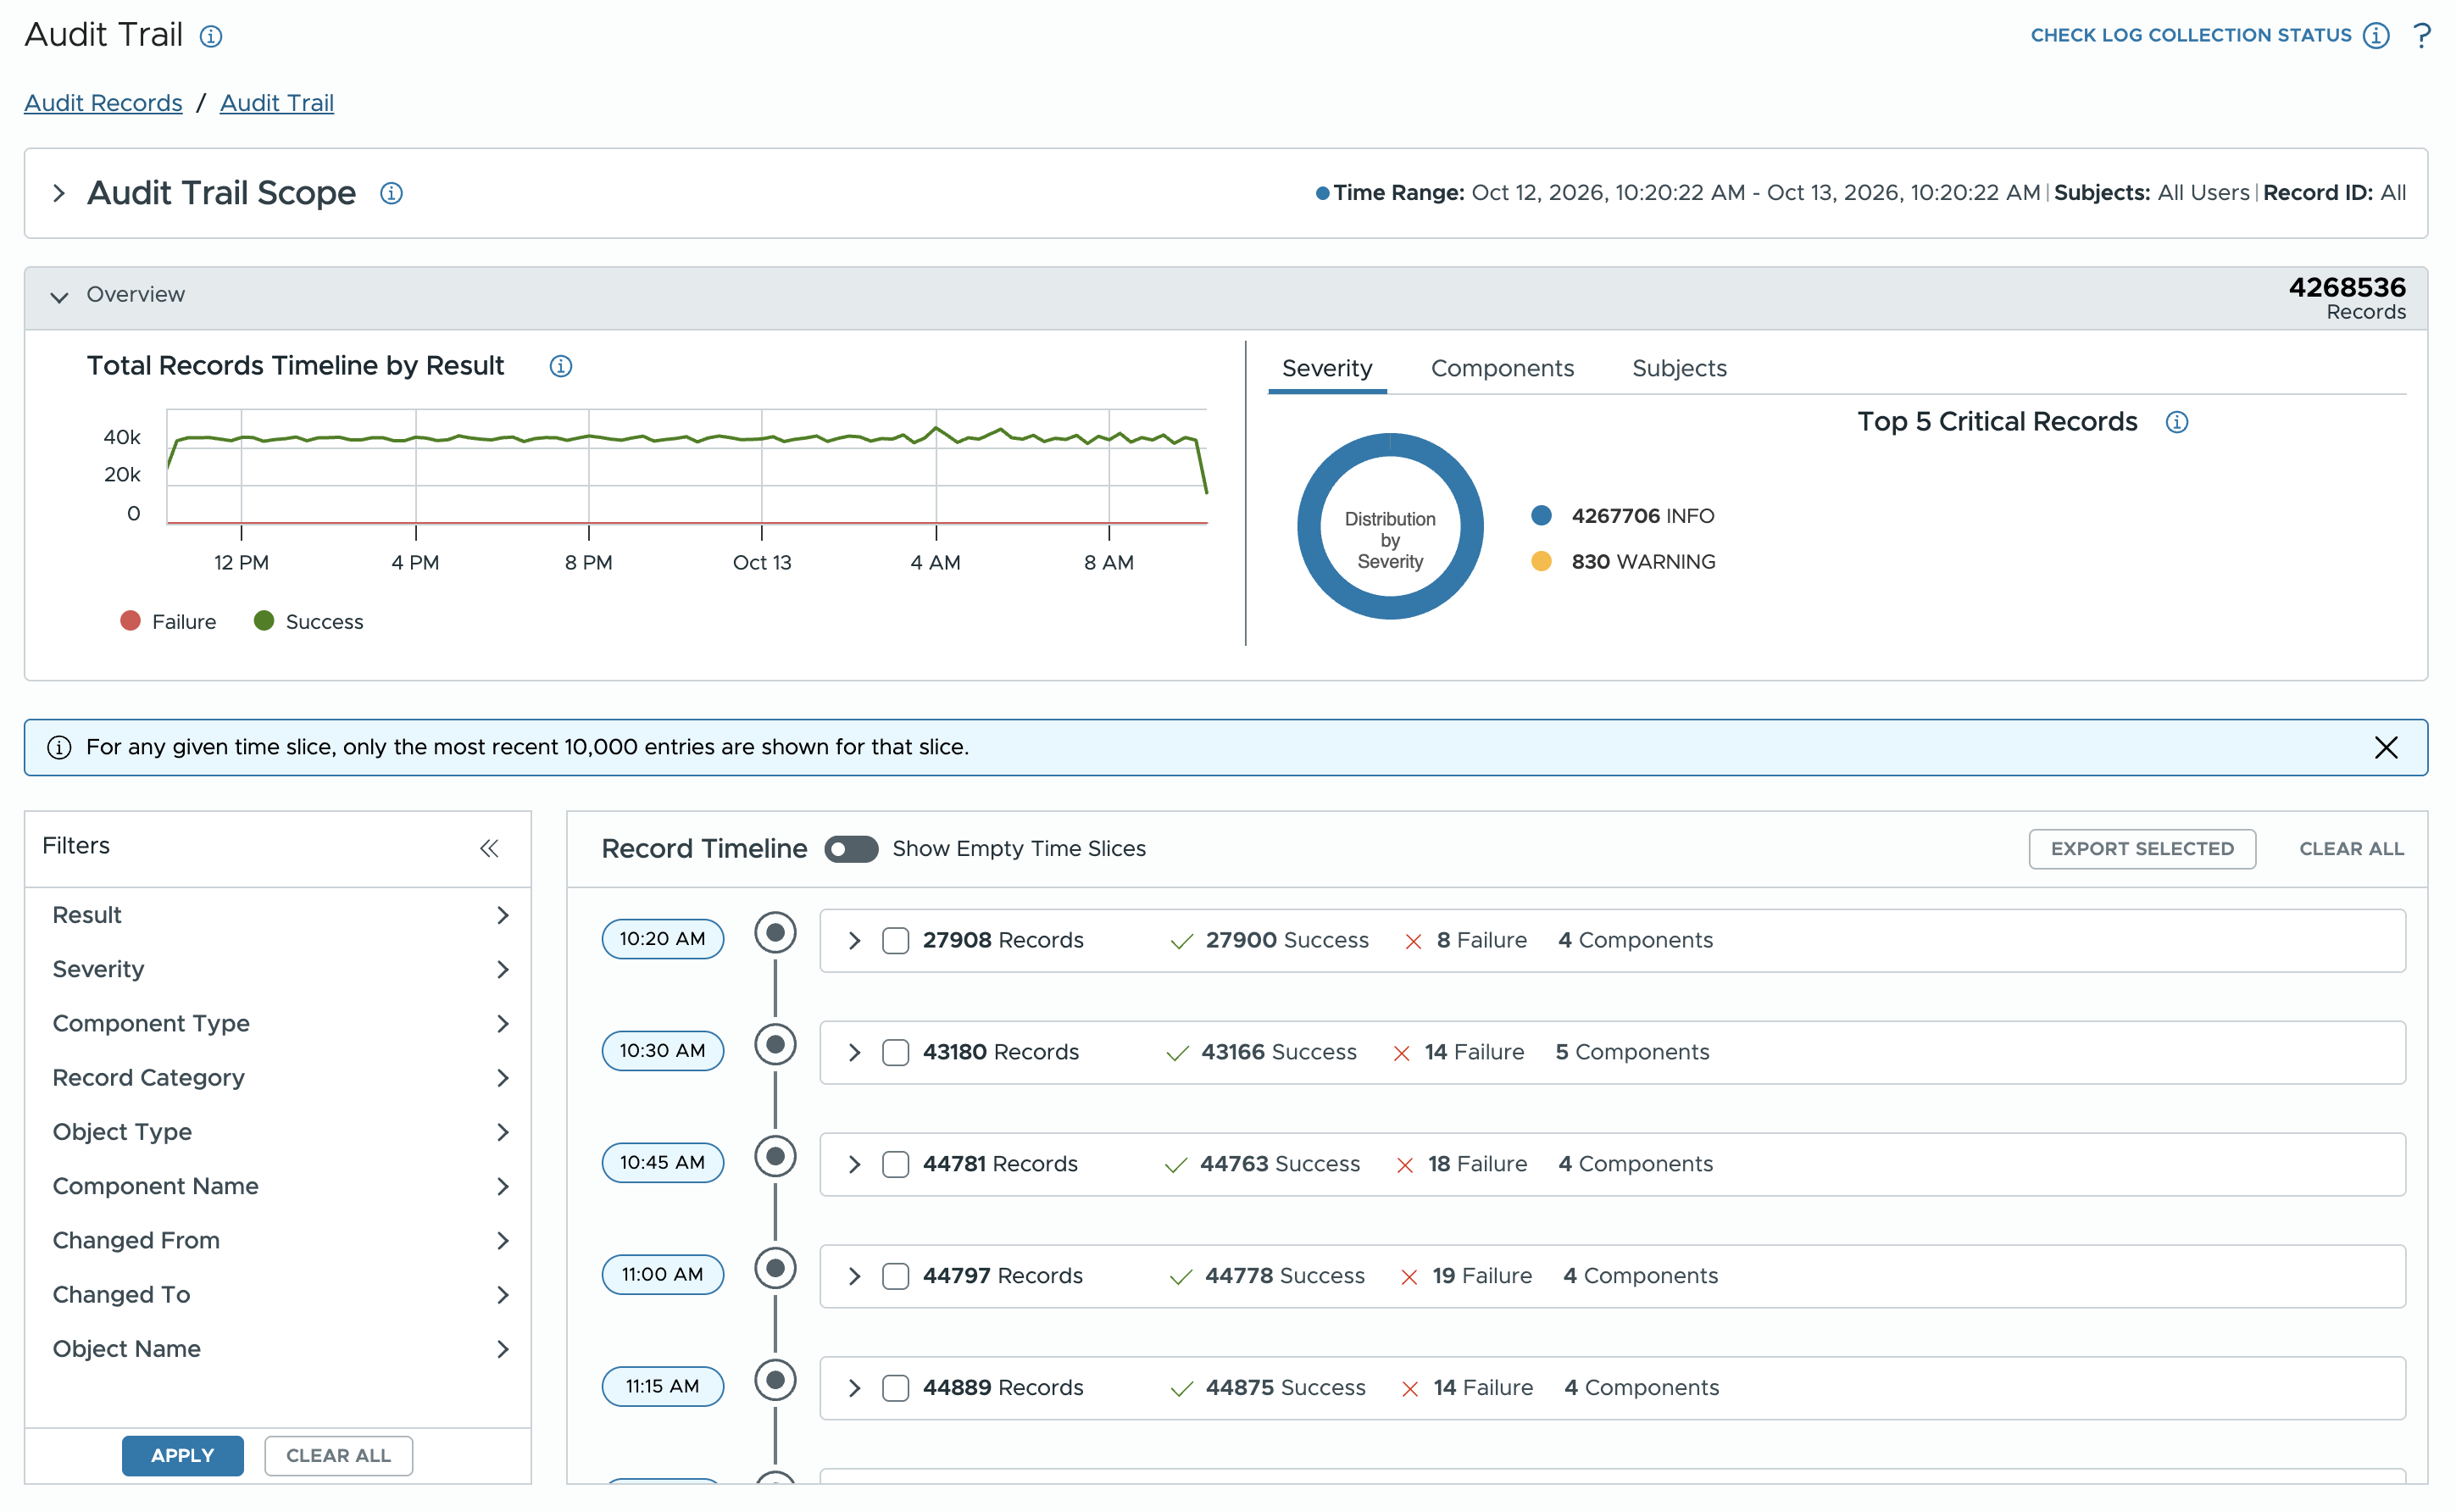
Threat hunting and Cross-Component Forensics with VCF Audit Trail

<div><img width="300" height="185" src="https://blogs.vmware.com/wp-content/uploads/2026/10/Screenshot-2026-10-13-at-10.20.39-AM.png" class=&...

Read source
aws.amazon.com /3 days ago

Trace security threats in multi-agent pipelines with Amazon OpenSearch Service

Learn how to trace two invisible threats in a multi-agent AI pipeline, prompt injection propagation and cross-tenant data exfiltration, using Amazon OpenSearch Service and Amazon B...

Read source
bleepingcomputer.com /3 weeks ago

Catch threats before they escalate with real-time Identity Telemetry

Identity governance helps control who should have access, but periodic reviews alone may not reveal attacks as they happen. tenfold Software explains how real-time identity telemet...

Read source
gbhackers.com /2 weeks ago

12 Best ASPM Platforms Compared (2026): Features & Pricing

Apiiro leads risk-graph depth, ArmorCode aggregation breadth, and the acquisition wave (Dazz into Wiz, Bionic into CrowdStrike, Enso into Snyk) tells you where ASPM is going: into...

Read source
weworkremotely.com /1 month ago

Expel: Managed SIEM Detection Engineer

Headquarters: Remote Are you a detection engineer who wants to bring real depth of expertise into a new and growing function and use it to deliver security excellence to customer...

Read source
computerweekly.com /1 week ago

MoD’s new SIEM, analytics platform up and running

At a critical moment for Britain's national security, the Ministry of Defence’s upgraded SIEM and security analytics platform is being delivered by Centerprise and Elastic

Read source

Turn fresh research into a full content calendar

Use SocialBu to discover ideas, generate post drafts, and schedule them across your social channels.

Sources covering Splunk Enterprise Security

computerweekly.com

Recent coverage from public sources
Public source

aws.amazon.com

Recent coverage from public sources
Public source

aws.amazon.com

Recent coverage from public sources
Public source

blogs.cisco.com

Recent coverage from public sources
Public source

blogs.vmware.com

Recent coverage from public sources
Public source

cybersecuritynews.com

Recent coverage from public sources
Public source