cloud.google.com /1 month ago

Defending Against Active Exploitation of Citrix NetScaler ADC and Gateway Appliances

Introduction In late September 2026, Mandiant Consulting and Google Threat Intelligence Group (GTIG) identified active, in-the-wild exploitation of a zero-day vulnerability (CVE-20...
Read source
gbhackers.com /1 week ago

Cisco Talos Uncovers KeyDrift Malware Targeting SD-WAN Controllers to Steal Network Encryption Keys

UAT-11473, an advanced persistent threat actor deploying KeyDrift, a custom malware framework targeting Cisco Catalyst SD-WAN controllers. The framework embeds inside legitimate co...

Read source
blogs.cisco.com /1 month ago

Chasing AMMYY at Splunk .conf

Discover how Cisco's Encrypted Visibility Engine (EVE) and Endace PCAP uncovered Flawed AMMYY RAT traffic at Splunk .conf without breaking TLS encryption.

Read source
thehackernews.com /1 week ago

Hackers Exploited Cisco SD-WAN Flaw to Plant Malware Built to Steal Encryption Keys

Hackers exploited a critical Cisco Catalyst SD-WAN flaw, fixed in February, to plant custom malware inside the systems that control an organization's SD-WAN network. The malware,...

Read source
thehackernews.com /1 day ago

Cisco BroadWorks and Openwave Flaws Actively Exploited Despite Available Patches

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) Tuesday added two security flaws impacting Cisco BroadWorks and Openwave Messaging Webtop Media Transcoder to its K...

Read source
bleepingcomputer.com /1 month ago

Cisco warns of new SD-WAN zero-day exploited in attacks

Cisco released security updates to address a critical zero-day in the Catalyst SD-WAN Manager (tracked as CVE-2026-76504) that attackers are actively exploiting to escalate to admi...

Read source
thehackernews.com /1 month ago

CISA Adds Exploited Cisco Catalyst SD-WAN Manager Auth Bypass to KEV

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Wednesday added a critical authentication bypass flaw impacting Cisco Catalyst SD-WAN Manager to its Known Explo...

Read source
blogs.cisco.com /2 weeks ago

Antares: a Security Analyst That Never Leaves Your Laptop – Security Loop Series, Part 1

A CWE advisory names your dependency, but not where the bug lives. See how Cisco's Antares-1B localizes it offline on a laptop, with auditable traces and honest benchmark numbers.

Read source
blogs.cisco.com /1 month ago

One Cisco in Action: Inside the Agentic SOC at .conf26

Read how Cisco Cloud Control and Splunk Enterprise Security powered the live Agentic SOC at .conf26 to deliver unified TDIR across live event traffic.

Read source
bleepingcomputer.com /1 week ago

New Cisco firewall zero-day exploited to crash SSL VPN devices

Cisco released security updates to patch a denial-of-service zero-day in Adaptive Security Appliance (ASA) and Threat Defense (FTD) software that attackers are exploiting to remote...

Read source
infosecurity-magazine.com /1 month ago

Critical Cisco Catalyst SD-WAN Zero-Day Under Active Exploitation

Vulnerability in Cisco Catalyst SD-WAN Manager allows an unauthenticated, remote attacker to access systems with admin privileges

Read source
smartermsp.com /1 week ago

Cybersecurity Threat Advisory: Cisco ASA & FTD VPN Flaw

A high-severity vulnerability affecting Cisco Secure Firewall ASA and FTD is under active exploitation. Tracked as CVE-2026-76418, the flaw poses a significant availability risk to...

Read source
thehackernews.com /1 month ago

Cisco Warns of Attackers Exploiting Critical Authentication Bypass in SD-WAN Manager

Attackers are exploiting a new critical zero-day flaw in Cisco Catalyst SD-WAN Manager, the system companies use to manage their Cisco SD-WAN networks, Cisco said in an advisory on...

Read source
bleepingcomputer.com /20 hours ago

CISA flags Cisco BroadWorks flaw as actively exploited in attacks

The US Cybersecurity and Infrastructure Security Agency (CISA) warned on Tuesday that hackers are now exploiting a high-severity Cisco BroadWorks vulnerability in attacks. [...]

Read source
thehackernews.com /1 month ago

Cisco Warns of New Zero-Day ISE Auth Bypass (CVSS 10.0) Exploited in Active Attacks

Cisco has warned of a fresh maximum-severity security flaw impacting Identity Services Engine (ISE) that has come under active exploitation. The vulnerability, tracked as CVE-2026...

Read source
infosecurity-magazine.com /1 month ago

Cisco Warns of Active Exploitation of Critical ISE Flaw

Cisco urged ISE customers to apply a software update, as well as check for signs of exploitation

Read source
bleepingcomputer.com /1 month ago

Cisco warns of max severity ISE zero-day exploited in attacks

Cisco has released security updates to address a maximum-severity Identity Services Engine vulnerability that attackers are actively exploiting in the wild. [...]

Read source
gbhackers.com /1 month ago

Sandworm-Linked Cyclops Blink Returns With Network Scanning and Packet-Sniffing Capabilities

A newly identified Cyclops Blink variant has resurfaced on compromised Cisco Secure Firewall Management Center (FMC) appliances, adding active internal-network scanning and program...

Read source
blogs.cisco.com /1 week ago

PHP2Shell: How Cisco Helps Customers Respond to AI-Accelerated Threats

The following resources address the coverage available for PHP2Shell today, as well as ways Cisco customers can begin to increase resilience for whatever AI-driven threat comes nex...

Read source
thehackernews.com /1 week ago

Cisco Patches Actively Exploited ASA and FTD VPN Flaw That Can Crash Firewalls

Cisco has released patches to address a high-severity security flaw in Secure Firewall Adaptive Security Appliance (ASA) Software and Secure Firewall Threat Defense (FTD) Software...

Read source
thehackernews.com /1 month ago

Antino Backdoor Uses Outlook and OneDrive for C2 in China-Nexus Espionage Campaign

Government and policy organizations across Asia have become the target of a new campaign orchestrated by a China-nexus threat actor. The activity, which has targeted government an...

Read source
thehackernews.com /4 weeks ago

Cisco Warns of Active Attacks Exploiting New Critical Secure Email Gateway Vulnerability

Attackers are exploiting a critical flaw in Cisco Secure Email Gateway that lets a sender with no login write files to the appliance's operating system, Cisco said in an advisory o...

Read source
bleepingcomputer.com /1 week ago

Hackers exploit Cisco SD-WAN flaw to deploy custom KeyDrift malware

A newly identified advanced persistent threat (APT) group tracked as UAT-11473 was observed exploiting CVE-2026-20127, an authentication-bypass flaw in Cisco Catalyst SD-WAN Contro...

Read source
blogs.cisco.com /2 weeks ago

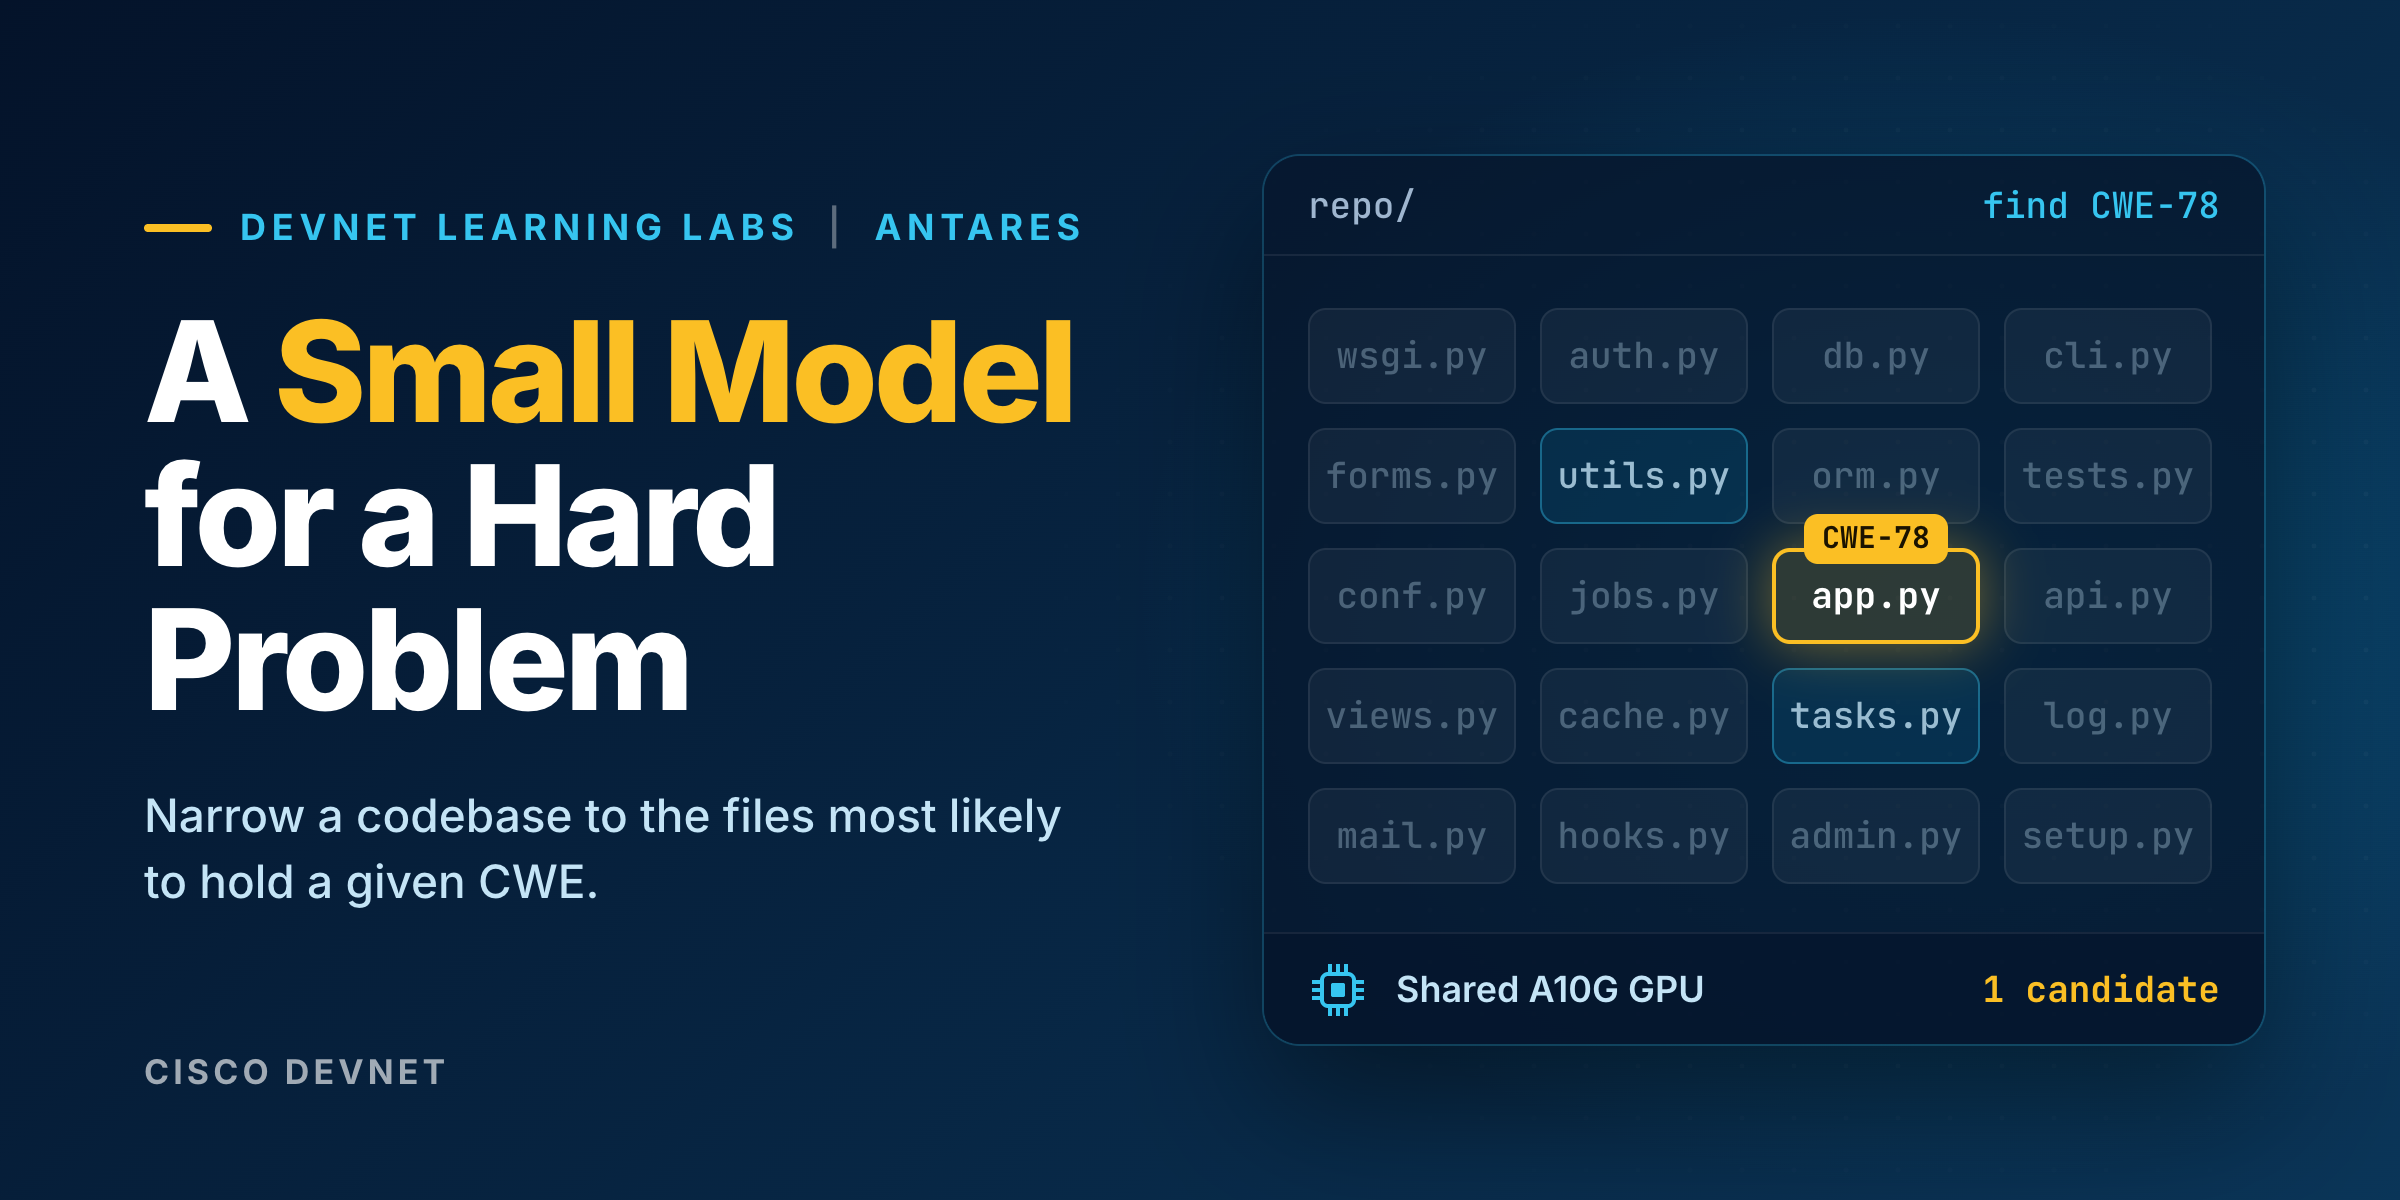
Scan Code for Vulnerabilities with Cisco Antares in DevNet Learning Labs

Two GPU-backed Antares Learning Labs are live. Use a small open-weight model to narrow a repo to the files that may hold a CWE, then see how DevNet shares one GPU across learners.

Read source

Turn fresh research into a full content calendar

Use SocialBu to discover ideas, generate post drafts, and schedule them across your social channels.