Your Security Stack Is Working. Are Your Security Operations?
Walk into a modern enterprise security operations center today, and you'll discover just how inexpensive 65-inch monitors are: The walls are covered with them, showing dashboards f...
Search fresh public links, source activity, and ready-to-use post angles for Security Operations Center.
Fresh curated links around Security Operations Center are collected here so marketers can spot useful updates and turn timely ideas into posts faster.
Recent items include:
Recent curated links from global sources. Generate one free draft from any story, then use SocialBu to schedule and refine your content calendar.
Walk into a modern enterprise security operations center today, and you'll discover just how inexpensive 65-inch monitors are: The walls are covered with them, showing dashboards f...
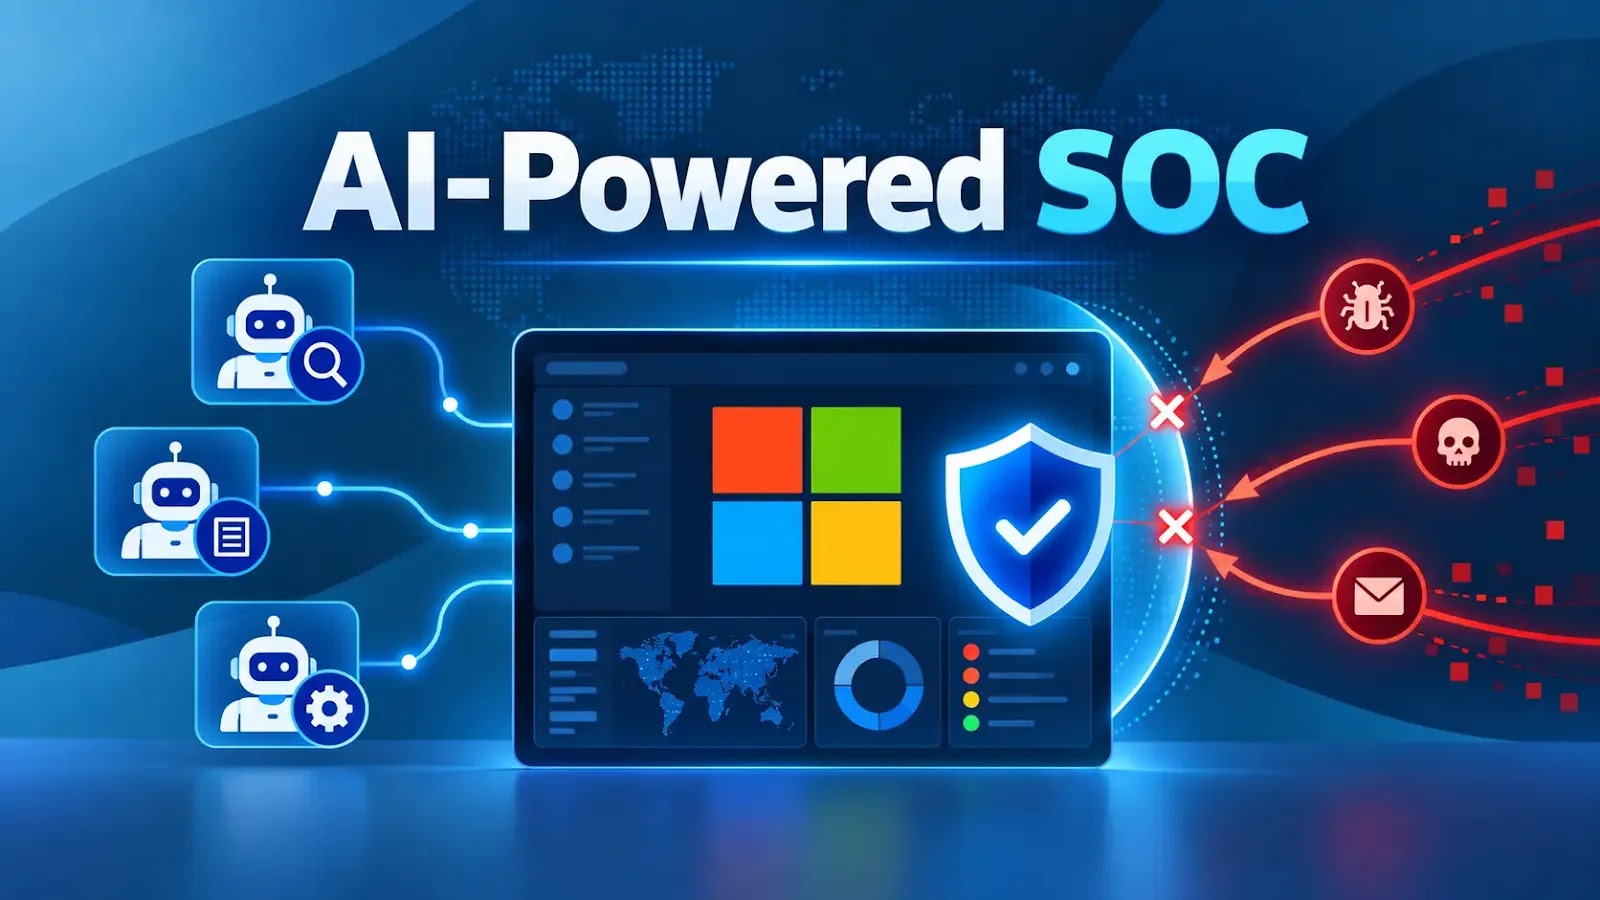
An Integrated Security Operations Center (ISOC) in Microsoft Defender, unifying security information and event management (SIEM) and threat-protection capabilities in a platform de...
Read how Cisco Cloud Control and Splunk Enterprise Security powered the live Agentic SOC at .conf26 to deliver unified TDIR across live event traffic.
Cisco is the Security Cloud Provider for the Black Hat conferences. Learn about the latest innovations for the Agentic SOC.
Cyberattacks can move faster than a security team can investigate them. Attackers increasingly use AI agents to automate steps that once needed several people, while defenders stil...
В эпоху цифровизации и постоянно растущих киберугроз мониторинг ИБ перестал быть просто «хорошим тоном». Однако как показывает практика, создание эффективной системы мониторинга в...
At Black Hat USA, we used Splunk Detection Editor Alpha to turn Cisco SNA alarms into risk events with context, drilldowns & analyst-ready investigation paths.
US security operations centers are not short on security products. They are short on time, people and context. Current industry research suggests the biggest obstacles to fast dete...
A Black Hat SOC analyst shares how agentic workflows, Splunk ES, packet evidence, and human mentorship accelerated triage & investigation in the NOC/SOC.
A new advisory from the Cybersecurity and Infrastructure Security Agency outlines how organizations can strengthen detection, response and protections in information technology (IT...
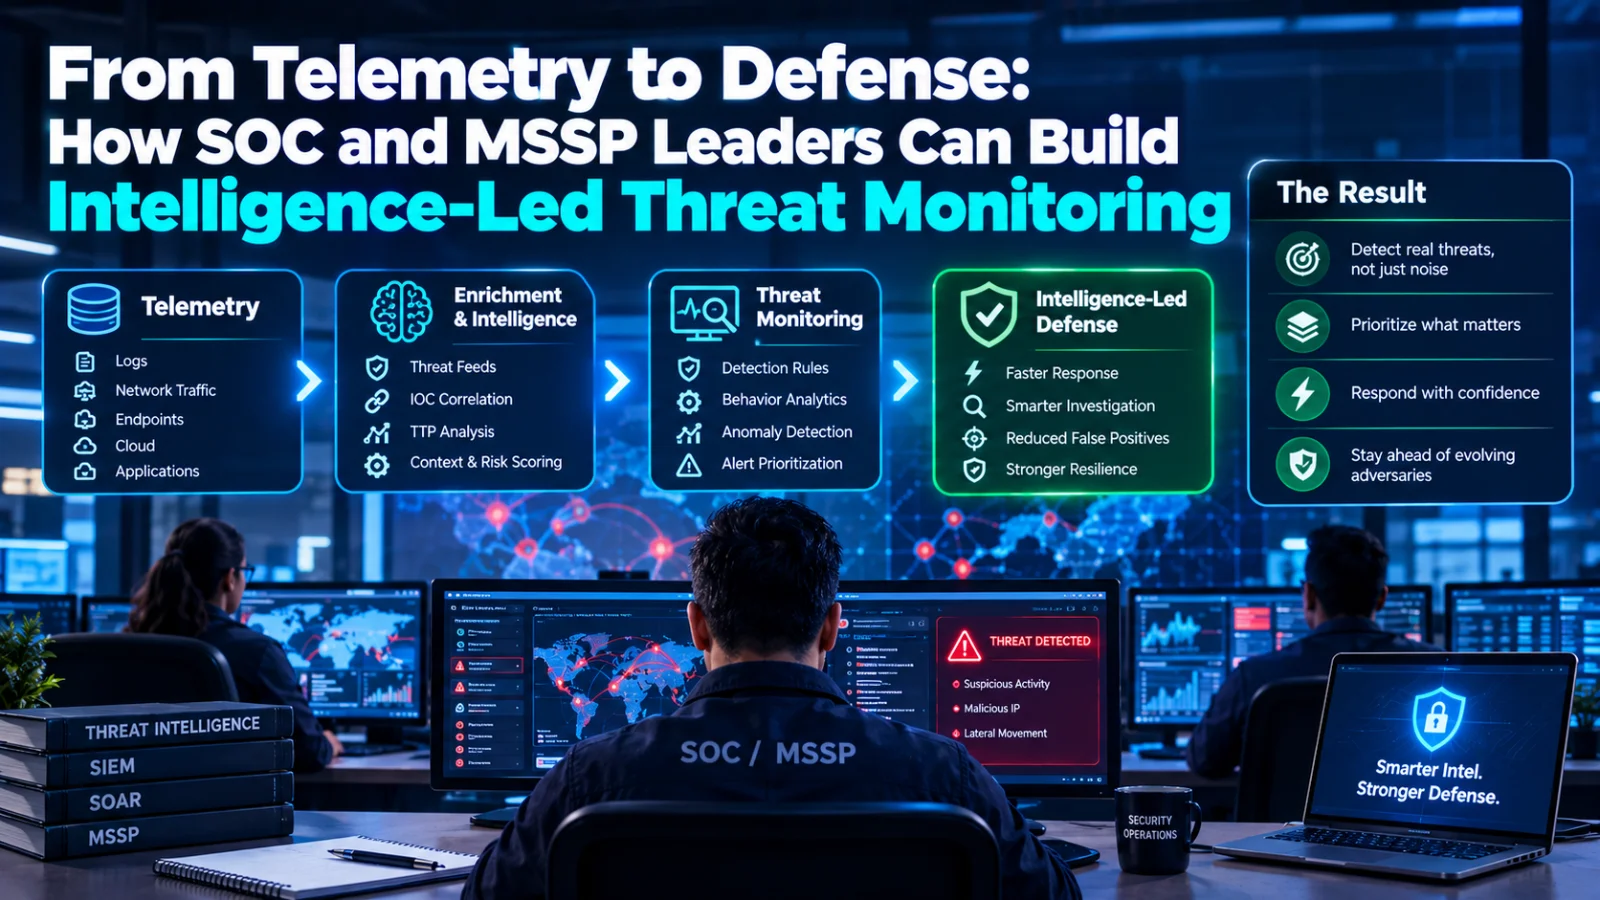
Every function in a security operations center, from alert triage to incident response, depends on how well threats are monitored. Yet many SOCs and managed security providers stil...
The dark web and threat actors have been targeting the healthcare industry for years, but the threats are improving in accuracy, legitimacy and damage as artificial intelligence (A...
Headquarters: Remote Ireland Reports to: Director, Security Operations Center Location: Remote Ireland Compensation Range: €115,200 to €133,000 base plus bonus and equity What We...
Discover how Cisco Secure Firewall and Cloud Control stream structured Snort 3 and EVE telemetry into Splunk ES to power the .conf26 Agentic SOC pipeline.
Over the past year, we watched a new class of alert appear in enterprise security operations centers and grow faster than anything else in the stream: alerts that were triggered by...
Headquarters: Remote US Reports to: Manager, Security Operations Center Location: Remote, US Compensation Range: $100,000-$125,000 base plus bonus and equity. This role may be el...
How Cisco used Splunk as the SOC data platform at .conf26 to unify security telemetry and track the Splunk AI Triage Agent with human-validated workflows.
OSINT has become essential for fighting counterespionage as data from platforms like social media make it hard to create cover stories.
CISA’s latest advisory for red teams warns critical infrastructure operators that security systems can fail even if they have a lot of funding. This is because trained analysts are...
A coach on a Counter-Strike 2 broadcast has about three seconds to call a rotation before the round is lost. No time to convene a meeting. No time to check with legal. Just a heads...
We’re pleased to confirm the successful completion of our annual Amazon Web Services (AWS) Outsourced Service Provider’s Audit Report (OSPAR) assessment on July 29, 2026, in line w...
AI is officially mainstream in security operations. According to Prophet Security's State of AI in Security Operations 2026 report (produced from ViB’s survey of 250+ cybersecurity...
The SOC we've always known was built around a model that guarantees most of the alert queue will never receive analyst review. There's never time. In a traditional SOC, the typical...
Источник: Компьютерра - Журнал о науке и технологиях После громких кибератак и публичных утечек данных компании зачастую приходят к тому, что без SOC не обойтись. Так называют цен...
Use SocialBu to discover ideas, generate post drafts, and schedule them across your social channels.