Beyond Passwords: Comprehensive Home Protection
A secure home in the 21st century needs more than just a strong front door lock. With our homes increasingly connected through smart devices, we have to update how we protect them,...
Search fresh public links, source activity, and ready-to-use post angles for Security Blogs.
Fresh curated links around Security Blogs are collected here so marketers can spot useful updates and turn timely ideas into posts faster.
Recent items include:
Recent curated links from global sources. Generate one free draft from any story, then use SocialBu to schedule and refine your content calendar.
A secure home in the 21st century needs more than just a strong front door lock. With our homes increasingly connected through smart devices, we have to update how we protect them,...
Identity was the target in roughly half of all confirmed malicious activity. Prophet Security breaks down the four main attack patterns seen across customer environments between Ma...
Read all about the latest AWS security features, compliance updates, and hands-on resources in our monthly digest posts. You’ll find expert blog posts, new service capabilities, co...
A blank field. A public repo. One reply to an email. A box left exposed. None of this sounds dramatic, which is partly the problem. This week’s threats keep finding leverage in sma...
我々が最も頻繁に目にするのは、攻撃者がペイロードを実行する前に、数日から数週間に &#8230; <a href="https://www.climb.co.jp/blog_vmware/security-9545">続きを読む...
A lot of tech content online seems to be written for people who already know the answer.Continue reading on Medium »
A CWE advisory names your dependency, but not where the bug lives. See how Cisco's Antares-1B localizes it offline on a laptop, with auditable traces and honest benchmark numbers.
Discover how Cisco Secure Firewall and Cloud Control stream structured Snort 3 and EVE telemetry into Splunk ES to power the .conf26 Agentic SOC pipeline.
Business risk often develops where separate systems, teams and procedures fail to share information. A door alarm may seem minor until it’s linked to an unusual login, a missing vi...
I wanted one place that tells me what is going on in my homelab: who is poking at it from outside, which boxes have known-exploited CVEs, what needs patching, and whether anything...
Beyond Bigger Servers: Keeping Websites Online Under Bot Attacks John Locke Mon, 10/05/2026 - 15:00 How la...
The boring parts caused most of the trouble. A router shipped ready to listen. A fake check turned the user into the installer. Trusted systems collected traffic and passwords, th...
Read how Cisco Cloud Control and Splunk Enterprise Security powered the live Agentic SOC at .conf26 to deliver unified TDIR across live event traffic.
Modern IT environments don’t stay still. Endpoints move between networks, users adopt new tools without approval, and infrastructure shifts between on-prem and cloud. As your envir...
This week, the useful words are boring ones: inspect, cache, compile, store, trust. Each sounds harmless. Each can become an attack path when a system does a little more than peopl...
A browser. A plugin. A package. A login screen. Normal stuff. That is basically the problem this week. The trouble keeps showing up inside things people already trust: code that t...
A fake login page. A fake security scan. A fake productivity app. Apparently, pretending to be useful is still one of the easier ways into a machine. The rest of the week gets str...
Windows systems are the backbone of most IT environments, running critical applications and enabling distributed workforces worldwide. Yet many organizations still rely on reactive...
Tim Purpura and Jordan Andrews from Morse Watchmans share information about how rising insider threats are causing lines between cyber and physical security to vanish. Individuals...
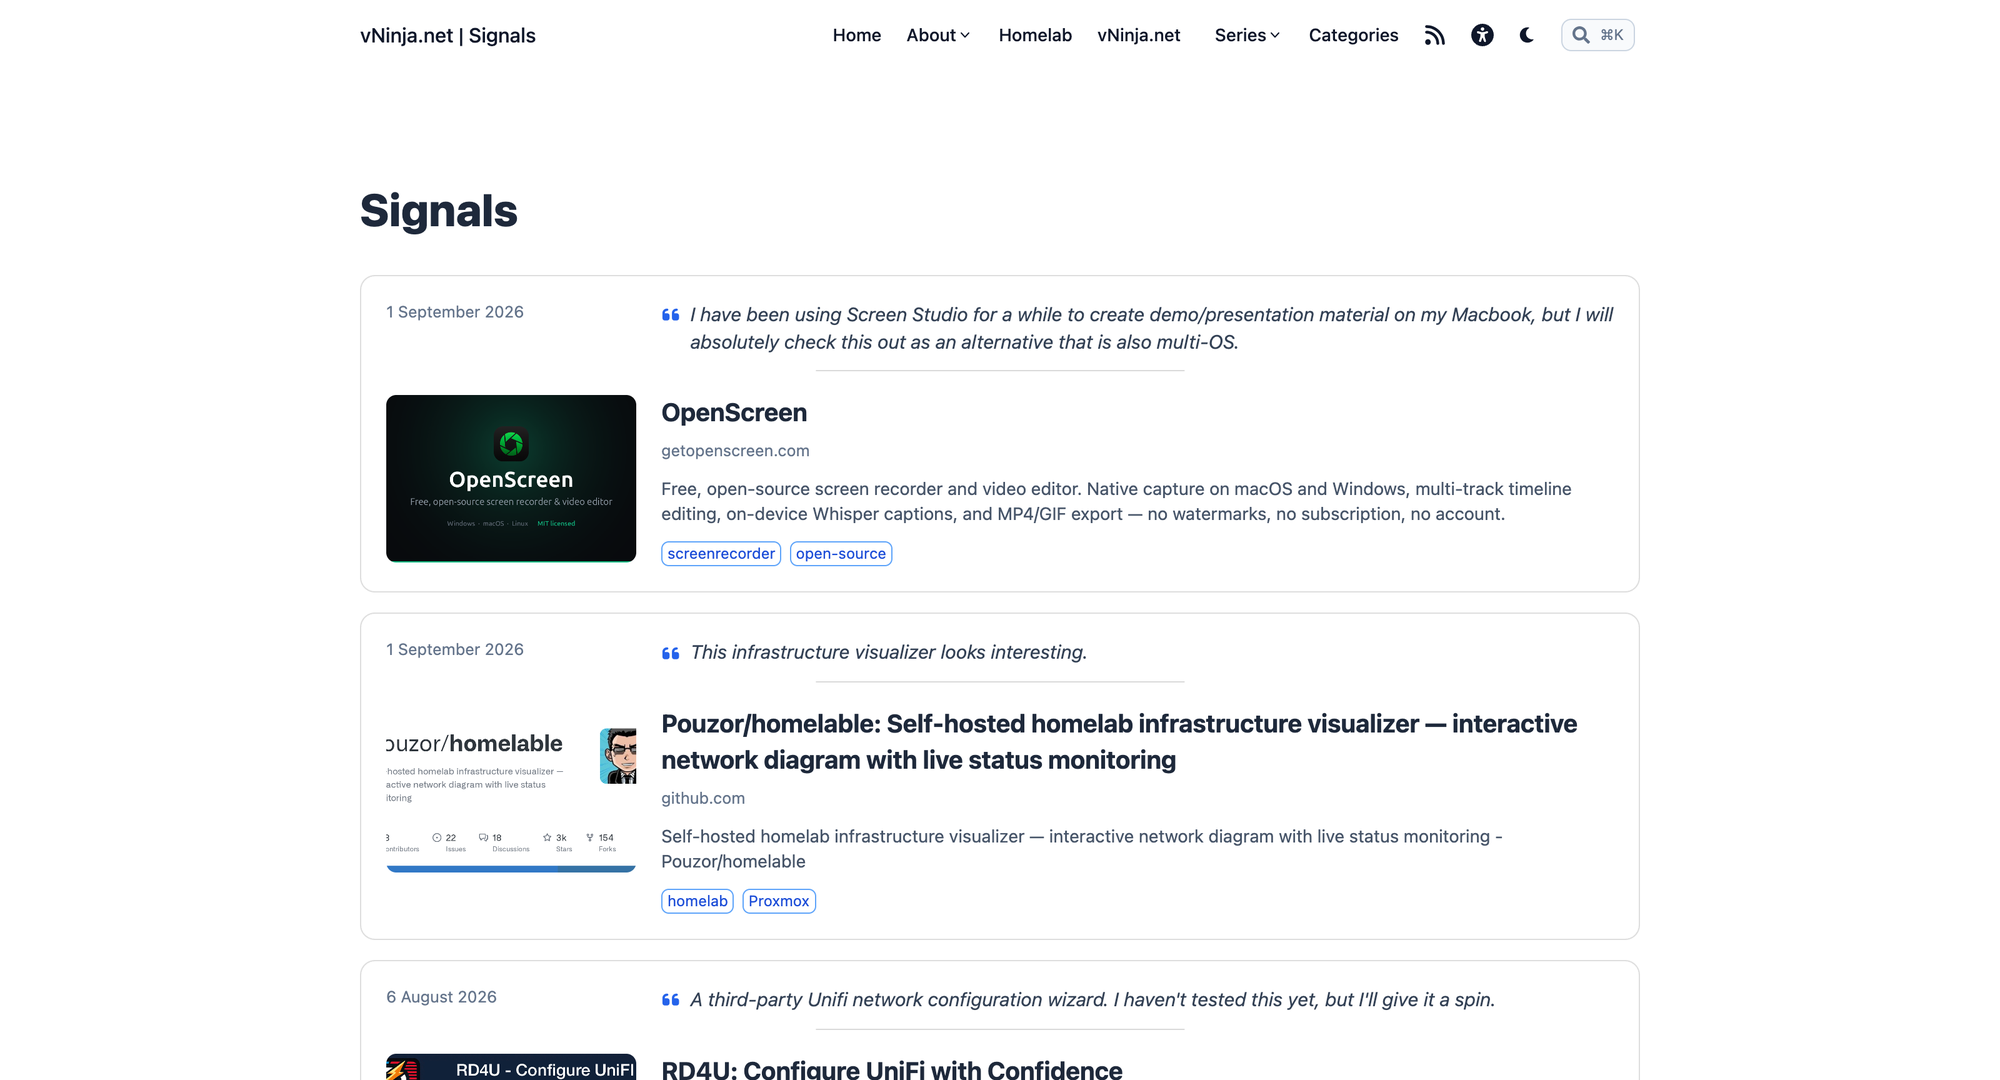
A new linkblog at signals.vninja.net for everything I bookmark but never write a full post about, heavily inspired by Tsugliani's
At Black Hat USA, we used Splunk Detection Editor Alpha to turn Cisco SNA alarms into risk events with context, drilldowns & analyst-ready investigation paths.
Compliance drift; adoption tax credit; distort the P&L statement; and other highlights from our favorite tax bloggers.
The post Sytex Ltd.: Delivering Smarter and More Reliable IT Solutions for Businesses first appeared on
Standardizing QA tools doesn't mean one IP type for every test. It means each test declares the network profile it needs, and one registry supplies it.
Use SocialBu to discover ideas, generate post drafts, and schedule them across your social channels.