CloudSEK investigates BigBear 2.0 phishing network exposures
CloudSEK’s researchers have revealed that a global Microsoft 365 phishing operation dubbed BigBear 2.0 has exposed 5,137 credential records across 461 organisations, including 4,14...
Search fresh public links, source activity, and ready-to-use post angles for Cloudsek.
Fresh curated links around CloudSEK are collected here so marketers can spot useful updates and turn timely ideas into posts faster.
Recent items include:
Recent curated links from global sources. Generate one free draft from any story, then use SocialBu to schedule and refine your content calendar.
CloudSEK’s researchers have revealed that a global Microsoft 365 phishing operation dubbed BigBear 2.0 has exposed 5,137 credential records across 461 organisations, including 4,14...
CDR is the runtime, real-time half of cloud security: while CSPM tells you what’s misconfigured, CDR tells you what’s happening right now an attacker using stolen cloud credentials...
Apiiro leads risk-graph depth, ArmorCode aggregation breadth, and the acquisition wave (Dazz into Wiz, Bionic into CrowdStrike, Enso into Snyk) tells you where ASPM is going: into...
Snyk is the best developer-platform SCA, Sonatype the repository-firewall powerhouse, and Socket the malicious-package specialist the CVE-scanners aren’t. Twelve options priced acr...
Bottom line up front: cloud identities human and machine are the perimeter now, and most are wildly over-privileged. CIEM answers “who can reach what, and should they,” then right-...
Quick Answer: Kubernetes security quotes hinge on the node-vs-cluster-vs-developer unit choice, and the OSS floor (Kubescape, Falco, Calico, NeuVector, Cilium/Tetragon) resets ever...
Contrast Security remains the dedicated IAST anchor, Black Duck’s Seeker the QA-leverage specialist, and Dynatrace/Datadog prove the category’s future is observability-delivered. O...
Ransomware activity targeting the Middle East surged to its highest level during the 17-month period assessed by CloudSEK, jumping from 17 threat intelligence feeds in April 2025 t...
CloudSEK has uncovered BigBear 2.0, a new phishing-as-a-service operation targeting Microsoft 365
Claude Code reads files, runs shell commands, invokes MCP tools, and acts through the credentials available on a developer’s machine. Anthropic’s new Compliance API endpoints give...
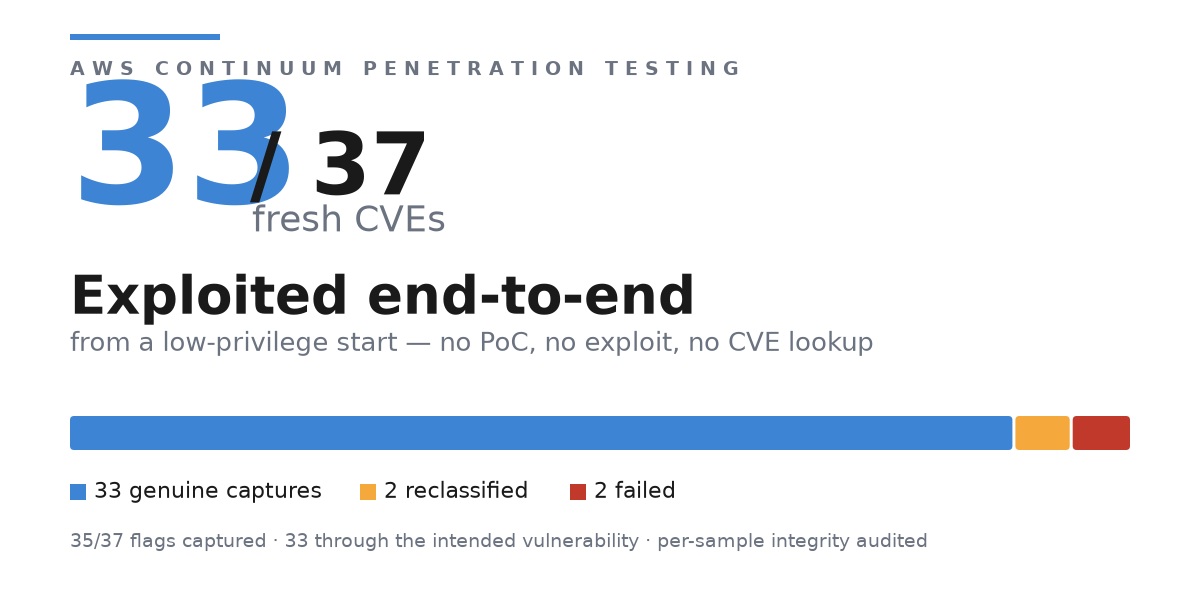
We applied AWS Security Agent (now part of AWS Continuum), our autonomous penetration-testing agent, to 37 real, recently disclosed Common Vulnerabilities and Exposures (CVEs), eac...
TL;DR: CSPM tools help organizations detect misconfigurations, risky permissions, exposed assets, and compliance gaps across cloud environments like AWS, Azure, and Google Cloud. T...
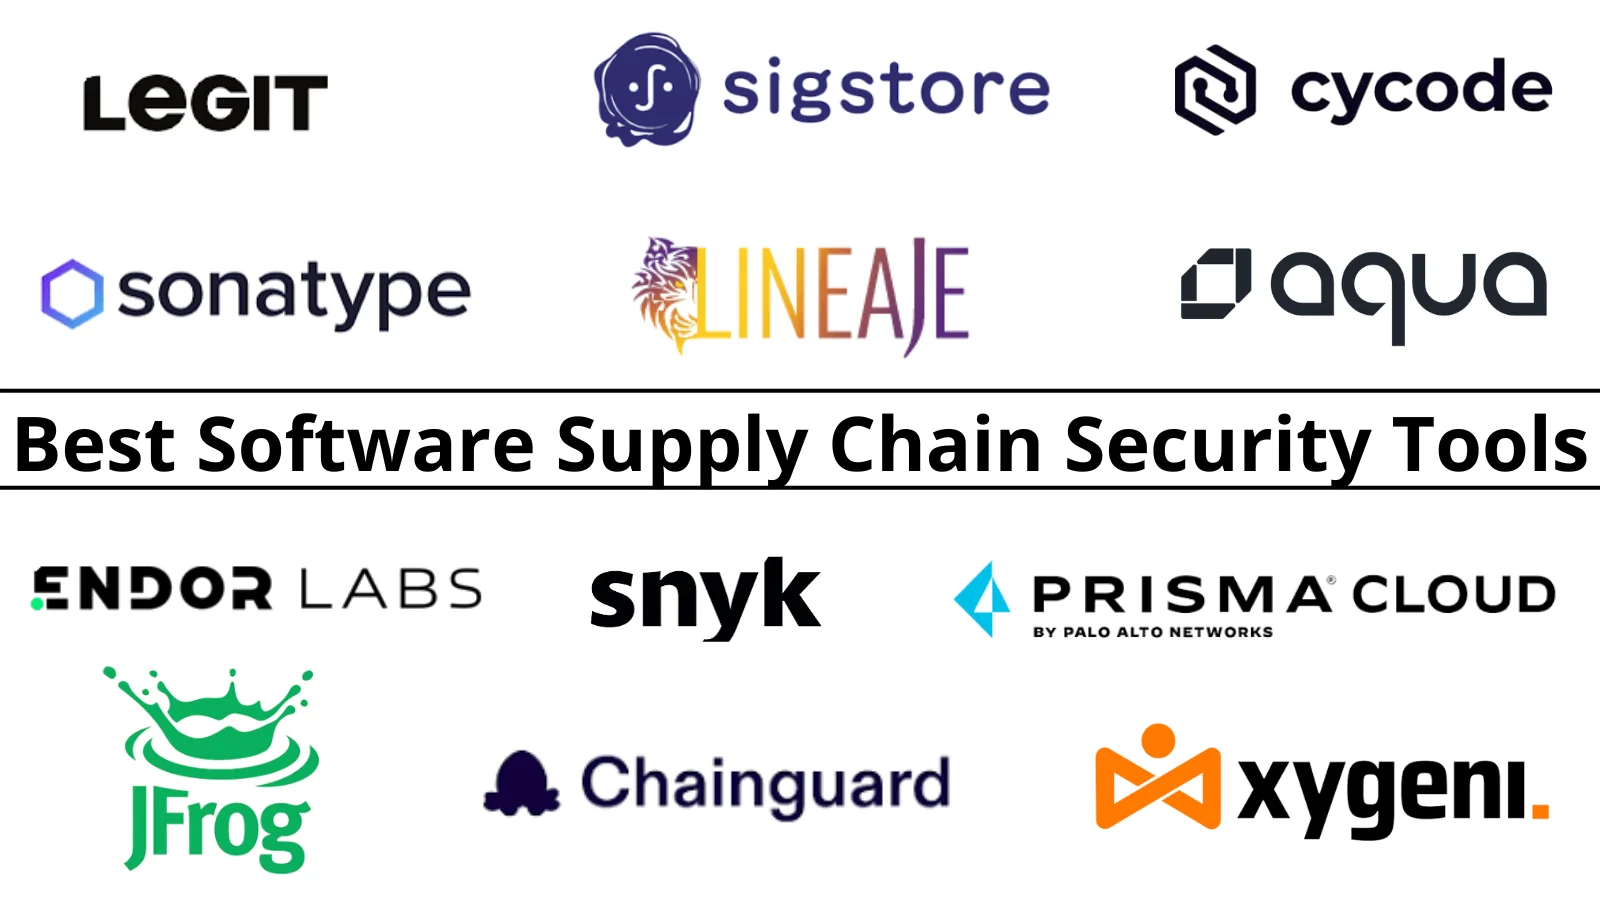
Chainguard leads the eliminate-the-problem lane with hardened zero-CVE images, Sonatype the block-at-ingestion lane, and Scribe/Lineaje the provenance-attestation frontier. Selecti...
Serverless changed the attack surface: no host to protect, but every function is a tiny privileged identity with its own code, dependencies, and permissions and there are thousands...
Salt Security and Traceable anchor dedicated discovery-plus-runtime defense, 42Crunch owns design-time contract security, and the edge giants (Akamai with Noname inside, Cloudflare...
HashiCorp Vault remains the best dedicated secrets platform the dynamic-secrets benchmark, now under IBM while cloud-native stores win single-cloud estates on price and Akeyless le...
Every modern enterprise depends on credentials. This is how humans, systems, and now AI, all connect to data, services, and each other securely. GitGuardian helps secure that crede...
Most companies start with generic IT. A managed service provider handles laptops, email and antivirus. A stack of SaaS subscriptions covers core functions. Someone internal becomes...
Container security spans the whole lifecycle build (image scanning, IaC), ship (registry, admission), and run (runtime detection, drift) across modern multi-cloud security architec...
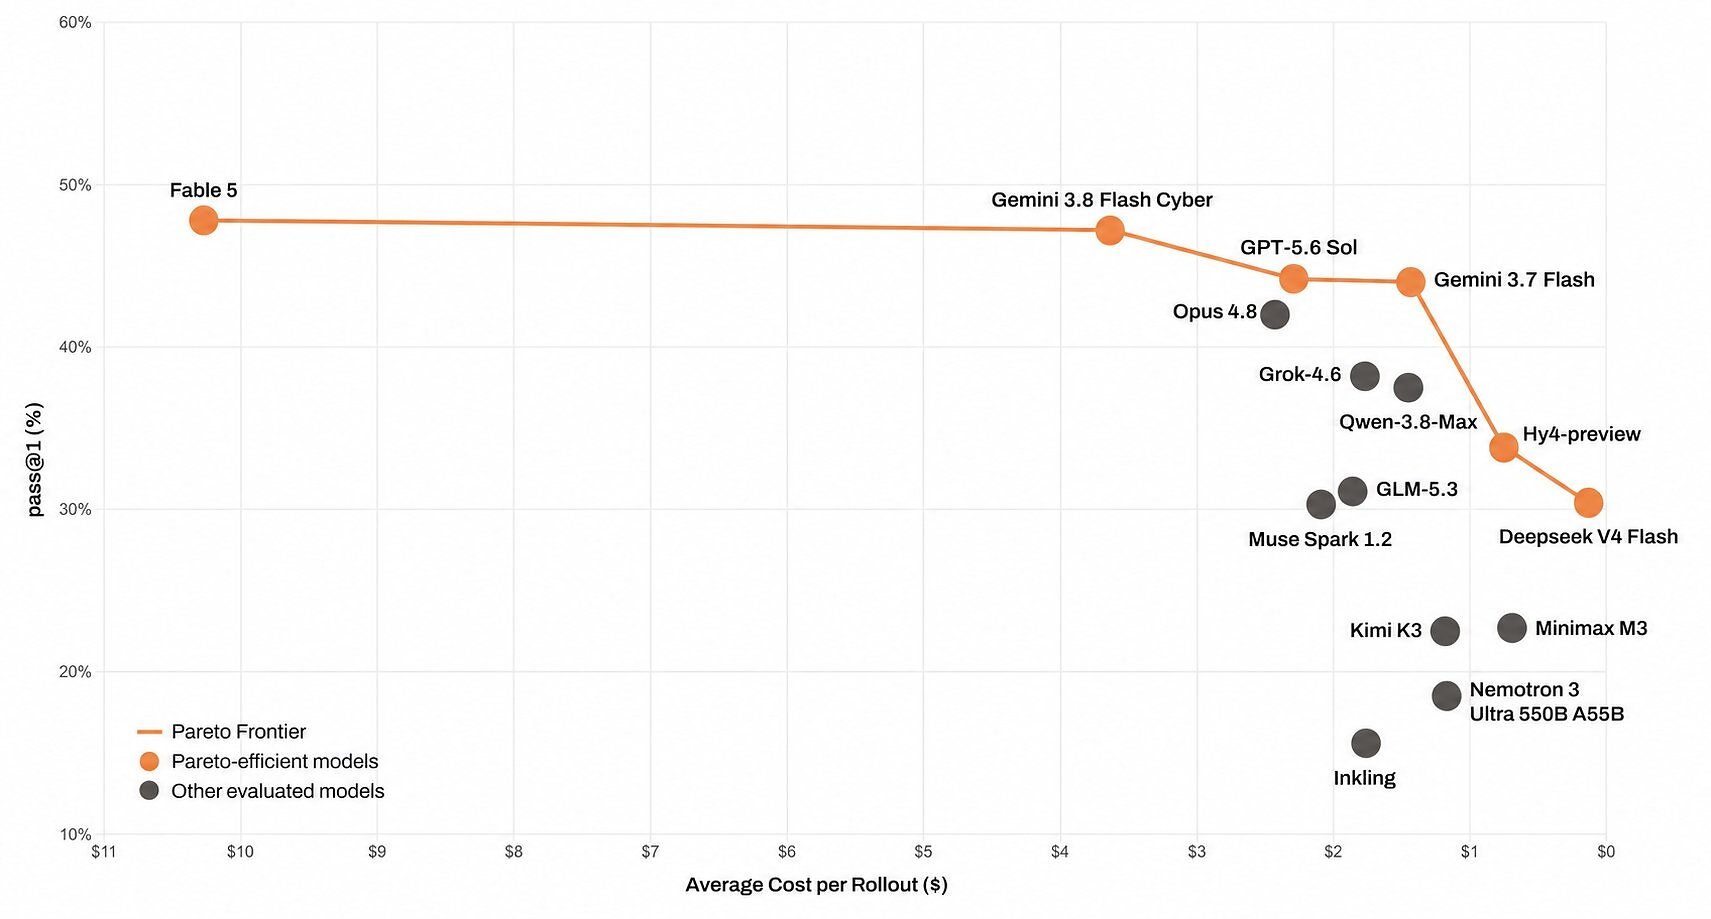
Held-out cybersecurity benchmark spans 54 weakness types; the leading agent passes less than 50% of tasks, and 18 remain unsolved. SAN FRANCISCO, Sept. 2, 2026 /PRNewswire-PRWeb/ -...
OpenAI has expanded its Codex platform with Codex Security Cloud, a cloud-hosted application security feature that continuously analyzes GitHub repositories, investigates potential...
Quick Answer: The free floor is unusually strong here: Harbor (CNCF registry with scanning/signing) and Anchore’s Grype/Syft (scanning + SBOM) cover startups at $0. Pay for Snyk (d...
<p>AWS Continuum for code vulnerabilities GA: kod aГ§Д±klarД±nД± sandbox'ta doДџruluyor, iЕџ etkisine gГ¶re sД±ralД±yor ve dГјzeltmeyi pull request olarak aГ§Д±yor.</p>
Cybersecurity has spent decades getting better at detecting events—suspicious logins, malware signatures, anomalous traffic, vulnerabilities and attempted intrusions. But today’s e...
Use SocialBu to discover ideas, generate post drafts, and schedule them across your social channels.