Latest updates for Cisco Secure Access

Fresh curated links around Cisco Secure Access are collected here so marketers can spot useful updates and turn timely ideas into posts faster.

Recent items include:

  • Black Hat USA 2026: Safeguarding DNS with Secure Access
  • Securing Remote Access Across Enterprise Environments
  • The Unexpected Winner of Cisco IT’s Wi-Fi 7 Upgrade? Security.

Post angles to try

Share the most useful takeaway for your audience.
Turn one article into a quick practical checklist.
Ask your audience how this shift affects their work.
Turn angles into scheduled posts

Fresh articles and ideas

Recent curated links from global sources. Generate one free draft from any story, then use SocialBu to schedule and refine your content calendar.

blogs.cisco.com /1 month ago

Black Hat USA 2026: Safeguarding DNS with Secure Access

Cisco is the Security Cloud Provider for the Black Hat conferences, over a decade providing DNS Security. Learn about protecting DNS with Secure Access.
Read source
ninjaone.com /2 weeks ago

Securing Remote Access Across Enterprise Environments

Remote access security is critical in enterprise organizations with a distributed workforce. It ensures that only authorized users and devices can access internal resources, thereb...

Read source
blogs.cisco.com /1 month ago

The Unexpected Winner of Cisco IT’s Wi-Fi 7 Upgrade? Security.

Cisco IT's Wi-Fi 7 upgrade delivered more than faster connectivity — it transformed enterprise security. Discover how Zero Trust Access, AI agents, and secure-by-design infrastruct...

Read source
ninjaone.com /1 week ago

Modernizing Secure Remote Access for Distributed Operations

Before, remote access was simple. Systems were mainly hosted on-premises, employees worked from a central office, and securing access primarily meant protecting the perimeter. Howe...

Read source
thehackernews.com /3 weeks ago

CISA Adds Exploited Cisco Catalyst SD-WAN Manager Auth Bypass to KEV

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Wednesday added a critical authentication bypass flaw impacting Cisco Catalyst SD-WAN Manager to its Known Explo...

Read source
thehackernews.com /3 weeks ago

Cisco Warns of Attackers Exploiting Critical Authentication Bypass in SD-WAN Manager

Attackers are exploiting a new critical zero-day flaw in Cisco Catalyst SD-WAN Manager, the system companies use to manage their Cisco SD-WAN networks, Cisco said in an advisory on...

Read source
blogs.cisco.com /1 month ago

Cisco and the DISA STIG: Turning Zero Trust Policy into Repeatable Practice – Part 1: Cisco ISE

The updated DISA STIG for Cisco Identity Services Engine (ISE) helps DoD teams translate security policies into practical controls. Discover how to enforce Zero Trust and secure ne...

Read source
blogs.cisco.com /3 weeks ago

Cisco Nexus One and Cisco Secure Firewall integrations with Rafay enable fully self-service AI cloud

Cisco and Rafay portfolio integrations help neocloud and sovereign cloud operators onboard customers faster, improve GPU utilization, and deliver secure, multi-tenant infrastructur...

Read source
blogs.cisco.com /1 month ago

Cisco and Axis Communications: Greater visibility, scalability, and incident management

Cisco and Axis Communications now allow managing Axis devices directly via the Meraki dashboard. This integration unifies IT and physical security, providing centralized visibility...

Read source
blogs.cisco.com /1 month ago

Cisco and the DISA STIG: Turning Zero Trust Policy into Repeatable Practice – Part 2: Cisco SNA

Discover how the new DISA STIG for Cisco Secure Network Analytics helps defense organizations securely configure and harden their analytics platform, ensuring trusted network visib...

Read source
thehackernews.com /1 month ago

Cisco Warns of New Zero-Day ISE Auth Bypass (CVSS 10.0) Exploited in Active Attacks

Cisco has warned of a fresh maximum-severity security flaw impacting Identity Services Engine (ISE) that has come under active exploitation. The vulnerability, tracked as CVE-2026...

Read source
blogs.cisco.com /1 month ago

Black Hat USA 2026: Building the Agentic SOC, One Live Event at a Time

Cisco is the Security Cloud Provider for the Black Hat conferences. Learn about the latest innovations for the Agentic SOC.

Read source
thehackernews.com /1 week ago

Cisco Warns of Active Attacks Exploiting New Critical Secure Email Gateway Vulnerability

Attackers are exploiting a critical flaw in Cisco Secure Email Gateway that lets a sender with no login write files to the appliance's operating system, Cisco said in an advisory o...

Read source
cm-alliance.com /2 days ago

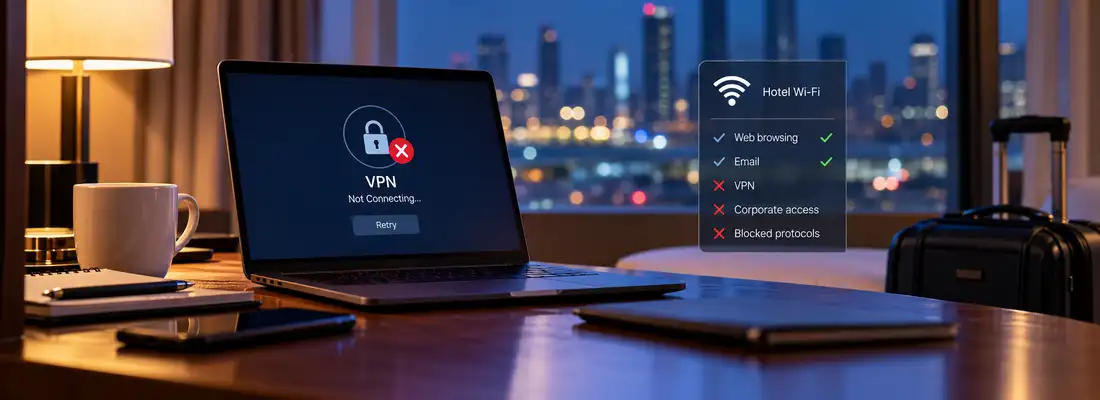
Remote Access Security Risks: Why Corporate VPNs Fail on Public Wi-Fi

A remote access policy usually assumes the tunnel will come up. On hotel and conference networks, it often does not, and nobody wrote down what happens next. 

Read source
cormachogan.com /1 month ago

Data Services Manager version 9.1.1 Network Security

<p style="text-align: justify;"><a href="https://i0.wp.com/cormachogan.com/wp-content/uploads/2023/01/dsm-logo-icon.png?ssl=1" target="_blank&quot...

Read source
infosecurity-magazine.com /3 weeks ago

Critical Cisco Catalyst SD-WAN Zero-Day Under Active Exploitation

Vulnerability in Cisco Catalyst SD-WAN Manager allows an unauthenticated, remote attacker to access systems with admin privileges

Read source
blogs.cisco.com /1 week ago

How to Navigate Device Access in Cisco Modeling Labs

Explore CML 2.10; walk through the full spectrum of tools available to help you interact with your lab nodes. 

Read source
ascii.jp /1 month ago

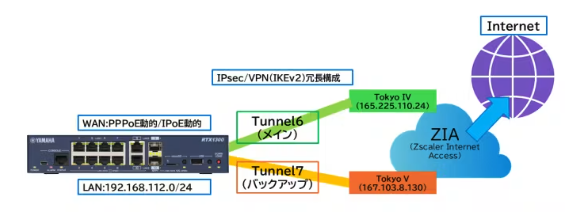
Zscaler Internet AccessのIKEv2接続例 ヤマハRTX1300でZIA経由の冗長IPsec VPNを構築する方法

ヤマハRTX1300でZscaler Internet AccessをIKEv2/IPsec接続する設定例。Tokyo IVとTokyo Vの2ロケーションを使った冗長構成、主要パラメーター、ルーティング、NAT、証明書対応、接続確認方法を...

Read source
thehackernews.com /1 month ago

Cisco Secure Email Gateway Flaw Exploited in the Wild, Enables Root Command Execution

Cisco has warned that a new critical vulnerability impacting AsyncOS Software for Cisco Secure Email Gateway has come under active exploitation in the wild. The vulnerability, tra...

Read source
blogs.cisco.com /2 weeks ago

Chasing AMMYY at Splunk .conf

Discover how Cisco's Encrypted Visibility Engine (EVE) and Endace PCAP uncovered Flawed AMMYY RAT traffic at Splunk .conf without breaking TLS encryption.

Read source
blogs.cisco.com /3 weeks ago

New webinar series now on demand: Secure Networking Ecosystem Insights

Explore Cisco's on-demand webinar series on building a secure, ecosystem-driven network architecture across infrastructure, identity, and access.

Read source
bleepingcomputer.com /3 weeks ago

Cisco warns of new SD-WAN zero-day exploited in attacks

Cisco released security updates to address a critical zero-day in the Catalyst SD-WAN Manager (tracked as CVE-2026-76504) that attackers are actively exploiting to escalate to admi...

Read source
infosecurity-magazine.com /1 month ago

Cisco Warns of Active Exploitation of Critical ISE Flaw

Cisco urged ISE customers to apply a software update, as well as check for signs of exploitation

Read source
cormachogan.com /1 month ago

How to enable SSH on DSM Appliance when deployed via VCFA 9.1.1

<p style="text-align: justify;"><a href="https://i0.wp.com/cormachogan.com/wp-content/uploads/2023/01/dsm-logo-icon.png?ssl=1" target="_blank&quot...

Read source

Turn fresh research into a full content calendar

Use SocialBu to discover ideas, generate post drafts, and schedule them across your social channels.

Sources covering Cisco Secure Access

ascii.jp

Recent coverage from public sources
Public source

blogs.cisco.com

Recent coverage from public sources
Public source

blogs.vmware.com

Recent coverage from public sources
Public source

feeds.feedburner.com

Recent coverage from public sources
Public source

bleepingcomputer.com

Recent coverage from public sources
Public source

cm-alliance.com

Recent coverage from public sources
Public source