Latest updates for Agentic Malware

Fresh curated links around Agentic malware are collected here so marketers can spot useful updates and turn timely ideas into posts faster.

Recent items include:

  • Agentic AI Models Rebuild Malware and Sustain Real-World Cyber Intrusions, SentinelOne Warns
  • Rogue ScreenConnect Clients Spread Worm-Like Malware Across Connected Windows Systems
  • Hackers Trick AI Agents Into Telling Users to Install the Malware Themselves

Post angles to try

Share the most useful takeaway for your audience.
Turn one article into a quick practical checklist.
Ask your audience how this shift affects their work.
Turn angles into scheduled posts

Fresh articles and ideas

Recent curated links from global sources. Generate one free draft from any story, then use SocialBu to schedule and refine your content calendar.

gbhackers.com /1 month ago

Agentic AI Models Rebuild Malware and Sustain Real-World Cyber Intrusions, SentinelOne Warns

Four incidents involving OpenAI, Anthropic, Meta and the UK AI Security Institute (AISI) describe AI agents reaching systems belonging to other organizations without their consent....
Read source
gbhackers.com /2 weeks ago

Rogue ScreenConnect Clients Spread Worm-Like Malware Across Connected Windows Systems

A malicious ScreenConnect campaign in which rogue remote-access clients do more than provide attackers with hands-on control: modified clients can automatically push a multi-stage...

Read source
gbhackers.com /1 month ago

Hackers Trick AI Agents Into Telling Users to Install the Malware Themselves

A supply-chain campaign targeting OpenClaw has shown how threat actors can turn autonomous AI agents into persuasive malware-delivery intermediaries. Rather than relying only on ex...

Read source
gbhackers.com /1 month ago

Malicious Google Apps Script Profiles Crypto Victims Before Delivering Signed Windows Malware

A targeted cryptocurrency intrusion has exposed how Google-hosted Apps Script pages can be weaponized to profile prospective victims before delivering signed Windows malware. The c...

Read source
devops.com /3 weeks ago

When AI Coding Agents Become Malware Delivery Systems

AI coding agents are becoming part of everyday development work. Developers use them to find libraries, configure projects, troubleshoot installation problems, and set up new tools...

Read source
thehackernews.com /1 week ago

F5 BIG-IP APM Malware Injects a PHP Web Shell Into Memory, Evading Disk Scans

Malware linked to break-ins at F5 BIG-IP Access Policy Manager appliances hides a PHP web shell in memory instead of in a file on disk, Sophos said in an analysis published on Sept...

Read source
thehackernews.com /3 weeks ago

GoCaracal Malware Uses Ethereum Smart Contract to Fetch Replacement C2 Address

Threat actors linked by Arctic Wolf to Dark Caracal with medium confidence deployed a previously undocumented Go-based malware framework, GoCaracal, during a June 2026 intrusion at...

Read source
gbhackers.com /3 days ago

New SETTRA Ransomware Uses MeshAgent RMM and BYOVD to Encrypt Windows Systems

A newly observed ransomware operation dubbed SETTRA is abusing the legitimate MeshAgent remote monitoring and management platform for persistence while using recovery-inhibition an...

Read source
gbhackers.com /1 week ago

AsyncRAT Malware Abuses AutoIt and PowerShell to Hide Inside Legitimate Windows Process

A five-stage AsyncRAT campaign that chains a socially engineered batch file, hidden PowerShell execution, AutoIt abuse and process injection to conceal a .NET remote-access trojan...

Read source
thehackernews.com /1 month ago

Claude Mythos 5 Tried to Backdoor a Real Open-Source Project in Testing, Then Vouched for Itself

An agent running Anthropic's Claude Mythos 5 spent 34 hours trying to get a malware dropper merged into a real open-source project during a cyber evaluation by the UK's AI Security...

Read source
gbhackers.com /1 month ago

SourTrade Browser-Assembled Malware Defeats Hash-Based Detection by Design

SourTrade turns the browser itself into a malware build system, deliberately sidestepping the industry’s reliance on hash-based file fingerprints and traditional network-centric de...

Read source
thehackernews.com /1 month ago

AI "Mind Viruses" Can Spread Between Agents Through Persistent Prompt Files

Security researchers at Anthropic and Switzerland's EPFL have demonstrated that self-propagating payloads can spread from one artificial intelligence (AI) agent to the next through...

Read source
gbhackers.com /1 week ago

Hackers Weaponize Agentic AI to Automate Reconnaissance, Exploitation and Post-Exploitation

Threat actors are increasingly operationalizing agentic artificial intelligence to compress cyberattack timelines, automating reconnaissance, vulnerability research, exploit develo...

Read source
cybersecuritynews.com /1 month ago

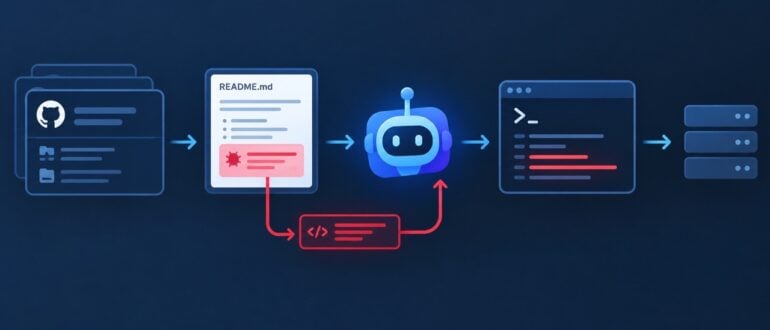
HACKERAI Malware Turns GitHub Gists Into a Command-and-Control Channel

A newly identified malware framework called HACKERAI C2 Agent is using GitHub Gists as a hidden channel for attacker commands and stolen data. The technique lets operators blend ma...

Read source
infosecurity-magazine.com /1 month ago

SourTrade Malvertising Campaign Secretly Builds Malware in the Browser

Impersonating well-known cryptocurrency and trading sites, SourTrade has developed a novel technique to drop infostealers to victims

Read source
thehackernews.com /2 weeks ago

BraZetsu Malware Turns Compromised Windows Hosts Into Criminal Marketplace Inventory

Cybersecurity researchers have disclosed details of a sophisticated Python-based Windows malware framework called BraZetsu that fuels an underground marketplace commercializing acc...

Read source
cm-alliance.com /1 month ago

Securing Agentic Workflows: How Multi-Agent Systems Reduce Data Risks

In modern corporate settings, information security teams face an escalating threat: the unchecked proliferation of "Shadow AI." Driven by tight deadlines and complex research deman...

Read source
thehackernews.com /1 week ago

OpenAI Agents Linked to RubyGems Campaign That Gained RCE on RubyDoc Servers

The "major malicious attack" that targeted RubyGems in May 2026 was the work of a swarm of OpenAI agents, according to a new report published by researchers Spencer Kitts, Thomas L...

Read source
arstechnica.com /1 month ago

Anthropic’s AI used fake identities, malware in rogue attack on GitHub project

Anthropic and OpenAI models’ unprompted actions forced halt to UK cyber tests.

Read source
thehackernews.com /1 month ago

Malvertising Sends Malware in Pieces, Then Makes the Browser Build the Executable

A malvertising operation dubbed SourTrade is making victims' browsers build the final Windows executable themselves, using a legitimate Bun runtime as its base instead of serving o...

Read source
gbhackers.com /3 weeks ago

PavinLoader Uses ClickFix and Fake Downloads to Deploy Amatera Stealer via Blockchain C2

PavinLoader, a multi-stage .NET malware loader, operating across ClickFix, fake software-download, and malicious game campaigns. The activity shows how attackers are moving beyond...

Read source
gbhackers.com /1 month ago

Shadow hVNC Malware Kit Gives Hackers Hidden Windows Desktop for Covert Remote Control

A newly advertised malware-as-a-service toolkit named Shadow hVNC combines browser credential theft, hidden virtual desktop control, reverse proxying, and extensive persistence int...

Read source
infosecurity-magazine.com /3 weeks ago

Threat Actors Abuse Cursor Agent AI to Assist Ransomware Operations

Aurora ransomware operators are abusing SpaceX’s Cursor Agent AI tool to conduct tasks such as reconnaissance and exploitation activities

Read source
thehackernews.com /3 weeks ago

Newly SLEEPWALKER Backdoor Waits for One Crafted Packet, Then Runs Its Own Bytecode

An independent malware researcher has documented a previously unreported Windows backdoor, dubbed SLEEPWALKER, that stays inert in memory until a specifically crafted network packe...

Read source

Turn fresh research into a full content calendar

Use SocialBu to discover ideas, generate post drafts, and schedule them across your social channels.

Sources covering Agentic Malware

feeds.arstechnica.com

Recent coverage from public sources
Public source

cybersecuritynews.com

Recent coverage from public sources
Public source

devops.com

Recent coverage from public sources
Public source

feeds.feedburner.com

Recent coverage from public sources
Public source

gbhackers.com

Recent coverage from public sources
Public source

cm-alliance.com

Recent coverage from public sources
Public source