Latest updates for Account Takeover

Fresh curated links around Account Takeover are collected here so marketers can spot useful updates and turn timely ideas into posts faster.

Recent items include:

  • When the attacker becomes the user: Rethinking account takeover
  • Infostealer Logs Expose Replayable AI Tokens That Can Bypass MFA
  • How to protect your accounts from AI-powered attacks

Post angles to try

Share the most useful takeaway for your audience.
Turn one article into a quick practical checklist.
Ask your audience how this shift affects their work.
Turn angles into scheduled posts

Fresh articles and ideas

Recent curated links from global sources. Generate one free draft from any story, then use SocialBu to schedule and refine your content calendar.

theregister.com /13 hours ago

When the attacker becomes the user: Rethinking account takeover

SPONSORED FEATURE: AI makes phishing easier than ever

Read source
thehackernews.com /1 month ago

Infostealer Logs Expose Replayable AI Tokens That Can Bypass MFA

Cybercriminals are hijacking artificial intelligence (AI) user accounts via information stealer logs to create "stolen keys" that grant illicit access to tools from model providers...

Read source
koreatimes.co.kr /2 weeks ago

How to protect your accounts from AI-powered attacks

A wave of account takeover attacks involving artificial intelligence (AI) against major banks is testing their defenses and putting personal cybersecurity in the spotlight. Shinhan...

Read source
bleepingcomputer.com /1 month ago

From Fake Workers to Account Recovery: The Growing Identity Verification Risk

Attackers are increasingly targeting the processes used to establish or recover identity rather than attacking the login itself. Specops explains how stronger identity verification...

Read source
bleepingcomputer.com /1 month ago

MFA's Weakest Link: Account Recovery Is the New Attack Path

MFA makes account takeover harder, but attackers are increasingly targeting the recovery processes used to reset passwords and authentication methods. Specops explains why stronger...

Read source
paymentsjournal.com /2 weeks ago

Ownership Authentication: Fighting Fraud Losses and First-Party Risk

Fraudsters no longer need to reinvent their tactics from scratch. With artificial intelligence and increasingly sophisticated access to consumer data, they can test new approaches...

Read source
infosecurity-magazine.com /1 month ago

ZeroTokens Phishing Platform Steers Attacks in Real Time

ZeroTokens gives phishing operators live control of victim sessions targeting 53 financial brands

Read source
cybersecuritynews.com /1 month ago

Tata’s B2B Platform Flaw Enables Account Takeover Just by Knowing Victim’s Phone Number

A critical authentication flaw in Tata Nexarc, a B2B procurement platform for small and medium businesses in India, allowed attackers to take over accounts by knowing only a regist...

Read source
gbhackers.com /1 month ago

StreamRAT Abuses Android Accessibility, MediaProjection and HVNC for Full Device Takeover

StreamRAT, a newly identified Android banking trojan distributed through fake free-TV streaming advertisements on Meta and TikTok. The campaign, tracked as “Steamtv Esp.,” primaril...

Read source
smartermsp.com /2 weeks ago

Cybersecurity Threat Advisory: TrustSink attack targets Microsoft Entra ID

TrustSink is an attack technique that abuses Microsoft Entra ID’s federated trust model. It uses a rogue MFA provider to intercept user credentials during legitimate login attempts...

Read source
cybersecuritynews.com /3 weeks ago

TWEAKOS Malware Turns Telegram Into a Stealer, C2 Platform and Stolen Account Marketplace

TWEAKOS steals messaging accounts and turns them into items for sale. The operation pairs a Windows stealer with a Telegram bot for managing victims and selling stolen access. The...

Read source
thehackernews.com /1 week ago

An AI Agent Found a Critical OTP Bypass in Production. The Attack Was the Easy Part.

The bug was simple: the login let you choose where your sign-in code went. Proving it on a live website was the hard part. TL;DR During an authorized assessment, an AI pentest...

Read source
thehackernews.com /1 month ago

Fake Apple Support AI Calls Target Stolen-Device Owners for Passcodes and 2FA Codes

Cybersecurity researchers have disclosed details of a phishing-as-a-service (PhaaS) platform built to strip Apple's Activation Lock from stolen devices, using rented AI voice agent...

Read source
thehackernews.com /1 month ago

N0va Phishkit Targets US and EU Businesses: A New Challenge for Identity Security

N0va is targeting organizations across North America and Europe with phishing campaigns that impersonate trusted services and abuse legitimate authentication flows. Successful atta...

Read source
cybersecuritynews.com /4 weeks ago

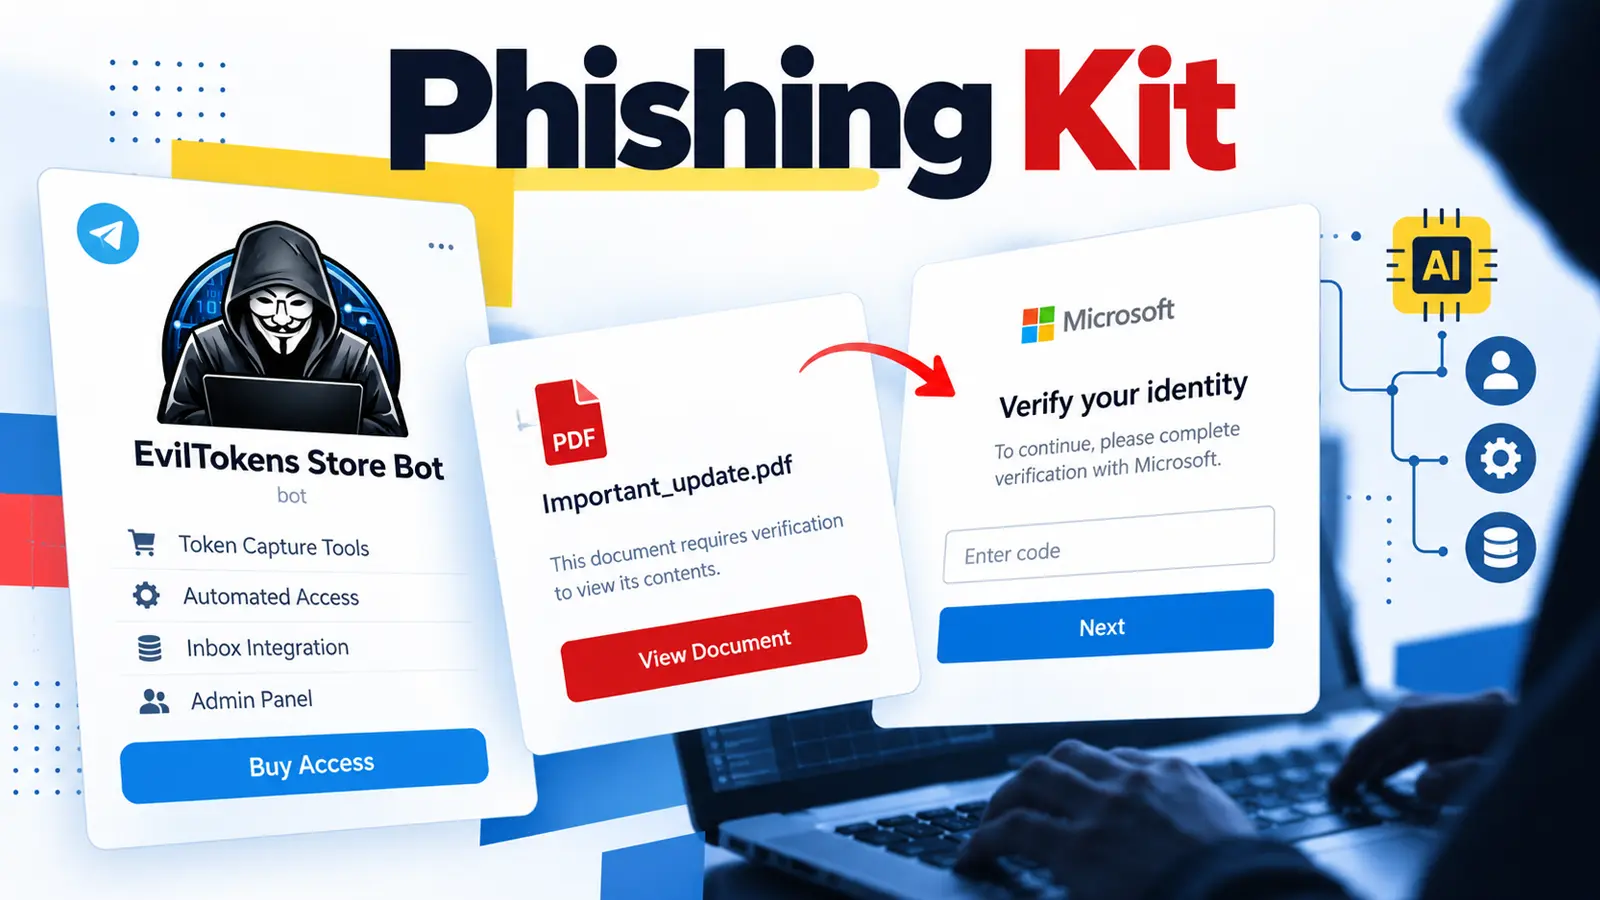
The Phishing Kit That Turned Microsoft’s Login Flow Into an AI-Powered Fraud Machine

EvilTokens turns a Microsoft sign-in into a route to corporate email fraud. The phishing kit, first seen in February 2026, tricks people into approving an attacker’s login through...

Read source
cybersecuritynews.com /3 weeks ago

Hackers Turn One Compromised Account Into Access to Azure DevOps and Kubernetes

A single compromised account can open the door to an entire cloud estate. A recent investigation shows how an attacker used one compromised identity to move from password recovery...

Read source
cybersecuritynews.com /3 weeks ago

TrustSink Attack Uses Rogue MFA Provider to Steal Microsoft Entra Passwords During Legitimate Logins

TrustSink is a newly disclosed identity attack that turns a trusted MFA step into a password-stealing trap. Rather than sending victims to a clearly fake website, it places a convi...

Read source
thehackernews.com /2 weeks ago

Fake ChatGPT, Gemini, and Claude Ad Portals Capture Credentials and MFA Codes

Cybersecurity researchers have disclosed details of a "human-operated phishing platform" that impersonates advertising products for artificial intelligence (AI) chatbots like Googl...

Read source
cybersecuritynews.com /1 week ago

Google AitM Phishing Kit Uses WebSockets to Bypass MFA in Real Time

A Google account phishing kit uses live WebSocket connections to guide victims through fake sign-in screens, relay authentication requests, and steal authenticated sessions. The ca...

Read source
fox59.com /3 weeks ago

Crooks using dual factor authentication for scams

WXIN/WTTV — Scammers have found a way to use a security tool that’s meant to keep our accounts secure for their schemes. According to Scamicide, online crooks are now using dual fa...

Read source
gbhackers.com /2 weeks ago

Fake ChatGPT, Claude and Gemini Ads Use Browser-in-the-Browser Phishing to Steal Accounts

A human-operated phishing platform impersonating AI advertising products to steal credentials and manipulate multifactor authentication workflows. The operation targets advertising...

Read source
cybersecuritynews.com /1 month ago

Hackers Impersonate ChatGPT Subscription Alerts to Steal OpenAI Account Credentials

ChatGPT subscription notices have become the latest cover for credential-stealing emails. The campaign uses a familiar billing problem to push recipients toward a fake sign-in page...

Read source
bleepingcomputer.com /2 weeks ago

Fake ChatGPT, Gemini Sites steal advertising accounts, MFA codes

A new campaign targeting ad account managers uses fake ChatGPT, Gemini, Claude, and Perplexity sites that steal login credentials and multi-factor authentication (MFA) codes throug...

Read source
blog.knowbe4.com /2 weeks ago

Threat Actors Abuse Trusted Accounts and Internal Tools to Launch Convincing BEC Attacks

Attackers are continually finding new ways to refine business email compromise (BEC) attacks, according to Douglas McKee, Director of Vulnerability Intelligence at Rapid7. When at...

Read source

Turn fresh research into a full content calendar

Use SocialBu to discover ideas, generate post drafts, and schedule them across your social channels.

Sources covering Account Takeover

smartermsp.com

Recent coverage from public sources
Public source

blog.knowbe4.com

Recent coverage from public sources
Public source

cybersecuritynews.com

Recent coverage from public sources
Public source

feeds.feedburner.com

Recent coverage from public sources
Public source

fox59.com

Recent coverage from public sources
Public source

gbhackers.com

Recent coverage from public sources
Public source