SSO Without Giving the Server Your Keys
Single sign-on is a solved problem. You redirect to an identity provider, it tells you who the person is, you mint a session. Every framework has a library for it. Then you try it...
Search fresh public links, source activity, and ready-to-use post angles for Authentication.
Fresh curated links around Authentication are collected here so marketers can spot useful updates and turn timely ideas into posts faster.
Recent items include:
Recent curated links from global sources. Generate one free draft from any story, then use SocialBu to schedule and refine your content calendar.
Single sign-on is a solved problem. You redirect to an identity provider, it tells you who the person is, you mint a session. Every framework has a library for it. Then you try it...
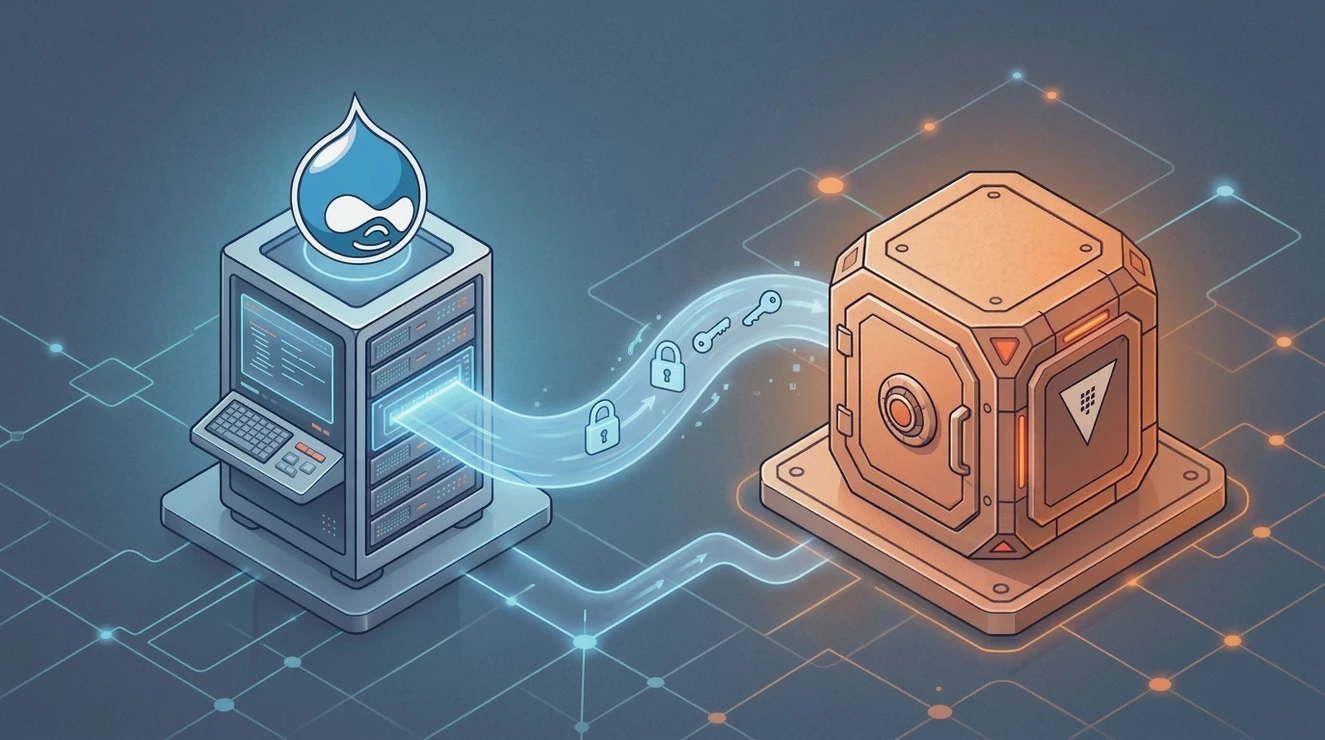
Every Druxt site I have built signs people in by sending them somewhere else to do it: out to Drupal's login page, on to a consent screen, and eventually back. With Druxt Auth 0.5....
Every app eventually needs to answer two questions: "who is this person?" and "what are they allowed to do?" Many tutorials either focus on integrating a specific authentication pr...
Two XenForo Flaws in One Release: Empty OAuth2 Credentials and a Passkey That Belonged to Someone Else Two authentication paths, one shared weakness in assumptions Xen...
Sign-In with Ethereum, or SIWE, authenticates an Ethereum account to an off-chain service using a signed message.Continue reading on Medium »
Credentials still travel by email and by Slack on projects that are otherwise carefully built. Every integration with an external service needs them, and forwarding them from one p...
Upwork Scout has no password field. It never had one. When I was sketching the signup flow I told myself I was removing work: no hashing, no reset flow, no rules about symbols and...
I need a brand-new login page built for our in-house Loan CRM. Security is the priority: after the usual username-and-password step, users must receive a one-time code and be able...
Every login on a BOA account is a key of one kind, and the ring holds six of them: your own panel login and your oN.ftp shell open everything; a colleague's login to the Ægir panel...
Login looks simple until you’re building password resets, email verification, MFA, social providers, session management, and the enterprise SSO your first big customer asked for la...
Spring Authorization Server now lives inside Spring Security 7 under the same Maven coordinates, so the upgrade is a version bump. This server-side guide covers enabling DPoP and R...
For years, authentication has been built around a simple question: Is this really the customer? That question is becoming harder to answer, and increasingly, it may not even be the...
Treat passwordless phone login as a small SMS OTP state machine, not as two Express or Node.js handlers named "send" and "check." For an edtech contact form, the useful decision ru...
QR-code login looks safe. You scan a code, approve on your phone, and the computer is signed in. No password typed, nothing to phish. We run ClientN, an anonymous sign-in service,...
Stolen credentials served as the entry point in 22% of breaches last year, and in attacks on basic web applications that figure climbs to 88%. Those numbers describe a password pro...
Short answer: for a property-management login, start with a dedicated SMS OTP flow, then keep direct SMS send for exceptional notices. The OTP endpoint owns code generation and mat...
Auth0 (Okta’s developer line) remains the best AaaS for most teams the ecosystem and enterprise-credibility benchmark while Entra External ID and Amazon Cognito win the price-floor...
Learn how to combine native Experience Cloud capabilities around the Account object to route authentication, align data access, and scale onboarding through configuration.
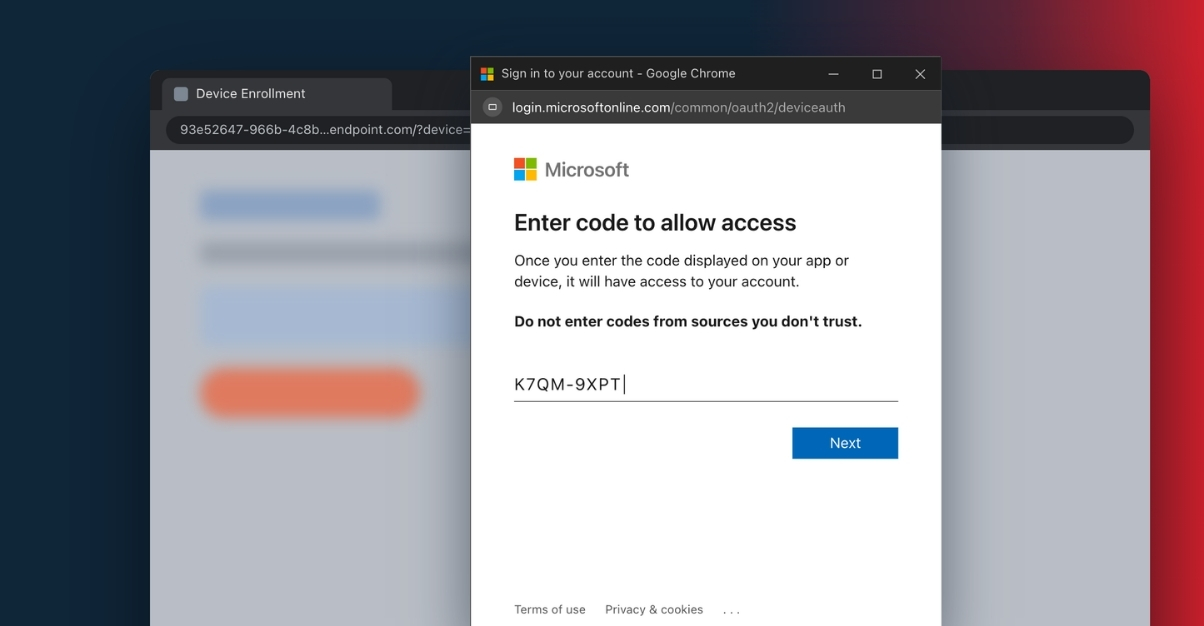
Cofense Phishing Defense Center (PDC) analysts uncovered a device code phishing campaign that impersonates trusted brands, including Microsoft, Syncfusion, and Mimecast, to trick u...
Use SocialBu to discover ideas, generate post drafts, and schedule them across your social channels.