New ClosedQuorum Windows malware uses AI for attack decisions
A new Windows malware named ClosedQuorum uses Google Gemini, DeepSeek, Qwen, and Mistral AI models to autonomously determine the actions to take during post-compromise stages of an...
Search fresh public links, source activity, and ready-to-use post angles for Ai Malware.
Fresh curated links around AI Malware are collected here so marketers can spot useful updates and turn timely ideas into posts faster.
Recent items include:
Recent curated links from global sources. Generate one free draft from any story, then use SocialBu to schedule and refine your content calendar.
A new Windows malware named ClosedQuorum uses Google Gemini, DeepSeek, Qwen, and Mistral AI models to autonomously determine the actions to take during post-compromise stages of an...
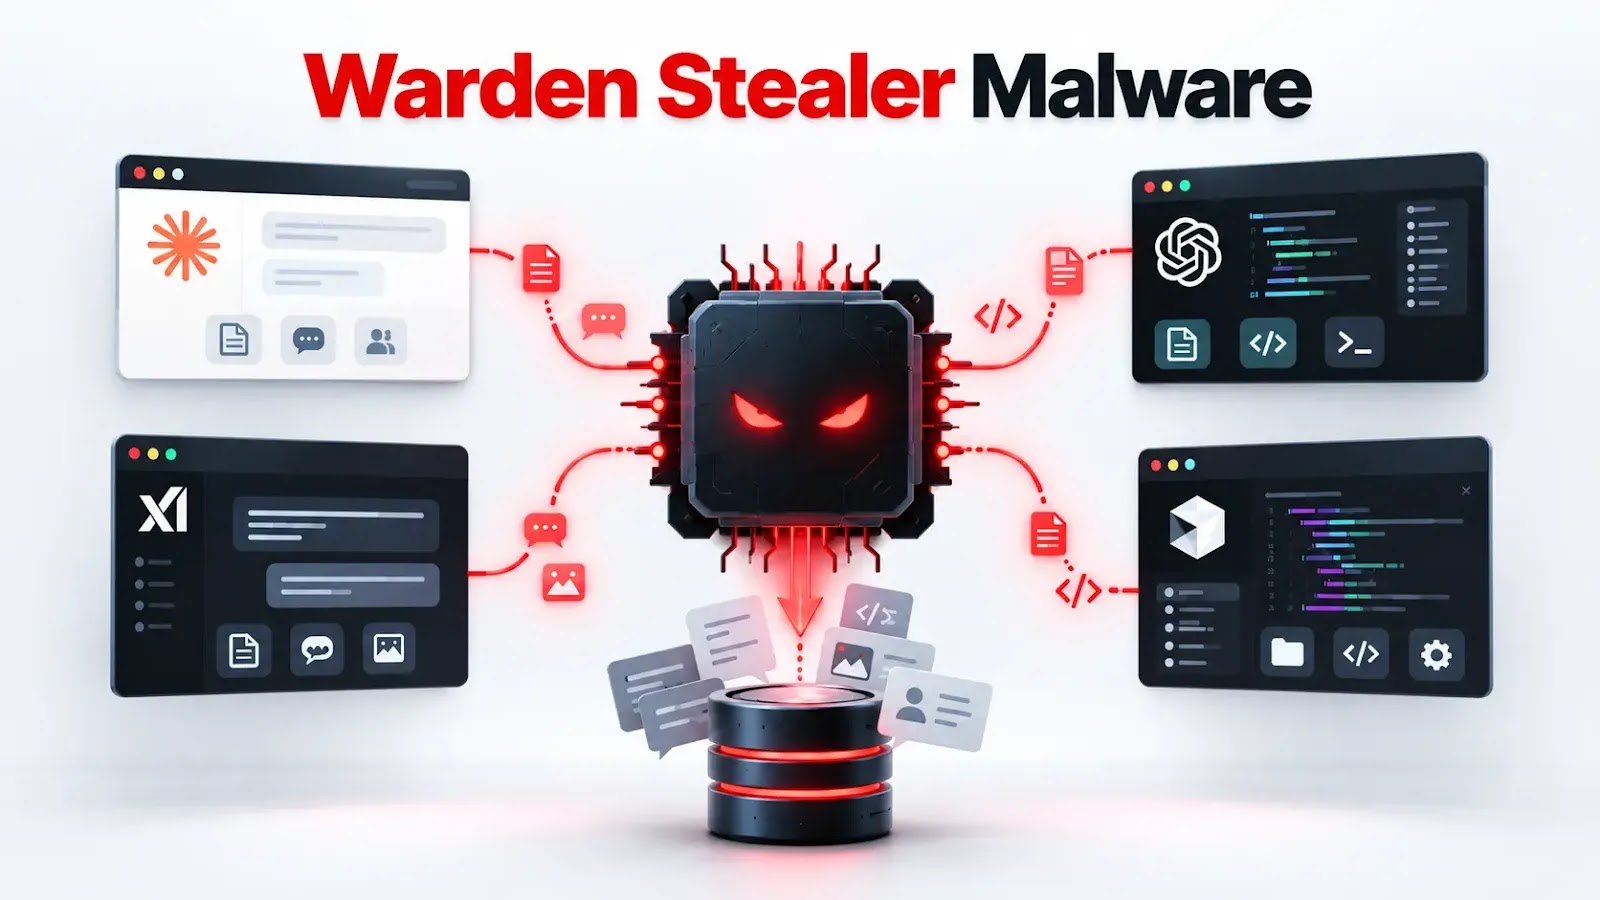
Malware is bad. Malware that uses AI to steal login credentials and crypto wallets is even worse.
Warden Stealer as a rapidly growing malware-as-a-service operation targeting data stored by AI assistants and coding agents, including Claude, Codex, Grok, and Cursor. The Rust-bas...
Cybersecurity researchers have identified a threat actor that leverages artificial intelligence throughout the attack lifecycle to conduct search engine optimization (SEO) fraud, s...
A newly documented Android banking trojan named RATHat is demonstrating how generative AI can be operationalized inside mobile malware. The threat uses Google Gemini models to navi...
A new Android malware called RatHat has been discovered, targeting users with an AI-powered subsystem that helps operators remotely navigate compromised devices. [...]
AI-powered malware is making a familiar security problem harder to contain. Instead of keeping the same code long enough for antivirus tools to recognize it, these programs can alt...
Cybercriminals are exploiting the popularity of ChatGPT, Claude, and Gemini by spreading fake AI apps that secretly install malware on ... Read More
A fake Web3 accelerator has been observed pushing information stealers and backdoors to Windows and macOS systems using malicious npm packages under the pretext of offering free ar...
A Windows malware called CLOSEDQUORUM is built to take orders from a vote of up to four AI models instead of an attacker's server, Cisco Talos said on September 22. The models can...
A cryptomining campaign targeting exposed AI services is using PoeLLM malware to turn compromised servers into scanners and exploit launchpads. [...]
You probably don’t give much thought to the smart functionality of ovens, washers, TV boxes. But Anthropic has—and it believes such IoT devices are ripe for AI exploitation. Ho...
Criminals are now selling malicious AI tools for use in cyberattacks, according to researchers at Trellix. These tools dramatically lower the barrier for unskilled crooks to launch...
Attackers are impersonating popular AI products to distribute malware, steal browser sessions, and compromise business accounts. ANY.RUN linked 1,258 public sandbox analyses to fak...
Symantec warned that Aoki can steal API keys and tokens from a number of popular AI coding assistants, including Claude and Gemini
Cisco Talos researchers created a new framework for identifying malware and hacking tools that rely on AI chatbots—and quickly discovered something unusual.
'first' publicly documented Windows implant to use LLMs for C2
Aoki, also known as Aokigahara, is a data-stealing malware that has added credentials for AI tools to its growing list of targets. Recent versions seek local files and session data...
Scammers are using AI to generate phishing pages that impersonate antivirus products, according to Malwarebytes.
Lead Analysts: Shikhar Dalela, Maddhav Grandy and Jeewan Singh Jalal
Threat actors are adapting malware not only for conventional endpoint defenses and sandboxes, but also for large language model-powered tools increasingly used to triage suspicious...
A financially motivated threat actor is using open-source AI agent frameworks to attack hundreds of online retailers at scale, stealing more than 600,000 credit card records. [...]
A new botnet malware called Carbonato is targeting insecure hosts running Docker daemons to install the Hermes Agent AI framework and take control. [...]
Anthropic warned that rogue “AI worms” are months away from the ability to self-replicate and autonomously infect user devices such as home appliances and other internet-connected...
Use SocialBu to discover ideas, generate post drafts, and schedule them across your social channels.