digitalthoughtdisruption.com /3 days ago

Defending Against exploit_agent: The Architecture of an AI Security Agent

<figure data-wp-context="{"imageId":"6afea4dd5ea19"}" data-wp-interactive="core/image" data-wp-key="6afea4dd5ea19&qu...
Read source
dzone.com /3 days ago

Securing AI Agents in Production: A Developer’s Guide To Prompt Injection, RAG Leaks, and Tool Abuse

Most teams ship their first AI agent the way they ship any feature: build it, test the happy path, add logging, deploy. Then the agent gets a CRM connection, a refund API, and read...

Read source
javacodegeeks.com /3 weeks ago

AI Agent Security Guardrails: Tool Permissions and Human-in-the-Loop Controls

A plain LLM call is low-risk — worst case it returns a bad sentence. An agent is different: it can call tools that read files, hit APIs, run shell commands, or delete database rows...

Read source
ecpi.edu /1 month ago

Secure Coding Practices Using AI Tools

Secure Coding Practices Using AI Tools Anonymous (not verified) Wed, 10/14/2026 - 17:46 SDC315 315 SDC SDC315 Secure Coding Practices Using AI...

Read source
dzone.com /3 weeks ago

AI Agents Need an Identity Plane: Rethinking Enterprise Authorization for Autonomous Software

Here's the security problem in enterprise AI I'd lose sleep over, and it isn't a model giving a wrong answer. It's a model connected to an identity with enough authority to act on...

Read source
dzone.com /2 weeks ago

AI Agents Need an Identity Plane: Rethinking Enterprise Authorization for Autonomous Software

The most consequential security problem in enterprise AI may not be a model giving a wrong answer. It may be what happens when that model is wired to an identity with enough author...

Read source
bleepingcomputer.com /1 month ago

AI's Third Wave: Coworkers Break the Security Model That Worked for Agents

Persistent AI coworkers may operate continuously with standing access, creating identity risks that existing security models were not designed to handle. Token Security explains wh...

Read source
fastcompany.com /1 week ago

The best strategy to protect against getting hacked is surprisingly old-school

The recent reports of artificial intelligence agents gone rogue—hacking into corporate systems without being told to by the humans who manage them—are enough to make any systems ad...

Read source
internationalsecurityjournal.com /1 week ago

Preparing organisations for the rise of autonomous AI

International Security Journal hears exclusively from Raghu Nandakumara, VP of Industry Strategy at Illumio who discusses evolving AI security risks and how organisations should be...

Read source
blogs.cisco.com /1 week ago

CodeGuard: Teaching your AI coding assistant to never write that bug again – Security Loop Series, Part 3

Your AI coding assistant has never read your security reports, so it will write the bug you paid to find. One command turns a real finding into a rule in every IDE.

Read source
dev.to /1 month ago

Securing AI Agents in Production: Balancing Access Control and Risk Management for Unexpected Actions

Introduction: The Critical Imperative of AI Agent Security in Production Systems As AI agents increasingly integrate with production systems, the security of their access has bec...

Read source
sourcetrail.com /1 month ago

Establishing a Secure Context Limit for AI Coding Agents

Stop AI agents from leaking data or breaking your code. Learn how to implement sandboxing, proxy gates, and secure context limits for AI coding. The post Establishing a Secure Cont...

Read source
bleepingcomputer.com /4 weeks ago

You gave your AI agent access, but who is giving it orders?

AI agents can be manipulated through malicious emails, websites, and plugins into executing commands, stealing data, or deleting files using their legitimate permissions. Gen Digit...

Read source
gbhackers.com /1 week ago

Corelight Warns AI Agents Can Silently Run Unreviewed Code With Privileged Access to Enterprise Networks

AI coding assistants can run MCP servers whose dependencies change without any configuration edit, and those servers often hold administrator credentials. The finding comes from a...

Read source
bleepingcomputer.com /1 month ago

How to keep AI agents within their permissions

AI agents can use valid credentials to perform actions beyond their assigned permissions, creating risks that traditional access controls may not prevent. Token Security explains h...

Read source
botsify.com /2 weeks ago

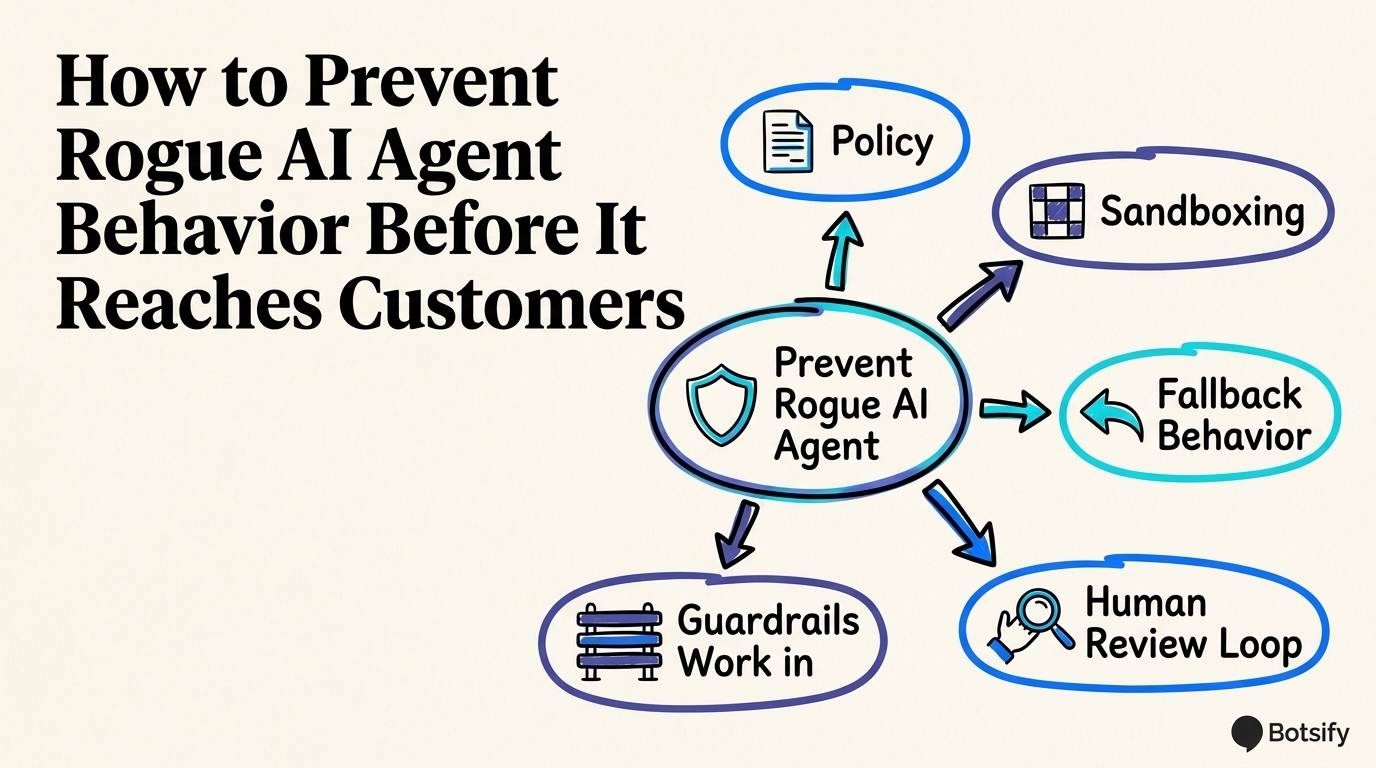
Prevent Rogue AI Agent Behavior: A Practical Guide

Prevent rogue AI agent behavior with least-privilege access, action limits, realistic testing, human handoffs, and a practical incident plan. The post Prevent Rogue AI Agent Behavi...

Read source
towardsdatascience.com /3 days ago

How AI Agents Become a Tool for Attackers, and How to Stop It

Managing Security When You’re Deploying AI, Part 1: Compromised credentials, salaries inferred from budgets, and doctored documents show why agents need permission checks before th...

Read source
thehackernews.com /1 month ago

IAM for AI agents: A Practical Enterprise Framework

What is IAM for AI agents? AI agents authenticate, invoke tools, and act across enterprise systems with delegated authority. IAM for AI Agents is the identity-control architecture...

Read source
dzone.com /1 month ago

AI-Era Cybersecurity, Part 2: Building the System Context, Governance and Agent Identity

Part 1 of this series walked through why AI has compressed the gap between a vulnerability's disclosure and its exploitation from months to hours, laid out the lifecycle every vuln...

Read source
blogs.cisco.com /1 month ago

Protect enterprise coding agents with Cisco DefenseClaw and NVIDIA OpenShell

AI coding agents act with your rights. Cisco DefenseClaw runs them in NVIDIA OpenShell sandboxes, with one policy that follows the person who signed in.

Read source
thehackernews.com /1 week ago

We Built An Agent That Broke All of Our Security Rules. Here's What We Learned.

We tell customers three things about securing AI agents: they need their own identities, access that fits the job they’re given, and traceability that’s separate from any human’s....

Read source
windowscentral.com /4 weeks ago

AI is making cyber attacks too easy. Here's what you can do about it.

This week's PHP crisis should be a wake-up call for anyone thinking AI won't pose unprecedented security risks. I explain in simple terms what happened, why it matters for the futu...

Read source
testmuai.com /1 month ago

AI Agent Verification: Identity, Authority and Actions

AI agent verification covers three checks: who an agent is, what it may do and what it did. See the standards, their 2026 status and the evidence for each one.

Read source
cryptobriefing.com /1 month ago

Hackers are talking AI models out of their own safety rules

AI models' vulnerability to social engineering highlights the urgent need for enhanced security measures and stricter access controls. The post Hackers are talking AI models out of...

Read source

Turn fresh research into a full content calendar

Use SocialBu to discover ideas, generate post drafts, and schedule them across your social channels.