How to Build an API Security Governance Program
API security remains a critical blind spot today, as nearly all organizations have faced an API-related incident, yet only 21% have robust attack detection capabilities. Establishi...
Search fresh public links, source activity, and ready-to-use post angles for Api Security.
Fresh curated links around api security are collected here so marketers can spot useful updates and turn timely ideas into posts faster.
Recent items include:
Recent curated links from global sources. Generate one free draft from any story, then use SocialBu to schedule and refine your content calendar.
API security remains a critical blind spot today, as nearly all organizations have faced an API-related incident, yet only 21% have robust attack detection capabilities. Establishi...
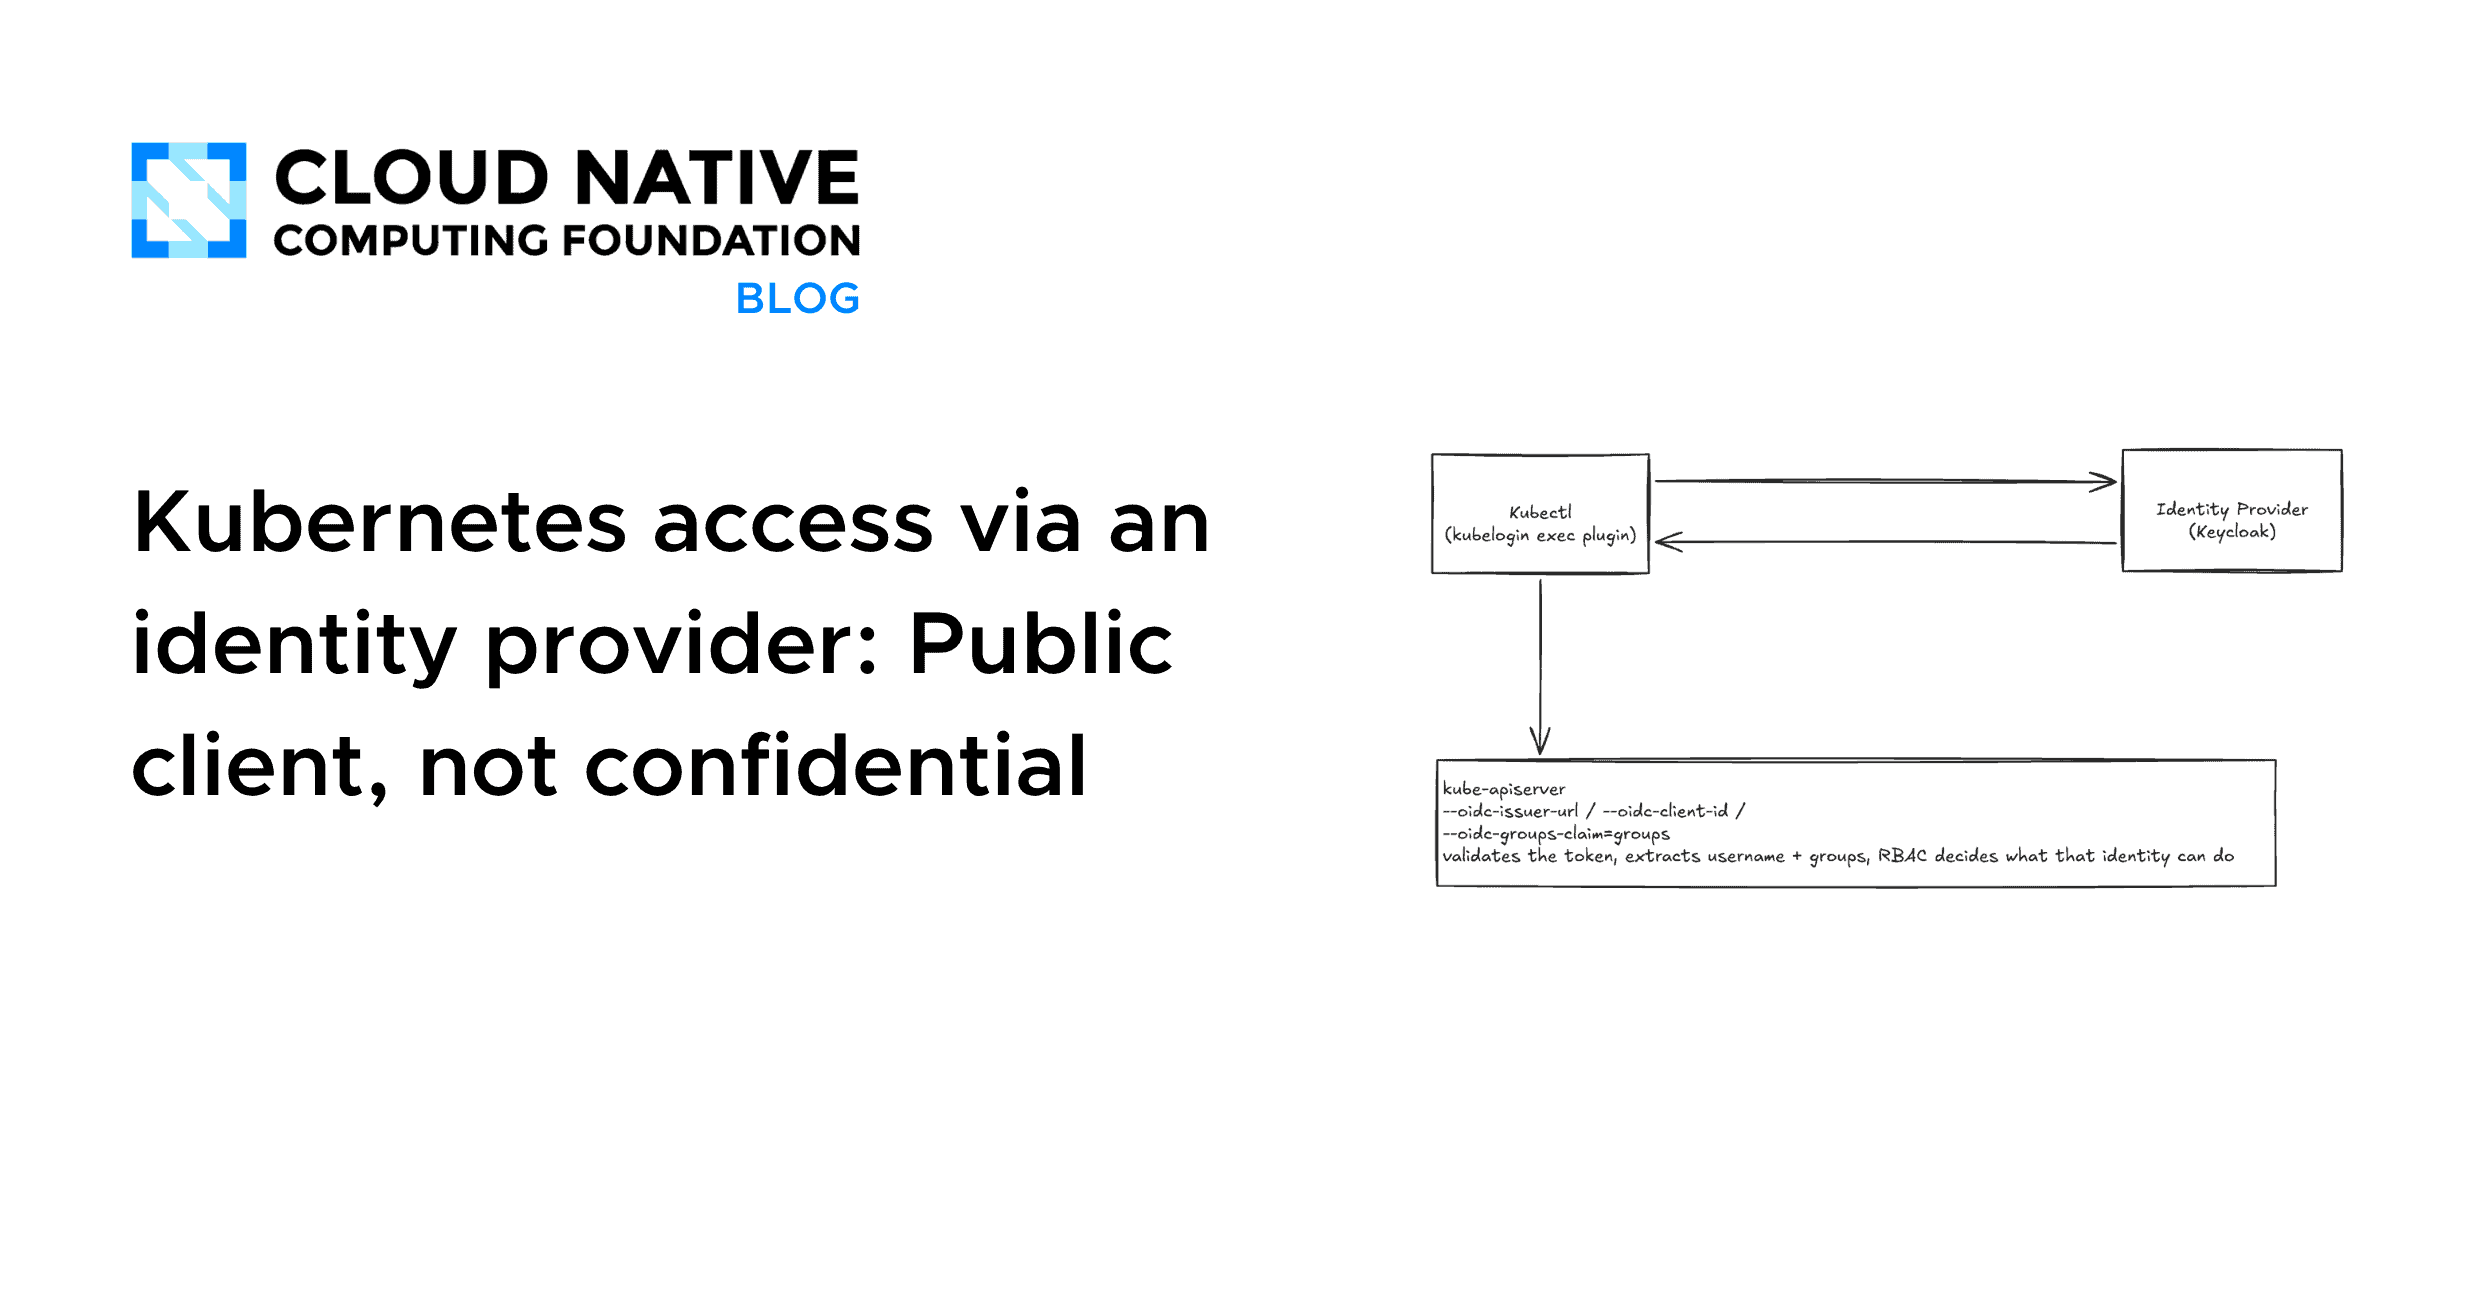
My previous guide used ingress-nginx annotations to put internal Kubernetes services behind OAuth2 Proxy. It was written for an ingress-nginx setup. That controller is being retire...
Stop API breaches! Learn how to integrate WAF and WAAP to block SQLi, XSS, and bots. Protect your data and ensure PCI DSS compliance today. The post Comprehensive Guide to API Thre...
A few months ago I got tired of hearing the same sentence in interviews and student forums: "we're on the cloud, so we're secure." I understand where it comes from. AWS handles the...
If you’re building an AI agent, there isn’t one authorization method that is right for every situation.Continue reading on Medium »
A critical security flaw in WSO2 API Manager has come under active exploitation in the wild, according to findings from watchTowr. The vulnerability, tracked as CVE-2026-5430 (CVS...
Salt Security and Traceable anchor dedicated discovery-plus-runtime defense, 42Crunch owns design-time contract security, and the edge giants (Akamai with Noname inside, Cloudflare...
Access control belongs on the same day-zero checklist as networking and storage. On most on-prem clusters, it never makes the list. The Identity Gap Managed cloud Kubernetes ships...
Broken Object Level Authorization (BOLA) occurs when a REST API exposes an object identifier—such as an account, transaction, or loan ID — without verifying whether the authenticat...
AI infrastructure is rapidly becoming a high-value enterprise attack surface. Attackers targeting LiteLLM AI gateways, RAGFlow retrieval platforms, and Kestra workflow orchestratio...
In cloud-centered environments, establishing trust between workloads is fundamental to securing machine-to-machine communication. Traditional approaches such as API keys, shared se...
The migration every banking app was forced to make, and why the client-side token is only half the jobContinue reading on Medium »
YApi — платформа документации API, мок-сервера и тестов с 27 тысячами звёзд — не обновлялась с 2022 года. На новом Node.js у неё ломаются токены, клиент не собирается, нужное ей ра...
Auth0 (Okta’s developer line) remains the best AaaS for most teams the ecosystem and enterprise-credibility benchmark while Entra External ID and Amazon Cognito win the price-floor...
zkAPI keeps prompts awayy from payment servers, but AI providers can read submitted content and may connect sessions through repeated details.
Добрый день, дорогие читатели!Мы с Вами просканировали основные типы активов. Можно выпустить гайды по сканированию сетевого оборудования и виртуализации, но здесь мне нечего добав...
Attackers are exploiting a critical flaw in F5 BIG-IP Access Policy Manager (APM) that lets them run code on a BIG-IP system without logging in, F5 says. The flaw, CVE-2026-94127,...
Claude Code reads files, runs shell commands, invokes MCP tools, and acts through the credentials available on a developer’s machine. Anthropic’s new Compliance API endpoints give...
Apiiro leads risk-graph depth, ArmorCode aggregation breadth, and the acquisition wave (Dazz into Wiz, Bionic into CrowdStrike, Enso into Snyk) tells you where ASPM is going: into...
Cybercriminals are hijacking artificial intelligence (AI) user accounts via information stealer logs to create "stolen keys" that grant illicit access to tools from model providers...
AI agents can use valid credentials to perform actions beyond their assigned permissions, creating risks that traditional access controls may not prevent. Token Security explains h...
The open-source AI coding project OpenCode has notified a small number of users that API keys they used with external providers were exposed in a security breach. [...]
Ethereum’s zkAPI is now live on mainnet, turning an earlier zero-knowledge API payment proposal into a working implementation for private, prepaid access.
Why zero knowledge credits, boundary controls and selective evidence matter more than blanket secrecyContinue reading on Medium »
Use SocialBu to discover ideas, generate post drafts, and schedule them across your social channels.