Cybersecurity Threat Advisory: Milk Dragon AiTM phishing kit
Security researchers have identified Milk Dragon (also known as NaiLong), a Phishing-as-a-Service (PhaaS) platform being used in large-scale social media fraud campaigns. By impers...
Search fresh public links, source activity, and ready-to-use post angles for Adversary-In-The-Middle Phishing Kit.
Fresh curated links around adversary-in-the-middle phishing kit are collected here so marketers can spot useful updates and turn timely ideas into posts faster.
Recent items include:
Recent curated links from global sources. Generate one free draft from any story, then use SocialBu to schedule and refine your content calendar.
Security researchers have identified Milk Dragon (also known as NaiLong), a Phishing-as-a-Service (PhaaS) platform being used in large-scale social media fraud campaigns. By impers...
Phishing kits are no longer limited to copying a familiar login page and waiting for a victim to enter credentials. Attackers are increasingly building filtering, session managemen...
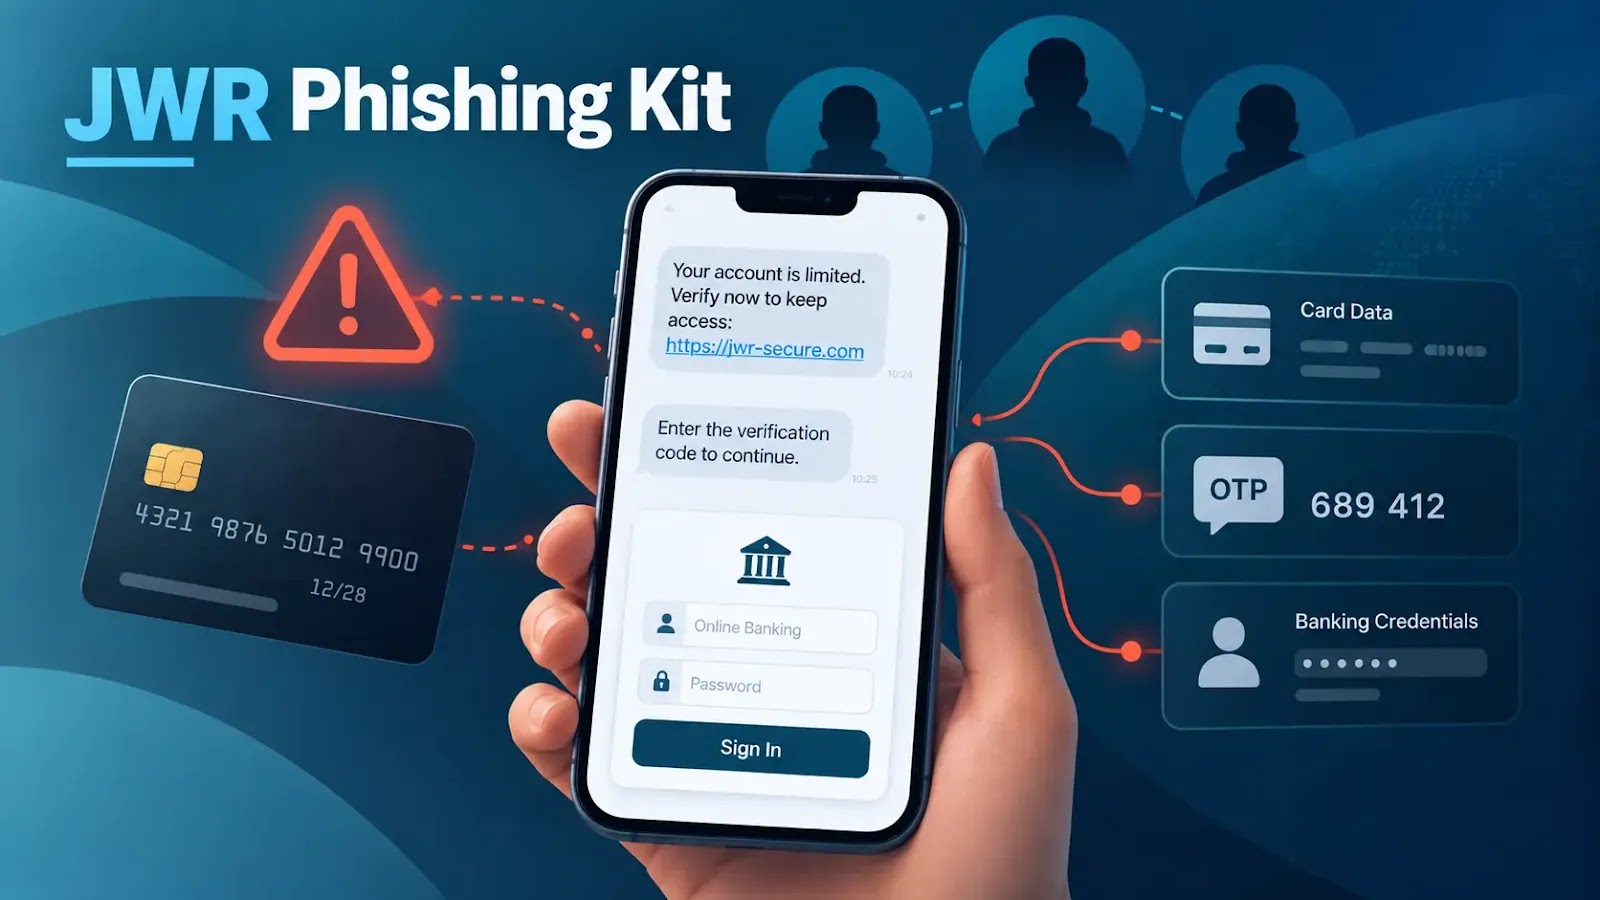
A large-scale SMS phishing campaign linked to the Smishing Triad is using a sophisticated phishing kit dubbed JWR to harvest payment-card data, one-time passwords, online-banking c...
Cybersecurity researchers have disclosed details of a new adversary-in-the-middle (AitM) phishing toolkit called NovaCookies that's used as a proxy to redirect Microsoft 365 sign-i...
A new phishing platform called “JWR” gives attackers real-time control over social engineering attacks, according to researchers at Cisco Talos. The kit livestreams the phishing pa...
ZeroTokens gives phishing operators live control of victim sessions targeting 53 financial brands
Outsider phishing kit generated 700 new pages after a Google-led disruption
A Google account phishing kit uses live WebSocket connections to guide victims through fake sign-in screens, relay authentication requests, and steal authenticated sessions. The ca...
A newly analyzed phishing operation is using server-side polymorphism to generate a distinct credential-harvesting page for virtually every request, undermining detection approache...
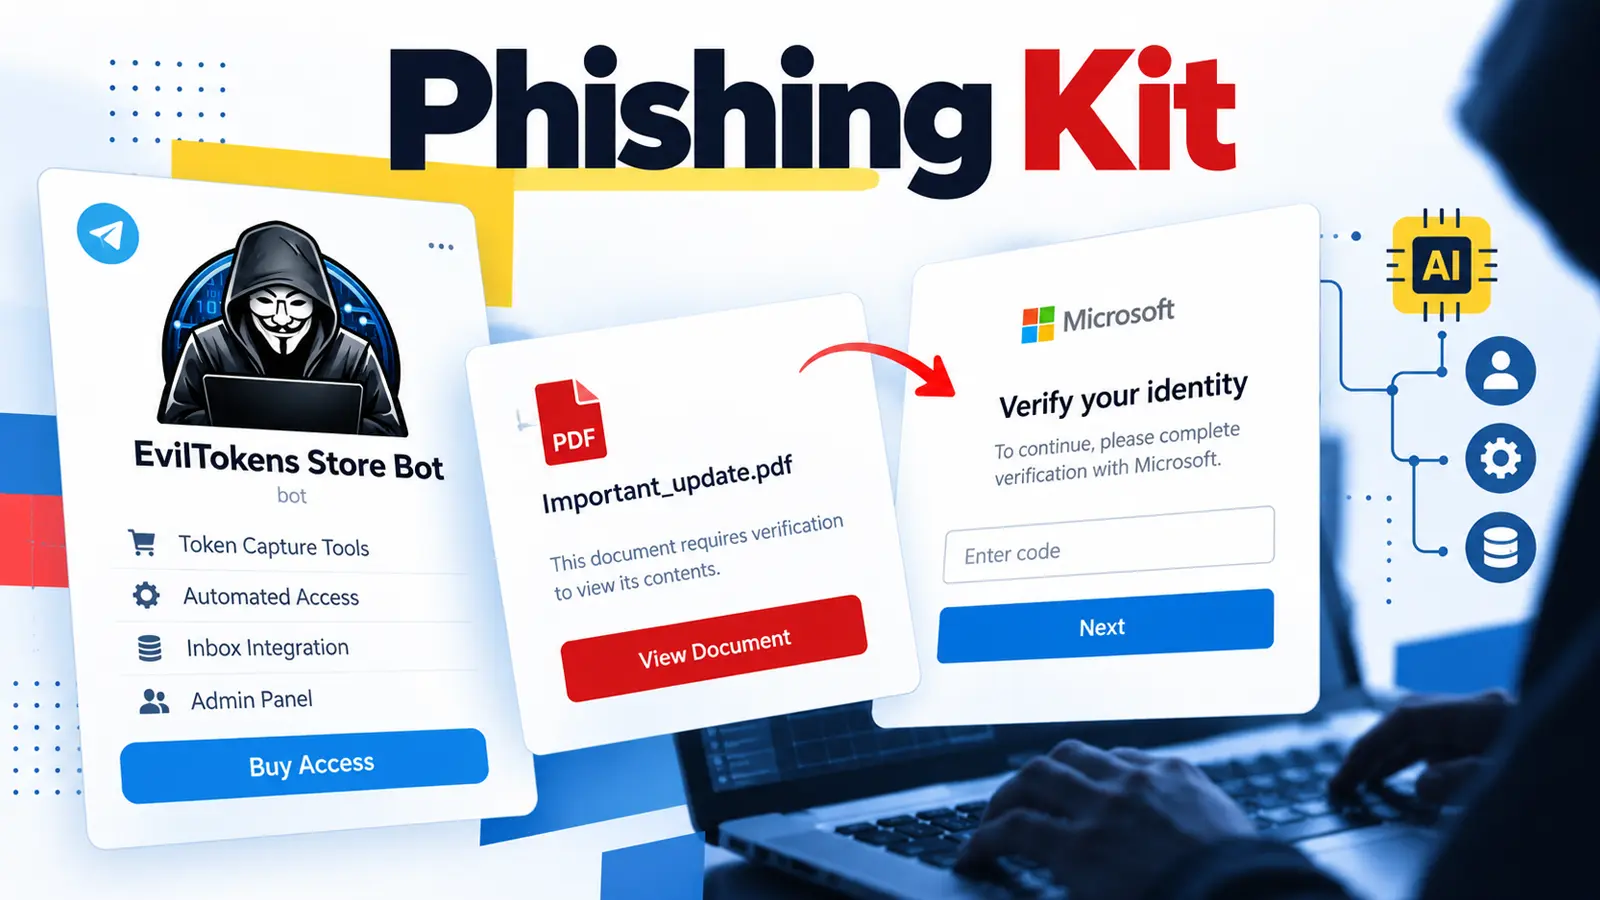
EvilTokens turns a Microsoft sign-in into a route to corporate email fraud. The phishing kit, first seen in February 2026, tricks people into approving an attacker’s login through...
A newly uncovered phishing-as-a-service (PhaaS) platform called AnonyMousKIT automates the retrieval of codes used to unlock stolen Apple devices and disable the Activation Lock fe...
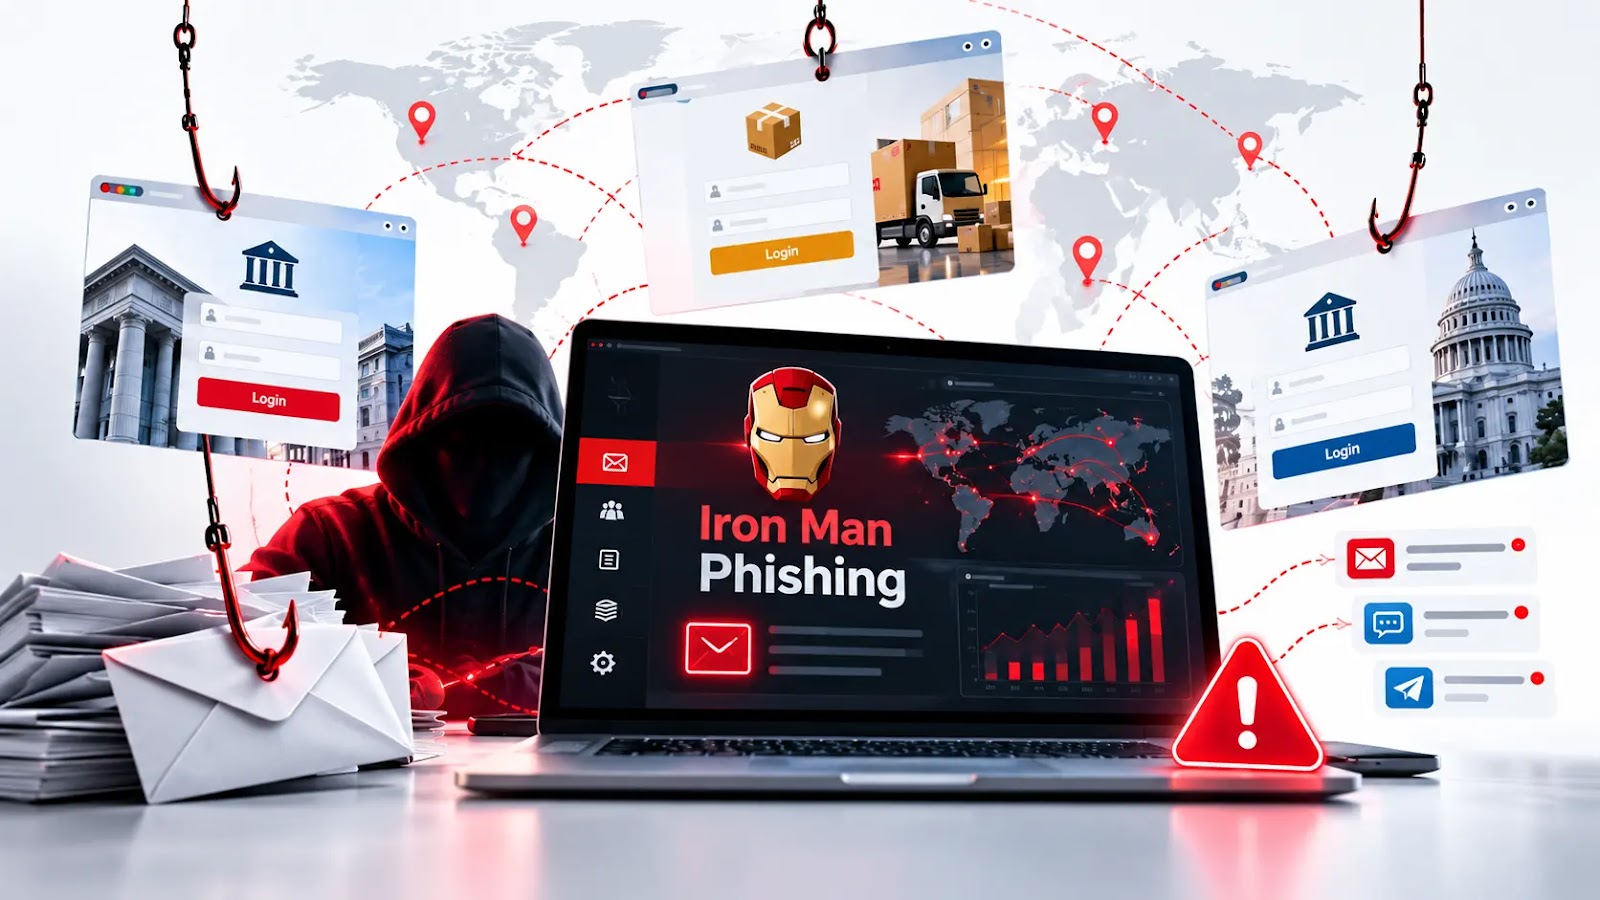
Iron Man System, a commercial phishing-as-a-service platform supplying criminals with ready-made websites impersonating banks, couriers, tax agencies, traffic authorities, and othe...
N0va is targeting organizations across North America and Europe with phishing campaigns that impersonate trusted services and abuse legitimate authentication flows. Successful atta...
Cybersecurity researchers have disclosed details of an advanced persistent threat (APT) spear-phishing campaign that has targeted individuals affiliated with Taiwan research organi...
BEC claims up 30% as US$500-a-month kits bypass MFA
Threat actors are using a new phishing kit called “GhostCode” to target sales teams with phony business inquiries, according to researchers at eSentire. The threat actors begin the...
Attackers have used a new phishing platform called “BigBear 2.0” to target hundreds of organizations across more than forty countries, according to researchers at CloudSEK. In abou...
The worst part is how normal these attacks look. A call from IT. A shared file. A trusted app. A simple request to click “Allow.” Why break in when someone might open the door? Th...
Researchers at ZeroBEC are tracking a phishing platform called “Greatness” that’s been significantly upgraded since it surfaced in 2023.
Microsoft is tracking phishing campaigns that use various lures to deliver MSP360, a legitimate RMM tool that attackers are abusing to gain a foothold on compromised systems.
Cybersecurity researchers have disclosed details of a "human-operated phishing platform" that impersonates advertising products for artificial intelligence (AI) chatbots like Googl...
A phishing campaign that moves the credential-harvesting page out of attacker-controlled web infrastructure and into the victim’s browser. Unlike ordinary phishing kits, which host...
Security researchers have identified a phishing campaign that uses Microsoft Teams messages impersonating IT support staff to distribute a newly discovered malware known as SynkLoa...
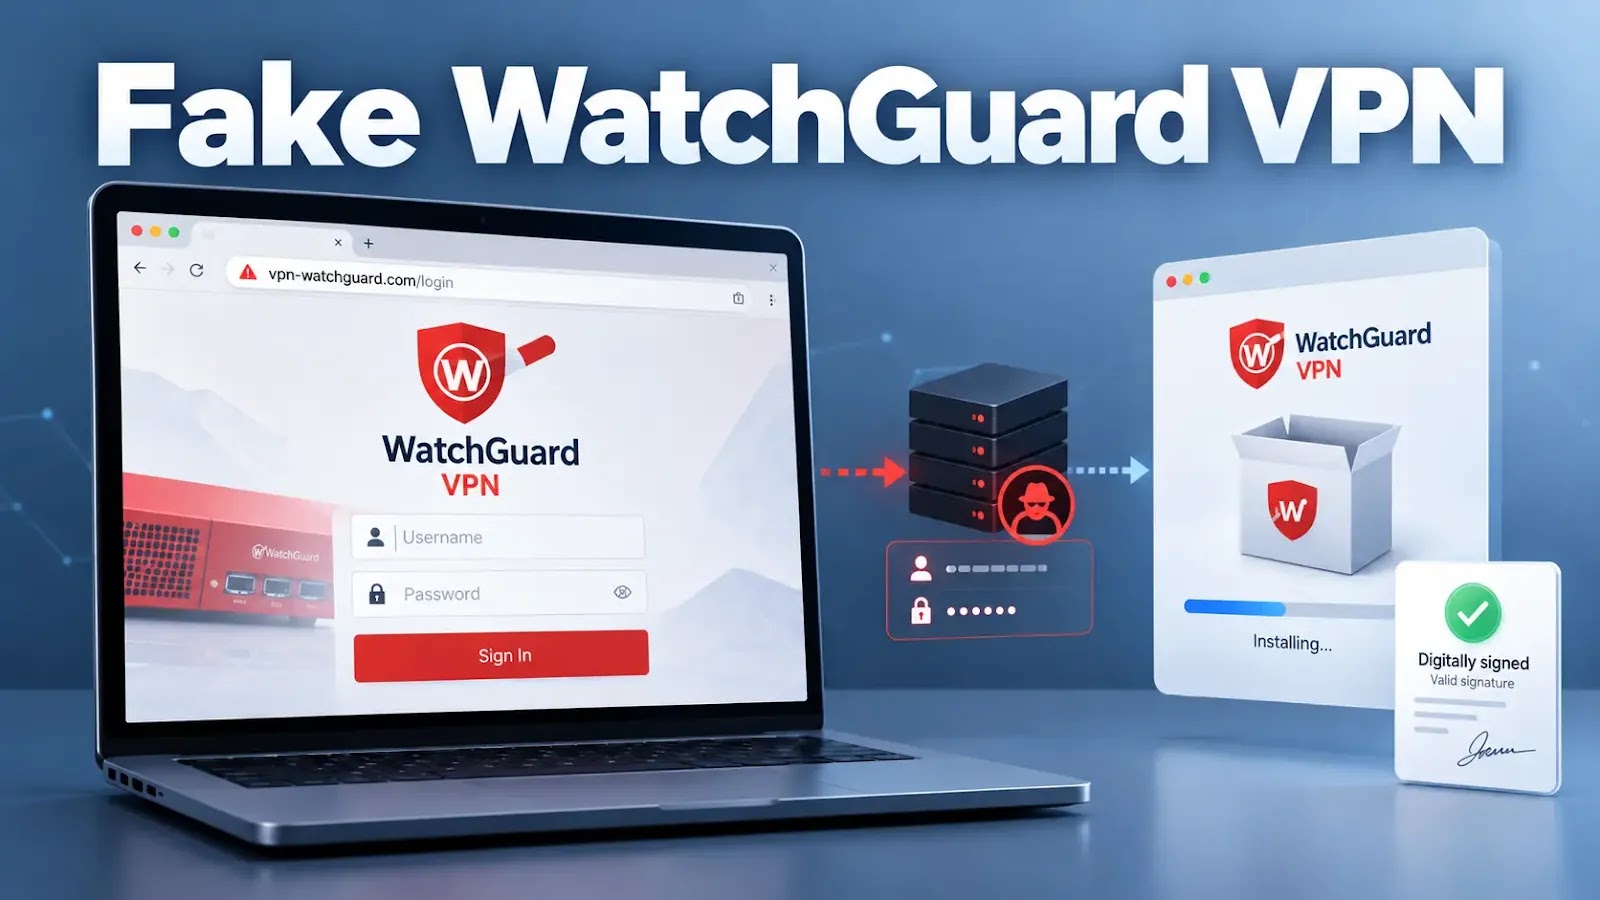
A WatchGuard VPN impersonation attack that steals connection credentials in the browser before delivering the vendor’s genuine, digitally signed installer. The campaign removes the...
Use SocialBu to discover ideas, generate post drafts, and schedule them across your social channels.