Latest updates for Web Security

Fresh curated links around Web Security are collected here so marketers can spot useful updates and turn timely ideas into posts faster.

Recent items include:

  • What your site tells a stranger before it renders a single pixel
  • Browser Security Policy Checklist: 5 Controls Every IT Team Should Lock Down
  • Running a Self-Hosted WAF in Production: Practical Lessons From SafeLine

Post angles to try

Share the most useful takeaway for your audience.
Turn one article into a quick practical checklist.
Ask your audience how this shift affects their work.
Turn angles into scheduled posts

Fresh articles and ideas

Recent curated links from global sources. Generate one free draft from any story, then use SocialBu to schedule and refine your content calendar.

dev.to /1 month ago

What your site tells a stranger before it renders a single pixel

Type a domain, hit enter, and before anything paints, your server and the browser have already had a short conversation. The server sends back response headers — and to anyone who...
Read source
ninjaone.com /1 month ago

Browser Security Policy Checklist: 5 Controls Every IT Team Should Lock Down

Most enterprise security programs focus on protecting servers, endpoints, and networks. This leaves browsers as busy yet vulnerable entry points into the business, since this is wh...

Read source
dzone.com /2 days ago

Running a Self-Hosted WAF in Production: Practical Lessons From SafeLine

Why Put a WAF in Front of the Application? Web application firewalls are often introduced as a list of security features: SQL injection protection, cross-site scripting detection,...

Read source
ministryoftesting.com /1 month ago

A Security Collection for the Security Chapter

Read source
ninjaone.com /1 month ago

Browser Extension Security: How to Manage Malicious and Abandoned Extensions

Your endpoints are managed. Your network is monitored. Your browser is not. This matters more than it used to. Applications, identity, SaaS access, and now AI tools all converge in...

Read source
sourcetrail.com /1 month ago

Comprehensive Guide to API Threat Protection with WAF and WAAP

Stop API breaches! Learn how to integrate WAF and WAAP to block SQLi, XSS, and bots. Protect your data and ensure PCI DSS compliance today. The post Comprehensive Guide to API Thre...

Read source
cloud.google.com /3 weeks ago

The future of browser-based security: Leveraging browser data for proactive defense

The browser has changed significantly. Rather than just a window to the web, it serves as an AI workspace and central operating environment for the modern enterprise. With knowledg...

Read source
testmuai.com /3 weeks ago

LLM Security: OWASP Top 10 for LLMs 2026 and How to Test It

LLM security explained: the OWASP Top 10 for LLM Applications 2026, how it differs from LLM safety, and one test per risk with the evidence that decides it.

Read source
gbhackers.com /1 month ago

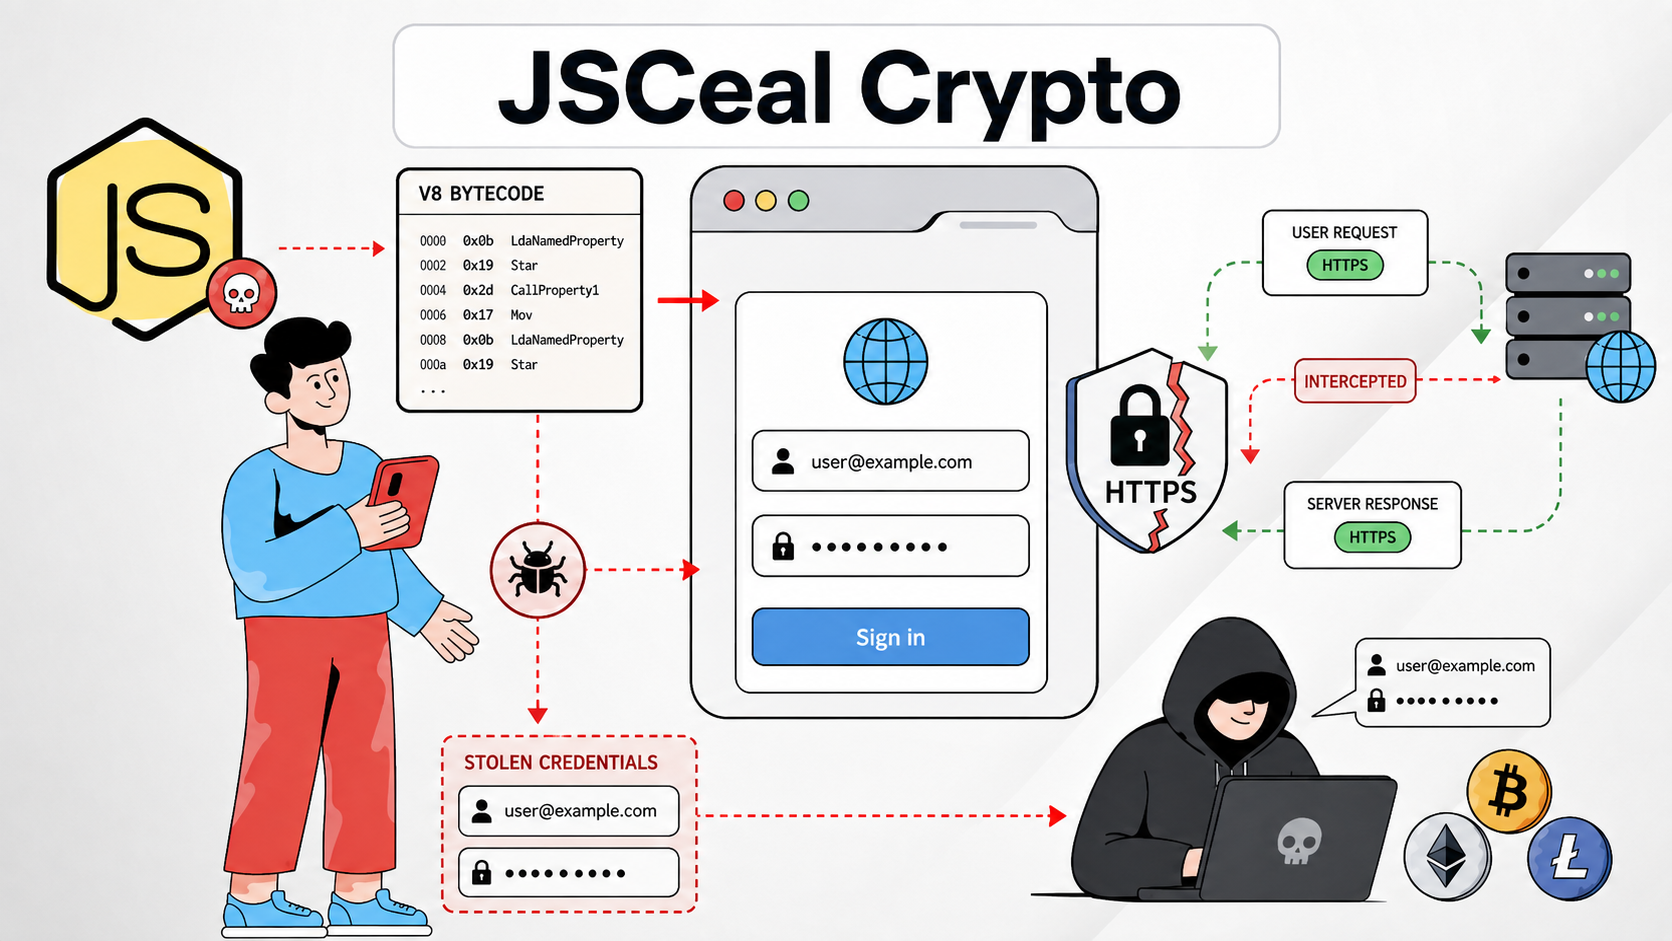
JSCeal Crypto Stealer Uses V8 Bytecode to Steal Browser Credentials and Intercept HTTPS

A sophisticated cryptocurrency-focused information stealer that hides its malicious logic inside compiled V8 JavaScript bytecode. JSCeal, also tracked by some vendors as WEEVILPROX...

Read source
cofense.com /1 month ago

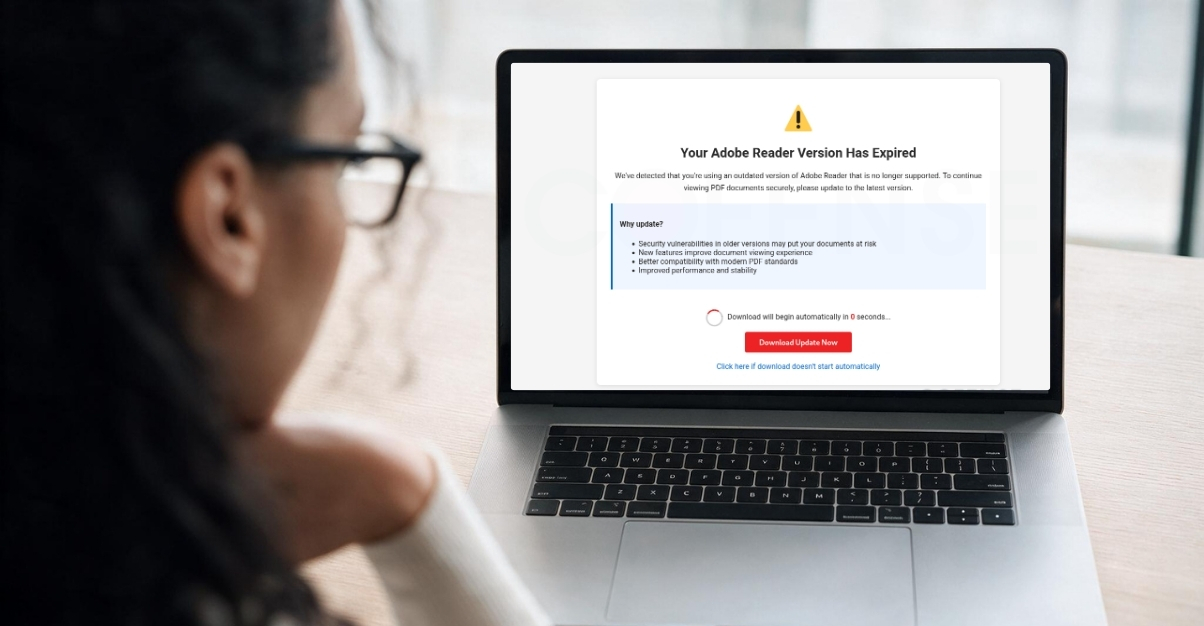
Understanding Browser Trust Abuse: Exploiting Enterprise’s Most Trusted Interface

By: Marie Mamaril, Intelligence TeamThe biggest change in browser-related threats is not a new flaw in browser software. It is a shift in how threat actors operate. Instead of brea...

Read source
jscrambler.com /1 month ago

The PCI DSS Gap: Why Relying on SAQ A Changes Leaves Retailers Exposed

with Gareth Bowker and Katia Kupidonova Cyberattacks targeting e-commerce payment flows continue to escalate, exposing a critical flaw in how online retailers manage client-side se...

Read source
onrec.com /1 month ago

Protect Recruitment Platforms with Automated Web Application Security Testing

Stuart Gentle Publisher at Onrec 18 Sep 2026|Recruitment & HR NewsProtect Recruitment Platforms with Automated Web Application Security TestingA recruitment platform can pass...

Read source
dev.to /1 day ago

A quick site hardening pass: email DNS, AI-crawler rules and security headers

Three things go quietly wrong on a lot of small sites: mail that fails authentication, a robots.txt that says something different from what you meant, and missing security headers....

Read source
ninjaone.com /1 month ago

5 Browser Management Best Practices to Reduce Security Risk

Browsers are how employees access the tools, systems, and platforms that get work done, with the average worker spending 85% of their day in one. However, despite their importance...

Read source
dzone.com /1 month ago

When Guest Access Becomes an Attack Surface: A Technical Analysis of the City-Forum Campaign

Learn how attackers enumerated Salesforce Experience Cloud and ServiceNow portals — and how defenders can detect and prevent the same abuse. When Guest Access Becomes an Attack Sur...

Read source
javacodegeeks.com /4 weeks ago

Spring Boot SSRF Mitigation with InetAddressFilter

Spring Boot applications often make HTTP requests to external services using clients such as RestClient, WebClient, or other HTTP client implementations. When the application contr...

Read source
jscrambler.com /1 month ago

Client-Side Risks in Healthcare: Reinforcing Existing Application Security Programs

Healthcare organizations routinely handle extremely sensitive personal data – including patient records, diagnostic histories, financial details, and personal identifiers. This has...

Read source
ninjaone.com /1 month ago

How Browser Policy Management Enforces Secure Browsing At Scale

Internet browsers are essential for opening emails, using collaboration tools, checking financial records, and more. Browser policy management enforces protective, proactive config...

Read source
thehackernews.com /1 month ago

JSCeal Malware Can Bypass Google Authentication Using Stolen Session Cookies

Cybersecurity researchers have unpacked JSCeal, a sophisticated compiled V8 JavaScript (JSC) malware with credential harvesting, surveillance, and traffic-interception capabilities...

Read source
gbhackers.com /1 month ago

The 12 Best Secure Web Gateway (SWG) Solutions, Compared and Priced

Best value overall: Cloudflare. It publishes per-user pricing, offers a free tier that lets you test the model properly, and delivers from one of the largest edge networks in the w...

Read source
dev.to /2 weeks ago

How We Audited and Hardened an Open-Source Anti-Bot Engine for Production (Synapse Shield v0.9.3)

Building a bot detection engine is challenging, but making it resilient against adversarial attacks, denial-of-service (DoS), and subtle concurrency bottlenecks in production is an...

Read source
ninjaone.com /2 weeks ago

Securing Remote Access Across Enterprise Environments

Remote access security is critical in enterprise organizations with a distributed workforce. It ensures that only authorized users and devices can access internal resources, thereb...

Read source
salesforce.com /1 month ago

Trust & Security at Dreamforce 2026

Discover how to secure the agentic enterprise with hands-on training, expert guidance, and Security Keynote in San Francisco and on Salesforce+.

Read source
blogs.cisco.com /1 month ago

Black Hat USA 2026: Safeguarding DNS with Secure Access

Cisco is the Security Cloud Provider for the Black Hat conferences, over a decade providing DNS Security. Learn about protecting DNS with Secure Access.

Read source

Turn fresh research into a full content calendar

Use SocialBu to discover ideas, generate post drafts, and schedule them across your social channels.

Sources covering Web Security

feeds.dzone.com

Recent coverage from public sources
Public source

blogs.cisco.com

Recent coverage from public sources
Public source

cloudblog.withgoogle.com

Recent coverage from public sources
Public source

cofense.com

Recent coverage from public sources
Public source

dev.to

Recent coverage from public sources
Public source

feeds.feedburner.com

Recent coverage from public sources
Public source