Latest updates for Vulnerability News

Fresh curated links around Vulnerability News are collected here so marketers can spot useful updates and turn timely ideas into posts faster.

Recent items include:

  • The Vulnerability Wave Is Here
  • Why Vulnerability Backlogs Are More Dangerous in the AI Era
  • Vulnerabilities: Everything You’ve Wanted To Know

Post angles to try

Share the most useful takeaway for your audience.
Turn one article into a quick practical checklist.
Ask your audience how this shift affects their work.
Turn angles into scheduled posts

Fresh articles and ideas

Recent curated links from global sources. Generate one free draft from any story, then use SocialBu to schedule and refine your content calendar.

ninjaone.com /3 weeks ago

The Vulnerability Wave Is Here

This summer delivered one record-breaking Patch Tuesday after another. First was July, when Microsoft issued its then-largest single month release to date (covering 600+ CVEs, trip...
Read source
cybersecuritytribe.com /1 month ago

Why Vulnerability Backlogs Are More Dangerous in the AI Era

For the first time in 19 years, the Verizon Data Breach Report, which samples over 22,000 breaches across 145 countries, has a new number one initial access vector: vulnerability e...

Read source
blogs.vmware.com /2 weeks ago

Vulnerabilities: Everything You’ve Wanted To Know

<div><img width="300" height="150" src="https://blogs.vmware.com/wp-content/uploads/2026/10/cybersecurity-awareness-banner-1200x600-1.png" cl...

Read source
ninjaone.com /4 weeks ago

Benefits of Vulnerability Management for Modern Enterprises

Adversaries today are weaponizing vulnerabilities even before patches are released. According to Qualys’s 2026 report on vulnerabilities, drawn from over one billion remediation re...

Read source
cybersecuritynews.com /1 month ago

Ivanti EPMM, Neurons and Sentry Vulnerabilities Enable Privilege Escalation and RCE Attacks

Ivanti has disclosed a wave of security advisories affecting three flagship enterprise products, Endpoint Manager Mobile, Neurons for ITSM, and Sentry, exposing organizations to ri...

Read source
insurancebusinessmag.com /1 day ago

PHP2Shell signals a “new reality of vulnerabilities” for businesses

"This won't be the last bad vulnerability we will see this month or this year," says Beazley Security head

Read source
tribune.com.pk /3 weeks ago

Meta bolsters Muse safety warning after security vulnerability found, The Information reports

Meta initially classified the vulnerability as "SEV-2", its third-highest severity level for impact incidents

Read source
xkcd.com /3 days ago

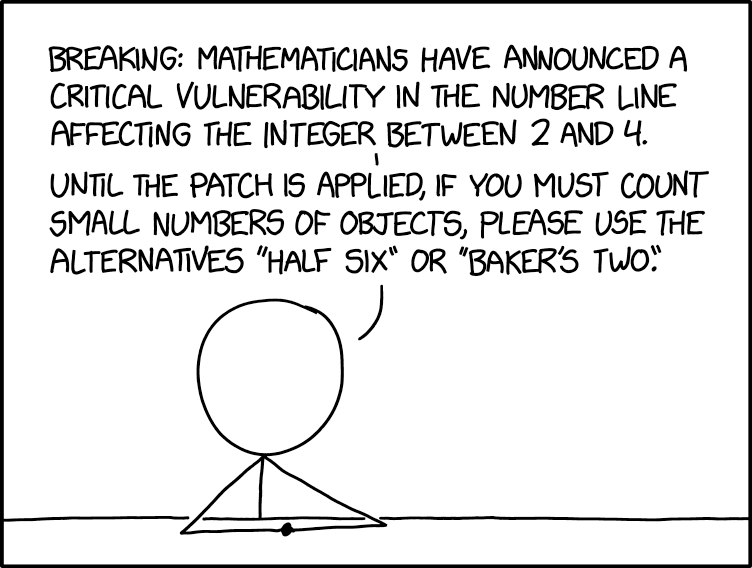
Vulnerability

Read source
gbhackers.com /1 month ago

Critical Veeam ONE Flaw Lets Unauthenticated Attackers Coerce SMB Authentication From Service Accounts

Veeam has released security updates for a critical vulnerability in Veeam ONE that could allow an unauthenticated network attacker to coerce SMB authentication from the account run...

Read source
thehackernews.com /2 weeks ago

âš¡ Weekly Recap: NetScaler and FortiMail 0-Days, AI Coding Leaks, Spectre v2 and Ransomware Arrests

A blank field. A public repo. One reply to an email. A box left exposed. None of this sounds dramatic, which is partly the problem. This week’s threats keep finding leverage in sma...

Read source
cybersecuritynews.com /1 month ago

Weekly Cybersecurity Newsletter Bulletin – Microsoft 0-day, FortiOS, PAN-OS Flaw, Revolut Data Breach, and 20+ Stories

This week’s roundup covers a massive Microsoft Patch Tuesday with two exploited zero-days, active FortiGate exploitation, a critical PAN-OS root-level RCE flaw, the Revolut KYC dat...

Read source
cybersecuritynews.com /1 week ago

Ivanti Connect Secure 0-Day Vulnerability Actively Exploited in the Wild

Ivanti has disclosed an actively exploited zero-day vulnerability in Ivanti Connect Secure (ICS) that allows remote attackers to execute arbitrary commands without logging in. Trac...

Read source
infosecurity-magazine.com /1 month ago

N-able Releases Hotfix for Critical Remote Code Execution Vulnerability

The vulnerability, CVE-2026-86218, was allocated a maximum-severity rating by the software provider itself

Read source
ninjaone.com /4 weeks ago

How System Vulnerability Scanning Supports Patch Governance

The window between vulnerability disclosure and active exploitation continues to shrink. About one-third (28.3%) of exploited vulnerabilities are weaponized within 24 hours of disc...

Read source
thehackernews.com /1 month ago

GitLab CVSS 10 File-Read Flaw Draws In-the-Wild Probes After Disclosure

GitLab has released patches to address multiple flaws, including a maximum-severity security vulnerability that has witnessed in-the-wild probes within hours of public disclosure....

Read source
dev.to /1 month ago

Artifactory on the Internet: Measuring the Exposure Behind CVE-2026-82329

Artifactory on the Internet: Measuring the Exposure Behind CVE-2026-82329 An authentication bypass that grants administrator rights on a package repository is only as dangerous a...

Read source
thehackernews.com /2 days ago

ThreatsDay: AI Secrets Leak, PingCAP Source Theft, Signal Hang-Up Flaw, Laravel Auth Bypass + 21 More

This week has already been rough for cybersecurity. Critical PHP and GitLab RCE flaws, serious Linux security bugs, compromised eMudhra certificates, a Node.js RCE flaw, a hacked L...

Read source
cybersecuritynews.com /1 month ago

Hackers Actively Exploiting Critical Langflow RCE and Rails Vulnerability

Two critical vulnerabilities affecting Langflow and Ruby on Rails deployments are being actively exploited, with attackers quickly moving from public disclosure to reconnaissance,...

Read source
cybersecuritynews.com /1 month ago

PaperCut NG/MF Vulnerability Actively Exploited in Attack – All Versions Impacted

PaperCut has confirmed that hackers are actively exploiting an unpatched vulnerability in its widely used PaperCut NG and PaperCut MF print management software, prompting the compa...

Read source
cybersecuritynews.com /3 weeks ago

Citrix NetScaler 0-Day RCE Vulnerabilities Actively Exploited in Attacks

Citrix NetScaler administrators are confronting reports of two undisclosed remote code execution vulnerabilities allegedly exploited in real-world attacks. watchTowr said the flaws...

Read source
thehackernews.com /1 month ago

Webinar: Learn How to Answer “Are We Exposed?” Faster After a New CVE

A major vulnerability is disclosed. The alert lands immediately. Then comes the harder question: Are we actually exposed? For many security teams, answering that means jumping bet...

Read source
infosecurity-magazine.com /1 week ago

Warning Over High-Risk Vulnerabilities in Widely Used LLM Gateway Tool

CVE-2026-35029 and CVE-2026-59823 affect LiteLLM, which is commonly used by enterprises to connect their AI applications to providers like OpenAI and Anthropic

Read source
thehackernews.com /11 hours ago

CISA Flags Two Actively Exploited Critical Flaws in Collabora Online and Arista VeloCloud

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Friday added two vulnerabilities impacting Collabora Online Built-in CODE Server and Arista VeloCloud Orchestrat...

Read source
cybersecuritynews.com /3 weeks ago

CISA Warns of Citrix NetScaler 0-Day RCE Vulnerabilities Exploited in Attacks

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added two critical Citrix NetScaler vulnerabilities to its Known Exploited Vulnerabilities catalog after eviden...

Read source

Turn fresh research into a full content calendar

Use SocialBu to discover ideas, generate post drafts, and schedule them across your social channels.

Sources covering Vulnerability News

blogs.vmware.com

Recent coverage from public sources
Public source

cybersecuritynews.com

Recent coverage from public sources
Public source

dev.to

Recent coverage from public sources
Public source

feeds.feedburner.com

Recent coverage from public sources
Public source

gbhackers.com

Recent coverage from public sources
Public source

tribune.com.pk

Recent coverage from public sources
Public source