Latest updates for Vulnerability Management

Fresh curated links around Vulnerability Management are collected here so marketers can spot useful updates and turn timely ideas into posts faster.

Recent items include:

  • Benefits of Vulnerability Management for Modern Enterprises
  • How to Explain Vulnerability Management to Executives
  • How Healthcare Organizations Manage Vulnerabilities

Post angles to try

Share the most useful takeaway for your audience.
Turn one article into a quick practical checklist.
Ask your audience how this shift affects their work.
Turn angles into scheduled posts

Fresh articles and ideas

Recent curated links from global sources. Generate one free draft from any story, then use SocialBu to schedule and refine your content calendar.

ninjaone.com /4 weeks ago

Benefits of Vulnerability Management for Modern Enterprises

Adversaries today are weaponizing vulnerabilities even before patches are released. According to Qualys’s 2026 report on vulnerabilities, drawn from over one billion remediation re...
Read source
ninjaone.com /13 hours ago

How to Explain Vulnerability Management to Executives

IT leaders and managed service providers (MSPs) need an adaptable cyber incident communication plan that executives can understand. With clearly communicated concepts, risks, and b...

Read source
ninjaone.com /1 month ago

How Healthcare Organizations Manage Vulnerabilities

Healthcare organizations manage some of the most operationally sensitive environments in modern enterprise IT, where a security gap can directly affect patient care. As attack surf...

Read source
ninjaone.com /4 weeks ago

How System Vulnerability Scanning Supports Patch Governance

The window between vulnerability disclosure and active exploitation continues to shrink. About one-third (28.3%) of exploited vulnerabilities are weaponized within 24 hours of disc...

Read source
ninjaone.com /3 weeks ago

How Real-Time Vulnerability Management Changes the Narrative for MSPs

If you’re an MSP overseeing vulnerability management for dozens or hundreds of client organizations you already know that powerful security capabilities are only useful if you use...

Read source
ninjaone.com /2 weeks ago

How To Build a Triage Process for Your Vulnerability Disclosure Program

Building an effective, transparent, and accessible vulnerability disclosure program (VDP) helps you build trust with your clients, users, and their customers. It’s not just softwar...

Read source
ninjaone.com /3 weeks ago

The Vulnerability Wave Is Here

This summer delivered one record-breaking Patch Tuesday after another. First was July, when Microsoft issued its then-largest single month release to date (covering 600+ CVEs, trip...

Read source
blogs.vmware.com /2 weeks ago

Vulnerabilities: Everything You’ve Wanted To Know

<div><img width="300" height="150" src="https://blogs.vmware.com/wp-content/uploads/2026/10/cybersecurity-awareness-banner-1200x600-1.png" cl...

Read source
cybersecuritytribe.com /1 month ago

Why Vulnerability Backlogs Are More Dangerous in the AI Era

For the first time in 19 years, the Verizon Data Breach Report, which samples over 22,000 breaches across 145 countries, has a new number one initial access vector: vulnerability e...

Read source
ninjaone.com /1 month ago

How to Operationalize Multi-Tenant Vulnerability Scanning

The shift to multi-tenant architectures has redefined what it means to secure a managed environment. There is now the additional challenge of managing IT at scale, across diverse i...

Read source
bleepingcomputer.com /1 month ago

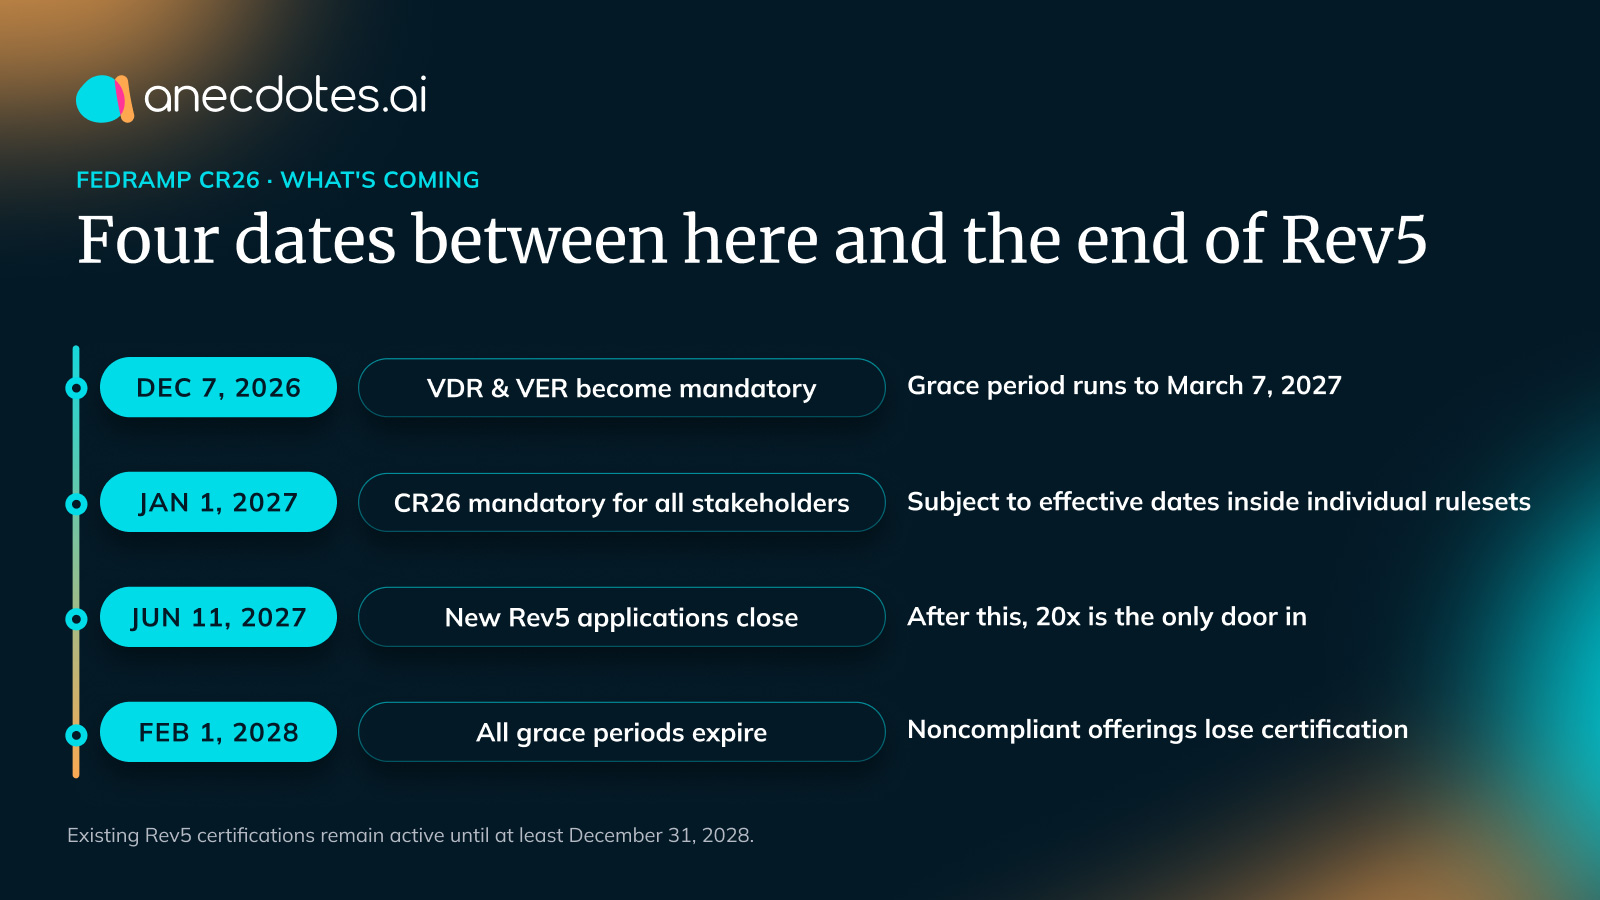
FedRAMP VDR & VER: Daily Scans Are Only the Beginning

FedRAMP's new VDR and VER requirements make vulnerability management more continuous, with faster scanning, tighter remediation deadlines, and stronger evidence requirements. Anecd...

Read source
thehackernews.com /1 month ago

Webinar: Learn How to Answer “Are We Exposed?” Faster After a New CVE

A major vulnerability is disclosed. The alert lands immediately. Then comes the harder question: Are we actually exposed? For many security teams, answering that means jumping bet...

Read source
thehackernews.com /1 month ago

Your Critical Vulnerabilities Might Not Be Your Biggest Risk

Security teams have become exceptionally talented at finding vulnerabilities. Now, it’s time to turn our attention to optimizing the process for determining which of those vulnerab...

Read source
blogs.vmware.com /2 weeks ago

Security Scanners and VCF

<div><img width="300" height="150" src="https://blogs.vmware.com/wp-content/uploads/2026/10/cybersecurity-awareness-banner-1200x600-1.png" cl...

Read source
ninjaone.com /2 weeks ago

ISO 27001 Patch Management Tools and Policy Guide

To comply with ISO 27001, patch management is a practical necessity. ISO 27001 is a broad cybersecurity standard, covering organizational processes and governance as well as techni...

Read source
cncf.io /1 month ago

Handling vulnerability reports: Recipe card

Recipe Handling Vulnerability Reports Target audience (the chef) This recipe is aimed at small and medium non-security focused projects. Maintainers of a high-risk security sensiti...

Read source
cm-alliance.com /1 day ago

Guarding the Digital Castle: Cyber Risk Management for Businesses

Have you ever wondered what separates a company that survives a breach from one that collapses after it? The answer usually comes down to preparation.Cyber risk managementis the di...

Read source
ninjaone.com /1 month ago

Understanding Vulnerability Scanning Software Costs

Vulnerability scanning automates the identification and reporting of vulnerabilities across an enterprise, making it a foundational cybersecurity practice. However, many organizati...

Read source
thehackernews.com /1 month ago

Can You Prove a New CVE Is Exploitable Before Attackers Do? Learn How in This Webinar

A new CVE drops. Your scanner finds it. The severity score looks ugly. But that still does not answer the question that matters: Can it actually be exploited in your environment?...

Read source
infosecurity-magazine.com /1 month ago

CISA Upgrades Vulnerability Reporting Platform with More Automation

The US cybersecurity agency is moving to a new vulnerability coordination platform called VINCE-NT

Read source
habr.com /2 weeks ago

Призраки в системе управления уязвимостями: как идентификация, слияние и история активов спасают от аномалий

Каждый актив в инфраструктуре проходит свой жизненный цикл: он появляется, функционирует, а со временем выводится из эксплуатации. Новые активы часто создаются как копии существующ...

Read source
sourcetrail.com /1 month ago

The Ultimate Guide to AI-Driven Vulnerability Management and Security Platforms

Stop guessing and start fixing. Discover how AI-powered vulnerability management identifies risks and automates remediation to secure your cloud. The post The Ultimate Guide to AI-...

Read source
forrester.com /3 weeks ago

Announcing The Forrester Waveâ„¢: Proactive Security Platforms, Q3 2026

Last week, we released The Forrester Waveâ„¢: Proactive Security Platforms, Q3 2026. This is the first evaluation of this market under this title, which has evolved from attack sur...

Read source
ninjaone.com /13 hours ago

How to Operationalize Enterprise Patch Management Governance

Enterprise patch management requires governance to ensure seamless coverage that enables security and compliance. Establishing a governance strategy, including assigning responsibi...

Read source

Turn fresh research into a full content calendar

Use SocialBu to discover ideas, generate post drafts, and schedule them across your social channels.

Sources covering Vulnerability Management

blogs.vmware.com

Recent coverage from public sources
Public source

feeds.feedburner.com

Recent coverage from public sources
Public source

go.forrester.com

Recent coverage from public sources
Public source

habr.com

Recent coverage from public sources
Public source

bleepingcomputer.com

Recent coverage from public sources
Public source

cm-alliance.com

Recent coverage from public sources
Public source