Latest updates for Spear Phishing

Fresh curated links around Spear Phishing are collected here so marketers can spot useful updates and turn timely ideas into posts faster.

Recent items include:

  • Fake Voicemail SVG Attachments Fuel Large-Scale Phishing Campaign
  • Phishing Attacks Target YouTubers With Phony Sponsorships
  • Direct Send: How Attackers Weaponize Your Infrastructure Against You

Post angles to try

Share the most useful takeaway for your audience.
Turn one article into a quick practical checklist.
Ask your audience how this shift affects their work.
Turn angles into scheduled posts

Fresh articles and ideas

Recent curated links from global sources. Generate one free draft from any story, then use SocialBu to schedule and refine your content calendar.

infosecurity-magazine.com /1 month ago

Fake Voicemail SVG Attachments Fuel Large-Scale Phishing Campaign

A large-scale phishing campaign used fake voicemail SVG attachments to bypass email defenses, targeting 5527 organizations with over 26,000 malicious messages
Read source
blog.knowbe4.com /1 week ago

Phishing Attacks Target YouTubers With Phony Sponsorships

A phishing campaign is targeting YouTubers with phony sponsorship offers, according to researchers at ESET. The emails are personalized to each target, making specific references t...

Read source
blog.knowbe4.com /1 month ago

Direct Send: How Attackers Weaponize Your Infrastructure Against You

Lead Analysts: Prabhakaran Ravichandhiran, Jeewan Singh Jalal

Read source
blog.knowbe4.com /1 month ago

Recruitment-Themed Phishing Campaign Targets Enterprise Users

Researchers at Zimperium are tracking widespread phishing campaigns that use Browser-in-the-Browser (BitB) attacks to trick users into handing over their enterprise credentials. Th...

Read source
thehackernews.com /1 month ago

N0va Phishkit Targets US and EU Businesses: A New Challenge for Identity Security

N0va is targeting organizations across North America and Europe with phishing campaigns that impersonate trusted services and abuse legitimate authentication flows. Successful atta...

Read source
blog.knowbe4.com /1 month ago

Social Engineering Campaign Uses Phony NDAs to Avoid Detection

Researchers at Gen Digital are tracking a sophisticated social engineering campaign that’s using phony NDA documents to trick employees into moving the conversation to WhatsApp and...

Read source
thehackernews.com /1 week ago

UAT-11985 Uses Fake Event Invites to Target Taiwan Research Affiliates With Google AitM Phishing

Cybersecurity researchers have disclosed details of an advanced persistent threat (APT) spear-phishing campaign that has targeted individuals affiliated with Taiwan research organi...

Read source
blog.knowbe4.com /1 week ago

Business-Themed Phishing Lures Deliver RMM Tools

Microsoft is tracking phishing campaigns that use various lures to deliver MSP360, a legitimate RMM tool that attackers are abusing to gain a foothold on compromised systems.

Read source
blog.knowbe4.com /1 month ago

Attackers Use Passkey-Themed Phishing to Breach Cloud Environments

Researchers at Microsoft are tracking a social engineering campaign that uses passkey-themed lures to trick users into granting persistent access to their accounts and online work...

Read source
blog.knowbe4.com /1 month ago

Voice Phishing Attacks Target Hedge Fund Employees

Google’s Threat Intelligence Group (GTIG) is tracking a voice phishing (vishing) campaign that’s targeting hedge funds and financial firms. The researchers attribute the attacks to...

Read source
blog.knowbe4.com /1 month ago

Phishing Campaign Targets Employees with Malicious SVG Files

Researchers at INKY observed a major phishing campaign that used SVG (Scalable Vector Graphics) image files to deliver malicious JavaScript. While abuse of SVG files isn’t new, INK...

Read source
gbhackers.com /1 month ago

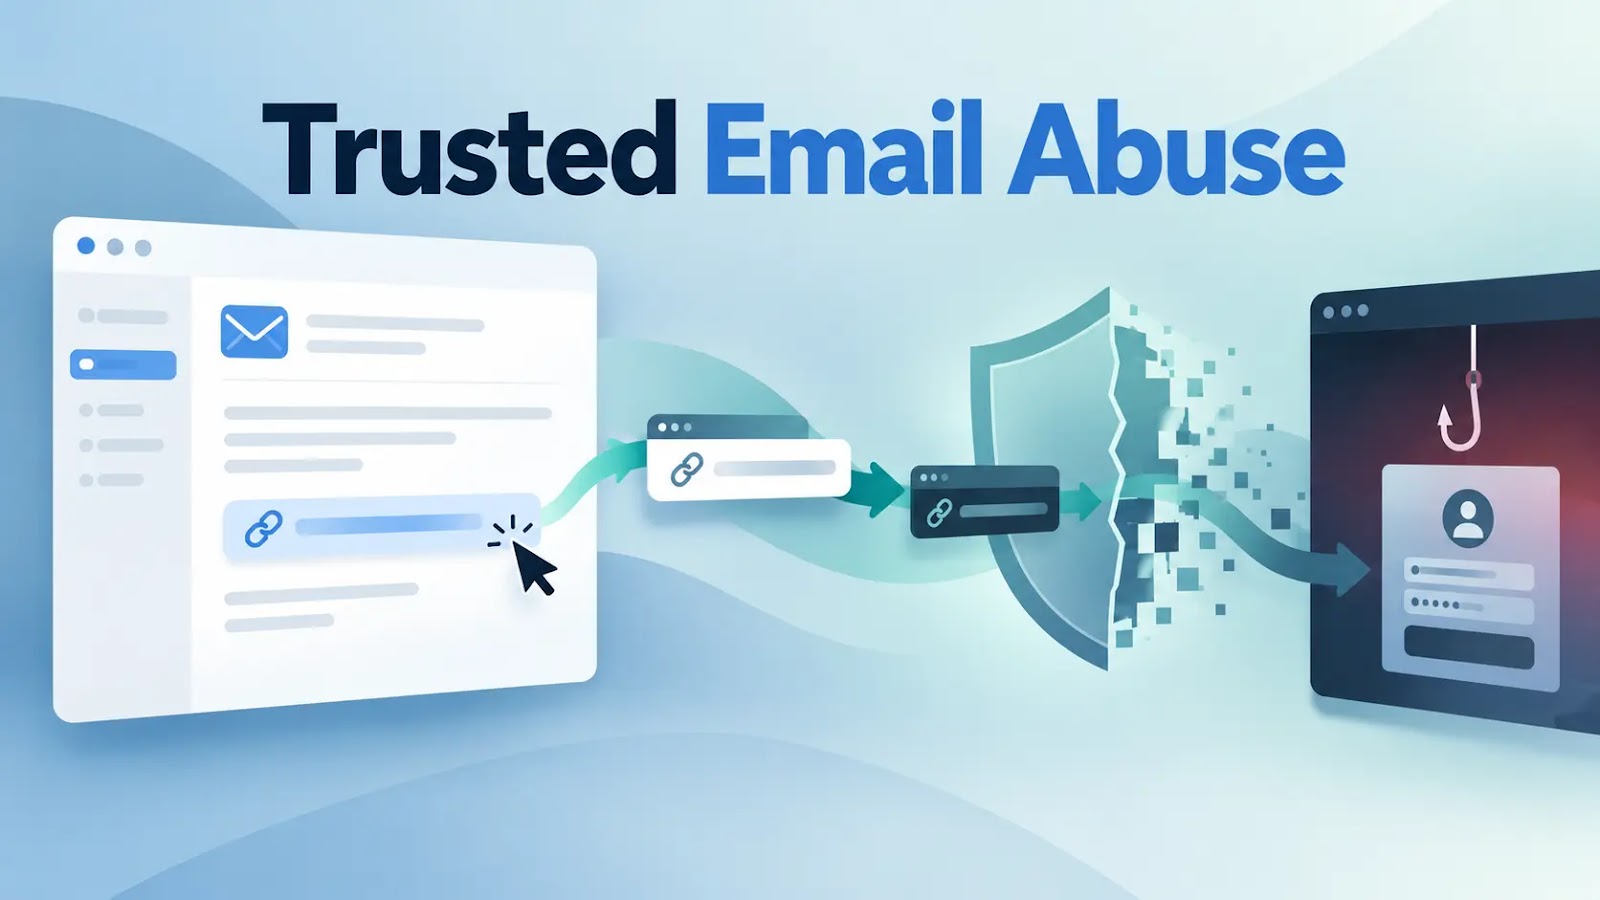
Phishing Attacks Abuse Trusted Email Infrastructure and URL Cloaking to Evade Security Filters

Phishing operators are increasingly shifting away from malware-laden attachments and toward trusted delivery services, authenticated domains, and multi-stage URL cloaking designed...

Read source
blog.knowbe4.com /1 week ago

Phishing Is Now A Criminal Impersonation Industry. Here Is How To Fight Back

For years, we described phishing as an email problem: an attacker writes a convincing message, sends it to thousands of people and waits for someone to click. That model is now out...

Read source
cofense.com /3 days ago

Threats Hidden in Replies: Threat Actors Deliver Malware and Credential Phishing in Email Threads

Recently, threat actors have been increasingly delivering malware or credential phishing attacks at the end of long email threads designed to exploit a potential victim’s trust in...

Read source
cofense.com /1 month ago

False Allegations, Real Threats: Sexual Misconduct Claims Used as Phishing Lures

Threat actors are impersonating university leaders and using fabricated sexual misconduct allegations to pressure recipients into downloading Zoho Assist, a legitimate remote acces...

Read source
blog.knowbe4.com /1 month ago

Bypassing the Gatekeepers: How a Global Phishing Campaign Turns Google's Infrastructure into a Trust Proxy

Lead Analysts: Prabhakaran Ravichandhiran, Jeewan Singh Jalal

Read source
blog.knowbe4.com /2 weeks ago

The Rise of Legitimate-Service Phishing: 1 in 10 Phishing Emails Now Comes From a Platform You Trust

Lead Analysts: Karthikeyan D, Prabhakaran Ravichandhiran, Jeewan Singh Jalal

Read source
gbhackers.com /2 weeks ago

Attackers Abuse Legitimate ScreenConnect Client in Phishing Campaign to Gain Remote Access

Threat actors are increasingly bypassing conventional malware detection by abusing legitimate remote monitoring and management software instead of deploying custom implants. In a r...

Read source
cofense.com /1 week ago

RSVP to Disaster: How One Click Installs a RAT

The Cofense Phishing Defense Center (PDC) uncovered a phishing campaign that disguises malware as a digital event invitation, exploiting recipients’ curiosity to lure them into dow...

Read source
gbhackers.com /1 month ago

Polymorphic Phishing Attack Generates Unique Credential-Stealing Page on Every Visit

A newly analyzed phishing operation is using server-side polymorphism to generate a distinct credential-harvesting page for virtually every request, undermining detection approache...

Read source
blog.knowbe4.com /1 day ago

Warning: Attackers Are Using Calendar Invite Files to Evade Security Filters

Phishing attacks are increasingly using legitimate calendar invites to bypass security filters, according to researchers at Netcraft. Attackers send ICS calendar invite files that...

Read source
natlawreview.com /1 month ago

Privacy Tip #507 – Coordinated Vishing Attacks Hit Microsoft Teams Users

Read source
blog.knowbe4.com /1 month ago

CyberheistNews Vol 16 #35 [New Report] Phishing Is Still the No. 1 Initial Threat Access Vector

Read source
cofense.com /4 days ago

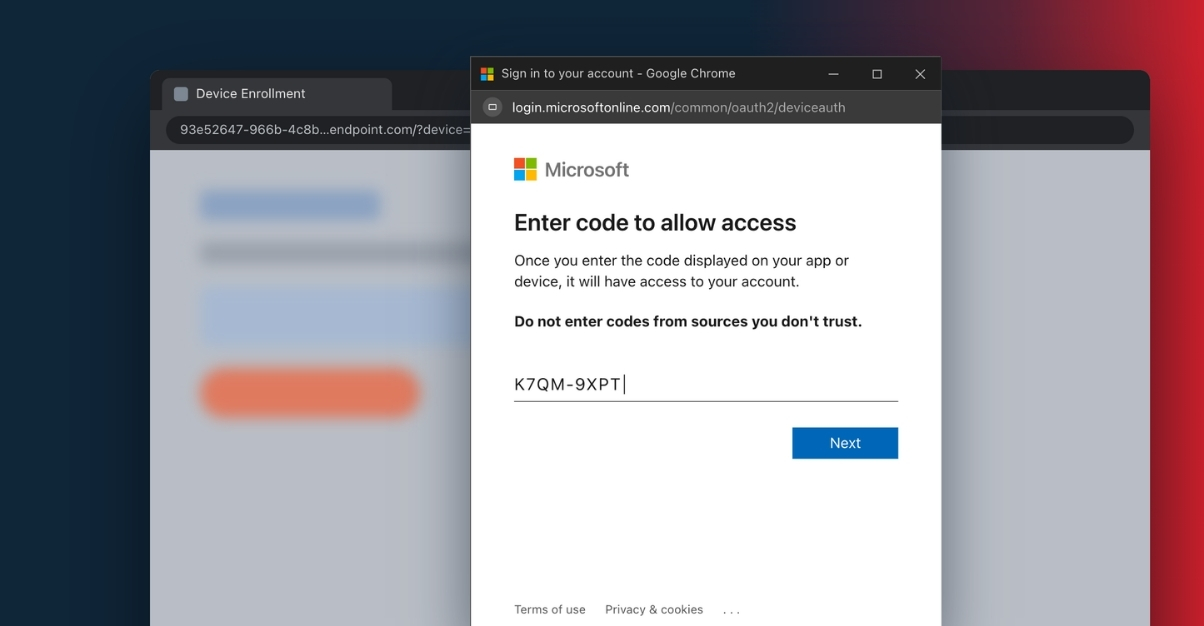
Beyond Passwords: How Attackers Abuse Device Code Authentication

Cofense Phishing Defense Center (PDC) analysts uncovered a device code phishing campaign that impersonates trusted brands, including Microsoft, Syncfusion, and Mimecast, to trick u...

Read source

Turn fresh research into a full content calendar

Use SocialBu to discover ideas, generate post drafts, and schedule them across your social channels.

Sources covering Spear Phishing

blog.knowbe4.com

Recent coverage from public sources
Public source

cofense.com

Recent coverage from public sources
Public source

feeds.feedburner.com

Recent coverage from public sources
Public source

gbhackers.com

Recent coverage from public sources
Public source

natlawreview.com

Recent coverage from public sources
Public source

infosecurity-magazine.com

Recent coverage from public sources
Public source