What Is OAuth 2.0 Authentication: A Complete Guide for Beginners!
This article provides a detailed guide to What Is OAuth 2.0 Authentication, how authorization works, and how applications access approved ... Read more The post What Is OAuth 2.0...
Search fresh public links, source activity, and ready-to-use post angles for Oauth 2.0.
Fresh curated links around OAUTH 2.0 are collected here so marketers can spot useful updates and turn timely ideas into posts faster.
Recent items include:
Recent curated links from global sources. Generate one free draft from any story, then use SocialBu to schedule and refine your content calendar.
This article provides a detailed guide to What Is OAuth 2.0 Authentication, how authorization works, and how applications access approved ... Read more The post What Is OAuth 2.0...
Most modern web and mobile apps don’t build authentication from the ground up. People want... The post OpenID Connect: Verifying User Identity on Top of OAuth 2.0 appeared first on...
Most REST APIs treat pagination and navigation as a solved problem, and then quietly ignore a much messier one: what happens when two different users hit the same endpoint and get...
OAuth grants create data highways between SaaS apps, AI agents, and other tools. And, they are multiplying faster than any security team can review them. As the recent Klue breach...
MSK Replicator now supports OAuth 2.0 (SASL/OAUTHBEARER) authentication to external Apache Kafka clusters. This post walks through the three supported grant types, how to configure...
Introduction VCF Automation supports integration with identity provider protocols for identity and access management. The supported identity provider types are:
Spring Authorization Server now lives inside Spring Security 7 under the same Maven coordinates, so the upgrade is a version bump. This server-side guide covers enabling DPoP and R...
My previous guide used ingress-nginx annotations to put internal Kubernetes services behind OAuth2 Proxy. It was written for an ingress-nginx setup. That controller is being retire...
redb.Identity получил WS-Trust фасад: Issue, Validate, Cancel, Renew на тех же маршрутах ядра. Тот же JWT, тот же реестр клиентов, WSDL для генератора. Когда мы делали gRPC-фасад,...
Comments
If you’re building an AI agent, there isn’t one authorization method that is right for every situation.Continue reading on Medium »
Picnic runs RabbitMQ as the messaging backbone for hundreds of microservices on Amazon MQ for RabbitMQ. This post shows how to configure one broker to trust multiple OAuth 2.0 iden...
Single sign-on is a solved problem. You redirect to an identity provider, it tells you who the person is, you mint a session. Every framework has a library for it. Then you try it...
Amazon Bedrock AgentCore Identity now offers a Consent portal, a managed web experience and session binding endpoint for AgentCore Gateway. This post walks through provisioning a p...
The U.S. Federal Bureau of Investigation (FBI) has issued an advisory warning of a wave of OAuth consent phishing attacks targeting “prominent victims, their family members, and pe...
The FBI issued a public service announcement on Tuesday warning that malicious cyber actors have been targeting high-profile individuals, their relatives and acquaintances using a...
Bearer-токен работает у любого, кто его держит. Разбор трёх слоёв в redb.Identity: BFF без токена в браузере, привязка к ключу через DPoP, быстрый отзыв. Access-token по умолчанию...
A critical security flaw in WSO2 API Manager has come under active exploitation in the wild, according to findings from watchTowr. The vulnerability, tracked as CVE-2026-5430 (CVS...
Login looks simple until you’re building password resets, email verification, MFA, social providers, session management, and the enterprise SSO your first big customer asked for la...
Two XenForo Flaws in One Release: Empty OAuth2 Credentials and a Passkey That Belonged to Someone Else Two authentication paths, one shared weakness in assumptions Xen...
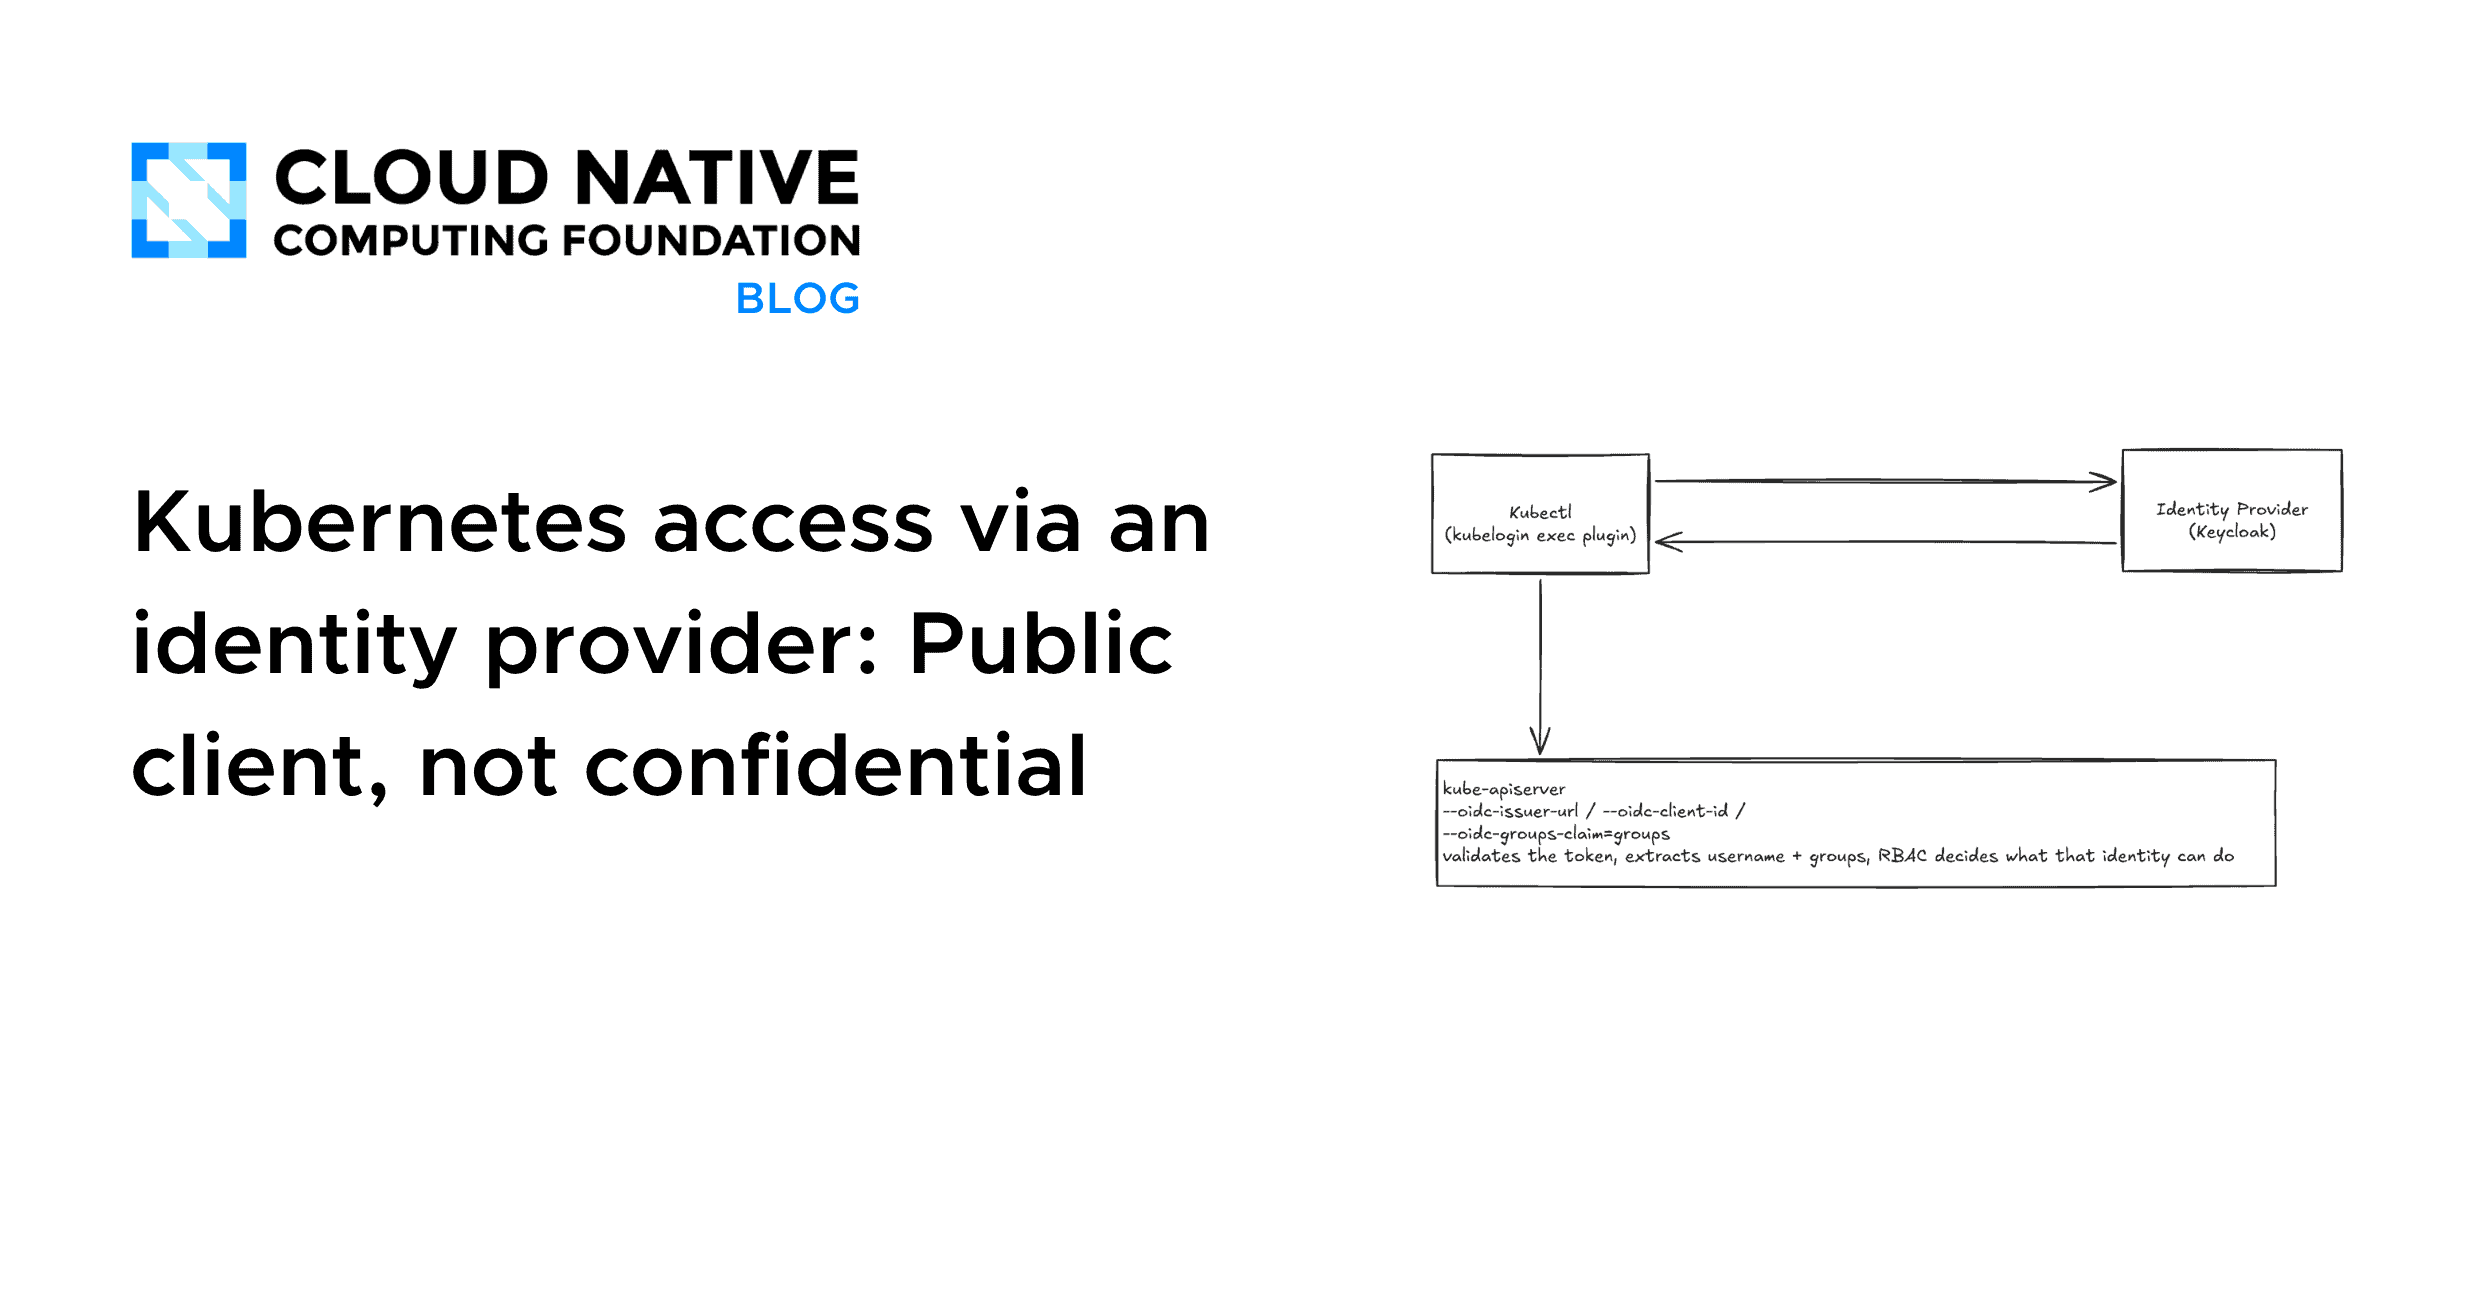
Access control belongs on the same day-zero checklist as networking and storage. On most on-prem clusters, it never makes the list. The Identity Gap Managed cloud Kubernetes ships...
Авторизация в Spring обычно живёт в аннотациях и SpEL — и ломается на иерархии ресурсов и фильтрации списков. Как вынести правила доступа в OPA, не потеряв ни фильтрацию в SQL, ни...
Every app eventually needs to answer two questions: "who is this person?" and "what are they allowed to do?" Many tutorials either focus on integrating a specific authentication pr...
Short answer: for a property-management login, start with a dedicated SMS OTP flow, then keep direct SMS send for exceptional notices. The OTP endpoint owns code generation and mat...
Use SocialBu to discover ideas, generate post drafts, and schedule them across your social channels.