Why Incident Response Plans Need Real-World Testing
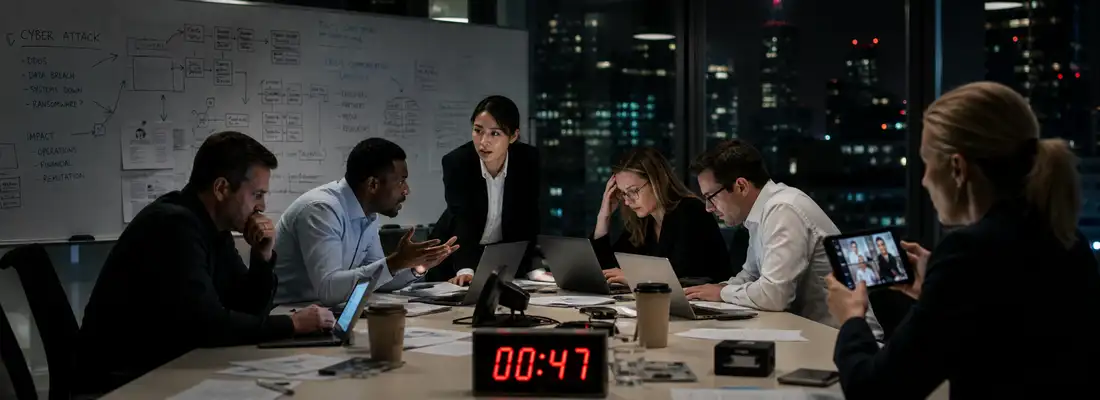
At 07:35 on 28 October 2023, the British Library detected a cyber attack. By 09:15 its crisis process was activated, and by 10:00 its Gold Crisis Response Team had convened. On pap...
Search fresh public links, source activity, and ready-to-use post angles for Incident Response.
Fresh curated links around Incident Response are collected here so marketers can spot useful updates and turn timely ideas into posts faster.
Recent items include:
Recent curated links from global sources. Generate one free draft from any story, then use SocialBu to schedule and refine your content calendar.
At 07:35 on 28 October 2023, the British Library detected a cyber attack. By 09:15 its crisis process was activated, and by 10:00 its Gold Crisis Response Team had convened. On pap...
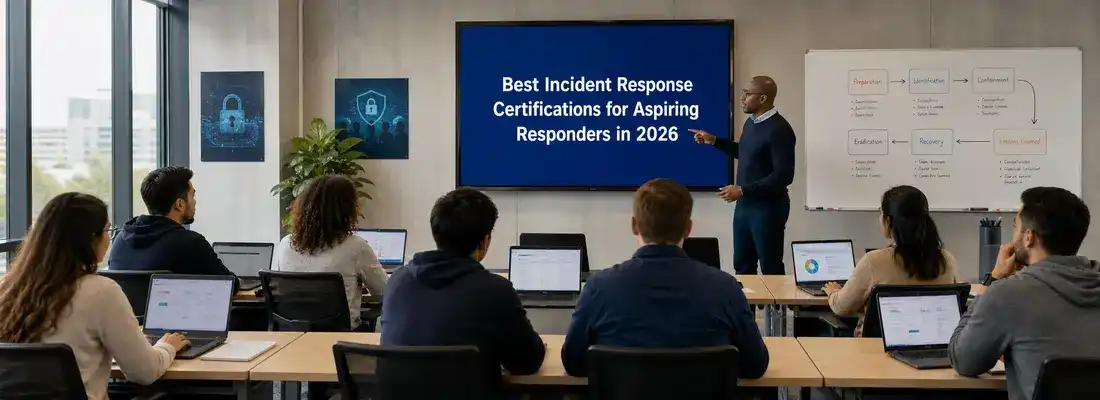
The right incident response certification depends on where you are now. A first SOC role, a structured handling process and senior forensic investigation each call for a different...
Every production incident starts with a simple question: "Has this happened before?" I've lost count of how many incident bridges I've joined where that question came up within the...
In Part 1 of this guide, we examined two common incident scenarios: cross-account Amazon Simple Storage Service (Amazon S3) data deletion with ransomware implications, and cryptocu...
A coach on a Counter-Strike 2 broadcast has about three seconds to call a rotation before the round is lost. No time to convene a meeting. No time to check with legal. Just a heads...
<figure data-wp-context="{&quot;imageId&quot;:&quot;6aa2f13c0eaa8&quot;}" data-wp-interactive="core/image" data-wp-key="6aa2f13c0eaa8&qu...
A new advisory from the Cybersecurity and Infrastructure Security Agency outlines how organizations can strengthen detection, response and protections in information technology (IT...
Every mature engineering team has a Security Incident Response Plan, refined over years of postmortems. But when the incident involves AI — a toxic hallucination with real conseque...
A host is isolated. A malicious process is killed. A compromised credential is revoked before an attacker can use it again. Detection and response worked exactly as intended, autom...
Alert fires at 3am.Continue reading on Medium »
AWS CloudTrail logs contain the evidence you need when investigating suspicious activity in your AWS environment, but knowing which fields matter and how to interpret them can mean...
Incident Management software helps IT teams detect, prioritize, coordinate, and resolve service disruptions before they affect users and business operations further. These platform...
Every incident goes through a series of stages before it’s resolved. It starts when an issue is reported, moves through diagnosis and resolution, and ends once the service is fully...
 🚨 INCIDENT REPORT | 5W & 1H APPROACH WITH HSE Trainer 🚨🔥 One incident can become a powerful safety lesson — if we investigate, learn, and act.This incident involve...
A cyber incident does not wait for the legal team to finish a licensing matrix. The first hour is messy: security analysts are checking logs, the CTO wants to know whether systems...
В последнее время всё чаще прилетают вопросы и просьбы о консультации после самых разных инцидентов: кого‑то зашифровали, где‑то поломали инфраструктуру, где‑то увели корпоративную...
Incident Management metrics help IT teams measure how effectively they detect, respond to, and resolve service disruptions. These numbers bring operational visibility, and they sho...
Walk into a modern enterprise security operations center today, and you'll discover just how inexpensive 65-inch monitors are: The walls are covered with them, showing dashboards f...
Data breach communications start before the SEC clock does. See the 24-hour plan, the four-business-day rule and IBM's $4.99 million average breach cost.
Cloud outages can range from global service disruptions to issues isolated to a specific region, zone, or even just your project, workload or application. If you suspect a Google C...
<p>Five steps to ensure the core of your business can get back up and running.</p>
A new report by ISACA found that 71% of orgs have not run AI incident response exercises as teams face rising pressure
Agentic AI can help SecOps teams investigate alerts by gathering context, correlating signals, and surfacing evidence-backed recommendations, without handing over control of respon...
Using AI for Incident Management is one of the most popular applications of predictive analytics and automation in ITSM. A recent study found that adoption of AI-assisted incident...
Use SocialBu to discover ideas, generate post drafts, and schedule them across your social channels.