VCF Automation Integration with OIDC External IDP (Keycloak)
Introduction VCF Automation supports integration with identity provider protocols for identity and access management. The supported identity provider types are:
Search fresh public links, source activity, and ready-to-use post angles for Federated Identity.
Fresh curated links around Federated Identity are collected here so marketers can spot useful updates and turn timely ideas into posts faster.
Recent items include:
Recent curated links from global sources. Generate one free draft from any story, then use SocialBu to schedule and refine your content calendar.
Introduction VCF Automation supports integration with identity provider protocols for identity and access management. The supported identity provider types are:
A federated gateway provides secure, policy-aware access to tool servers. The thing that made me stop and rethink our whole approach to agentic tooling was a text file.
<p style="text-align: justify;"><a href="https://i0.wp.com/cormachogan.com/wp-content/uploads/2026/09/native-object-storage.webp?ssl=1"><img data...
<div><img width="300" height="150" src="https://blogs.vmware.com/wp-content/uploads/2026/10/cybersecurity-awareness-banner-1200x600-1.png" cl...
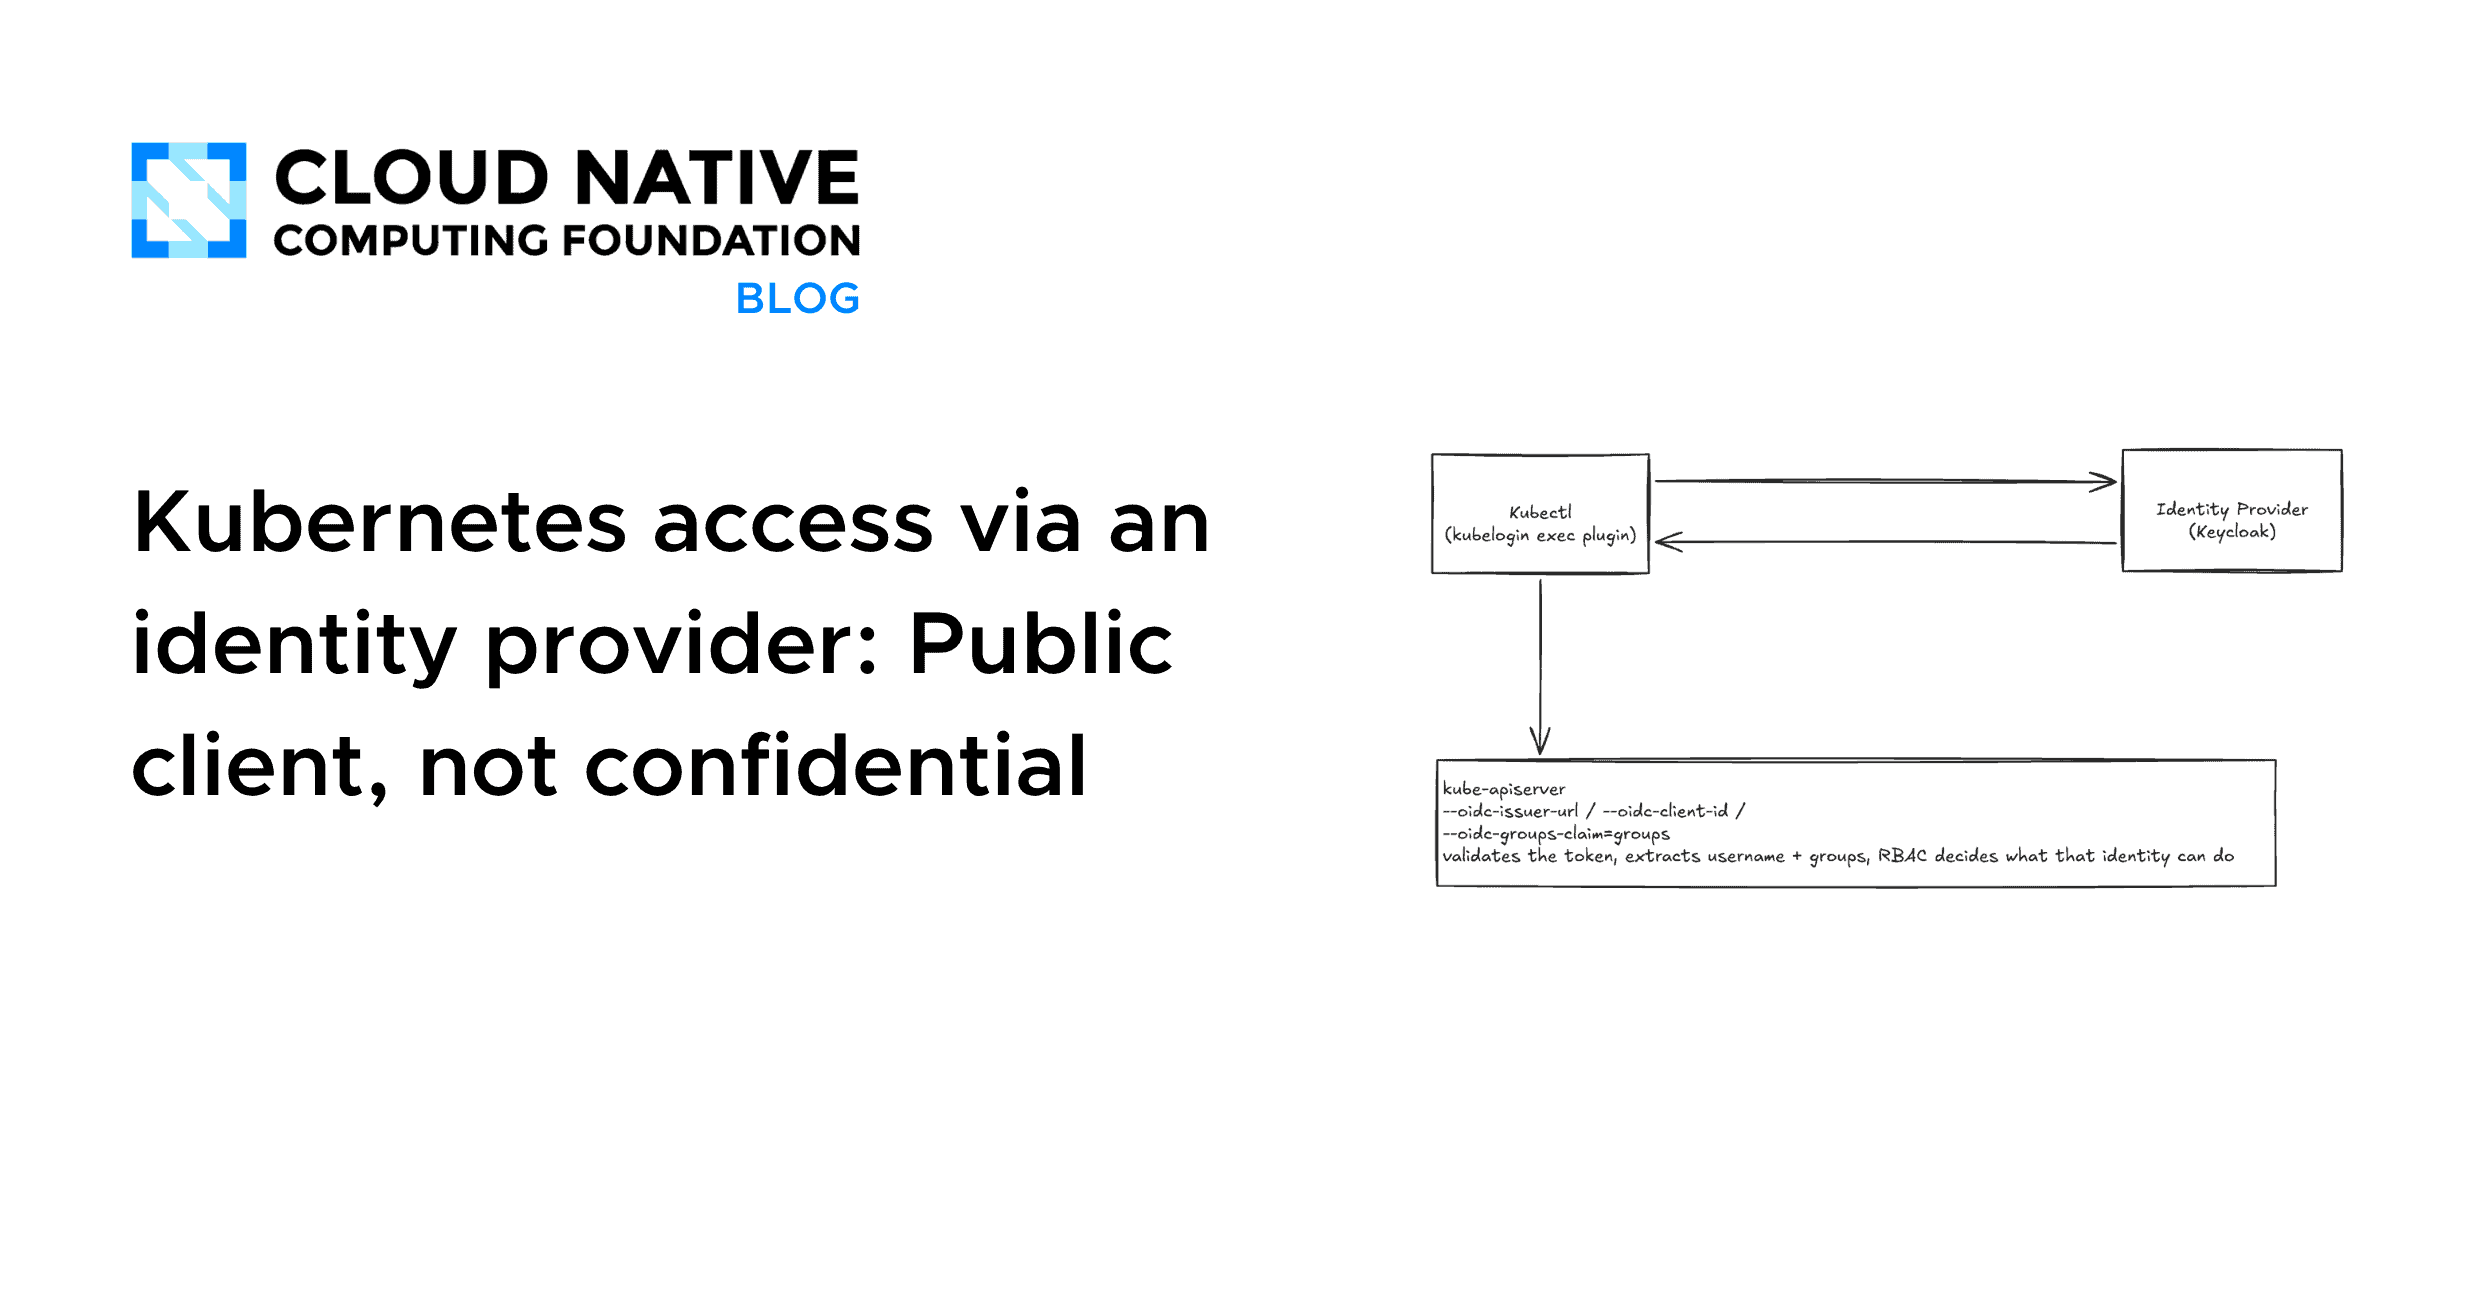
Access control belongs on the same day-zero checklist as networking and storage. On most on-prem clusters, it never makes the list. The Identity Gap Managed cloud Kubernetes ships...
Single sign-on is a solved problem. You redirect to an identity provider, it tells you who the person is, you mint a session. Every framework has a library for it. Then you try it...
An Identity Fabric knits fragmented identity systems into a coherent layer that observes how identities behave across applications, APIs, and infrastructure. As enterprise access s...
<p>If you&#8217;re moving to VMware Cloud Foundation (VCF) 9.x, one of the first architectural decisions you must consider is setting</p>
When there is corporate restructuring (like a merger or split), most IT teams often focus on getting emails, files and business applications running in the new environment. And fai...
Fragmented state laws and inconsistent standards have created gaps in identity verification and transactional risk for financial institutions. But even without a consistent standar...
With identity becoming the new security perimeter, many MSPs are looking for ways to simplify identity and access management (IAM) while delivering stronger protection to their cus...
Foundry IQ's pitch is that your agents get one endpoint for grounded, cited, multi-source context instead of a hand-rolled retrieval stack. What doesn't get talked about enough is...
Trusted Identity Propagation with AWS IAM Identity Center now works across Regions. Learn how to share AWS Lake Formation-governed Amazon S3 and Amazon Redshift data in one Region...
<figure data-wp-context="{&quot;imageId&quot;:&quot;6aa33ccab66e6&quot;}" data-wp-interactive="core/image" data-wp-key="6aa33ccab66e6&qu...
Most modern web and mobile apps don’t build authentication from the ground up. People want... The post OpenID Connect: Verifying User Identity on Top of OAuth 2.0 appeared first on...
SSO is table stakes for enterprise deals, but building it into your app yourself means writing SAML controllers, parsing XML assertions, and handling IdP-specific quirks for each p...
AWS IAM Identity Center integrates with external identity provider (IdP) to provide customers with a centralized authentication and authorization solution for AWS resources across...
September 2, 2026: This post was republished to include Active Directory migration strategies and automation for permission sets. AWS IAM Identity Center manages user access to Ama...
Stuart Gentle Publisher at Onrec 08 Sep 2026|Digital Identity in the US: From One-Time Verification to Continuous TrustUS digital identity is entering a new phase. Instead of requ...
The way we handle trust globally is broken. Not because we lack the technology, but because institut...
We have spent thirty years building an internet that is extraordinarily good at moving information and increasingly good at moving money, but remarkably bad at establishing who or...
Quick Answer: Microsoft Entra ID is the bundled default for M365 estates; Okta leads neutral catalog breadth; Ping Identity owns complex enterprise; JumpCloud wins SMB directory+SS...
Identity visibility is a starting point for modern identity security, because stolen and misused credentials are among the most frequently reported initial access vectors in breach...
Every app eventually needs to answer two questions: "who is this person?" and "what are they allowed to do?" Many tutorials either focus on integrating a specific authentication pr...
Use SocialBu to discover ideas, generate post drafts, and schedule them across your social channels.