New Serious PHP Vulnerabilities Released and Patched
PHP maintainers have released two critical vulnerabilities: PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35 fix two critical vulnerabilities that can allow unauthenticated remote code execut...
Search fresh public links, source activity, and ready-to-use post angles for Critical Vulnerabilities.
Fresh curated links around Critical vulnerabilities are collected here so marketers can spot useful updates and turn timely ideas into posts faster.
Recent items include:
Recent curated links from global sources. Generate one free draft from any story, then use SocialBu to schedule and refine your content calendar.
PHP maintainers have released two critical vulnerabilities: PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35 fix two critical vulnerabilities that can allow unauthenticated remote code execut...
Multiple critical security flaws have been disclosed in WordPress plugins and themes, including WPMU DEV Dashboard, Avada, TranslatePress, Pods, and GiveWP, that could lead to auth...
Introduction Two critical security vulnerabilities affecting PHP have been identified that result in unauthenticated remote code execution (RCE) for any PHP application. The vulner...
This story is developing and was written before PHP's scheduled 14:00 UTC release on October 21. Once the release is out, the affected and fixed versions below are confirmed by the...
GitLab released fixes on October 21 for a flaw that lets an attacker run code on a self-managed server without logging in, and it affects every version of the software going back t...
At 14:00 UTC on October 21, PHP released patches to two critical CVEs, both of which can lead to remote code execution. CVE-2026-109618 addresses an RCE through an out-of-memory er...
Two of 31 newly disclosed flaws in Progress Software's MarkLogic Server database could let an account given only some management privileges take administrator control of the server...
Two critical vulnerabilities in PHP were leaked one day before their scheduled disclosure and security patches
Crucial vulnerabilities in a programming language that underpins much of the internet are so severe that European and British authorities have recommended websites temporarily go o...
The PHP Foundation has revealed two serious vulnerabilities that could impact millions of websites. Security experts warn that failure to quickly patch the flaws could have dire co...
MariaDB maintainers have disclosed ten vulnerabilities affecting database server components, Linux packaging, and Connector/C. Under specific conditions, these flaws could lead to...
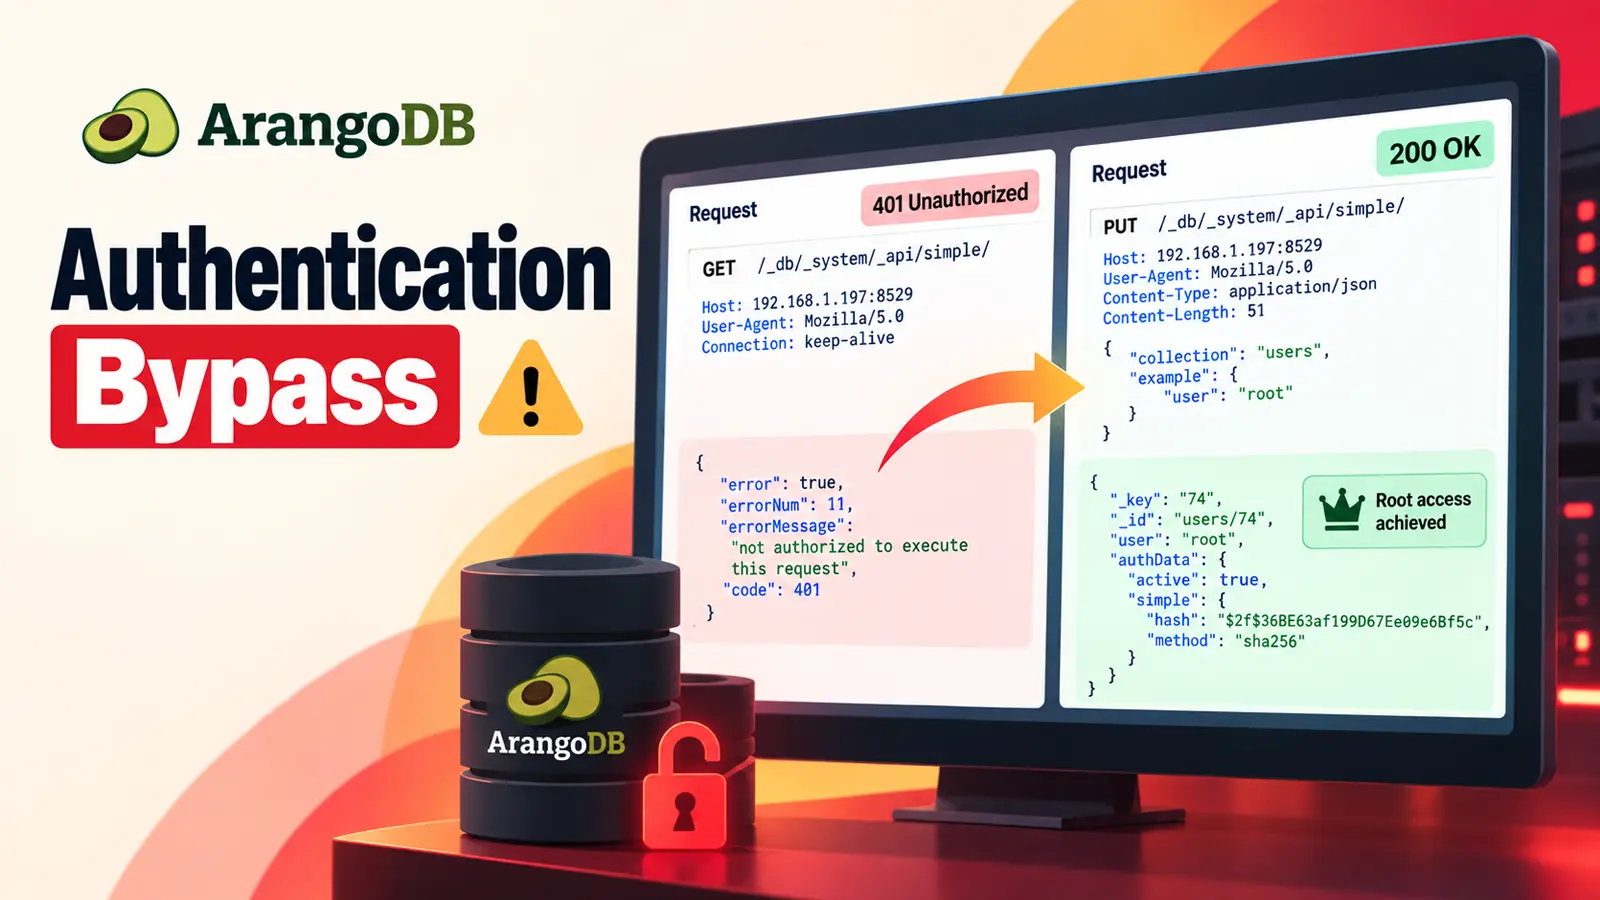
Two critical ArangoDB vulnerabilities can allow unauthenticated attackers to access protected database APIs and, after obtaining valid database access, escalate to root-level code...
Two critical flaws in ArangoDB can let an outsider bypass login controls, read or alter database data, and then gain root-level code execution on the underlying host. The issues af...
SAP has released security updates to address multiple vulnerabilities, including a maximum-severity flaw in SAP Extended Passport (EPP) Processing that could have a severe impact o...
Citrix has disclosed a critical memory overflow vulnerability in NetScaler ADC and NetScaler Gateway that could enable remote code execution or denial of service under specific con...
Ubiquiti has patched 21 critical-severity vulnerabilities spanning nearly its entire UniFi product line, warning that attackers with only network access could chain the flaws to by...
Four security flaws described in the supplied Apache Struts advisories could expose affected applications to remote code execution, denial-of- service, and unintended data disclosu...
ServiceNow has released patches for four security flaws impacting the ServiceNow AI Platform, three of them rated 10.0 on the CVSS scoring system and exploitable, in certain circum...
Two WordPress Core vulnerabilities can be chained to execute remote code without authentication, according to analysis by Seqrite researcher Amruta Wagh. Dubbed WP2Shell, the explo...
Progress has disclosed 31 vulnerabilities in MarkLogic Server that could lead to privilege escalation, server-side code execution, authentication bypass, credential exposure, and d...
Two critical vulnerabilities in Citrix NetScaler ADC and NetScaler Gateway that allow remote code execution have been exploited in the wild, Citrix confirmed on September 27. It re...
Drupal has patched two critical vulnerabilities that could allow attackers to execute code remotely on websites running any supported version of the content management system. [......
Drupal core has a critical flaw in its Field UI module that could let an attacker run code on the site's server, and fixes were shipped on October 14 in Drupal 11.4.10, 11.3.19, an...
A critical vulnerability impacting Orkes Conductor is being actively exploited in the wild, according to Fortinet. The vulnerability in question is CVE-2026-58138 (CVSS v3.1 score...
Use SocialBu to discover ideas, generate post drafts, and schedule them across your social channels.