Latest updates for Credential Theft

Fresh curated links around Credential theft are collected here so marketers can spot useful updates and turn timely ideas into posts faster.

Recent items include:

  • AWS Shows How Hackers Can Turn Stolen Cloud Credentials Into Full-Scale Attacks
  • Credential-Stealing GitHub Actions Workflows Planted in Tens of Thousands of Repositories
  • Infostealer Logs Expose Replayable AI Tokens That Can Bypass MFA

Post angles to try

Share the most useful takeaway for your audience.
Turn one article into a quick practical checklist.
Ask your audience how this shift affects their work.
Turn angles into scheduled posts

Fresh articles and ideas

Recent curated links from global sources. Generate one free draft from any story, then use SocialBu to schedule and refine your content calendar.

cybersecuritynews.com /1 month ago

AWS Shows How Hackers Can Turn Stolen Cloud Credentials Into Full-Scale Attacks

Stolen cloud credentials can turn an incident into a wider breach. An attacker who gets a valid AWS key or session can enter as an approved user and move toward sensitive systems....

Read source
thehackernews.com /2 weeks ago

Credential-Stealing GitHub Actions Workflows Planted in Tens of Thousands of Repositories

Cybersecurity researchers have disclosed details of an ongoing credential-theft campaign that has compromised two high-profile open-source maintainer accounts to push a malicious w...

Read source
thehackernews.com /1 month ago

Infostealer Logs Expose Replayable AI Tokens That Can Bypass MFA

Cybercriminals are hijacking artificial intelligence (AI) user accounts via information stealer logs to create "stolen keys" that grant illicit access to tools from model providers...

Read source
gbhackers.com /3 weeks ago

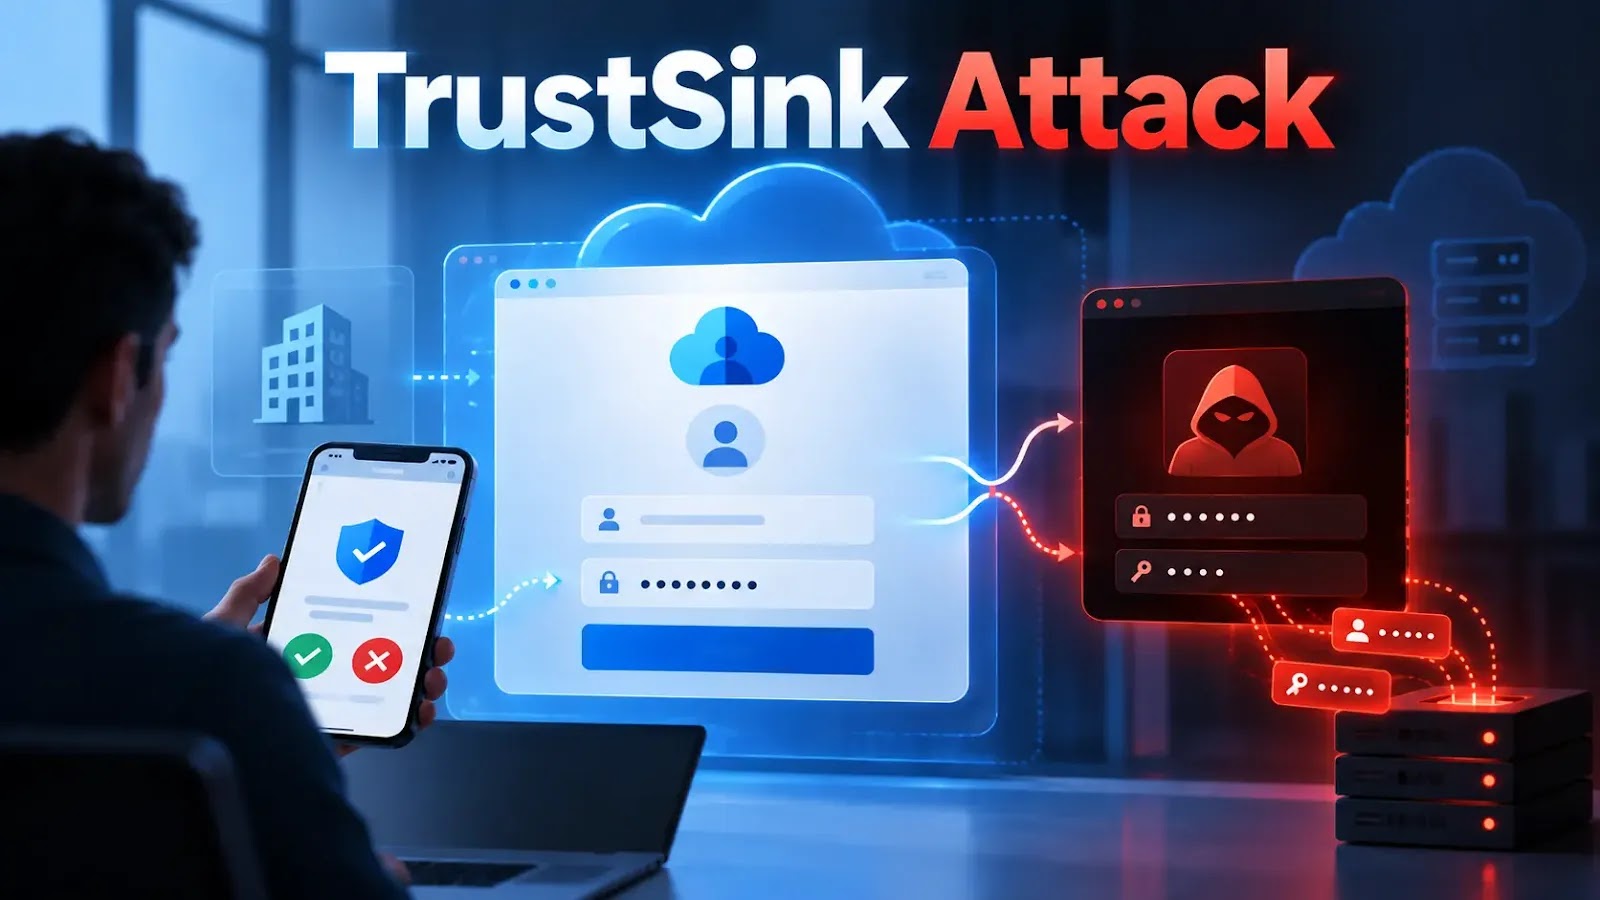
Microsoft Entra TrustSink Attack Uses Rogue MFA Provider to Steal Passwords

TrustSink, a post-compromise credential-phishing technique that abuses Microsoft Entra External Authentication Methods (EAMs) to place a rogue password prompt inside an otherwise l...

Read source
theregister.com /2 weeks ago

AWS AgentCore security undone by prompt requesting credentials

Tokens transmitted in metadata, weak VM isolation, and expansive permissions make hacking a lot easier

Read source
cybersecuritynews.com /2 weeks ago

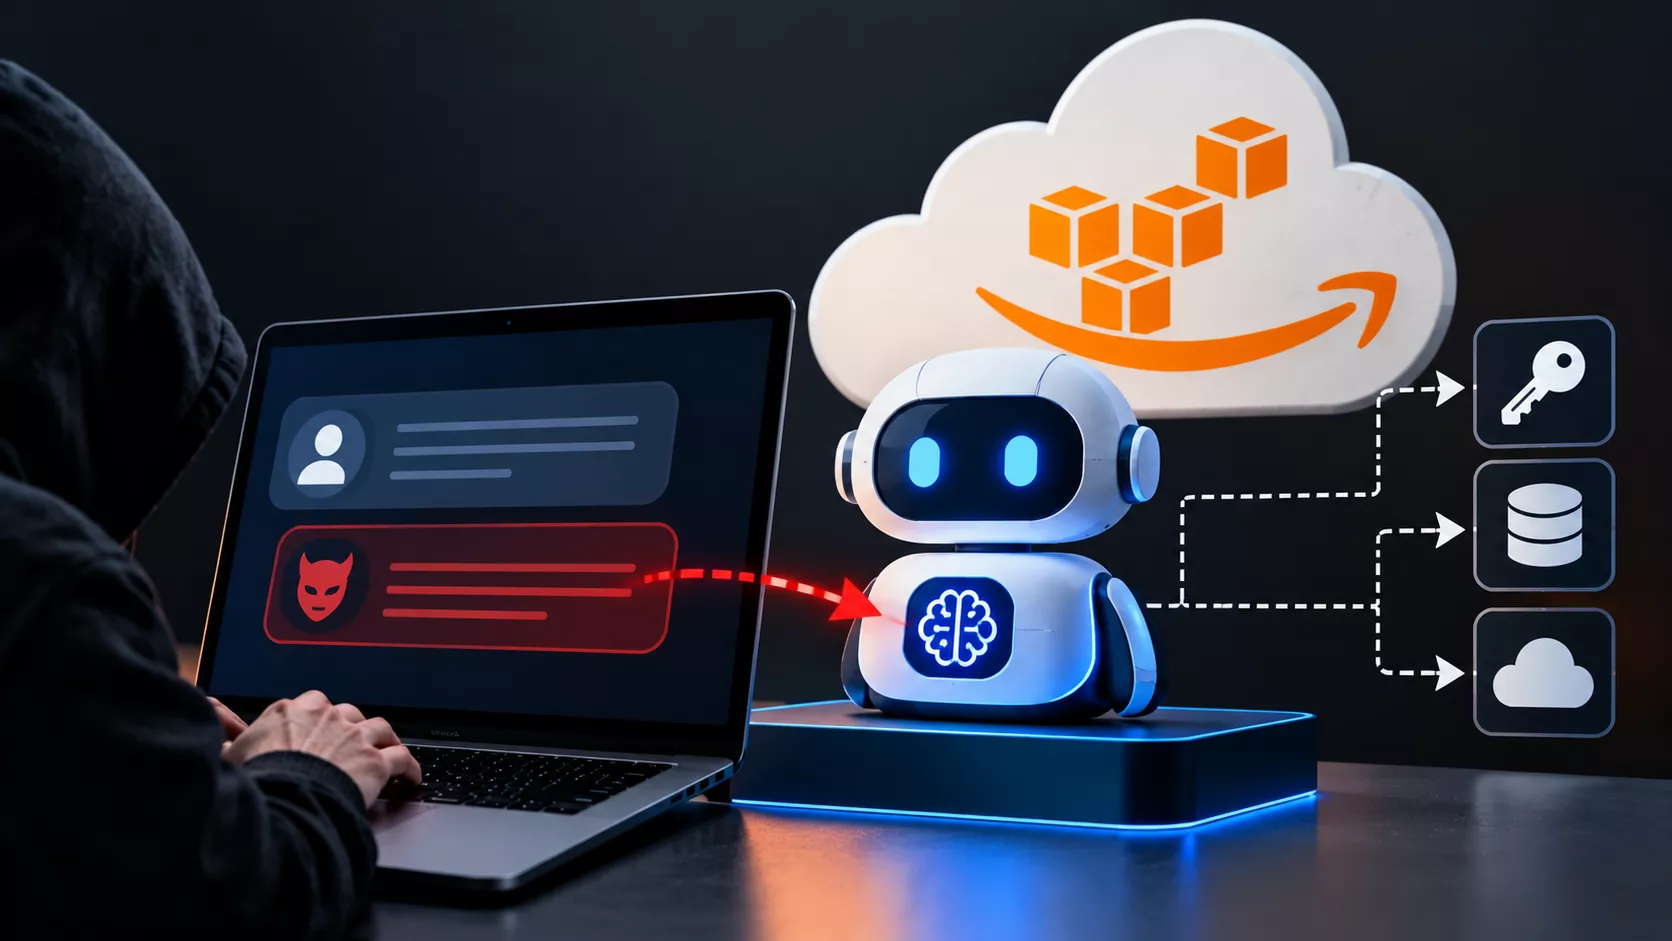
One Prompt Could Hijack AWS AI Agents and Steal Cloud Credentials

A single prompt sent to a public-facing AI agent could have exposed every Amazon Bedrock AgentCore agent in the same AWS account and region, according to new research from Zenity L...

Read source
cybersecuritynews.com /3 weeks ago

TrustSink Attack Uses Rogue MFA Provider to Steal Microsoft Entra Passwords During Legitimate Logins

TrustSink is a newly disclosed identity attack that turns a trusted MFA step into a password-stealing trap. Rather than sending victims to a clearly fake website, it places a convi...

Read source
cybersecuritynews.com /3 weeks ago

Hackers Poison Trusted Software Updates to Steal Developer and Cloud Credentials

Hackers are turning trusted software updates into a route for stealing developer and cloud credentials. Recent supply chain incidents show how a single altered package, build actio...

Read source
cofense.com /4 days ago

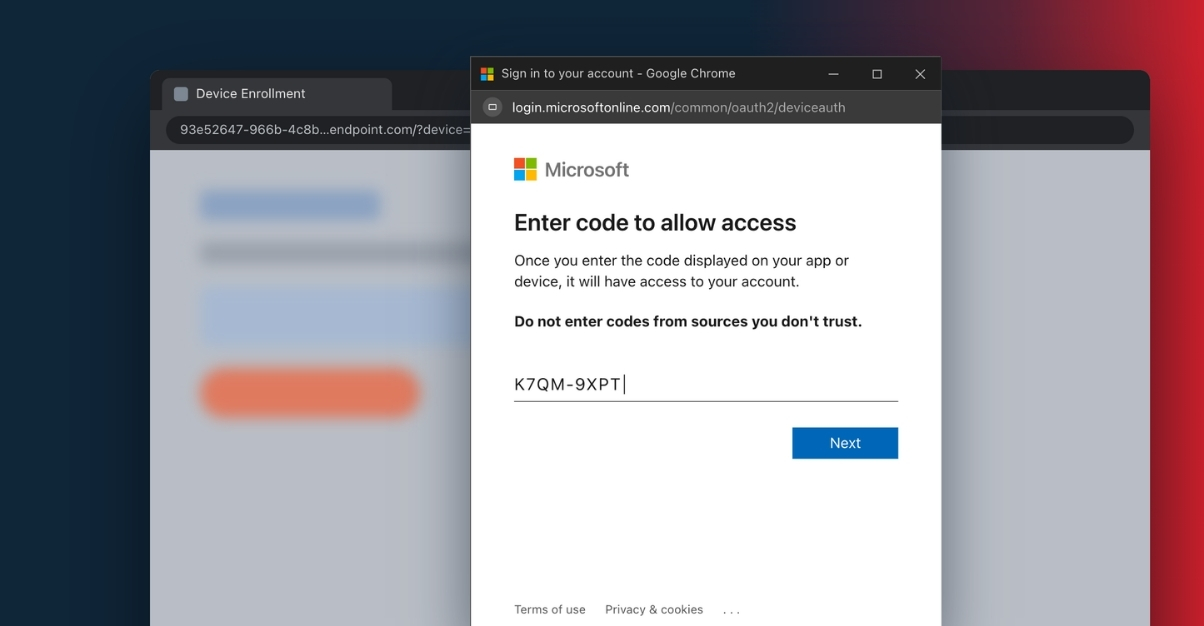
Beyond Passwords: How Attackers Abuse Device Code Authentication

Cofense Phishing Defense Center (PDC) analysts uncovered a device code phishing campaign that impersonates trusted brands, including Microsoft, Syncfusion, and Mimecast, to trick u...

Read source
metadrop.net /1 month ago

Metadrop: How to eliminate manual credential sharing in Drupal integrations with a Vault service

Credentials still travel by email and by Slack on projects that are otherwise carefully built. Every integration with an external service needs them, and forwarding them from one p...

Read source
gbhackers.com /1 month ago

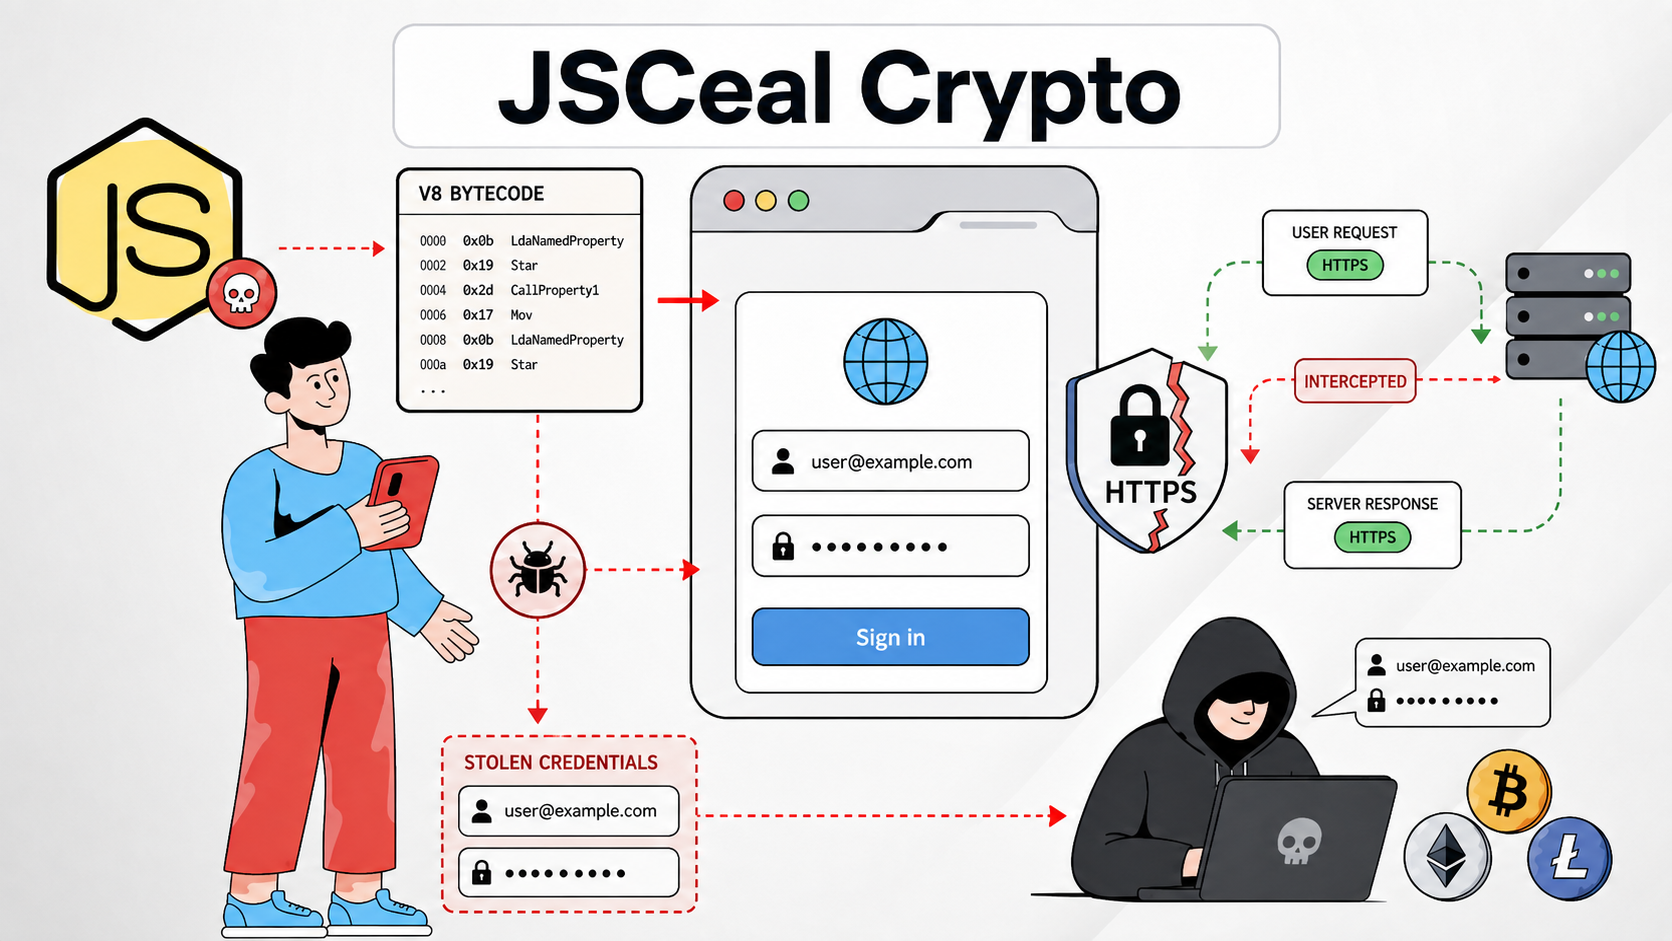
JSCeal Crypto Stealer Uses V8 Bytecode to Steal Browser Credentials and Intercept HTTPS

A sophisticated cryptocurrency-focused information stealer that hides its malicious logic inside compiled V8 JavaScript bytecode. JSCeal, also tracked by some vendors as WEEVILPROX...

Read source
thehackernews.com /2 days ago

LiteLLM Suspects GitHub Token Leak in AI Gateway Logs Behind Malicious Package Release

LiteLLM on Wednesday disclosed that threat actors compromised "multiple independent security controls" to push a malicious version of the Python package containing a credential ste...

Read source
thehackernews.com /1 month ago

Compromised MemTensor Packages Deliver sckit Credential Stealer via npm and PyPI

Unknown threat actors have managed to compromise two legitimate MemTensor packages across the npm and Python Package Index (PyPI) repositories to push a platform-specific Go-based...

Read source
bleepingcomputer.com /1 month ago

Passkey-themed phishing attacks lead to Microsoft 365 data theft

Microsoft says threat actors linked to ShinyHunters, Helix, and other extortion gangs are using passkey and single sign-on-themed social engineering attacks to compromise corporate...

Read source
gbhackers.com /1 month ago

New Phishing Campaign Abuses Windows Mshta.exe to Steal Credentials and Secrets

A newly identified phishing campaign is abusing the legitimate Windows utility mshta.exe to execute malicious HTML Application (HTA) files, conduct system reconnaissance, and poten...

Read source
blog.knowbe4.com /1 month ago

Attackers Use Passkey-Themed Phishing to Breach Cloud Environments

Researchers at Microsoft are tracking a social engineering campaign that uses passkey-themed lures to trick users into granting persistent access to their accounts and online work...

Read source
cybersecuritynews.com /3 weeks ago

Exposed WordPress Backups Became a Gold Mine of AWS and Email Credentials

Exposed WordPress backups have become a valuable source of cloud and email credentials for attackers using a toolkit called TIKTOUK. Rather than relying on one technique, its compo...

Read source
cybersecuritynews.com /1 month ago

LLMjacking Attack Uses Leaked AWS IAM Key to Steal Paid AI Model Access

A newly documented cloud intrusion shows how quickly attackers can turn a single leaked AWS credential into a revenue stream by hijacking access to premium AI models, a technique r...

Read source
bleepingcomputer.com /1 month ago

Rogue external MFA providers can steal passwords during logins

Security researchers developed an attack that lets hackers with privileged access register a rogue external MFA provider that steals users' passwords during legitimate login attemp...

Read source
smartermsp.com /2 weeks ago

Cybersecurity Threat Advisory: TrustSink attack targets Microsoft Entra ID

TrustSink is an attack technique that abuses Microsoft Entra ID’s federated trust model. It uses a rogue MFA provider to intercept user credentials during legitimate login attempts...

Read source
cybersecuritynews.com /1 month ago

Hackers Pose as OpenAI, Anthropic and DeepSeek to Steal Credentials and Secrets

Threat actors are impersonating web crawlers from OpenAI, Anthropic, DeepSeek, and other major organizations to scan websites for exposed credentials and sensitive configuration fi...

Read source
bleepingcomputer.com /1 month ago

Your Employee’s Password Appeared in an Infostealer Log. Now What?

Infostealers can expose far more than passwords, including authenticated sessions that may let attackers bypass MFA. Flare explains how defenders can prioritize compromised identit...

Read source
gbhackers.com /2 weeks ago

AWS Bedrock AgentCore Flaw Allowed Attackers to Hijack AI Agents Using a Single Prompt

A newly disclosed attack chain in Amazon Bedrock AgentCore that could turn a single malicious prompt into credential theft and compromise of other AI agents within the same AWS acc...

Read source
cybersecuritynews.com /1 month ago

Hackers Use Passkey-Themed Phishing to Hijack Microsoft 365 Accounts and Steal Cloud Data

Hackers are using passkey-themed phishing to take control of Microsoft 365 accounts and collect cloud data. It can defeat MFA protections. The campaign starts with calls and texts...

Read source

Turn fresh research into a full content calendar

Use SocialBu to discover ideas, generate post drafts, and schedule them across your social channels.

Sources covering Credential Theft

smartermsp.com

Recent coverage from public sources
Public source

blog.knowbe4.com

Recent coverage from public sources
Public source

cofense.com

Recent coverage from public sources
Public source

cybersecuritynews.com

Recent coverage from public sources
Public source

feeds.feedburner.com

Recent coverage from public sources
Public source

gbhackers.com

Recent coverage from public sources
Public source