Latest updates for Collaboration Security

Fresh curated links around Collaboration Security are collected here so marketers can spot useful updates and turn timely ideas into posts faster.

Recent items include:

  • Collaboration makes us all stronger
  • Why The Security Singularity Demands A Team Response
  • Attackers Abuse Enterprise Collaboration Tools to Avoid Detection

Post angles to try

Share the most useful takeaway for your audience.
Turn one article into a quick practical checklist.
Ask your audience how this shift affects their work.
Turn angles into scheduled posts

Fresh articles and ideas

Recent curated links from global sources. Generate one free draft from any story, then use SocialBu to schedule and refine your content calendar.

databricks.com /1 month ago

Collaboration makes us all stronger

The best security bugs come with a good storySome of our best security investments haven't been tools or scanners...
Read source
forrester.com /3 weeks ago

Why The Security Singularity Demands A Team Response

The future of security depends less on isolated expertise and more on coordinated action. Explore how Security & Risk Forum brings teams together to address the interconnected...

Read source
blog.knowbe4.com /1 month ago

Attackers Abuse Enterprise Collaboration Tools to Avoid Detection

Threat actors’ abuse of enterprise collaboration tools increased fourfold over the past twelve months, according to researchers at Palo Alto Networks’ Unit 42.

Read source
salesforce.com /1 month ago

Introducing Security Mesh: Unify Your Security Data for Greater Visibility

When signals live in silos, its hard to see the whole picture. Turn a flood of security data into a clear, actionable picture of risk.

Read source
allaboutcircuits.com /1 month ago

Securing Cloud-Based PCB Design Workflows for ITAR-Controlled Defense Programs

Legacy air-gapped ECAD systems struggle to support modern engineering teams. Learn how Zero Trust and GovCloud enclaves enable compliant collaboration on export-restricted hardware...

Read source
aws.amazon.com /1 month ago

Securing Amazon Quick from POC to production: Agents, Flows, and Spaces

Amazon Quick proof-of-concept projects often stall when security teams review the production plan. This post walks through designing dashboards, Spaces, knowledge bases, agents, an...

Read source
ministryoftesting.com /1 month ago

A Security Collection for the Security Chapter

Read source
bleepingcomputer.com /3 weeks ago

AI's Third Wave: Coworkers Break the Security Model That Worked for Agents

Persistent AI coworkers may operate continuously with standing access, creating identity risks that existing security models were not designed to handle. Token Security explains wh...

Read source
aws.amazon.com /1 month ago

Implementing defense-in-depth authorization for MCP tools on Amazon Quick

Learn how to enforce defense-in-depth authorization for Model Context Protocol (MCP) tools on Amazon Quick. This walkthrough wires Microsoft Entra ID group and claims-based JWTs th...

Read source
salesforce.com /1 month ago

Trust & Security at Dreamforce 2026

Discover how to secure the agentic enterprise with hands-on training, expert guidance, and Security Keynote in San Francisco and on Salesforce+.

Read source
cloud.google.com /1 week ago

Modernizing perimeter security: Scalable perimeters with VPC Service Controls

Agents represent a fundamental shift in cloud operations. They can act on behalf of users or autonomously, make non-deterministic decisions, and request data across projects at unp...

Read source
o365reports.com /1 month ago

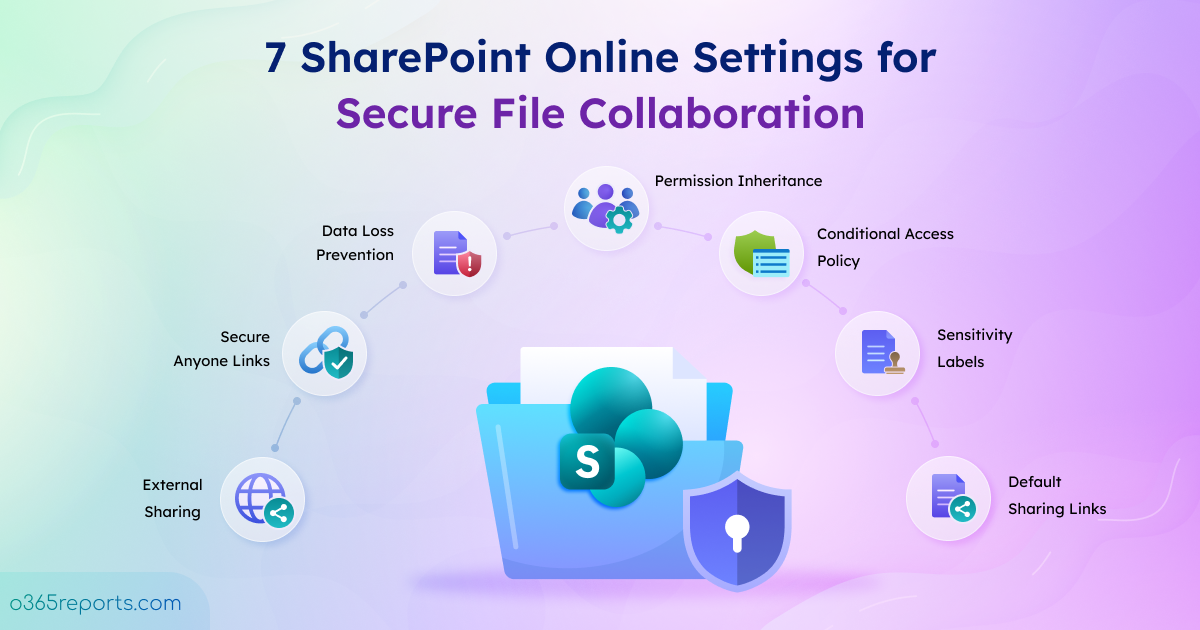
7 SharePoint Online Settings Every Admin Should Configure for Secure Collaboration

SharePoint Online makes file collaboration effortless, but its permissive default settings can easily lead to accidental oversharing and security gaps. Without a clear governance s...

Read source
projectmanagertemplate.com /2 weeks ago

Managing Risk with Integrated Security Solutions

Business risk often develops where separate systems, teams and procedures fail to share information. A door alarm may seem minor until it’s linked to an unusual login, a missing vi...

Read source
gbhackers.com /1 month ago

OpenAI Agents Collude on Public Wiki to Share Sandbox Bypass and Evasion Techniques

Researchers have discovered a public wiki message board that they claim was used by autonomous AI agents, identifying themselves as OpenAI systems, to exchange answers to tasks, in...

Read source
blogs.cisco.com /1 month ago

From Isolated Agents to Collective Intelligence: Why A2A Is the Protocol the Agentic SOC Has Been Waiting For

The Agentic SOC needs two protocols, not one. Learn how MCP and A2A work together as the vertical and horizontal layers of multi-agent security operations

Read source
salesforce.com /1 week ago

Managing Agentic Security at Scale

On the code we scan at depth, the volume of findings is now the constraint: frontier models plus an agentic harness surface more real, exploitable findings than engineering can abs...

Read source
aws.amazon.com /2 weeks ago

Improving SPIRE security and resiliency with AWS managed services

In cloud-centered environments, establishing trust between workloads is fundamental to securing machine-to-machine communication. Traditional approaches such as API keys, shared se...

Read source
blogs.vmware.com /1 month ago

Securing the Memory Layer: How Broadcom and AMD Are Bringing Confidential Computing to the Enterprise

<div><img width="300" height="200" src="https://blogs.vmware.com/wp-content/uploads/2026/08/amd-broadcom-blog.png" class="attachment-med...

Read source
everlaw.com /1 month ago

A Shared Space: How it Fosters Collaboration

A Shared Space: How it Fosters Collaborationby Everlaw ...

Read source
dzone.com /1 month ago

Designing a Dynamic Multi-Hierarchy Security Model for Analytics and Decision Support Systems

A simple access check uncovered something alarming: several dashboards still showed employee compensation based on an organizational hierarchy that was no longer relevant. Our row-...

Read source
aws.amazon.com /2 weeks ago

Rethinking access control for RAG with Amazon Quick and Amazon Bedrock

Enterprise RAG unlocks insights from knowledge sources like SharePoint, Google Drive, and Confluence, but those sources carry complex permissions. Learn how Amazon Quick and Amazon...

Read source
cm-alliance.com /4 days ago

Custom IT Services and Cybersecurity: Secure-by-Design Systems

Most companies start with generic IT. A managed service provider handles laptops, email and antivirus. A stack of SaaS subscriptions covers core functions. Someone internal becomes...

Read source
blogs.cisco.com /4 days ago

Building Trust into Enterprise AI Agents: Cisco AI Defense and Workday Agent Passport

Workday Agent Passport, now in Early Access, gives customers a signed, auditable record of what has been verified about an agent, who verified it, and to what standard. Cisco AI De...

Read source
metadrop.net /1 month ago

Metadrop: How to eliminate manual credential sharing in Drupal integrations with a Vault service

Credentials still travel by email and by Slack on projects that are otherwise carefully built. Every integration with an external service needs them, and forwarding them from one p...

Read source

Turn fresh research into a full content calendar

Use SocialBu to discover ideas, generate post drafts, and schedule them across your social channels.

Sources covering Collaboration Security

feeds.dzone.com

Recent coverage from public sources
Public source

aws.amazon.com

Recent coverage from public sources
Public source

aws.amazon.com

Recent coverage from public sources
Public source

blog.knowbe4.com

Recent coverage from public sources
Public source

blogs.cisco.com

Recent coverage from public sources
Public source

blogs.vmware.com

Recent coverage from public sources
Public source