Latest updates for Cui Attacks

Fresh curated links around CUI Attacks are collected here so marketers can spot useful updates and turn timely ideas into posts faster.

Recent items include:

  • Chinese Hackers Exploit Chrome-Windows Zero-Day Chain to Deploy CLEANGULP Malware
  • What Small and Mid-Size Defense Contractors Get Wrong About CUI Handling
  • Threat Actors Don’t Want Better Attacks. They Want Repeatable Ones

Post angles to try

Share the most useful takeaway for your audience.
Turn one article into a quick practical checklist.
Ask your audience how this shift affects their work.
Turn angles into scheduled posts

Fresh articles and ideas

Recent curated links from global sources. Generate one free draft from any story, then use SocialBu to schedule and refine your content calendar.

thehackernews.com /1 month ago

Chinese Hackers Exploit Chrome-Windows Zero-Day Chain to Deploy CLEANGULP Malware

A Chinese threat actor codenamed UTA0565 has been observed exploiting the recently disclosed Google Chrome-Microsoft Windows exploit chain as zero-days through fake websites. The...

Read source
dailycivil.com /3 weeks ago

What Small and Mid-Size Defense Contractors Get Wrong About CUI Handling

Controlled Unclassified Information (CUI) is any government-created or government-owned data that isn’t classified but still requires safeguarding under federal law, regulation, or...

Read source
thehackernews.com /1 month ago

Threat Actors Don’t Want Better Attacks. They Want Repeatable Ones

The most common way into a company last year was to ask. A web page tells the visitor to prove they are not a robot. While they read the instructions, it quietly places a command...

Read source
cybersecuritynews.com /1 month ago

Claude Code Opus 5 Auto Mode Hijacked via Prompt Injection to Execute Malicious Code

Claude Code Opus 5 in Auto Mode can be tricked into running malicious code via a simple website summary request. In a limited lab test, the attack reportedly succeeded in 60% to 80...

Read source
thehackernews.com /1 month ago

China-Linked UNC3569 Exploited Sogou Input Method Flaw to Deploy GRAYRABBIT Backdoor

A China-linked hacking group exploited a flaw in Sogou Input Method, one of the most widely used tools for typing Chinese characters on Windows, to install a backdoor on victims' c...

Read source
thehackernews.com /1 month ago

Attackers Exploit Critical Switchvox Flaw to Deploy Reverse Shells Without Credentials

Threat actors are exploiting a severe security vulnerability in Sangoma Switchvox, an enterprise VoIP platform, that could allow unauthenticated remote code execution. The vulnera...

Read source
thehackernews.com /1 month ago

CISA Adds Seven Exploited Flaws as Attackers Deploy Reverse Shells and Crypto Miners

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Wednesday added seven security flaws to its Known Exploited Vulnerabilities (KEV) catalog after they landed in a...

Read source
bleepingcomputer.com /1 month ago

Attackers conceal phishing lures using invisible Unicode characters

Threat actors have adopted the ASCII smuggling technique in phishing campaigns, using invisible Unicode characters to evade email security filters. [...]

Read source
bleepingcomputer.com /1 month ago

Hackers exploit Sangoma Switchvox flaw to deploy reverse shells

Attackers are actively exploiting CVE-2026-9586, an unauthenticated SQL injection vulnerability in the Sangoma Switchvox VoIP platform that can lead to remote code execution. [...]

Read source
gbhackers.com /1 month ago

Attackers Exploit MCP RCE, Blind Prompt Injection and Memory Credential Theft Against AI Infrastructure

Attackers are increasingly treating AI infrastructure as a high-value cloud entry point, exploiting exposed Model Context Protocol (MCP) services, agent frameworks, and AI gateways...

Read source
rorymon.com /1 month ago

AI Attacks on Critical Infrastructure, Grok Leaks Data & Critical Entra ID Flaw

<p>On this week’s episode, security agencies warn that attackers are using AI-generated tools to target industrial control systems, researchers demonstrate</p>

Read source
thehackernews.com /1 month ago

Attackers Exploit Issabel Framework Flaw Enabling Unauthenticated OS Command Execution

A critical security flaw in Issabel Framework, a web-based framework for the open-source unified communications PBX software, has come under active exploitation. The vulnerability...

Read source
bleepingcomputer.com /1 month ago

InfraTrust report warns network management systems under attack

Attackers are increasingly targeting the management systems used to control enterprise infrastructure, with several critical vulnerabilities actively exploited before or shortly af...

Read source
thehackernews.com /1 week ago

Cisco Warns of Active Attacks Exploiting New Critical Secure Email Gateway Vulnerability

Attackers are exploiting a critical flaw in Cisco Secure Email Gateway that lets a sender with no login write files to the appliance's operating system, Cisco said in an advisory o...

Read source
infosecurity-magazine.com /4 days ago

Siemens Customers Targeted by ClickFix Attackers Exploiting DLL Side-Loading Flaw

Siemens identified the activity to be from the Romulus multi-platform ClickFix campaign, with Siemens Software Center users urged to apply an update

Read source
thehackernews.com /2 weeks ago

UAC-0099 Targets Ukrainian Government Personnel With ASHVEIN RAT Hiding Commands in HTML

The Russia-aligned threat actor known as UAC-0099 has been attributed to a previously undocumented .NET infostealer and remote access trojan (RAT) codenamed ASHVEIN. According to...

Read source
bleepingcomputer.com /1 month ago

Critical ScreenConnect flaw now actively exploited in attacks

Attackers now exploit a critical-severity ConnectWise ScreenConnect vulnerability in the wild, according to the U.S. Cybersecurity and Infrastructure Security Agency (CISA). [...]

Read source
cofense.com /4 days ago

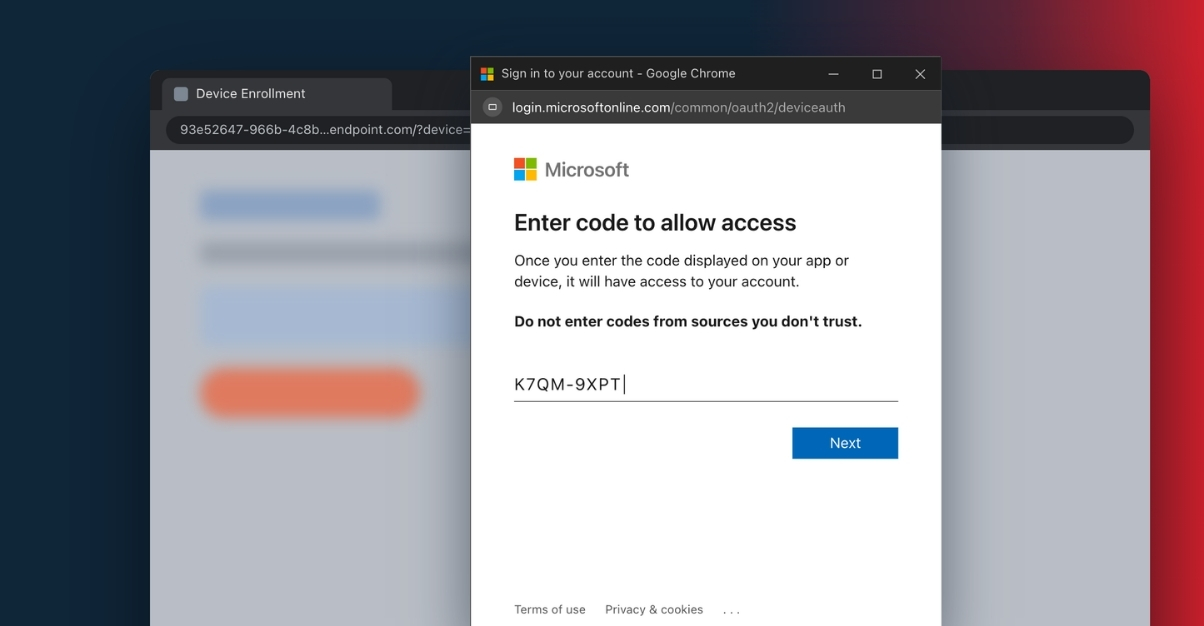
Beyond Passwords: How Attackers Abuse Device Code Authentication

Cofense Phishing Defense Center (PDC) analysts uncovered a device code phishing campaign that impersonates trusted brands, including Microsoft, Syncfusion, and Mimecast, to trick u...

Read source
thehackernews.com /2 days ago

Arista Warns of Critical VeloCloud SQL Injection Zero-Day Exploited in Attacks

Attackers are exploiting a zero-day SQL injection flaw in Arista's VeloCloud Orchestrator (VCO), the central management system for VeloCloud SD-WAN networks, the company said in an...

Read source
bleepingcomputer.com /1 month ago

BragJack attacks hijack AI browser agents through malicious extensions

BragJack, a proof-of-concept attack from Forever Security's Gal Weizman, hijacks the AI assistants in Chrome, Edge, Opera Neon, Perplexity Comet, and Claude in Chrome using one mal...

Read source
thehackernews.com /4 days ago

ClickFix Attackers Exploit Siemens Software Center Flaw to Deploy Remote Access Trojan

Siemens has addressed a DLL sideloading vulnerability impacting Siemens Software Center that it said has been exploited in ClickFix attacks. The high-severity vulnerability, track...

Read source
thehackernews.com /3 weeks ago

CISA Says Attackers Are Exploiting Two Critical Citrix NetScaler Flaws Globally

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Sunday added two critical Citrix NetScaler ADC and Gateway flaws to its Known Exploited Vulnerabilities (KEV) ca...

Read source
gbhackers.com /3 weeks ago

TerminalFix Attacks Deploy Lorem Ipsum Loader to Create Covert Tunnels Into Corporate Networks

A newly tracked intrusion set, STAC4924, is using TerminalFix social-engineering lures to deploy the Lorem Ipsum Loader and establish covert reverse tunnels into enterprise environ...

Read source
thehackernews.com /4 weeks ago

SharePoint RCE and MikroTik RouterOS Flaws Actively Exploited in the Wild

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Friday added two security flaws impacting Microsoft SharePoint and Mikrotik RouterOS to its Known Exploited Vuln...

Read source

Turn fresh research into a full content calendar

Use SocialBu to discover ideas, generate post drafts, and schedule them across your social channels.

Sources covering Cui Attacks

blogs.vmware.com

Recent coverage from public sources
Public source

cofense.com

Recent coverage from public sources
Public source

cybersecuritynews.com

Recent coverage from public sources
Public source

dailycivil.com

Recent coverage from public sources
Public source

feeds.feedburner.com

Recent coverage from public sources
Public source

gbhackers.com

Recent coverage from public sources
Public source