Latest updates for Breach And Attack

Fresh curated links around Breach and Attack are collected here so marketers can spot useful updates and turn timely ideas into posts faster.

Recent items include:

  • ARMORY CASTLE Exploits BeyondTrust
  • Attack Chains, Not Just Attack Surfaces: Why Testing Individual Techniques Misses the Point
  • Direct Send: How Attackers Weaponize Your Infrastructure Against You

Post angles to try

Share the most useful takeaway for your audience.
Turn one article into a quick practical checklist.
Ask your audience how this shift affects their work.
Turn angles into scheduled posts

Fresh articles and ideas

Recent curated links from global sources. Generate one free draft from any story, then use SocialBu to schedule and refine your content calendar.

cloud.google.com /1 week ago

ARMORY CASTLE Exploits BeyondTrust

Written by: Jayson Frost, Bryce Greathouse, Brian Meyer, John Palmisano, Rajesh Rajeshirke, Steve Rasch, John Wolfram Introduction  On October 15, BeyondTrust disclosed a vulnerab...

Read source
thehackernews.com /1 month ago

Attack Chains, Not Just Attack Surfaces: Why Testing Individual Techniques Misses the Point

Introduction Security teams have gotten pretty good at testing against what can hurt them. Can this EDR agent catch this payload? Will my organization fail the phishing simulation...

Read source
blog.knowbe4.com /1 month ago

Direct Send: How Attackers Weaponize Your Infrastructure Against You

Lead Analysts: Prabhakaran Ravichandhiran, Jeewan Singh Jalal

Read source
thehackernews.com /3 weeks ago

Know Your Enemy: Browser-Based Attack Techniques in 2026

Given that the browser is where business apps are accessed and used, it makes sense that attacks are happening there too. Most breaches today begin in a browser session. Often, the...

Read source
bleepingcomputer.com /1 week ago

The Blind Spots of Agentic Pentesting and How to Close Them

AI-powered penetration testing can uncover complex attack paths, but safety restrictions and network limitations leave many assets and vulnerabilities untested. Picus Security expl...

Read source
infosecurity-magazine.com /1 month ago

Human Attacker Hits Machine-Speed Exploitation of Marimo RCE

A human attacker exploited a Marimo RCE and reached an SSH bastion in eight seconds

Read source
medium.com /1 month ago

THREAT DETECTION AND ANALYSIS: THE CYBERSECURITY BATTLE AFTER THE ATTACK BEGINS.

The most dangerous cyber attack is not necessarily the one that gets through your defenses. It is the one that gets through and remains…Continue reading on Medium »

Read source
thehackernews.com /1 month ago

Threat Intelligence Alone Won't Close the Exploitation Gap

A leaked credential shows up in a criminal marketplace, or a vulnerability gets a disclosure advisory, and either one can be weaponized against a real target before most security t...

Read source
thehackernews.com /3 weeks ago

Attackers Exploit NetScaler Flaw for Root Access, Deploy WHIPSHOT and SLAPSHOT

Unknown threat actors have been observed exploiting a newly patched security flaw in Citrix NetScaler ADC and NetScaler Gateway appliances to target organizations in North America...

Read source
gbhackers.com /1 month ago

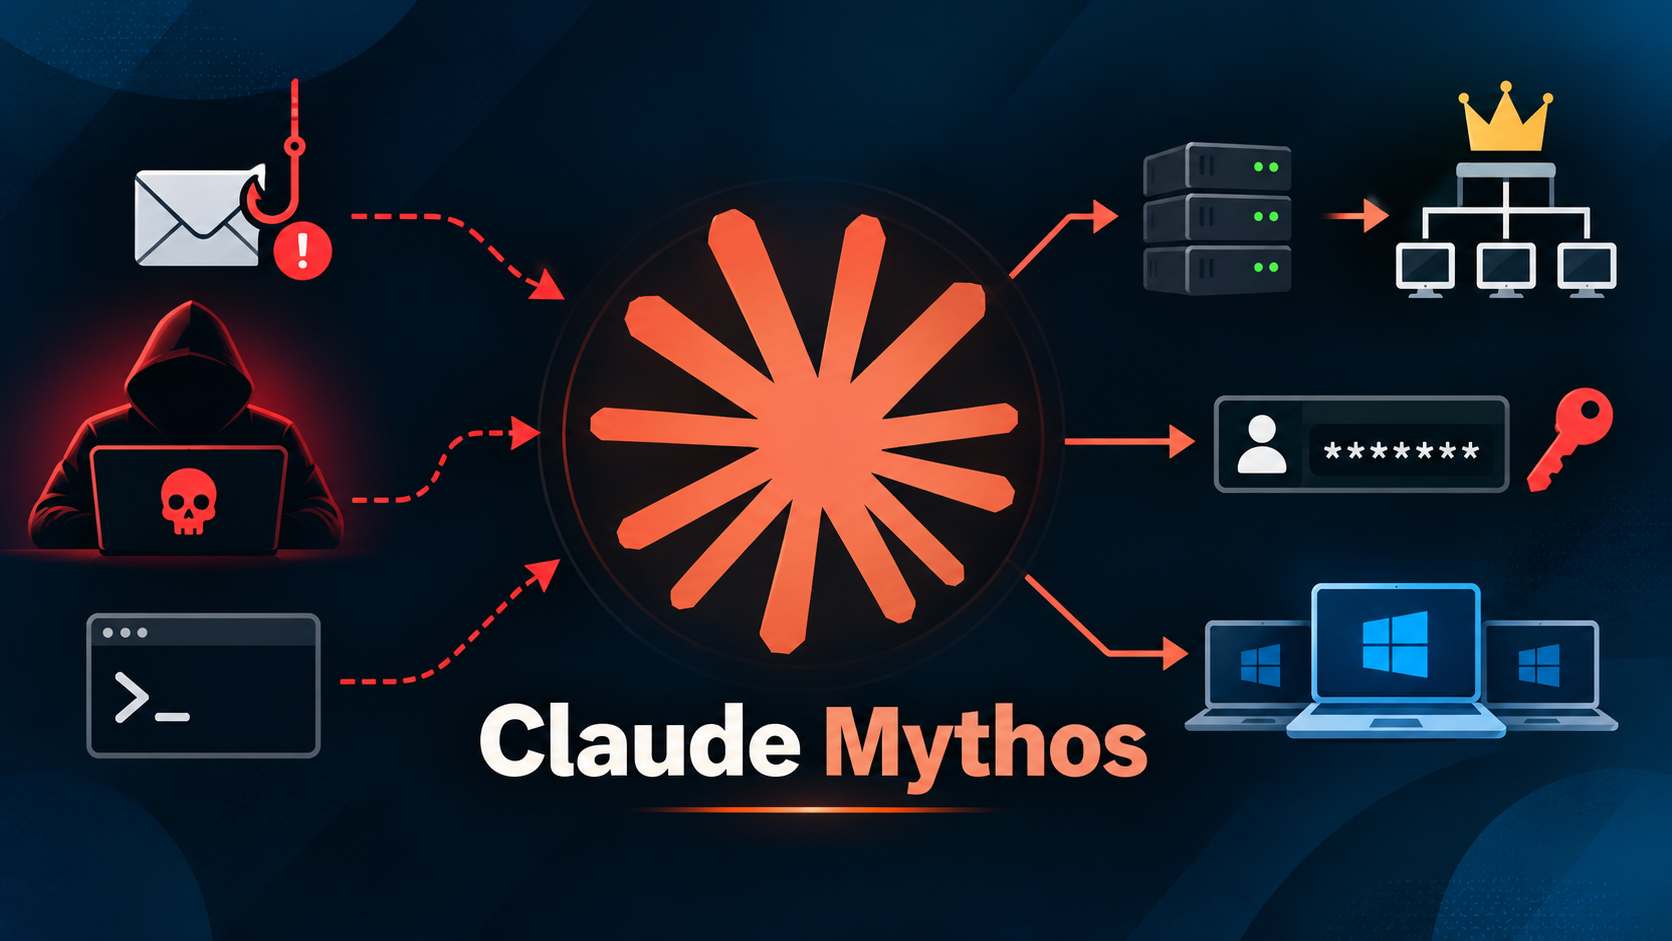
Claude Mythos Executes End-to-End Intrusion From Initial Access to Full Domain Compromise

Anthropic’s Claude Mythos Preview has demonstrated the ability to complete an end-to-end enterprise intrusion simulation, progressing from initial access through chained exploitati...

Read source
bleepingcomputer.com /2 days ago

Machine speed attacks require machine speed detection and response

Attackers can steal credentials and begin exfiltrating data within minutes, often before security teams can respond. Exaforce examines real-world attacks involving stolen GitHub to...

Read source
supplychaingamechanger.com /3 weeks ago

Inside the Mind of a Cyber Attacker!

In the perpetual game of cat and mouse between cyber attackers and defenders, the battleground is vast and dynamic. Understanding the Tactics, Techniques, and Procedures (TTPs) emp...

Read source
thehackernews.com /1 month ago

Human Attacker Exploits Marimo RCE, Reaches SSH Bastion in Eight Seconds

With artificial intelligence (AI) shrinking the window between vulnerability discovery and exploitation and lowering the barrier to entry for bad actors, new findings from Sysdig s...

Read source
blog.knowbe4.com /2 weeks ago

Threat Actors Abuse Trusted Accounts and Internal Tools to Launch Convincing BEC Attacks

Attackers are continually finding new ways to refine business email compromise (BEC) attacks, according to Douglas McKee, Director of Vulnerability Intelligence at Rapid7. When at...

Read source
cybersecuritytribe.com /1 month ago

Why Vulnerability Backlogs Are More Dangerous in the AI Era

For the first time in 19 years, the Verizon Data Breach Report, which samples over 22,000 breaches across 145 countries, has a new number one initial access vector: vulnerability e...

Read source
cofense.com /1 month ago

Understanding Browser Trust Abuse: Exploiting Enterprise’s Most Trusted Interface

By: Marie Mamaril, Intelligence TeamThe biggest change in browser-related threats is not a new flaw in browser software. It is a shift in how threat actors operate. Instead of brea...

Read source
legaltechdaily.com /3 weeks ago

Hijacking the Castle: The Rise of Autonomous Adversarial Cyber Warfare

Cambridge, MA – MIT Media Lab – EmTech Future. In modern corporate cybersecurity, an uncomfortable truth has emerged: the bad guys adopted generative artificial intelligence faster...

Read source
cloud.google.com /3 weeks ago

Defending Against Active Exploitation of Citrix NetScaler ADC and Gateway Appliances

Introduction In late September 2026, Mandiant Consulting and Google Threat Intelligence Group (GTIG) identified active, in-the-wild exploitation of a zero-day vulnerability (CVE-20...

Read source
thehackernews.com /1 month ago

CISO's Expert Guide to Agentic Pentesting for Websites

Attackers now weaponize new vulnerabilities in about five days (Mandiant, part of Google Cloud). The median organization takes 43 days to patch one (Verizon DBIR 2026). A new free...

Read source
natlawreview.com /1 month ago

The Breach Is Over- The Defense Costs Are Just Beginning

Read source
natlawreview.com /1 week ago

Don't Wait for a Breach

Read source
legaltechmonitor.com /3 weeks ago

Hijacking the Castle: The Rise of Autonomous Adversarial Cyber Warfare

Cambridge, MA – MIT Media Lab – EmTech Future. In modern corporate cybersecurity, an uncomfortable truth has emerged: the bad guys adopted generative artificial intelligence faster...

Read source
blogs.cisco.com /1 month ago

Your Agent Trusts Things You Never Approved

Several notable breach retrospectives of the last decade have the same shape. The attacker didn't break down the front door. They compromised something the target had already decid...

Read source
cybersecuritynews.com /2 weeks ago

CyberXero Combines Claude Code, PentAGI and Cobalt Strike in AI-Augmented Cyberattacks

CyberXero has emerged as an initial access broker that combines familiar hacking tools with artificial intelligence to run large-scale intrusions. The Russian-speaking operator tar...

Read source

Turn fresh research into a full content calendar

Use SocialBu to discover ideas, generate post drafts, and schedule them across your social channels.

Sources covering Breach And Attack

blog.knowbe4.com

Recent coverage from public sources
Public source

blogs.cisco.com

Recent coverage from public sources
Public source

cloudblog.withgoogle.com

Recent coverage from public sources
Public source

cofense.com

Recent coverage from public sources
Public source

cybersecuritynews.com

Recent coverage from public sources
Public source

feeds.feedburner.com

Recent coverage from public sources
Public source