Latest updates for Attack Surface Management

Fresh curated links around Attack Surface Management are collected here so marketers can spot useful updates and turn timely ideas into posts faster.

Recent items include:

  • 5 Best AI Attack Surface Management Platforms
  • Your Application Has an Unindexed Attack Surface. Do You Know What’s in It?
  • Criminal IP Introduces AITEM as the Next Evolution of Attack Surface Management

Post angles to try

Share the most useful takeaway for your audience.
Turn one article into a quick practical checklist.
Ask your audience how this shift affects their work.
Turn angles into scheduled posts

Fresh articles and ideas

Recent curated links from global sources. Generate one free draft from any story, then use SocialBu to schedule and refine your content calendar.

cm-alliance.com /1 month ago

5 Best AI Attack Surface Management Platforms

Security teams cannot manage an AI attack surface they cannot see. Models, inference APIs, agents, experimental applications, service identities, and supporting cloud resources may...
Read source
dzone.com /1 month ago

Your Application Has an Unindexed Attack Surface. Do You Know What’s in It?

Security teams usually describe an application through the assets they know about. This includes the production domain, documented APIs, the services currently in use, and the repo...

Read source
bleepingcomputer.com /1 week ago

Criminal IP Introduces AITEM as the Next Evolution of Attack Surface Management

Traditional attack surface management helps organizations discover exposed assets, but visibility alone is not enough to address threats. Criminal IP introduces AITEM, an AI-powere...

Read source
dev.to /1 month ago

Measuring the Edge: What ZoomEye Sees When You Search for Exposed Access Gateways

Measuring the Edge: What ZoomEye Sees When You Search for Exposed Access Gateways The SonicWall SMA1000 zero-day chain disclosed in September 2026 raised a question that vulnerab...

Read source
thehackernews.com /1 month ago

Attack Chains, Not Just Attack Surfaces: Why Testing Individual Techniques Misses the Point

Introduction Security teams have gotten pretty good at testing against what can hurt them. Can this EDR agent catch this payload? Will my organization fail the phishing simulation...

Read source
thehackernews.com /1 month ago

Frontier AI: Vulnerability Management's Systemic Revolution

Vulnerability management has been a staple of security programs since the dawn of the cybersecurity discipline. The symbiotic relationship between vulnerability and patch managemen...

Read source
medium.com /2 weeks ago

Five of 32 MCP Attack Vectors Are Covered by No Tool I Measured.

Picture an office building with one very good security guard at the front door. Every visitor and every parcel goes past the desk. The…Continue reading on Medium »

Read source
healthtechmagazine.net /1 week ago

Your Security Stack Is Working. Are Your Security Operations?

Walk into a modern enterprise security operations center today, and you'll discover just how inexpensive 65-inch monitors are: The walls are covered with them, showing dashboards f...

Read source
dzone.com /1 month ago

When Guest Access Becomes an Attack Surface: A Technical Analysis of the City-Forum Campaign

Learn how attackers enumerated Salesforce Experience Cloud and ServiceNow portals — and how defenders can detect and prevent the same abuse. When Guest Access Becomes an Attack Sur...

Read source
dzone.com /1 week ago

AI-Era Cybersecurity, Part 2: Building the System Context, Governance and Agent Identity

Part 1 of this series walked through why AI has compressed the gap between a vulnerability's disclosure and its exploitation from months to hours, laid out the lifecycle every vuln...

Read source
gbhackers.com /2 weeks ago

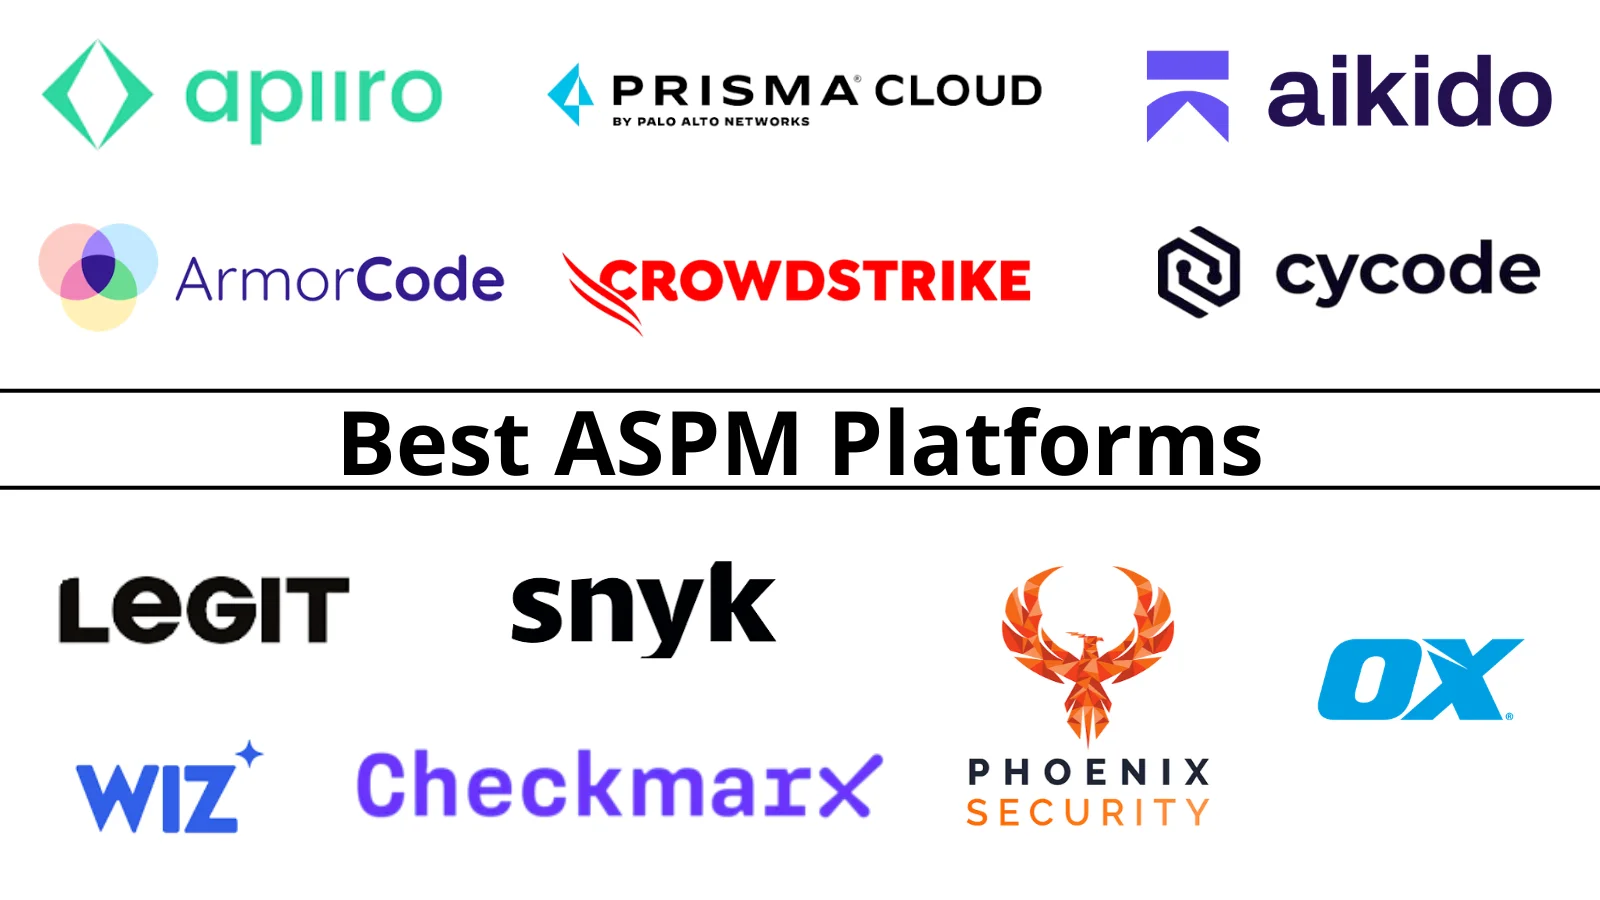
12 Best ASPM Platforms Compared (2026): Features & Pricing

Apiiro leads risk-graph depth, ArmorCode aggregation breadth, and the acquisition wave (Dazz into Wiz, Bionic into CrowdStrike, Enso into Snyk) tells you where ASPM is going: into...

Read source
salesforce.com /1 week ago

Managing Agentic Security at Scale

On the code we scan at depth, the volume of findings is now the constraint: frontier models plus an agentic harness surface more real, exploitable findings than engineering can abs...

Read source
ninjaone.com /1 month ago

Browser Extension Security: How to Manage Malicious and Abandoned Extensions

Your endpoints are managed. Your network is monitored. Your browser is not. This matters more than it used to. Applications, identity, SaaS access, and now AI tools all converge in...

Read source
ninjaone.com /3 weeks ago

How System Vulnerability Scanning Supports Patch Governance

The window between vulnerability disclosure and active exploitation continues to shrink. About one-third (28.3%) of exploited vulnerabilities are weaponized within 24 hours of disc...

Read source
forrester.com /3 weeks ago

Announcing The Forrester Waveâ„¢: Proactive Security Platforms, Q3 2026

Last week, we released The Forrester Waveâ„¢: Proactive Security Platforms, Q3 2026. This is the first evaluation of this market under this title, which has evolved from attack sur...

Read source
projectmanagertemplate.com /3 days ago

SaaS Security Posture Management (SSPM): How It Protects SaaS Environments

SaaS Security Posture Management (SSPM): How It Protects SaaS Environments SaaS Security Posture Management (SSPM) is the practice of continuously identifying, assessing, prioritiz...

Read source
smartermsp.com /1 week ago

Cybersecurity Threat Advisory: Critical SonicWall SMA1000 vulnerabilities

Barracuda Managed XDR’s Security Operations Center has observed increased scanning and profiling of internet-exposed SonicWall SMA 1000 Series appliances following the disclosure o...

Read source
dzone.com /1 week ago

AI-Era Cybersecurity, Part 1: Mapping Glasswing, Daybreak, Lightwell and the Tools Racing to Find and Fix Bugs

Every few weeks, a new name shows up in security news. Project Glasswing. Daybreak. Lightwell. CodeMender. Big Sleep. Each one is presented as the next answer to AI-driven cyberatt...

Read source
cloud.google.com /1 week ago

ARMORY CASTLE Exploits BeyondTrust

Written by: Jayson Frost, Bryce Greathouse, Brian Meyer, John Palmisano, Rajesh Rajeshirke, Steve Rasch, John Wolfram Introduction  On October 15, BeyondTrust disclosed a vulnerab...

Read source
smartermsp.com /1 month ago

Cybersecurity Threat Advisory: AI-Powered Server Attacks

Cybersecurity researchers have identified a threat actor that leverages artificial intelligence throughout the attack lifecycle to conduct search engine optimization (SEO) fraud, s...

Read source
bleepingcomputer.com /1 month ago

Reducing shadow IT visibility gaps with Wazuh

Shadow IT can leave security teams unaware of unmanaged endpoints, unauthorized software, and other assets that fall outside existing monitoring. Wazuh explains how endpoint invent...

Read source
blog.knowbe4.com /4 weeks ago

Are Your AI Assistants the Next Attack Surface?

Lead Analysts: Shikhar Dalela, Maddhav Grandy and Jeewan Singh Jalal

Read source
ninjaone.com /1 month ago

How to Build a Sustainable Windows Security Posture

Windows systems are the backbone of most IT environments, running critical applications and enabling distributed workforces worldwide. Yet many organizations still rely on reactive...

Read source
smartermsp.com /1 month ago

Cybersecurity Threat Advisory: SonicWall zero‑day RCE campaign

Threat actors are actively targeting SonicWall SMA1000 appliances by exploiting two zero-day vulnerabilities affecting models 6210, 7210, and 8200v. Review this Cybersecurity Threa...

Read source

Turn fresh research into a full content calendar

Use SocialBu to discover ideas, generate post drafts, and schedule them across your social channels.

Sources covering Attack Surface Management

feeds.dzone.com

Recent coverage from public sources
Public source

smartermsp.com

Recent coverage from public sources
Public source

blog.knowbe4.com

Recent coverage from public sources
Public source

cloudblog.withgoogle.com

Recent coverage from public sources
Public source

dev.to

Recent coverage from public sources
Public source

feeds.feedburner.com

Recent coverage from public sources
Public source