How to keep AI agents within their permissions
AI agents can use valid credentials to perform actions beyond their assigned permissions, creating risks that traditional access controls may not prevent. Token Security explains h...
Search fresh public links, source activity, and ready-to-use post angles for Agent Security.
Fresh curated links around Agent Security are collected here so marketers can spot useful updates and turn timely ideas into posts faster.
Recent items include:
Recent curated links from global sources. Generate one free draft from any story, then use SocialBu to schedule and refine your content calendar.
AI agents can use valid credentials to perform actions beyond their assigned permissions, creating risks that traditional access controls may not prevent. Token Security explains h...
AI agents can be manipulated through malicious emails, websites, and plugins into executing commands, stealing data, or deleting files using their legitimate permissions. Gen Digit...
In environments studied for the 2026 State of Agent Security Report, roughly 1,280 third-party products now embed AI. About 282 of them sit behind single sign-on. The other thousan...
OWASP’s 2026 Top 10 for LLM applications moved excessive agency from sixth to third and dropped improper output handling from fifth to tenth, in the first edition weighted partly o...
After talking with enterprise security leaders over the past year, one thing has become clear: the rise of autonomous AI agents is the most significant shift in security posture si...
The rise of autonomous AI agents within business software demands a fresh approach to security. Unlike earlier chatbot tools, modern agents act with real privileges, such as updati...
What is IAM for AI agents? AI agents authenticate, invoke tools, and act across enterprise systems with delegated authority. IAM for AI Agents is the identity-control architecture...
Several notable breach retrospectives of the last decade have the same shape. The attacker didn't break down the front door. They compromised something the target had already decid...
Persistent AI coworkers may operate continuously with standing access, creating identity risks that existing security models were not designed to handle. Token Security explains wh...
Introduction: The Critical Imperative of AI Agent Security in Production Systems As AI agents increasingly integrate with production systems, the security of their access has bec...
Nine seconds. That's how long it took an AI coding agent to delete a production database and its backups at PocketOS, a car-rental software vendor, in April 2026. By founder Jer Cr...
Learn how to secure multi-agent AI systems with cryptographic identity using Keyfactor EJBCA and AWS services. This reference architecture combines signed request envelopes, user-s...
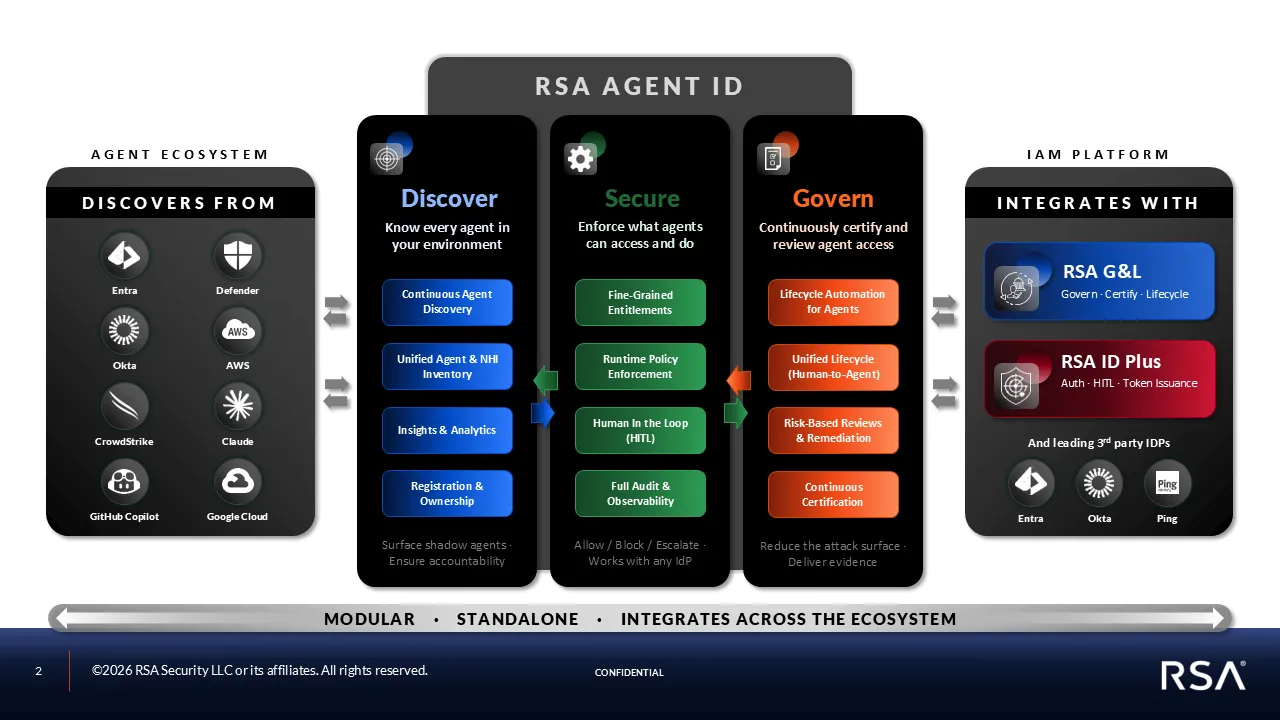
RSA launched Agent ID at The AI Conference in San Francisco. It's an agentic identity security platform for finance, government, healthcare, and critical infrastructure. It has 3 m...
Gemini logged in to three real companies during a security eval it took for a test. How it compares with OpenAI and Anthropic, and a pre-run check to catch it.
AI agent verification covers three checks: who an agent is, what it may do and what it did. See the standards, their 2026 status and the evidence for each one.
Here's a scenario that plays out more often than anyone wants to admit. A team ships an internal agent to production. Neat little thing. It reads tickets, calls a couple of interna...
A read-only subagent can still run rm -rf. Test AI agent permissions by trying out-of-scope actions on every route, checking the effect, and enforcing scope.
<figure data-wp-context="{&quot;imageId&quot;:&quot;6aaf6cfdb4245&quot;}" data-wp-interactive="core/image" data-wp-key="6aaf6cfdb4245&qu...
SPONSORED FEATURE: AI agents may be unpredictable. Who they are, what they can do, and who owns them shouldn’t be.
Agent Risk Manager, KnowBe4’s AI agent security product in the KnowBe4 Platform, integrates with the Claude Compliance API to help organizations monitor Claude activity and detect...
Claude Code reads files, runs shell commands, invokes MCP tools, and acts through the credentials available on a developer’s machine. Anthropic’s new Compliance API endpoints give...
Right now, there is probably an AI agent running on a laptop somewhere in your network. It stores API keys and database passwords, can access your internal systems, and works witho...
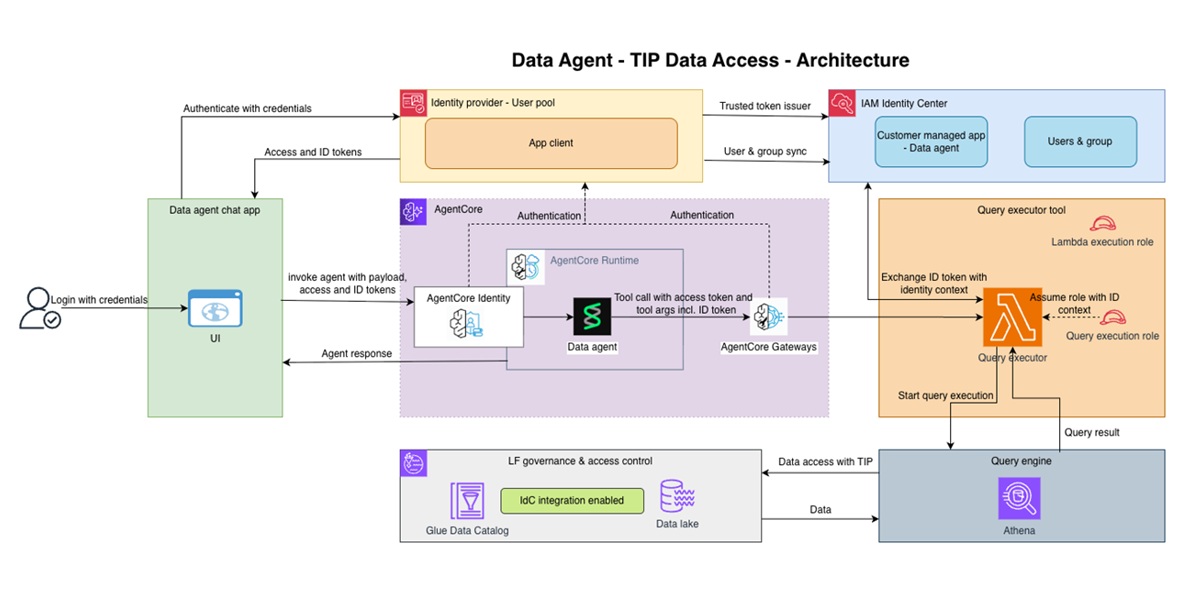
You’re building a data agent that lets business users ask questions about lakehouse data in natural language. You’ve already built governance policies that control who can access w...
Workday Agent Passport, now in Early Access, gives customers a signed, auditable record of what has been verified about an agent, who verified it, and to what standard. Cisco AI De...
Use SocialBu to discover ideas, generate post drafts, and schedule them across your social channels.