Latest updates for Api Security B...

Fresh curated links around API security b... are collected here so marketers can spot useful updates and turn timely ideas into posts faster.

Recent items include:

  • Static API Key vs. OAuth vs. JWT vs. Participant-Held Authority for AI Agents: Which Should I Use?
  • Comprehensive Guide to API Threat Protection with WAF and WAAP
  • Как строить сканирование активов в MaxPatrol VM. Ч.4 — Автоматизация по API. Ч.0 — авторизация

Post angles to try

Share the most useful takeaway for your audience.
Turn one article into a quick practical checklist.
Ask your audience how this shift affects their work.
Turn angles into scheduled posts

Fresh articles and ideas

Recent curated links from global sources. Generate one free draft from any story, then use SocialBu to schedule and refine your content calendar.

medium.com /1 month ago

Static API Key vs. OAuth vs. JWT vs. Participant-Held Authority for AI Agents: Which Should I Use?

If you’re building an AI agent, there isn’t one authorization method that is right for every situation.Continue reading on Medium »

Read source
sourcetrail.com /1 month ago

Comprehensive Guide to API Threat Protection with WAF and WAAP

Stop API breaches! Learn how to integrate WAF and WAAP to block SQLi, XSS, and bots. Protect your data and ensure PCI DSS compliance today. The post Comprehensive Guide to API Thre...

Read source
habr.com /6 days ago

Как строить сканирование активов в MaxPatrol VM. Ч.4 — Автоматизация по API. Ч.0 — авторизация

Добрый день, дорогие читатели!Мы с Вами просканировали основные типы активов. Можно выпустить гайды по сканированию сетевого оборудования и виртуализации, но здесь мне нечего добав...

Read source
thehackernews.com /1 month ago

Active Exploitation Attempts Target WSO2 API Manager JWT Bypass With Forged Admin Tokens

A critical security flaw in WSO2 API Manager has come under active exploitation in the wild, according to findings from watchTowr. The vulnerability, tracked as CVE-2026-5430 (CVS...

Read source
cryptopotato.com /2 weeks ago

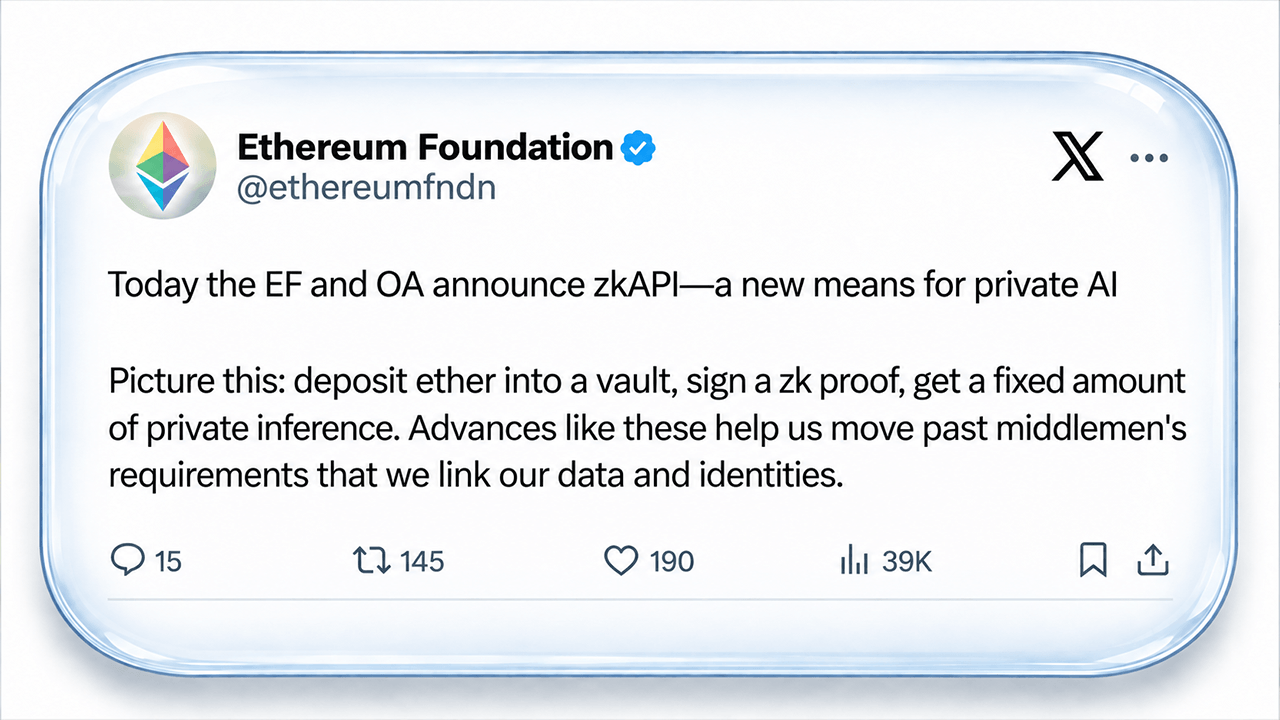
Ethereum Foundation and OA Launch zkAPI for Private AI Payment

zkAPI keeps prompts awayy from payment servers, but AI providers can read submitted content and may connect sessions through repeated details.

Read source
ninjaone.com /6 days ago

How to Build an API Security Governance Program

API security remains a critical blind spot today, as nearly all organizations have faced an API-related incident, yet only 21% have robust attack detection capabilities. Establishi...

Read source
habr.com /3 weeks ago

YApi заброшен с 2022 года. Я продолжил его и нашёл токены, которые может подделать любой участник проекта

YApi — платформа документации API, мок-сервера и тестов с 27 тысячами звёзд — не обновлялась с 2022 года. На новом Node.js у неё ломаются токены, клиент не собирается, нужное ей ра...

Read source
bleepingcomputer.com /3 days ago

OpenCode hack exposes API keys amid AI distillation attacks

The open-source AI coding project OpenCode has notified a small number of users that API keys they used with external providers were exposed in a security breach. [...]

Read source
medium.com /2 weeks ago

Private API Payments Show What Web3 Privacy Should Become

Why zero knowledge credits, boundary controls and selective evidence matter more than blanket secrecyContinue reading on Medium »

Read source
weworkremotely.com /1 week ago

Toptal: Apigee Engineer for Global Consumer Food Company

Headquarters: General Information:Our client is a global leader in the food and beverage industry and is recognized as one of the top brands in the world.……………………………………………………………...

Read source
news.bitcoin.com /2 weeks ago

Ethereum’s zkAPI Gives AI Payments a Privacy Cloak With a Catch

The Ethereum Foundation and Open Anonymity Project have launched zkAPI, a system that lets people prepay for AI and other metered services without attaching their billing identity...

Read source
habr.com /2 weeks ago

Как опубликовать внутренний API из DMZ, если соединения в LAN запрещены: пять подходов, которые мы проверили

Как опубликовать внутренний API из DMZ, если соединения в LAN запрещены: пять подходов, которые мы проверилиВсе пять схем мы собирали на NEOMSA APIM, российской платформе управлени...

Read source
dzone.com /1 month ago

How to Secure Fintech REST APIs Against BOLA Vulnerabilities

Broken Object Level Authorization (BOLA) occurs when a REST API exposes an object identifier—such as an account, transaction, or loan ID — without verifying whether the authenticat...

Read source

Turn fresh research into a full content calendar

Use SocialBu to discover ideas, generate post drafts, and schedule them across your social channels.

Sources covering Api Security B...

feeds.dzone.com

Recent coverage from public sources
Public source

cryptopotato.com

Recent coverage from public sources
Public source

feeds.feedburner.com

Recent coverage from public sources
Public source

habr.com

Recent coverage from public sources
Public source

medium.com

Recent coverage from public sources
Public source

news.bitcoin.com

Recent coverage from public sources
Public source