Latest updates for Api Security

Fresh curated links around API Security are collected here so marketers can spot useful updates and turn timely ideas into posts faster.

Recent items include:

  • How to Build an API Security Governance Program
  • Static API Key vs. OAuth vs. JWT vs. Participant-Held Authority for AI Agents: Which Should I Use?
  • Comprehensive Guide to API Threat Protection with WAF and WAAP

Post angles to try

Share the most useful takeaway for your audience.
Turn one article into a quick practical checklist.
Ask your audience how this shift affects their work.
Turn angles into scheduled posts

Fresh articles and ideas

Recent curated links from global sources. Generate one free draft from any story, then use SocialBu to schedule and refine your content calendar.

ninjaone.com /1 week ago

How to Build an API Security Governance Program

API security remains a critical blind spot today, as nearly all organizations have faced an API-related incident, yet only 21% have robust attack detection capabilities. Establishi...

Read source
medium.com /1 month ago

Static API Key vs. OAuth vs. JWT vs. Participant-Held Authority for AI Agents: Which Should I Use?

If you’re building an AI agent, there isn’t one authorization method that is right for every situation.Continue reading on Medium »

Read source
sourcetrail.com /1 month ago

Comprehensive Guide to API Threat Protection with WAF and WAAP

Stop API breaches! Learn how to integrate WAF and WAAP to block SQLi, XSS, and bots. Protect your data and ensure PCI DSS compliance today. The post Comprehensive Guide to API Thre...

Read source
thehackernews.com /1 day ago

Critical x402 SDK Flaw Could Let Malicious APIs Drain AI Agents’ Token Balances

AI agents paying for API calls with the x402 SDKs could sign a payment for their full balance of a supported token if a malicious API asked for it, security firm V12 said on Octobe...

Read source
dev.to /1 month ago

Protect Kubernetes Services with OAuth2 Proxy, Gateway API, Traefik, and Pocket ID

My previous guide used ingress-nginx annotations to put internal Kubernetes services behind OAuth2 Proxy. It was written for an ingress-nginx setup. That controller is being retire...

Read source
habr.com /4 weeks ago

YApi заброшен с 2022 года. Я продолжил его и нашёл токены, которые может подделать любой участник проекта

YApi — платформа документации API, мок-сервера и тестов с 27 тысячами звёзд — не обновлялась с 2022 года. На новом Node.js у неё ломаются токены, клиент не собирается, нужное ей ра...

Read source
thehackernews.com /1 month ago

Active Exploitation Attempts Target WSO2 API Manager JWT Bypass With Forged Admin Tokens

A critical security flaw in WSO2 API Manager has come under active exploitation in the wild, according to findings from watchTowr. The vulnerability, tracked as CVE-2026-5430 (CVS...

Read source
dev.to /1 month ago

I Attacked My Own AWS API Four Times, Then Fixed It, and Wrote Down Everything

A few months ago I got tired of hearing the same sentence in interviews and student forums: "we're on the cloud, so we're secure." I understand where it comes from. AWS handles the...

Read source
gbhackers.com /2 weeks ago

11 Best API Security Tools Compared (2026): Features & Pricing

Salt Security and Traceable anchor dedicated discovery-plus-runtime defense, 42Crunch owns design-time contract security, and the edge giants (Akamai with Noname inside, Cloudflare...

Read source
dev.to /1 week ago

WordPress REST API Deep Dive: Custom Routes, Multiple Methods on One Endpoint, and Full CRUD

🚪 Why the WP REST API Deserves Your Attention Every WordPress site already ships with a front door for data. Open yourdomain.com/wp-json/ and you'll see a big JSON map of everyt...

Read source
ministryoftesting.com /1 week ago

API-immunity?

Read source
cointelegraph.com /3 weeks ago

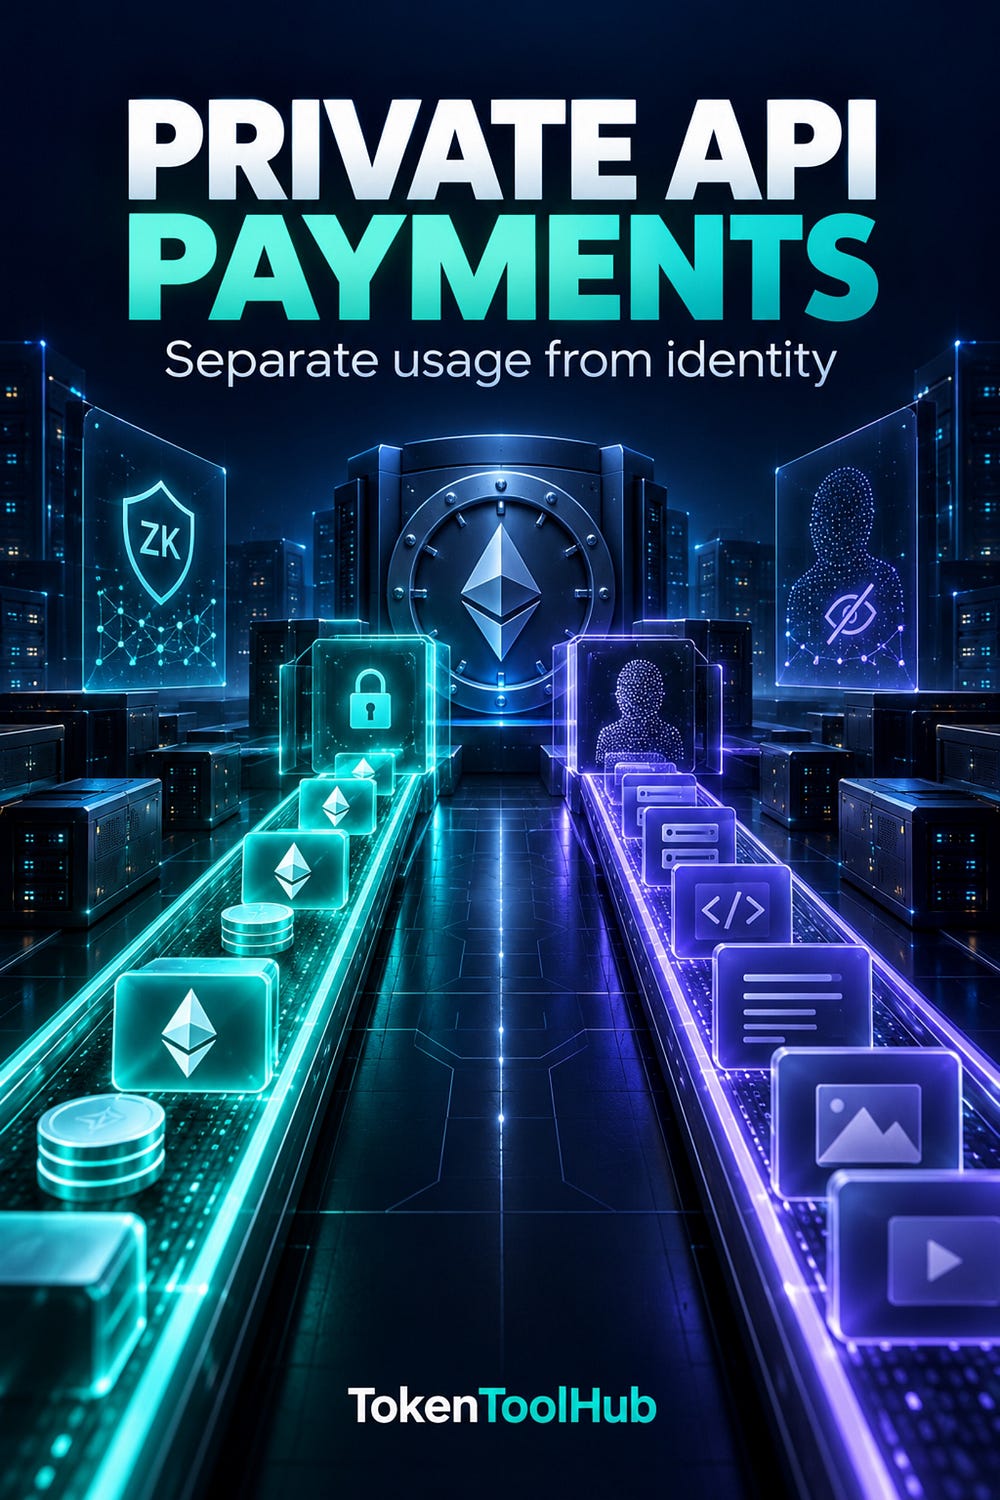
Ethereum’s zkAPI brings privacy-preserving API payments to mainnet

Ethereum’s zkAPI is now live on mainnet, turning an earlier zero-knowledge API payment proposal into a working implementation for private, prepaid access.

Read source
gbhackers.com /1 month ago

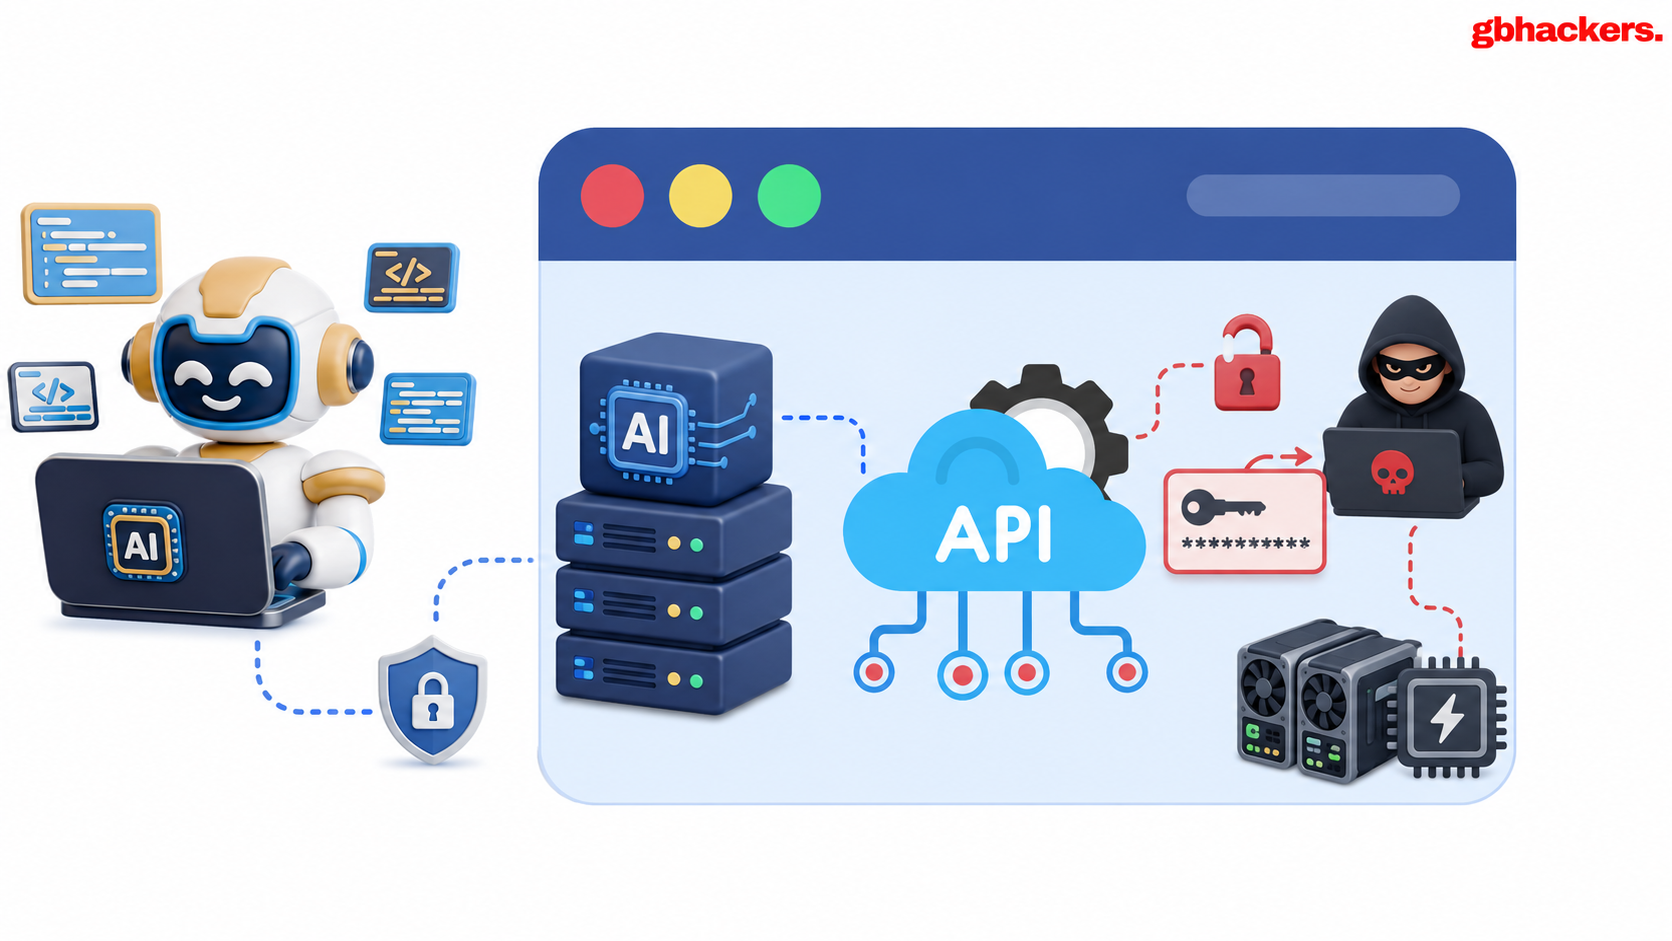
Hackers Are Targeting AI Servers to Steal API Keys and Hijack Computing Power

AI infrastructure is rapidly becoming a high-value enterprise attack surface. Attackers targeting LiteLLM AI gateways, RAGFlow retrieval platforms, and Kestra workflow orchestratio...

Read source
medium.com /3 weeks ago

Private API Payments Show What Web3 Privacy Should Become

Why zero knowledge credits, boundary controls and selective evidence matter more than blanket secrecyContinue reading on Medium »

Read source
habr.com /1 week ago

Как строить сканирование активов в MaxPatrol VM. Ч.4 — Автоматизация по API. Ч.0 — авторизация

Добрый день, дорогие читатели!Мы с Вами просканировали основные типы активов. Можно выпустить гайды по сканированию сетевого оборудования и виртуализации, но здесь мне нечего добав...

Read source
dev.to /3 weeks ago

The Data Was Public. The Agent Path Wasn't. So His Mock Became My Documentation.

Two commands against the same data. Run them yourself: $ curl -sS --get 'https://u58x3mt0.api.sanity.io/v2025-08-15/data/query/production' \ --data-urlencode 'query=count...

Read source
cryptoslate.com /1 month ago

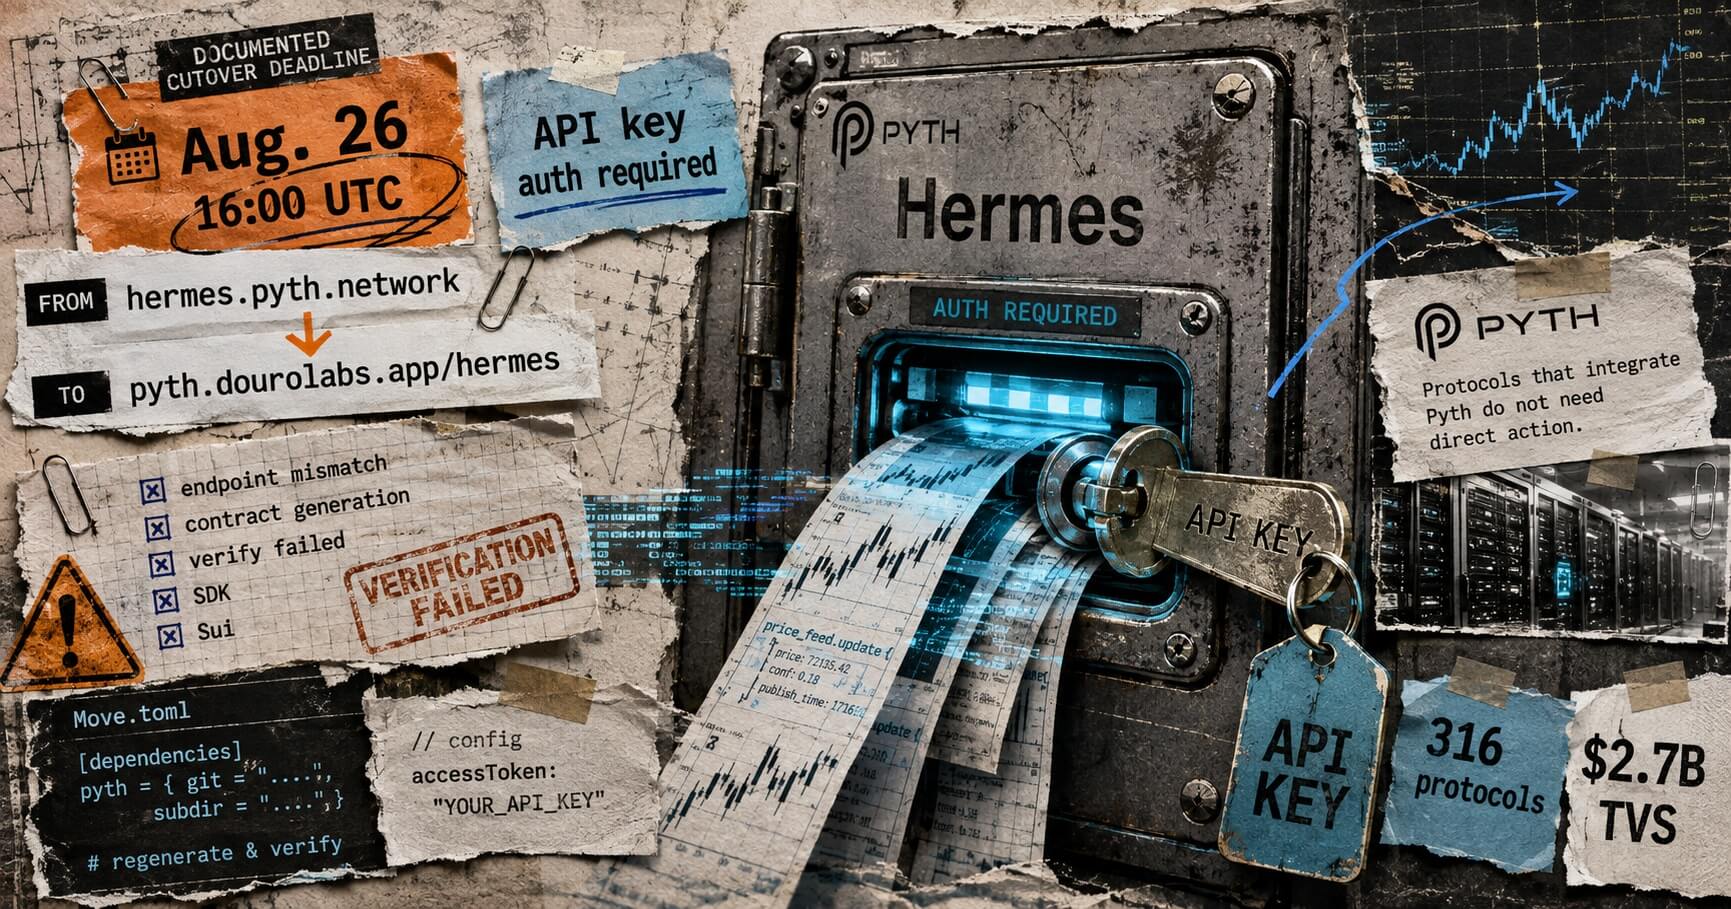
Pyth Network’s API overhaul threatens to freeze unpatched smart contracts across 300 DeFi protocols

Direct callers now need API keys, while Sui builders had to align their SDK, endpoint and on-chain package. The post Pyth Network’s API overhaul threatens to freeze unpatched smart...

Read source
cncf.io /1 month ago

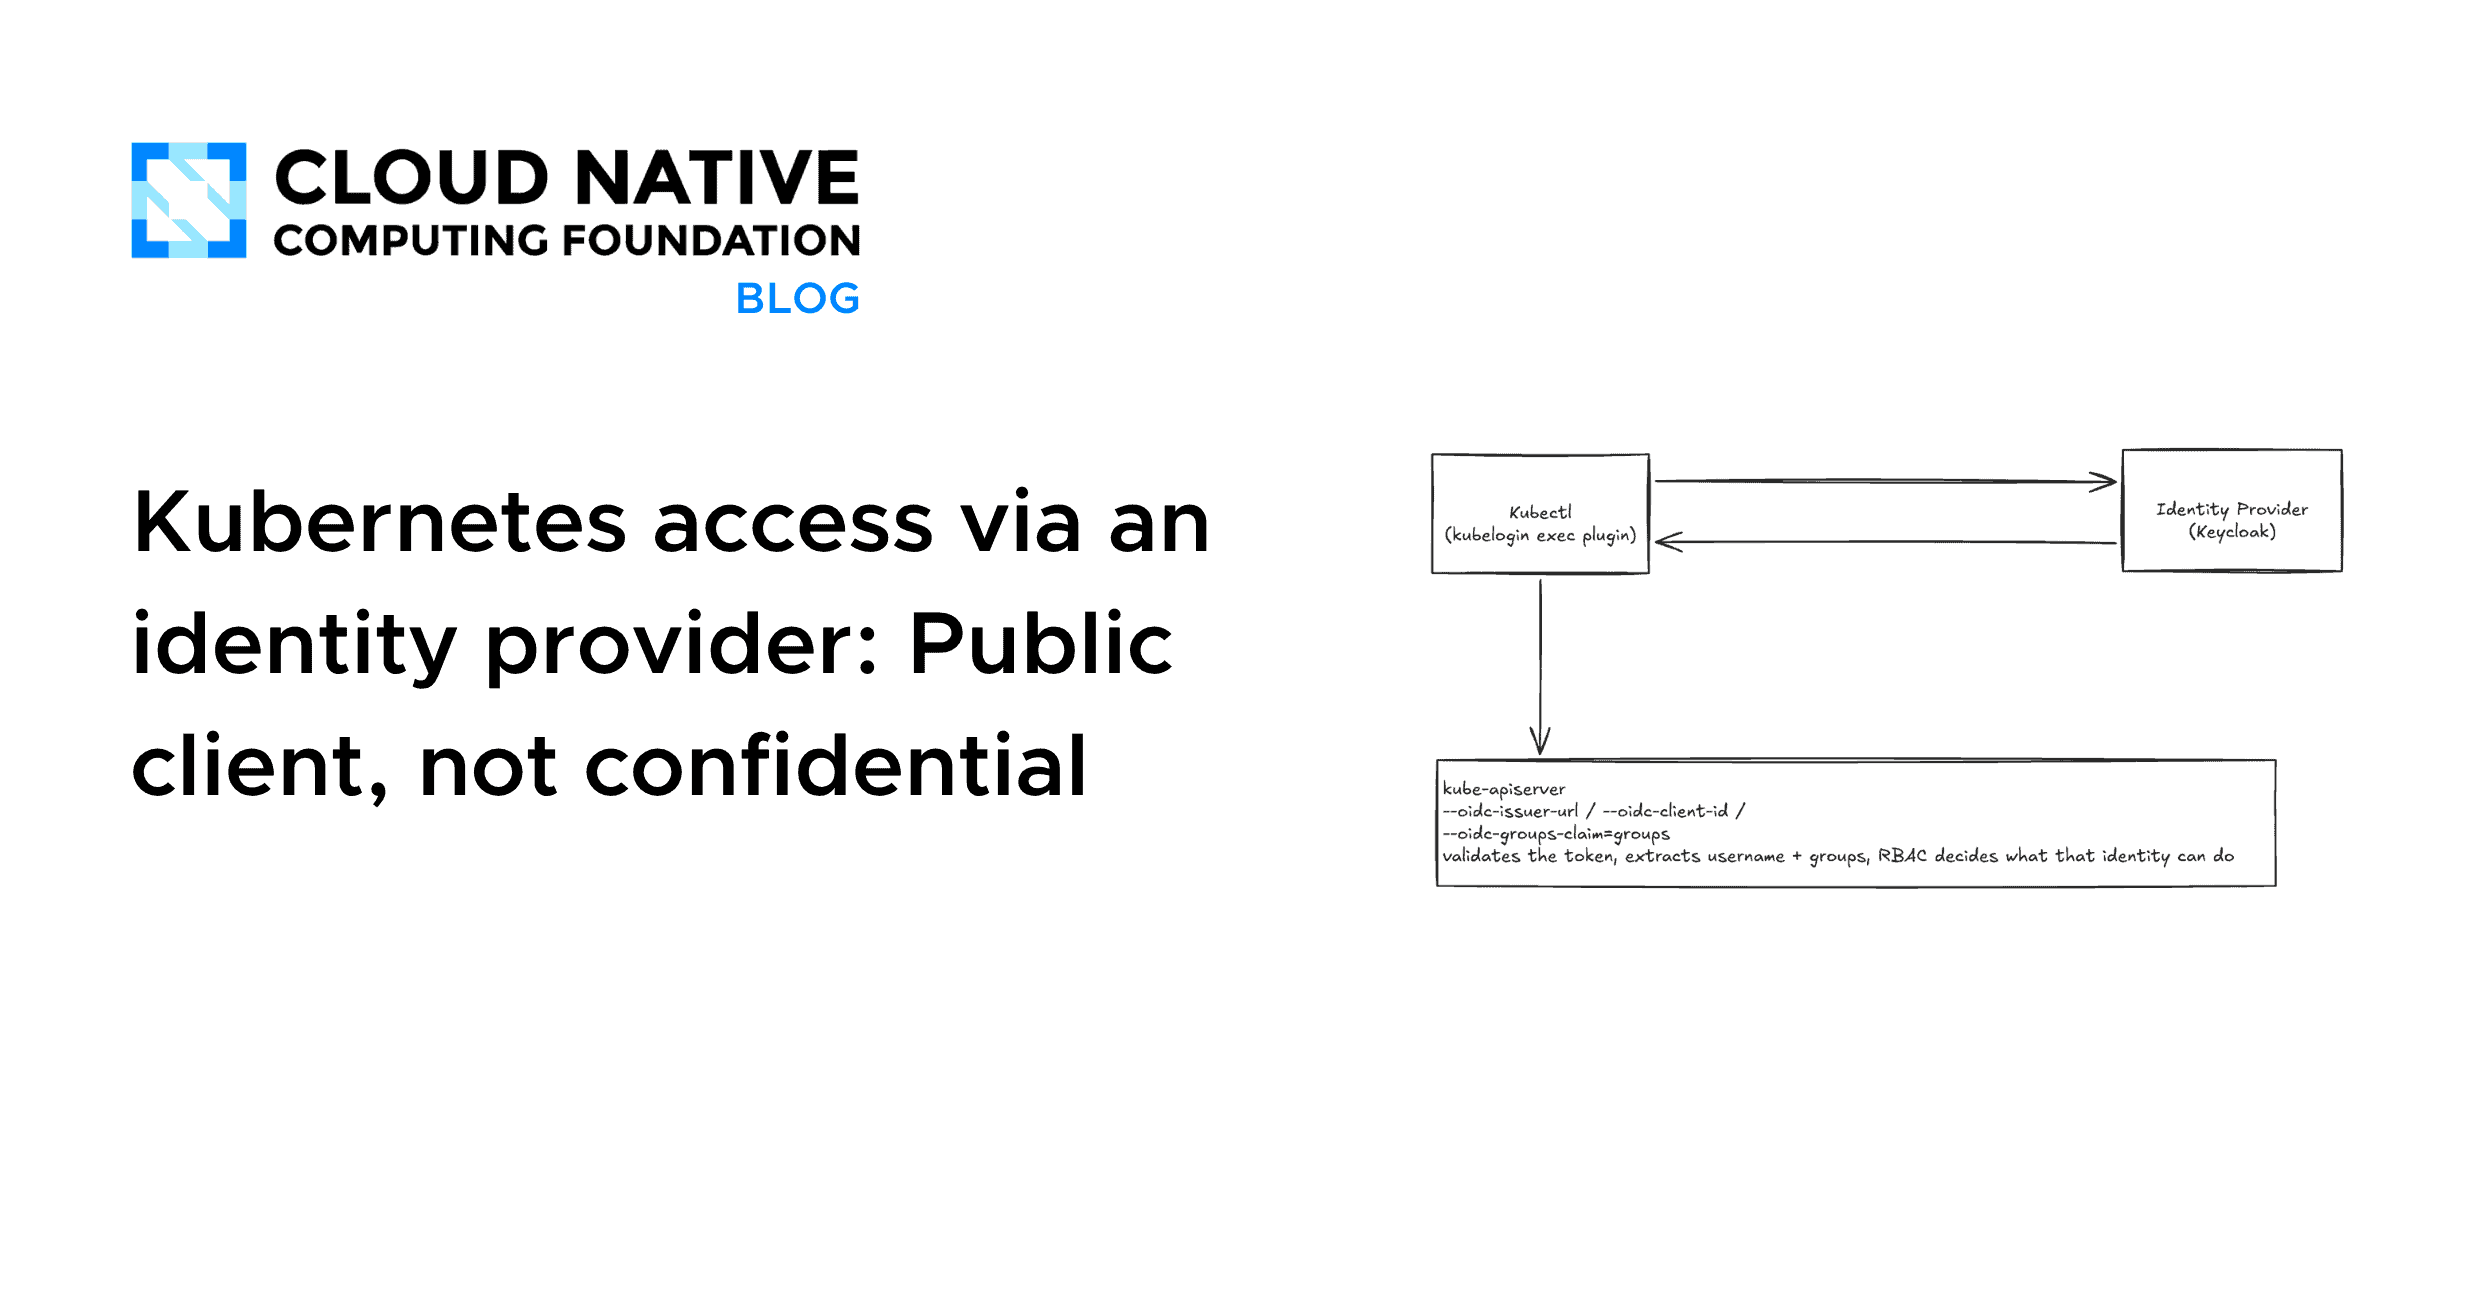
Kubernetes access via an identity provider: Public client, not confidential

Access control belongs on the same day-zero checklist as networking and storage. On most on-prem clusters, it never makes the list. The Identity Gap Managed cloud Kubernetes ships...

Read source
infoq.com /1 week ago

Article: Server-Side DPoP and Token Exchange in Spring Security 7

Spring Authorization Server now lives inside Spring Security 7 under the same Maven coordinates, so the upgrade is a version bump. This server-side guide covers enabling DPoP and R...

Read source
medium.com /1 month ago

SafetyNet Is Dead: Detecting Tampered Devices with Play Integrity API

The migration every banking app was forced to make, and why the client-side token is only half the jobContinue reading on Medium »

Read source
cryptopotato.com /3 weeks ago

Ethereum Foundation and OA Launch zkAPI for Private AI Payment

zkAPI keeps prompts awayy from payment servers, but AI providers can read submitted content and may connect sessions through repeated details.

Read source
habr.com /1 month ago

[Перевод] Жизненный цикл токена API: от выпуска до отзыва

Токены (tokens) API часто расцениваются как незначительные детали реализации.Пользователь входит в систему, сервер создает токен, браузер сохраняет его и включает в каждый защищенн...

Read source
dzone.com /1 month ago

Building a Secure MCP Server for File Processing: Auth, Rate Limiting, and Idempotency

Most write-ups on building an MCP server focus on the protocol itself: defining tools, handling requests, wiring up a client. That part is genuinely straightforward. What gets skip...

Read source
blog.codepen.io /1 week ago

444: A Gosh-Dang Full-Blown Read/Write API

Marie and Chris are on the podcast to talk about our very new v2 API. This baby (slaps the hood) can do it all. It’s complete read/write access to all your Pens, Collections, and A...

Read source

Turn fresh research into a full content calendar

Use SocialBu to discover ideas, generate post drafts, and schedule them across your social channels.

Sources covering Api Security

feeds.dzone.com

Recent coverage from public sources
Public source

blog.codepen.io

Recent coverage from public sources
Public source

cointelegraph.com

Recent coverage from public sources
Public source

cryptopotato.com

Recent coverage from public sources
Public source

cryptoslate.com

Recent coverage from public sources
Public source

dev.to

Recent coverage from public sources
Public source