Latest updates for Cyber Incident Response

Fresh curated links around cyber incident response are collected here so marketers can spot useful updates and turn timely ideas into posts faster.

Recent items include:

  • 5 Incident Response Habits Recommended for Distributed Teams
  • What Cyber Incident Response Teams Can Learn From Esports War Rooms
  • What Incident Response Documentation Does UK CAF Require?

Post angles to try

Share the most useful takeaway for your audience.
Turn one article into a quick practical checklist.
Ask your audience how this shift affects their work.
Turn angles into scheduled posts

Fresh articles and ideas

Recent curated links from global sources. Generate one free draft from any story, then use SocialBu to schedule and refine your content calendar.

cm-alliance.com /1 month ago

5 Incident Response Habits Recommended for Distributed Teams

Strong incident response rarely happens by accident. It is shaped by deliberate preparation, clearly assigned authority, and the organizational infrastructure that allows qualified...
Read source
cm-alliance.com /2 weeks ago

What Cyber Incident Response Teams Can Learn From Esports War Rooms

A coach on a Counter-Strike 2 broadcast has about three seconds to call a rotation before the round is lost. No time to convene a meeting. No time to check with legal. Just a heads...

Read source
cm-alliance.com /4 weeks ago

What Incident Response Documentation Does UK CAF Require?

The UK Cyber Assessment Framework (CAF) requires incident response documentation across two principles under Objective D: D1 (Response and Recovery Planning), which needs a documen...

Read source
infosecurity-magazine.com /1 month ago

NCSC Publishes Guidance to Aid Incident Response and Recovery

The National Cyber Security Centre has released a detailed framework to assist with incident response and recovery

Read source
homelandprepnews.com /2 weeks ago

CISA issues advisory helping organizations identify threats, enable effective response

A new advisory from the Cybersecurity and Infrastructure Security Agency outlines how organizations can strengthen detection, response and protections in information technology (IT...

Read source
cm-alliance.com /1 month ago

Does PCI DSS Require an Incident Response Plan?

PCI DSS Requirement 12.10 gets summarised everywhere as "have an incident response plan." That's true, but it undersells what an assessor actually checks — a single plan document d...

Read source
cm-alliance.com /1 month ago

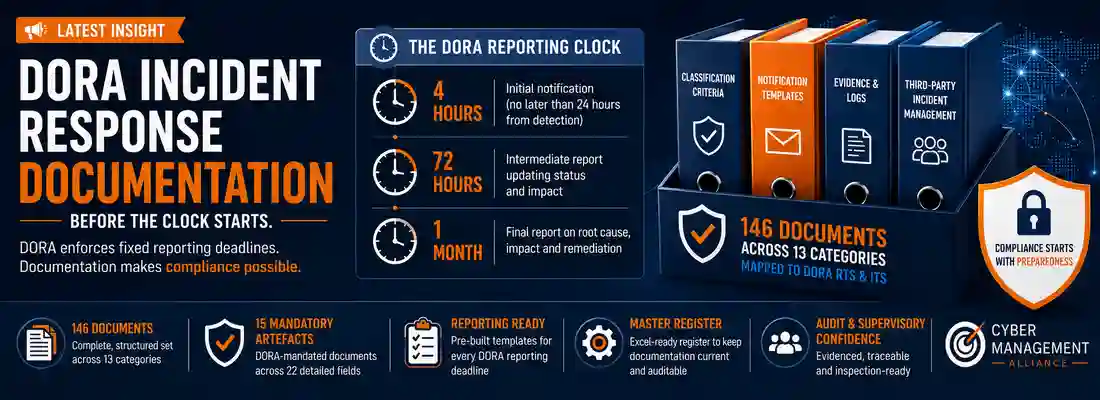
DORA Incident Response Documentation: Which Documents Do You Need?

 DORA compliance conversations tend to focus on ICT risk management frameworks and third-party oversight. What gets less attention is the thing supervisors actually check first dur...

Read source
cm-alliance.com /1 month ago

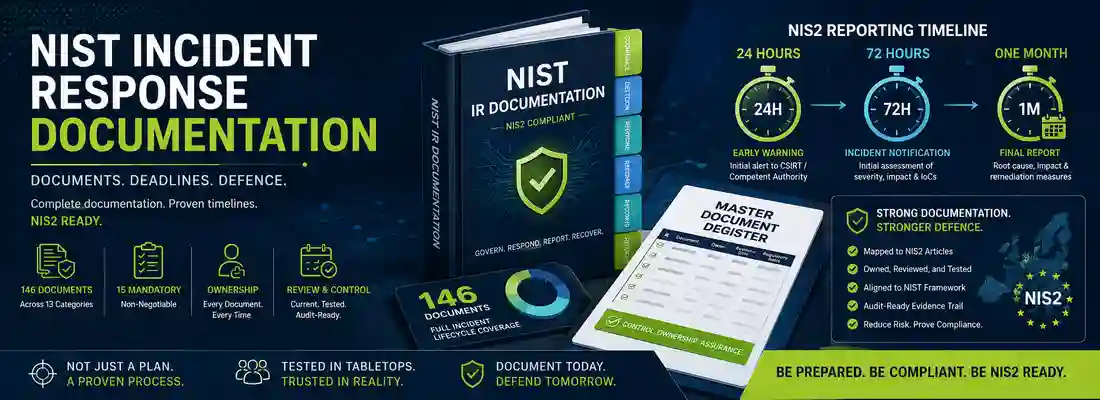
NIS2 Incident Response Documentation: How Many Documents Do You Need?

Most NIS2 conversations start with technical controls... detection tooling, network segmentation and access management. Fewer start with the question that actually determines wheth...

Read source
thehackernews.com /1 month ago

73% of Organizations Say They Are Not Fully Ready for a Major Cyberattack

Most organizations have incident response plans, security tools, and technical teams in place. Yet new research suggests that many still lack the coordination, visibility, and exec...

Read source
police1.com /3 weeks ago

When a cyberattack becomes a public safety incident

Command decisions chiefs and sheriffs should make before failures involving CAD, records, jail systems and other essential services put operations at risk

Read source
cm-alliance.com /4 days ago

US Cyber Incident Reporting: Managing Multiple Notification Clocks

A cyber incident does not wait for the legal team to finish a licensing matrix. The first hour is messy: security analysts are checking logs, the CTO wants to know whether systems...

Read source
cm-alliance.com /1 month ago

Visualising Workflows for Better Security and Incident Response

Walk into a Security Operations Centre and then into a cyber incident debrief, and you might think you had entered two entirely different worlds. The tooling is different, the pres...

Read source
cm-alliance.com /1 month ago

EU DORA 2026 Guide: Cyber Incident Response Requirements Explained

DORA is dominating headlines and if you’re in the financial services space in the EU, it’s probably also dominating all boardroom discussions. The Digital Operational Resilience Ac...

Read source
digitalthoughtdisruption.com /5 days ago

Enterprise AI Incident Response: A Runbook for Containing Compromised Agents

<figure data-wp-context="{"imageId":"6aa2f13c0eaa8"}" data-wp-interactive="core/image" data-wp-key="6aa2f13c0eaa8&qu...

Read source
infosecurity-magazine.com /1 week ago

France Establishes New Government-Focused Cyber Incident Response Unit

After a major cyber-attack targeted France's national tax authority, the Prime Minister called for the establishment of a new dedicated cyber incident response capability

Read source
ecpi.edu /1 month ago

SOC Analyst II

SOC Analyst II Anonymous (not verified) Mon, 07/27/2026 - 11:59 CYB471 471 CYB CYB471 SOC Analyst II (3) This course advances SOC anal...

Read source
cm-alliance.com /1 month ago

Cybersecurity Consultancy and Training for Stronger Risk Management

Most business security failures do not start with a dramatic breach. They start with a missed update, a rushed password reset, a vendor who was never properly briefed, or a team th...

Read source
executivegov.com /1 week ago

CISA, International Partners Issue Guidance on Outage Communications

CISA, FBI and international cyber agencies have issued guidance to help service providers communicate during IT and OT outages. The post CISA, International Partners Issue Guidance...

Read source
cm-alliance.com /1 month ago

The 5 Best Enterprise Security Companies in 2026

Enterprise cybersecurity companies are increasingly judged by more than the products they sell. For crisis management and incident response teams, the important question is whether...

Read source
aws.amazon.com /1 week ago

Incident response guide for AWS CloudTrail investigations – Part 2

In Part 1 of this guide, we examined two common incident scenarios: cross-account Amazon Simple Storage Service (Amazon S3) data deletion with ransomware implications, and cryptocu...

Read source
ecpi.edu /1 month ago

SOC Analyst I

SOC Analyst I Anonymous (not verified) Mon, 07/27/2026 - 11:59 CYB470 470 CYB CYB470 SOC Analyst I (3) This course introduces foundati...

Read source
cm-alliance.com /1 month ago

How Enterprise Exposure Management Reduces Cyber Risk

Cyber risk builds quietly when security teams see hazards late, treat every alert alike, and accept ticket closure as proof of safety. Enterprise systems shift daily through cloud...

Read source
cm-alliance.com /2 weeks ago

How Cyber Tabletop Exercises Align with the UK CAF Principles

TheNCSC Cyber Assessment Framework asks a demanding question that cannot be answered by policy documents alone: Can an organisation demonstrate that its essential functions are gen...

Read source
cm-alliance.com /1 month ago

What Counts as a Significant Incident Under NIS2?

NIS2 doesn't require essential and important entities to report every disruption, failed login or blocked phishing email to their CSIRT. It requires them to correctly identify whic...

Read source

Turn fresh research into a full content calendar

Use SocialBu to discover ideas, generate post drafts, and schedule them across your social channels.

Sources covering Cyber Incident Response

aws.amazon.com

Recent coverage from public sources
Public source

blogs.vmware.com

Recent coverage from public sources
Public source

executivegov.com

Recent coverage from public sources
Public source

feeds.feedburner.com

Recent coverage from public sources
Public source

homelandprepnews.com

Recent coverage from public sources
Public source

cm-alliance.com

Recent coverage from public sources
Public source