Latest updates for Access Management

Fresh curated links around Access Management are collected here so marketers can spot useful updates and turn timely ideas into posts faster.

Recent items include:

  • Implementing defense-in-depth authorization for MCP tools on Amazon Quick
  • Identity Providers and Access Controls in VCFA 9.1.1 for Native Object Storage
  • Managing identity source transition for AWS IAM Identity Center

Post angles to try

Share the most useful takeaway for your audience.
Turn one article into a quick practical checklist.
Ask your audience how this shift affects their work.
Turn angles into scheduled posts

Fresh articles and ideas

Recent curated links from global sources. Generate one free draft from any story, then use SocialBu to schedule and refine your content calendar.

aws.amazon.com /2 weeks ago

Implementing defense-in-depth authorization for MCP tools on Amazon Quick

Learn how to enforce defense-in-depth authorization for Model Context Protocol (MCP) tools on Amazon Quick. This walkthrough wires Microsoft Entra ID group and claims-based JWTs th...
Read source
cormachogan.com /2 weeks ago

Identity Providers and Access Controls in VCFA 9.1.1 for Native Object Storage

<p style="text-align: justify;"><a href="https://i0.wp.com/cormachogan.com/wp-content/uploads/2026/09/native-object-storage.webp?ssl=1"><img data...

Read source
aws.amazon.com /1 month ago

Managing identity source transition for AWS IAM Identity Center

September 2, 2026: This post was republished to include Active Directory migration strategies and automation for permission sets. AWS IAM Identity Center manages user access to Ama...

Read source
thedroptimes.com /3 weeks ago

The Drop Times: Permissions Define Drupal’s Agent Interfaces

Drupal's emerging agent interfaces are beginning to expose actions as well as information. MCPIO 1.0.0-alpha1 presents external Model Context Protocol clients with two entry points...

Read source
javacodegeeks.com /1 month ago

Role-Based Access Control in Node.js with JWT

Role-Based Access Control (RBAC) is a fundamental security pattern used to restrict system access based on user roles. When combined with JSON Web Tokens (JWT), it enables stateles...

Read source
dzone.com /2 weeks ago

Federated MCP Control Plane: Policy-Aware Access to Multi-Backend Tool Servers

A federated gateway provides secure, policy-aware access to tool servers. The thing that made me stop and rethink our whole approach to agentic tooling was a text file.

Read source
aws.amazon.com /1 month ago

Extend your data perimeter to the AWS Management Console with Private Access

Organizations in regulated industries such as financial services, government, defense, and healthcare restrict their sensitive workloads to isolated network environments with no ac...

Read source
aws.amazon.com /1 month ago

Securing your Amazon S3 buckets: Identifying and remediating over-permissioned access

Misconfigured Amazon Simple Storage Service (Amazon S3) buckets can expose your data to unauthorized access. Without proactive review, S3 bucket policies or Access Control Lists (A...

Read source
aws.amazon.com /3 weeks ago

Automate user-level custom permissions for Amazon Quick

Amazon Quick custom permissions let you enforce least-privilege access by toggling features per user. This post walks through four patterns to automate custom permissions across th...

Read source
habr.com /4 days ago

Ловушки классического IdM. Как их обойти и построить управление доступами в постоянно изменяющихся условиях

Всем привет! Меня зовут Артём, я продуктовый лидер с опытом управления линейкой высоконагруженных продуктов информационной безопасности и клиентского сервиса — IDM, PAM, PKI, SSO,...

Read source
aws.amazon.com /1 month ago

Govern AI agent tool access with Amazon Bedrock AgentCore Gateway

Give your AI agents governed, auditable access to enterprise tools without consolidating infrastructure. This post walks through a four-scope maturity model (Connect, Control, Cata...

Read source
dev.to /3 weeks ago

Designing a User Management system with JWTs, Ktor, and Exposed

Every app eventually needs to answer two questions: "who is this person?" and "what are they allowed to do?" Many tutorials either focus on integrating a specific authentication pr...

Read source
javacodegeeks.com /6 days ago

Dynamic Link Generation Based on OAuth2 User Permissions

Most REST APIs treat pagination and navigation as a solved problem, and then quietly ignore a much messier one: what happens when two different users hit the same endpoint and get...

Read source
salesforce.com /3 weeks ago

Start with Accounts: Design Identity and Access That Scales

Learn how to combine native Experience Cloud capabilities around the Account object to route authentication, align data access, and scale onboarding through configuration.

Read source
aws.amazon.com /1 month ago

Securing Amazon Quick from POC to production: Agents, Flows, and Spaces

Amazon Quick proof-of-concept projects often stall when security teams review the production plan. This post walks through designing dashboards, Spaces, knowledge bases, agents, an...

Read source
dev.to /4 weeks ago

I Wrote a Security Policy, Then Made Myself Break It

A guardrail you haven't tried to violate is just documentation with better formatting. That's the premise behind aws-boundary: an AWS multi-account setup using AWS Organizations,...

Read source
aws.amazon.com /2 weeks ago

Operationalizing least privilege: Automate IAM remediation through your CI/CD pipeline

The principle of least privilege is straightforward to articulate but challenging to maintain at scale. When teams first deploy applications to AWS, they often grant broader permis...

Read source
ninjaone.com /1 month ago

How to Distinguish Between Conditional Access and Extended Access Strategies

Many organizations deploy multiple access control mechanisms, but their roles are not always clearly defined in practice. Recent findings from Microsoft Security highlight this shi...

Read source
aws.amazon.com /1 month ago

IAM authentication with OAuth 2.0 for Amazon MQ for RabbitMQ

IAM authentication with OAuth 2.0 lets clients connect to Amazon MQ for RabbitMQ using their existing IAM identity instead of static broker-local credentials. This post covers the...

Read source
aws.amazon.com /1 month ago

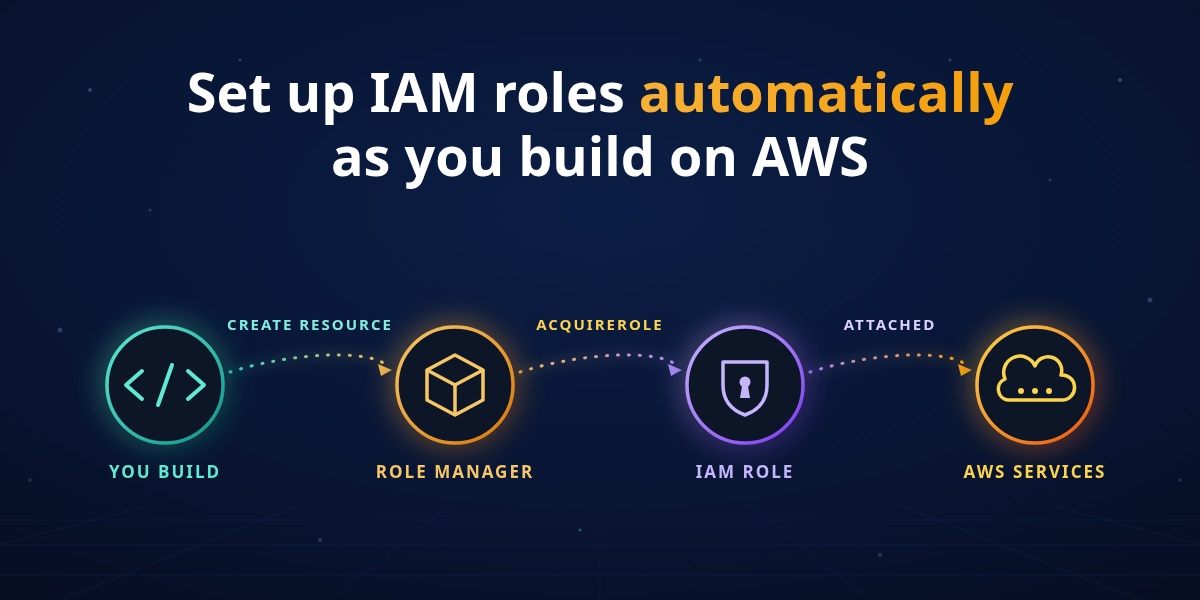
How AWS IAM role manager rethinks the starting point for IAM roles

When you build a new application or capability on Amazon Web Services (AWS), you want to focus on what you’re building. Getting a service running almost always begins with AWS Iden...

Read source
dzone.com /1 month ago

Securing AI Retrieval Pipelines and Adding Identity-Aware Access Controls to RAG Systems

Most RAG tutorials focus on relevance — chunking strategies, embedding models, and hybrid search fusion. What they rarely address is security. In production, retrieval pipelines pu...

Read source
martechseries.com /1 month ago

Descope Unveils Cross-App Access (XAA) Support, Letting Enterprises Manage AI Agent Access With Their Existing Identity...

Organizations can now use Descope to validate ID-JAG tokens from their customers’ identity providers, issue ID-JAG tokens for their own internal agents, and provide self-service XA...

Read source
aws.amazon.com /14 hours ago

Making Amazon Quick enterprise-ready: Automated, auditable cross-account resource promotion

Promoting Amazon Quick resources (agents, action connectors, knowledge bases, flows, and spaces) from a development to a production AWS account has been a manual, error-prone chore...

Read source
aws.amazon.com /1 month ago

Enable cross-cloud analytics with Amazon S3 Tables and Google BigQuery, Part 2: access control with Lake Formation

In Part 2 of this series, connect Google BigQuery to Amazon S3 Tables using AWS Lake Formation credential vending. Lake Formation manages fine-grained permissions and issues short-...

Read source

Turn fresh research into a full content calendar

Use SocialBu to discover ideas, generate post drafts, and schedule them across your social channels.

Sources covering Access Management

feeds.dzone.com

Recent coverage from public sources
Public source

aws.amazon.com

Recent coverage from public sources
Public source

aws.amazon.com

Recent coverage from public sources
Public source

aws.amazon.com

Recent coverage from public sources
Public source

blogs.vmware.com

Recent coverage from public sources
Public source

dev.to

Recent coverage from public sources
Public source